Meet every requirement for
ISO 27001

Assuric gives you the ISMS, policies and risk register to get ISO 27001 certified, all in one place.

  • Automated compliance tracking
  • ISO 27001 Policies
  • Information Security Management System

By continuing you agree to our privacy notice

AccurxTandemSembleLimbicBraiveDrDoctorCircle Health GroupNorthern Care Alliance NHS Foundation TrustCleo SystemsCorelineGuardantSanomePolyAIEolas MedicalChequpHeimDelfaHippo LabsInfixMegiNursebuddyOnion AIRhazesRosenfieldSurgery AIHealthnixThink DivergentHestaVitVioUniversity Hospitals of Derby and Burton NHS Foundation TrustAnimaAscentiAsterixEvergreen LifeHello PatientHealthtech-1Modality PartnershipNHS Wales Performance & ImprovementCwm Taf Morgannwg University Health BoardOperose HealthPatient Care Locally CIC (LLR)Theta SleepAccentureCareStackSouth Warwickshire University NHS Foundation TrustUniversity Hospitals of Leicester NHS TrustMersey and West Lancashire Teaching Hospitals NHS TrustWeymouth Bay Medical PracticeNottingham CityCare PartnershipMid Mersey Digital AlliancePenrose Health

Features

Everything you need for
ISO 27001

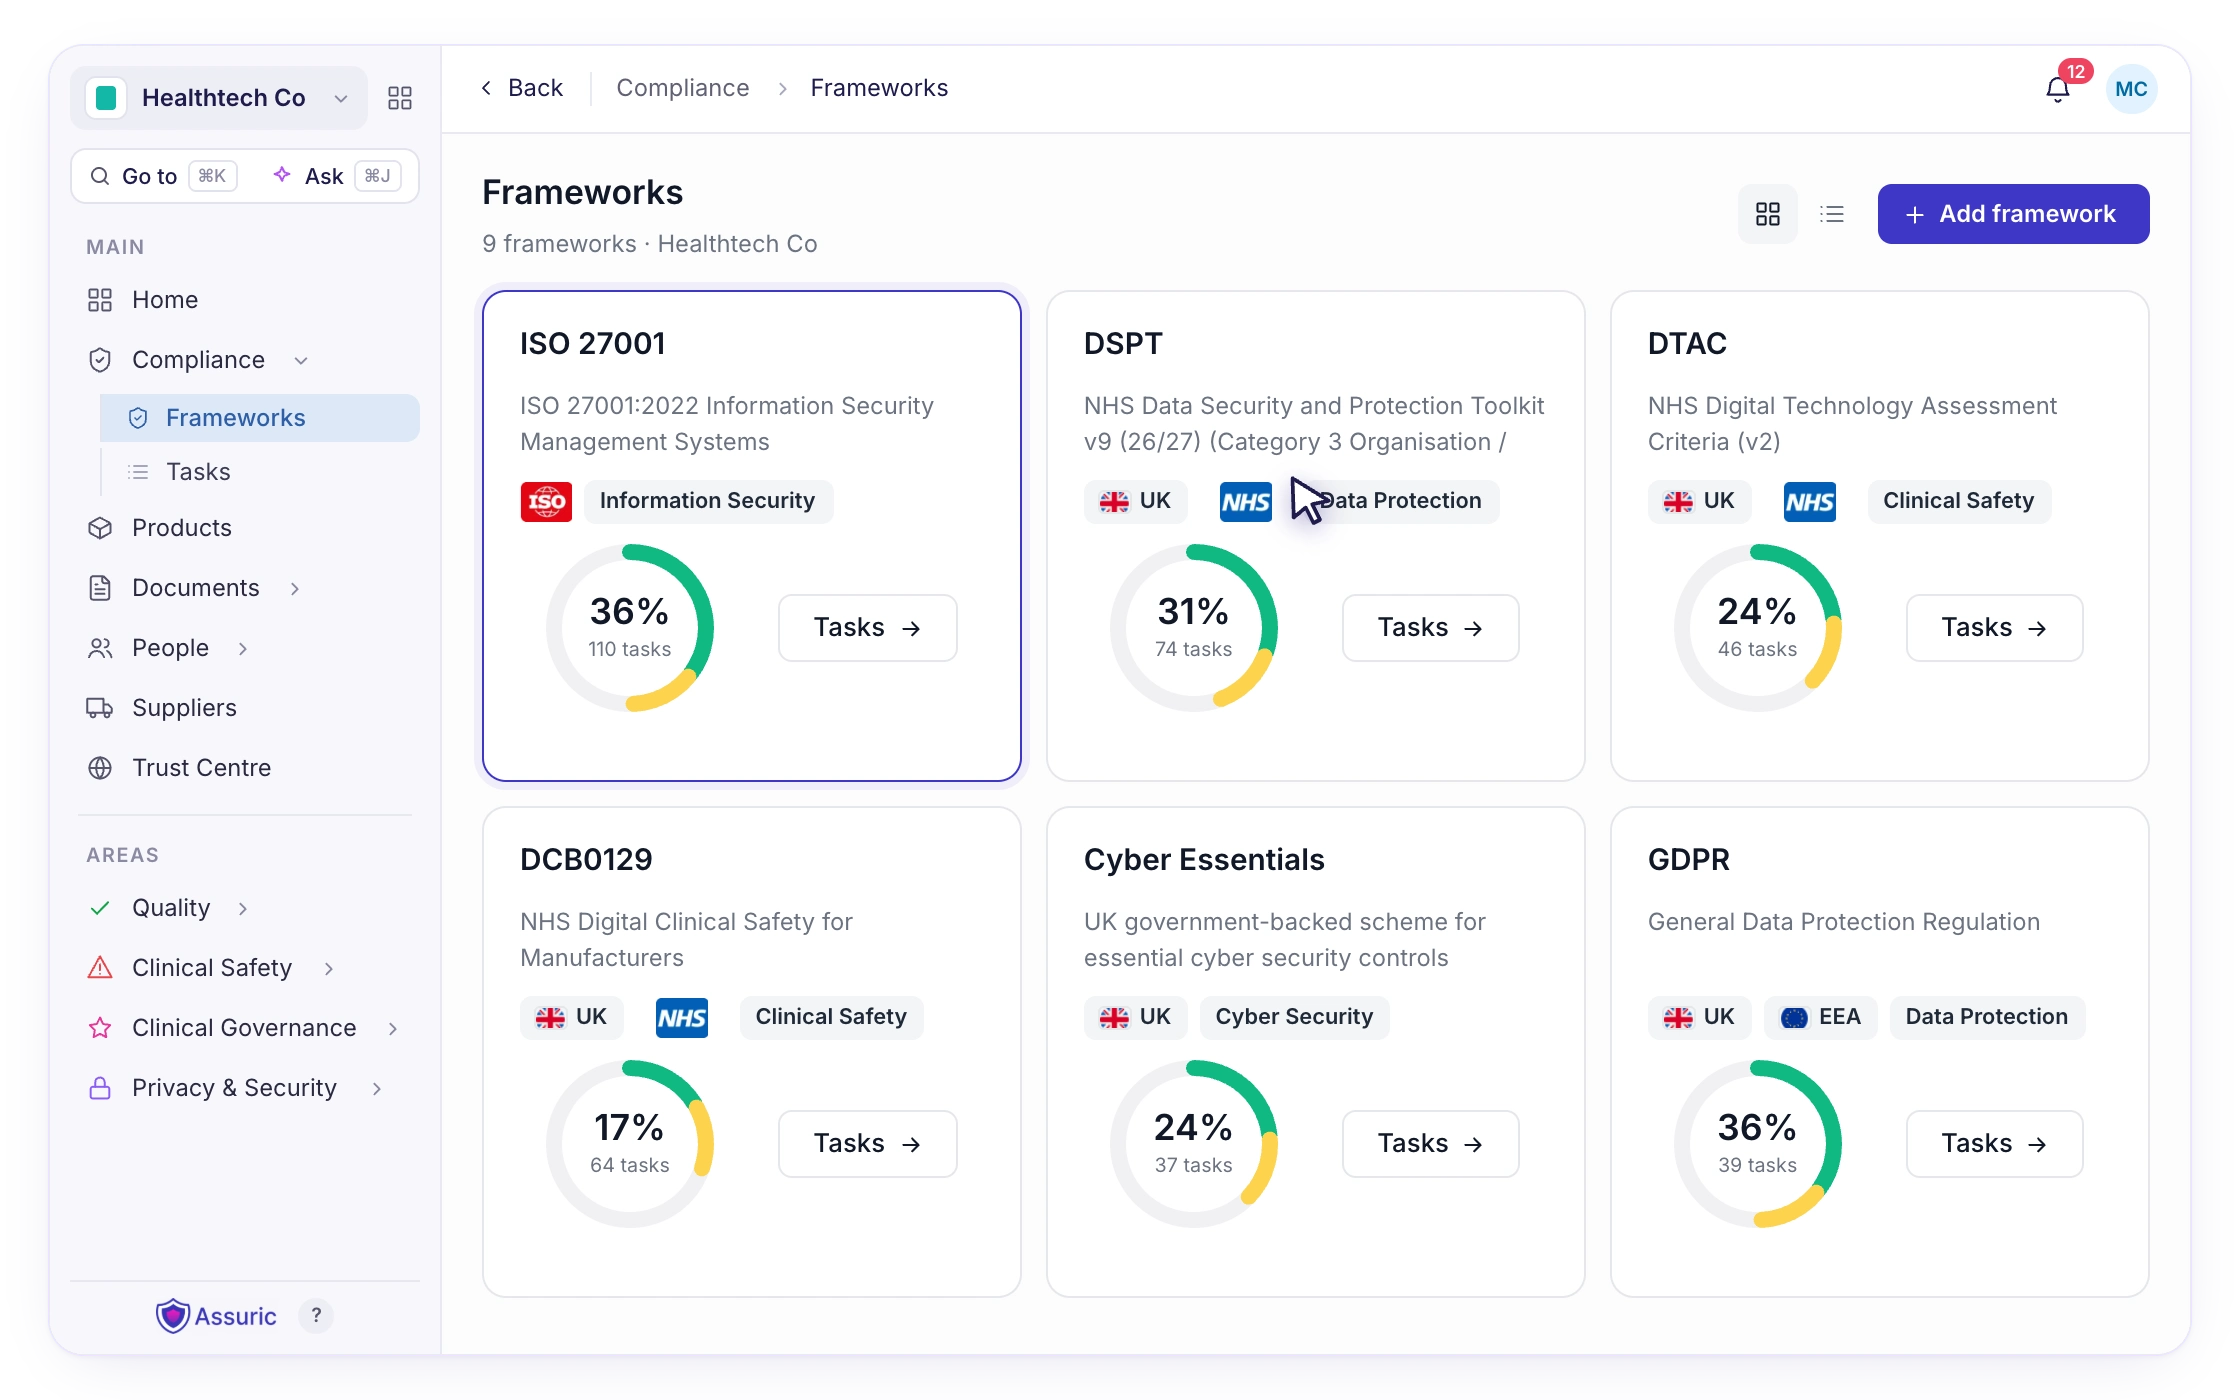
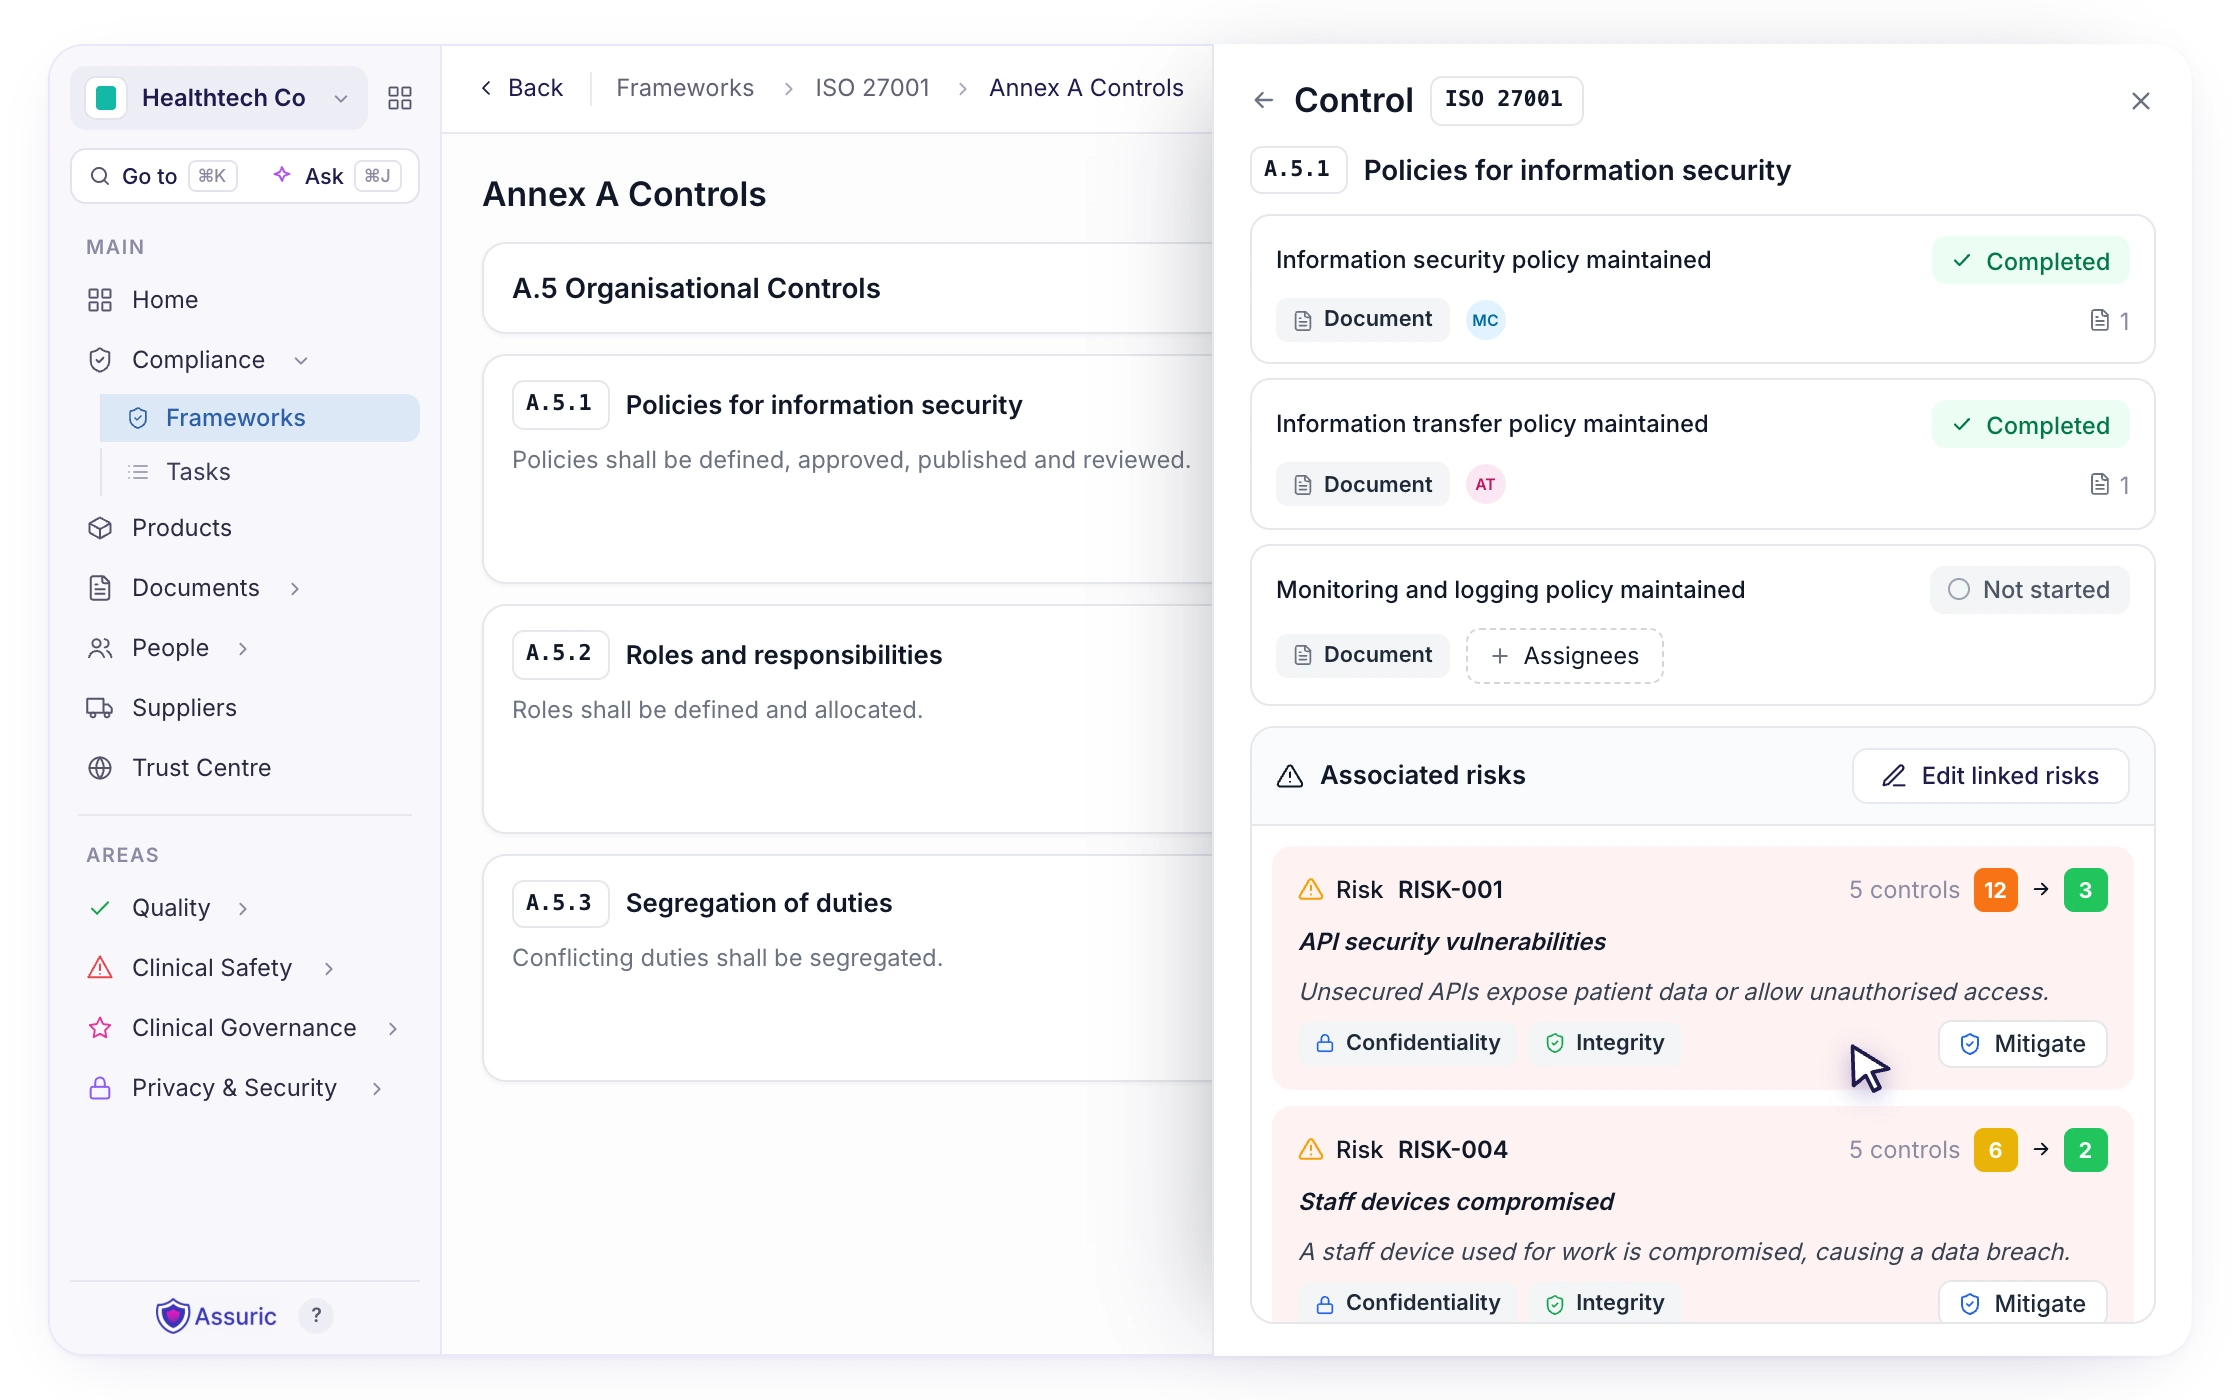
F01 — Framework tasks view

Automated compliance tracking

Automated compliance tracking

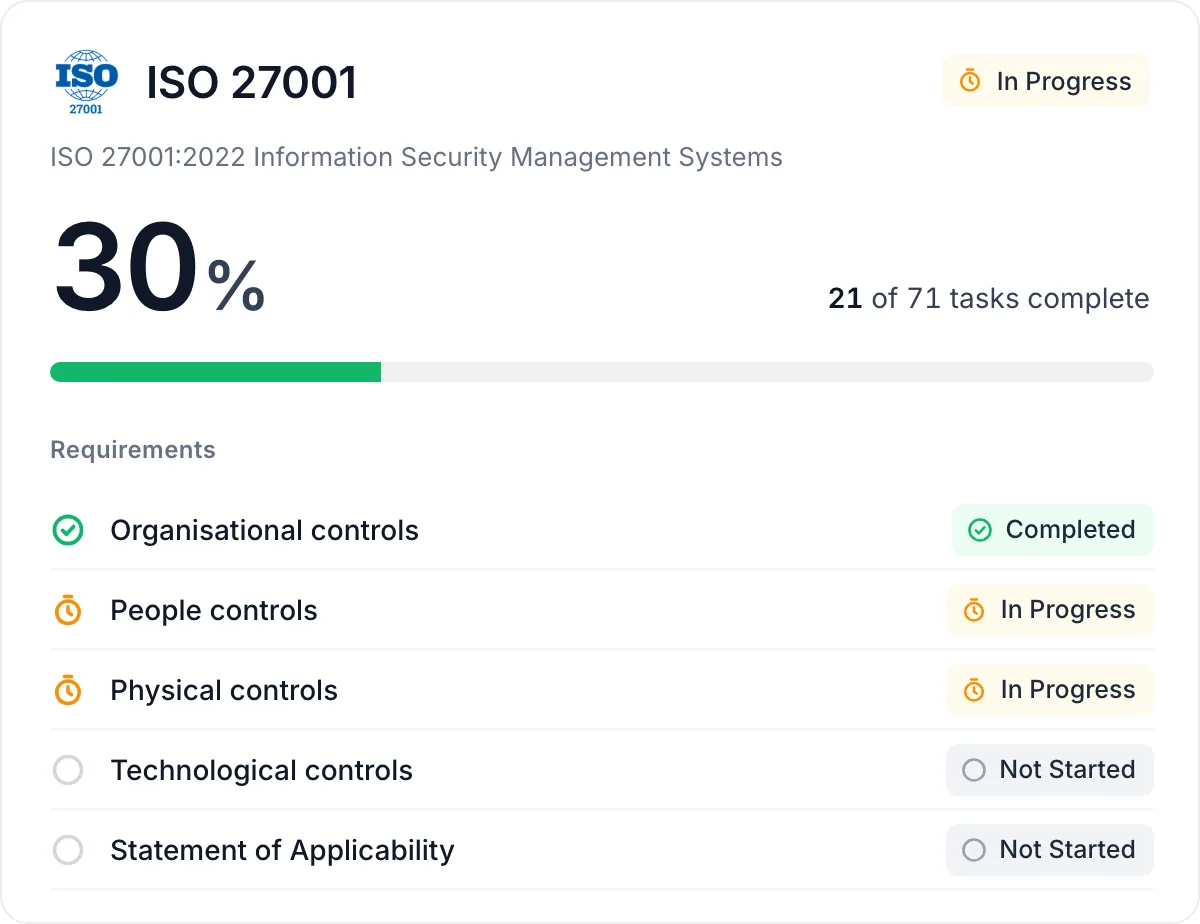
Easily fill any gaps, automate tasks, track compliance, and receive proactive alerts - ensuring requirements are met in record time.

Explore
F18 — Proof your team has read them

Document & policy management

ISO 27001 Policies

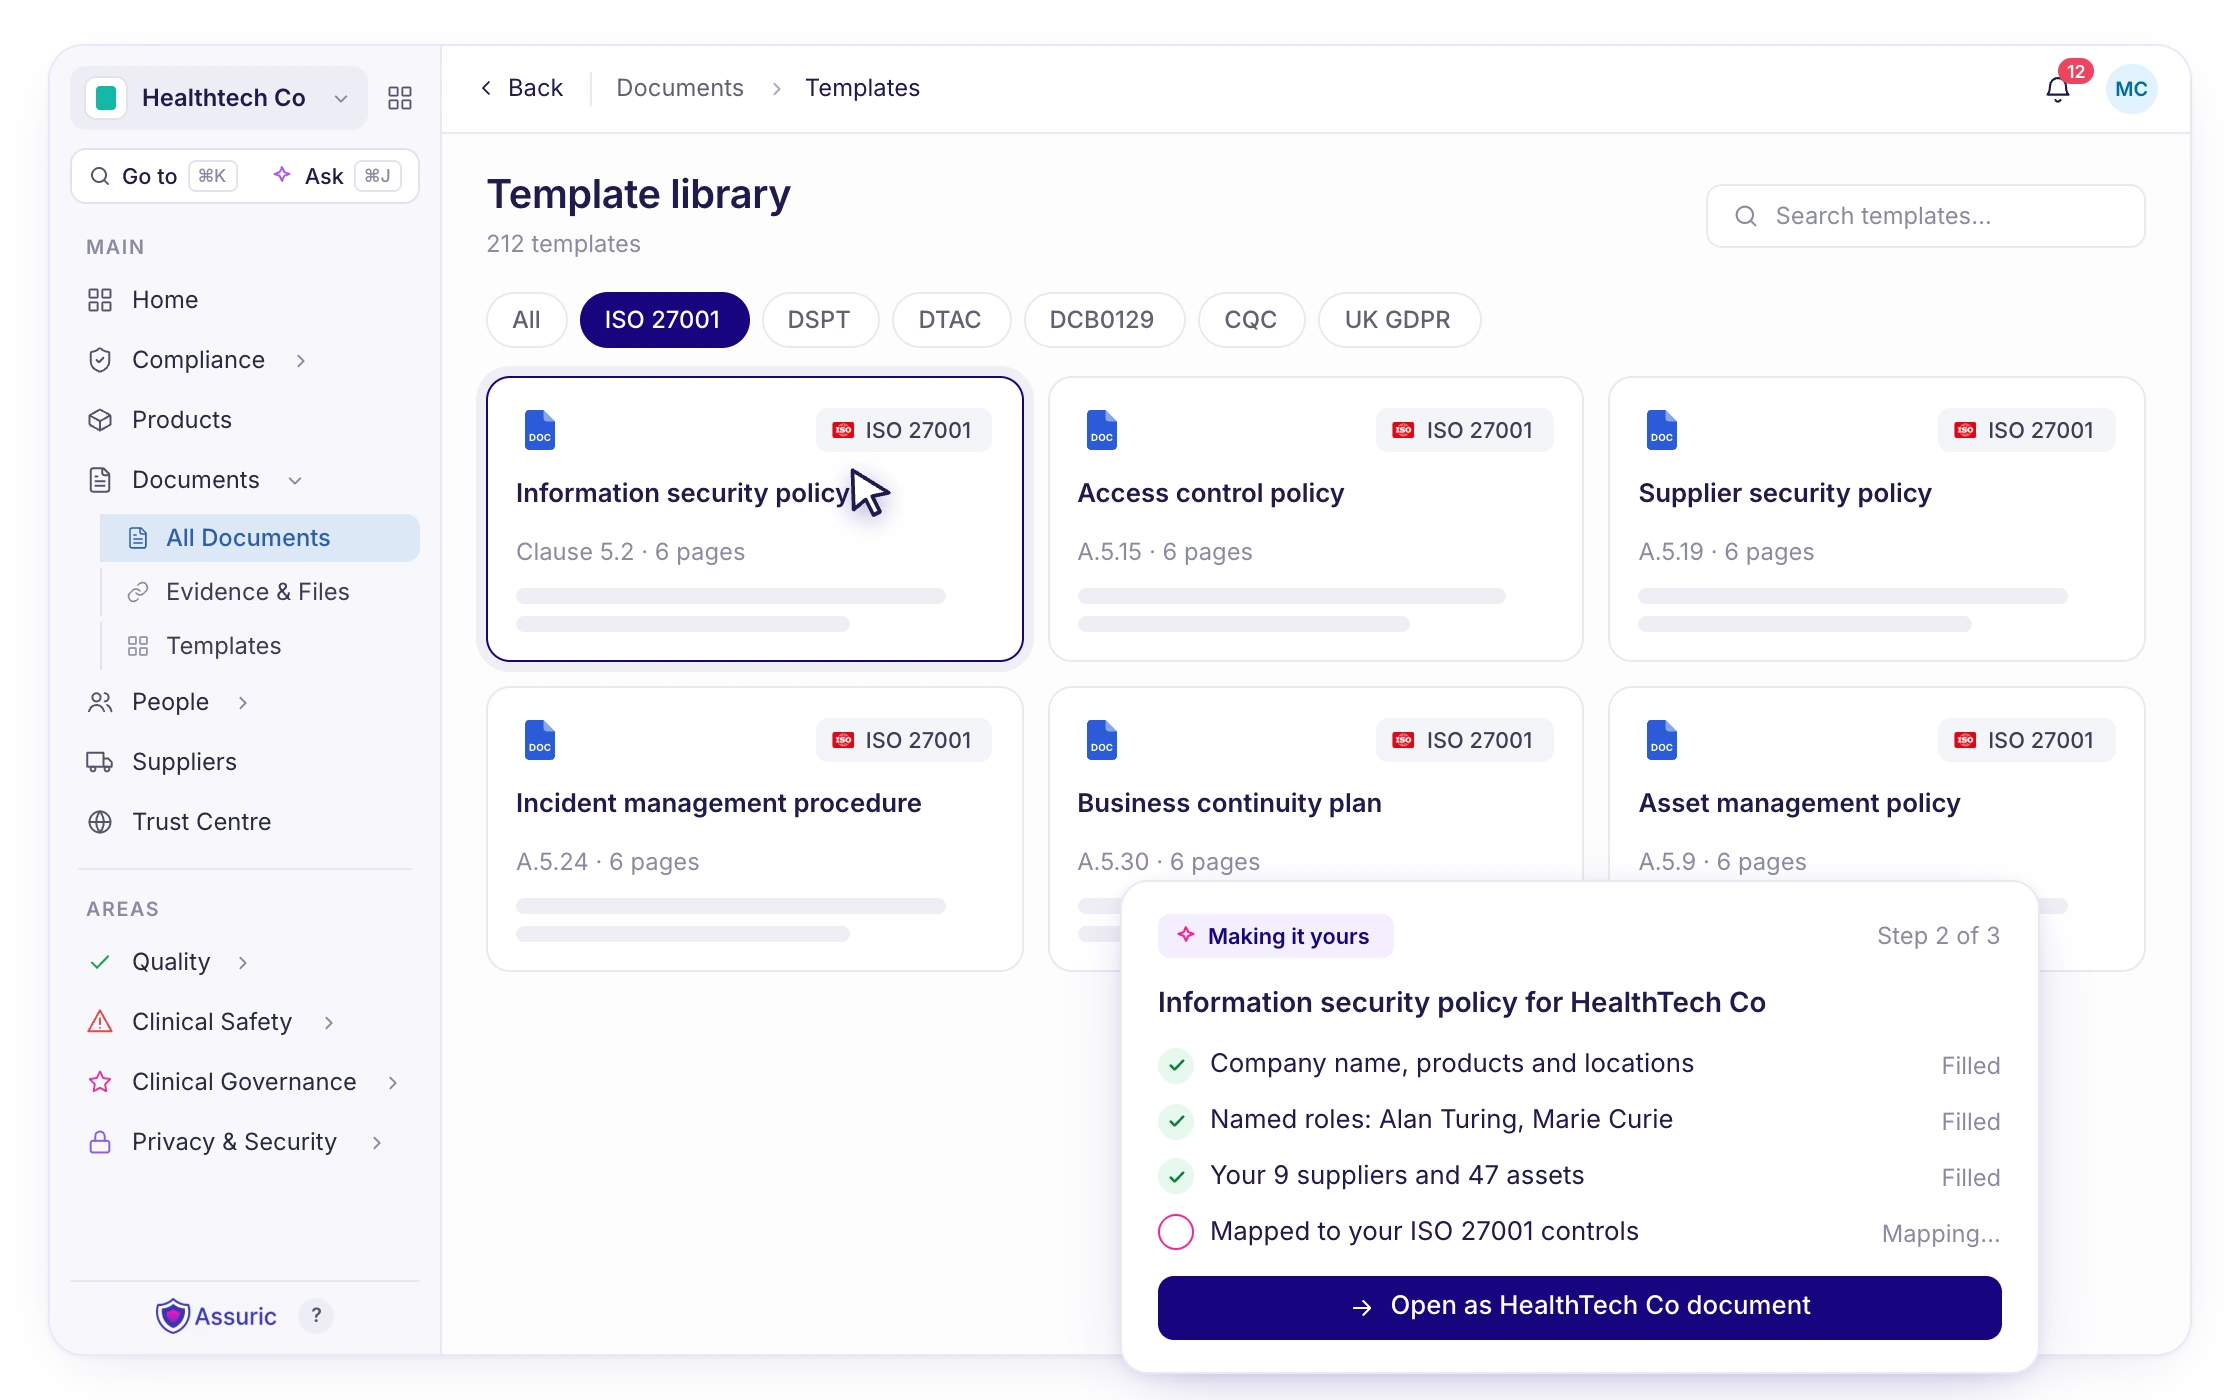
Access our library of customisable templates, documents and procedures.

Explore
G07 — Statement of applicability

All-in-one compliance

Information Security Management System

Use our structured framework for managing and implementing your policies, procedures and security controls.

Explore
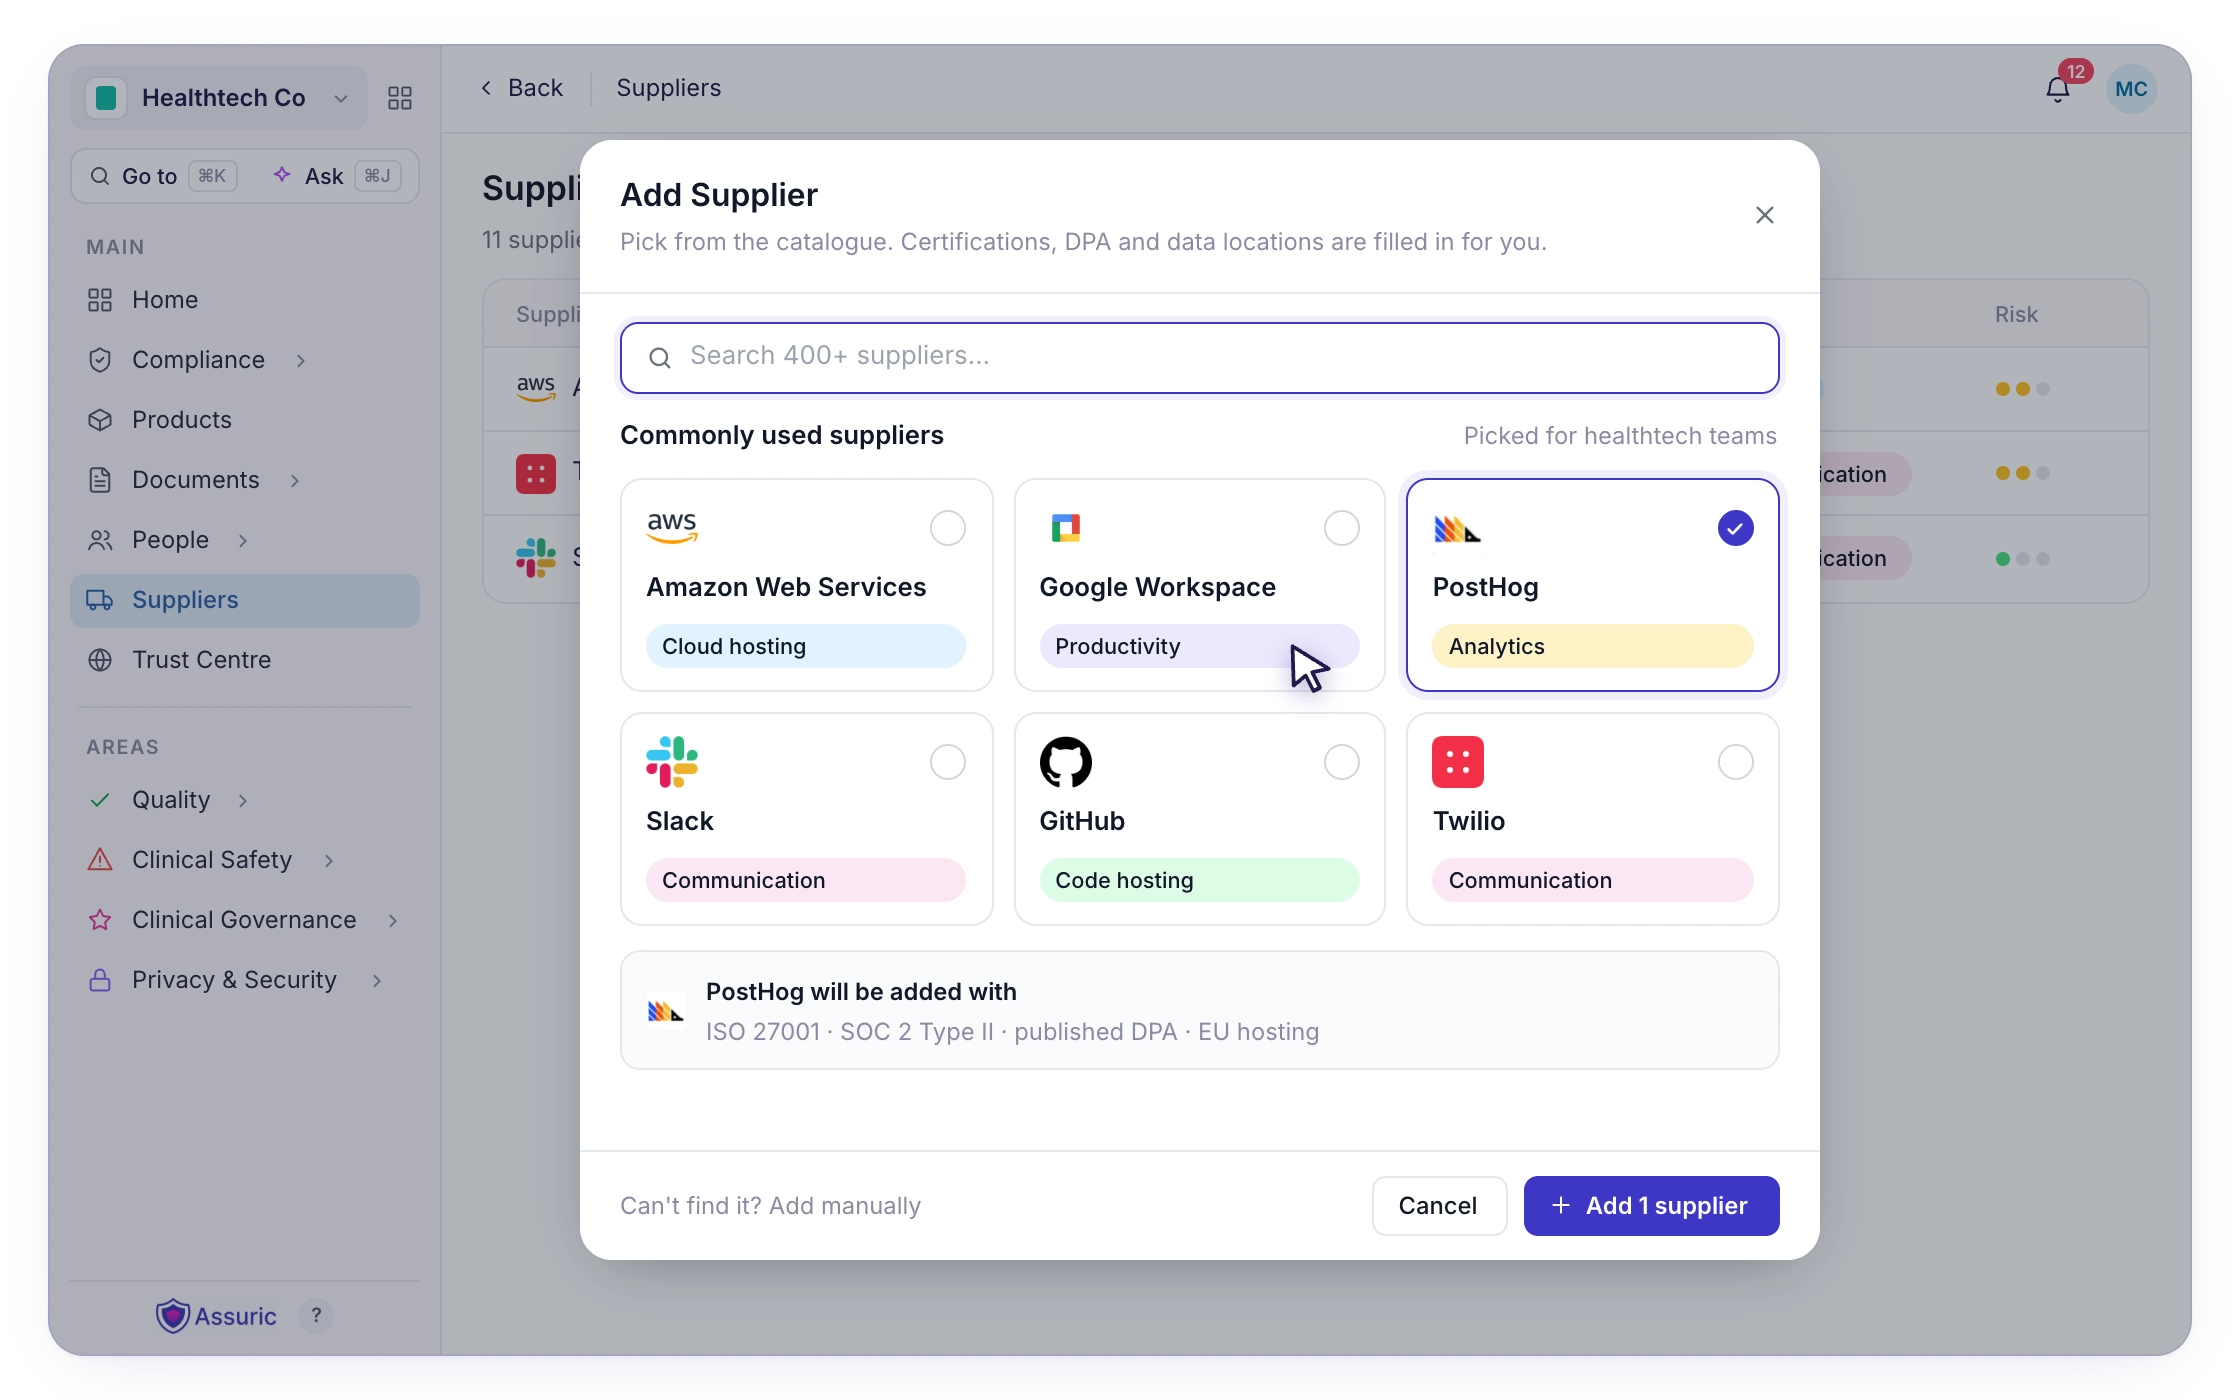
G04 — Supplier due diligence record

Third-party supplier management

Supplier Management

Add suppliers and associated evidence in one click from our library of over 100 suppliers. Automate supplier security assessments and due diligence processes.

Explore
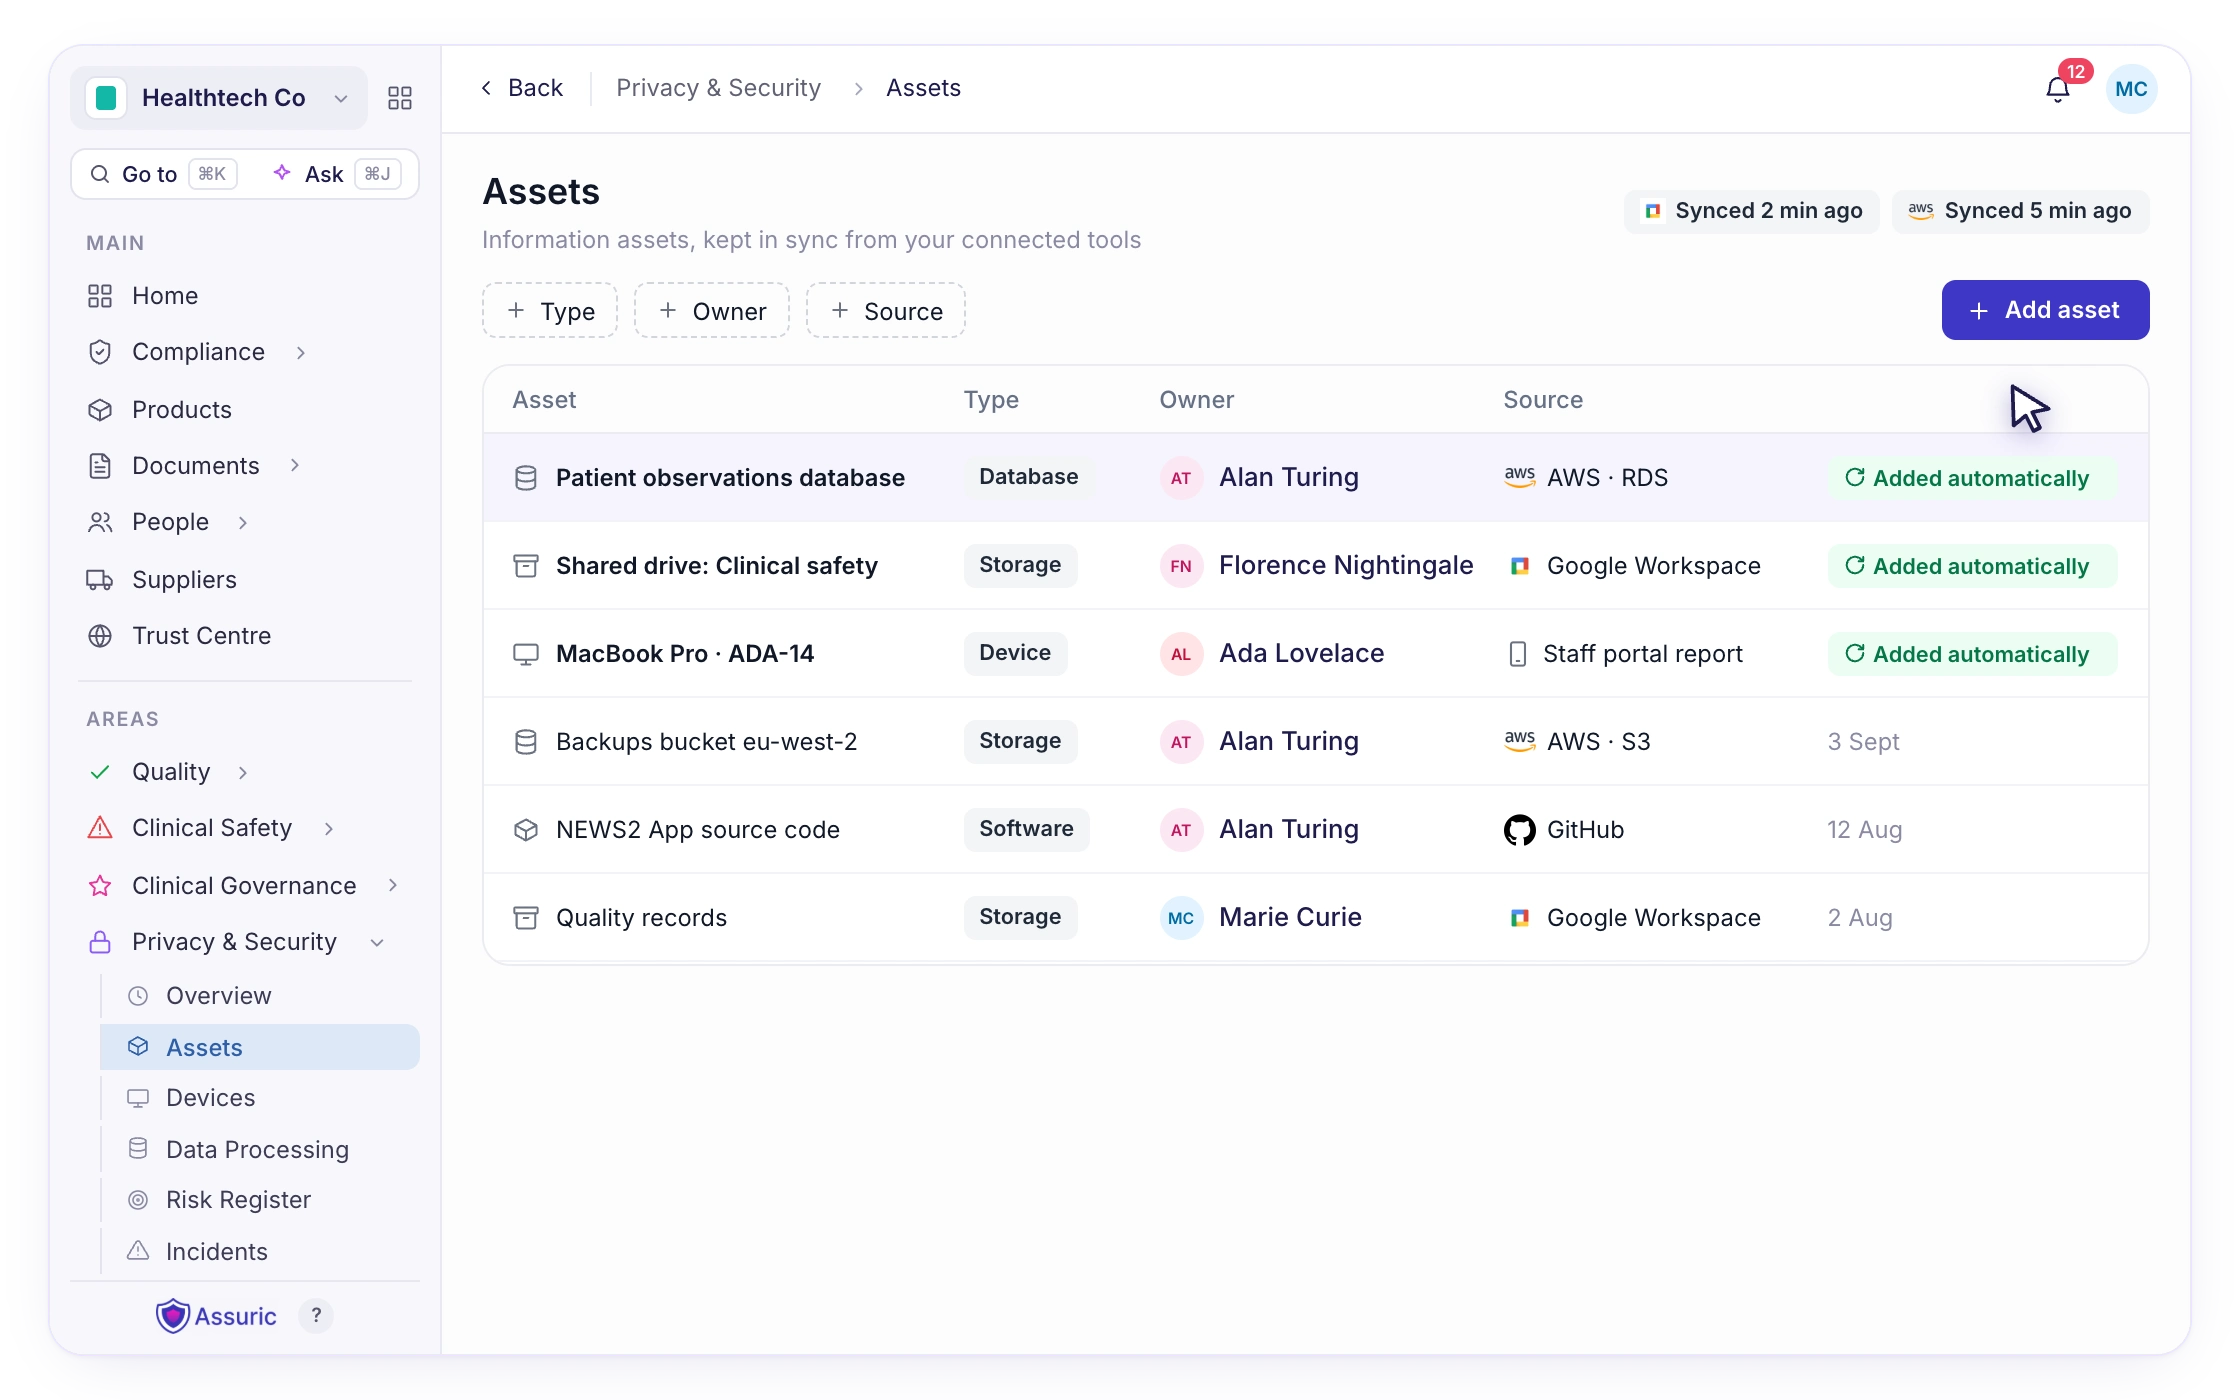
F41 — Infrastructure in the same register

Asset & device management

Asset Management

Identify and track information assets including company devices.

Explore
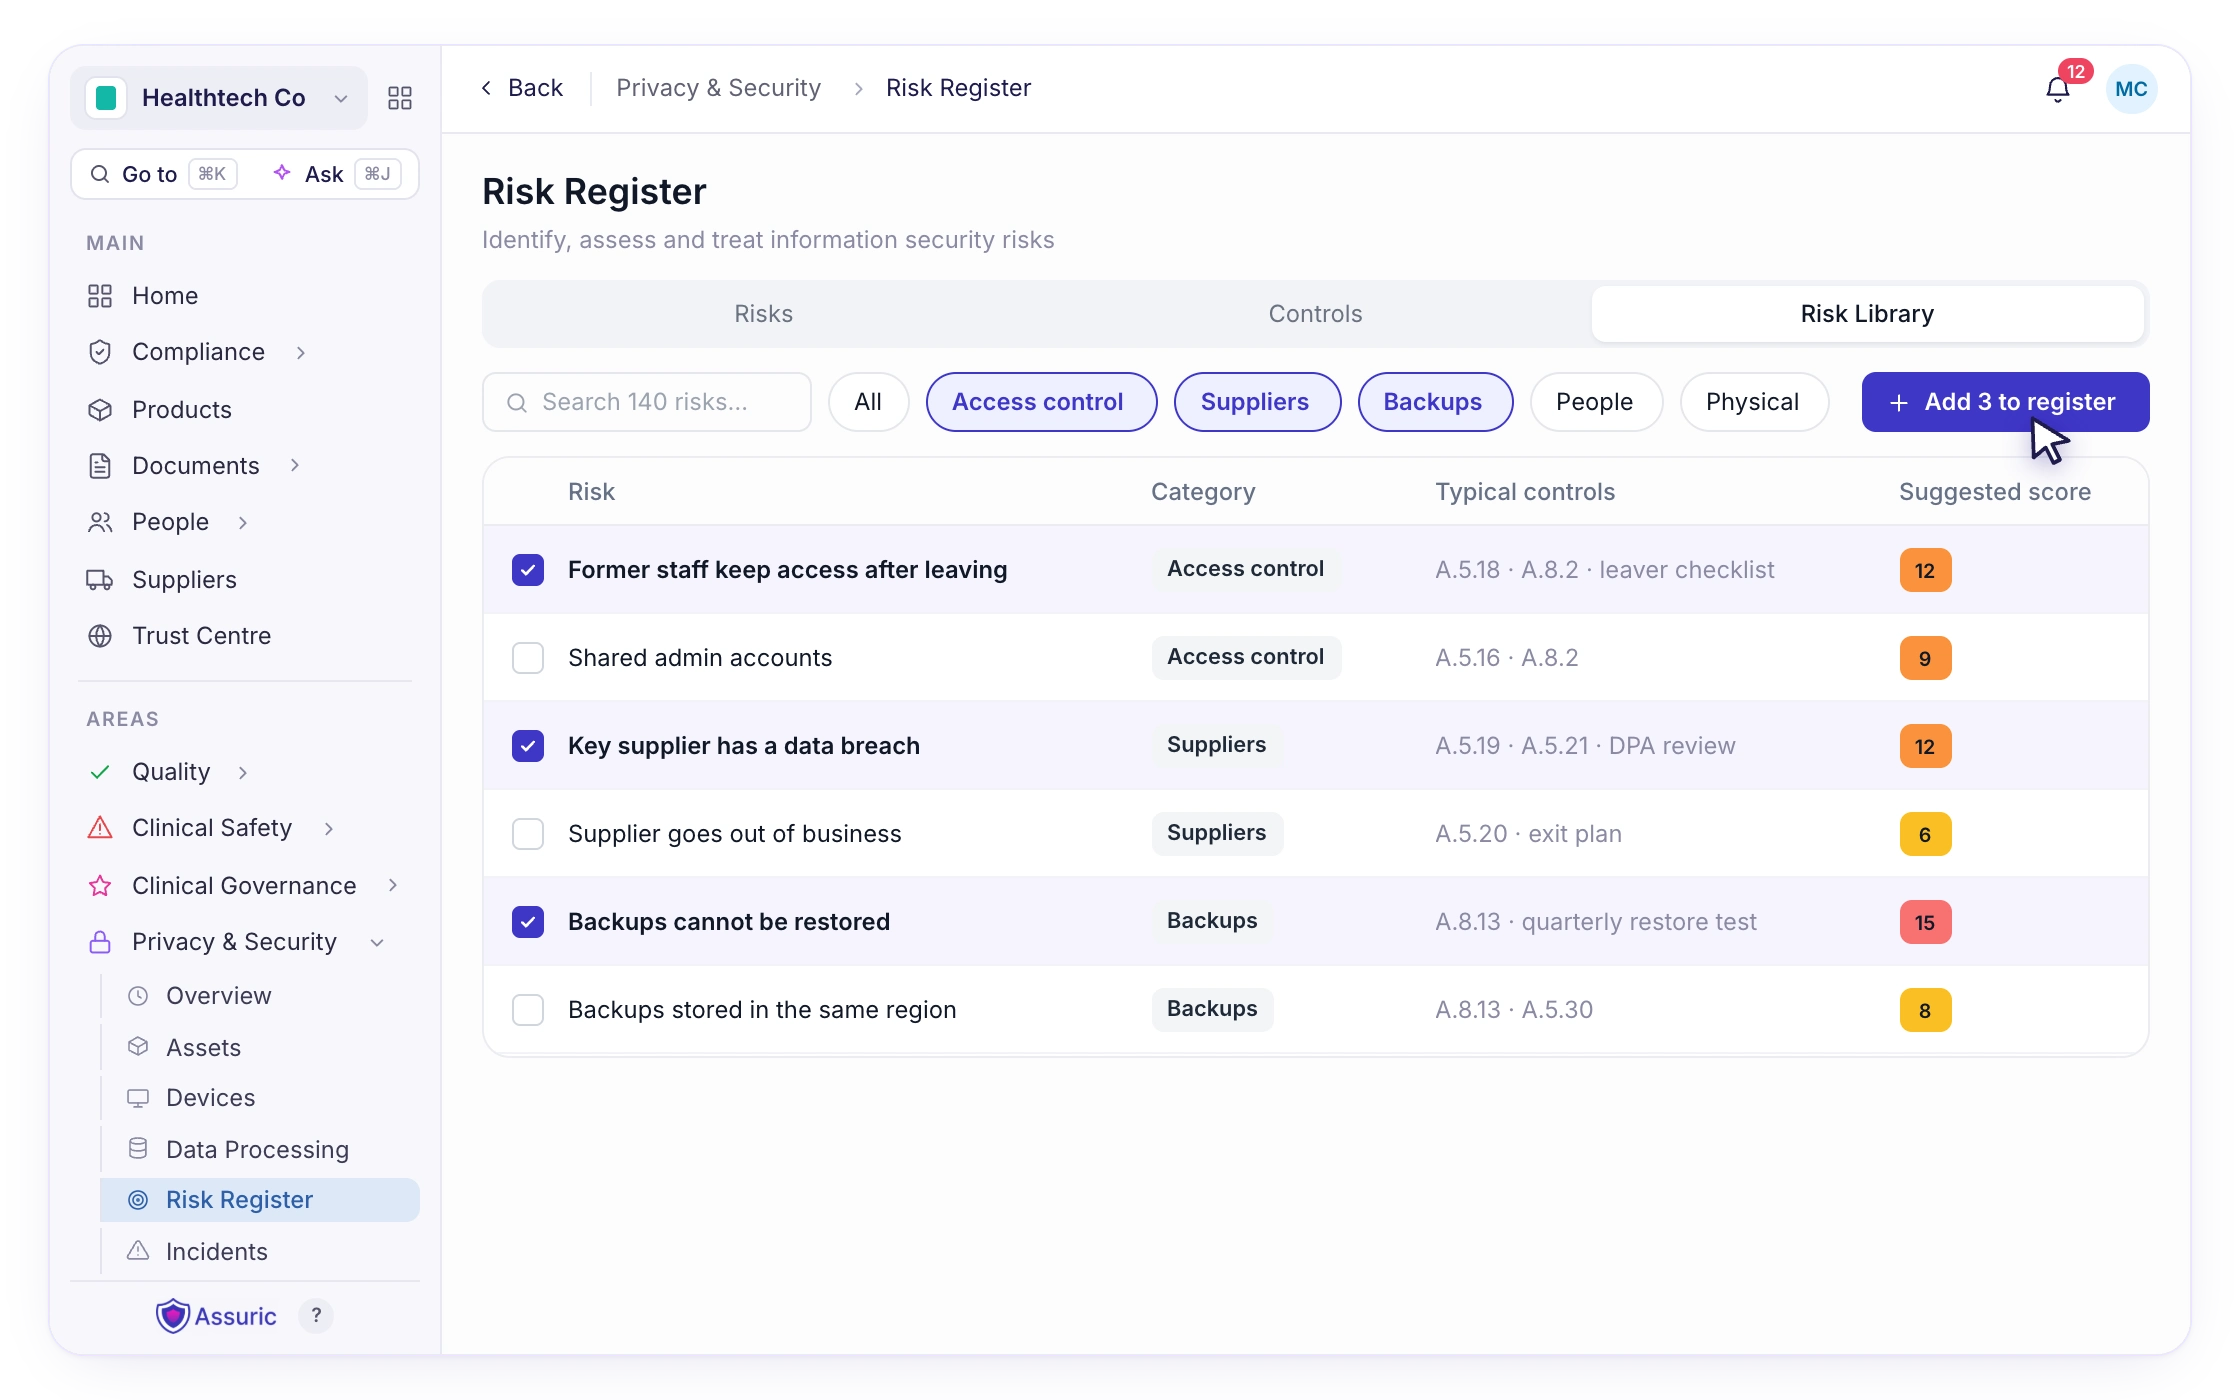
G08 — Risk with its treatment plan

DPIA, RoPA & risk management

Risk Register

Record risks with the help of our risk library and AI. Develop actionable mitigation strategies and track the risk treatment process to maintain continuous compliance.

Explore

Benefits

An ISMS that runs itself

Meet several standards at once

Annex A controls overlap heavily with Cyber Essentials, NHS DSPT and NHS DTAC, and the evidence you gather for one answers a large part of the others. Each control shows which frameworks it satisfies, so you can see what a second certification actually costs before you commit to it.
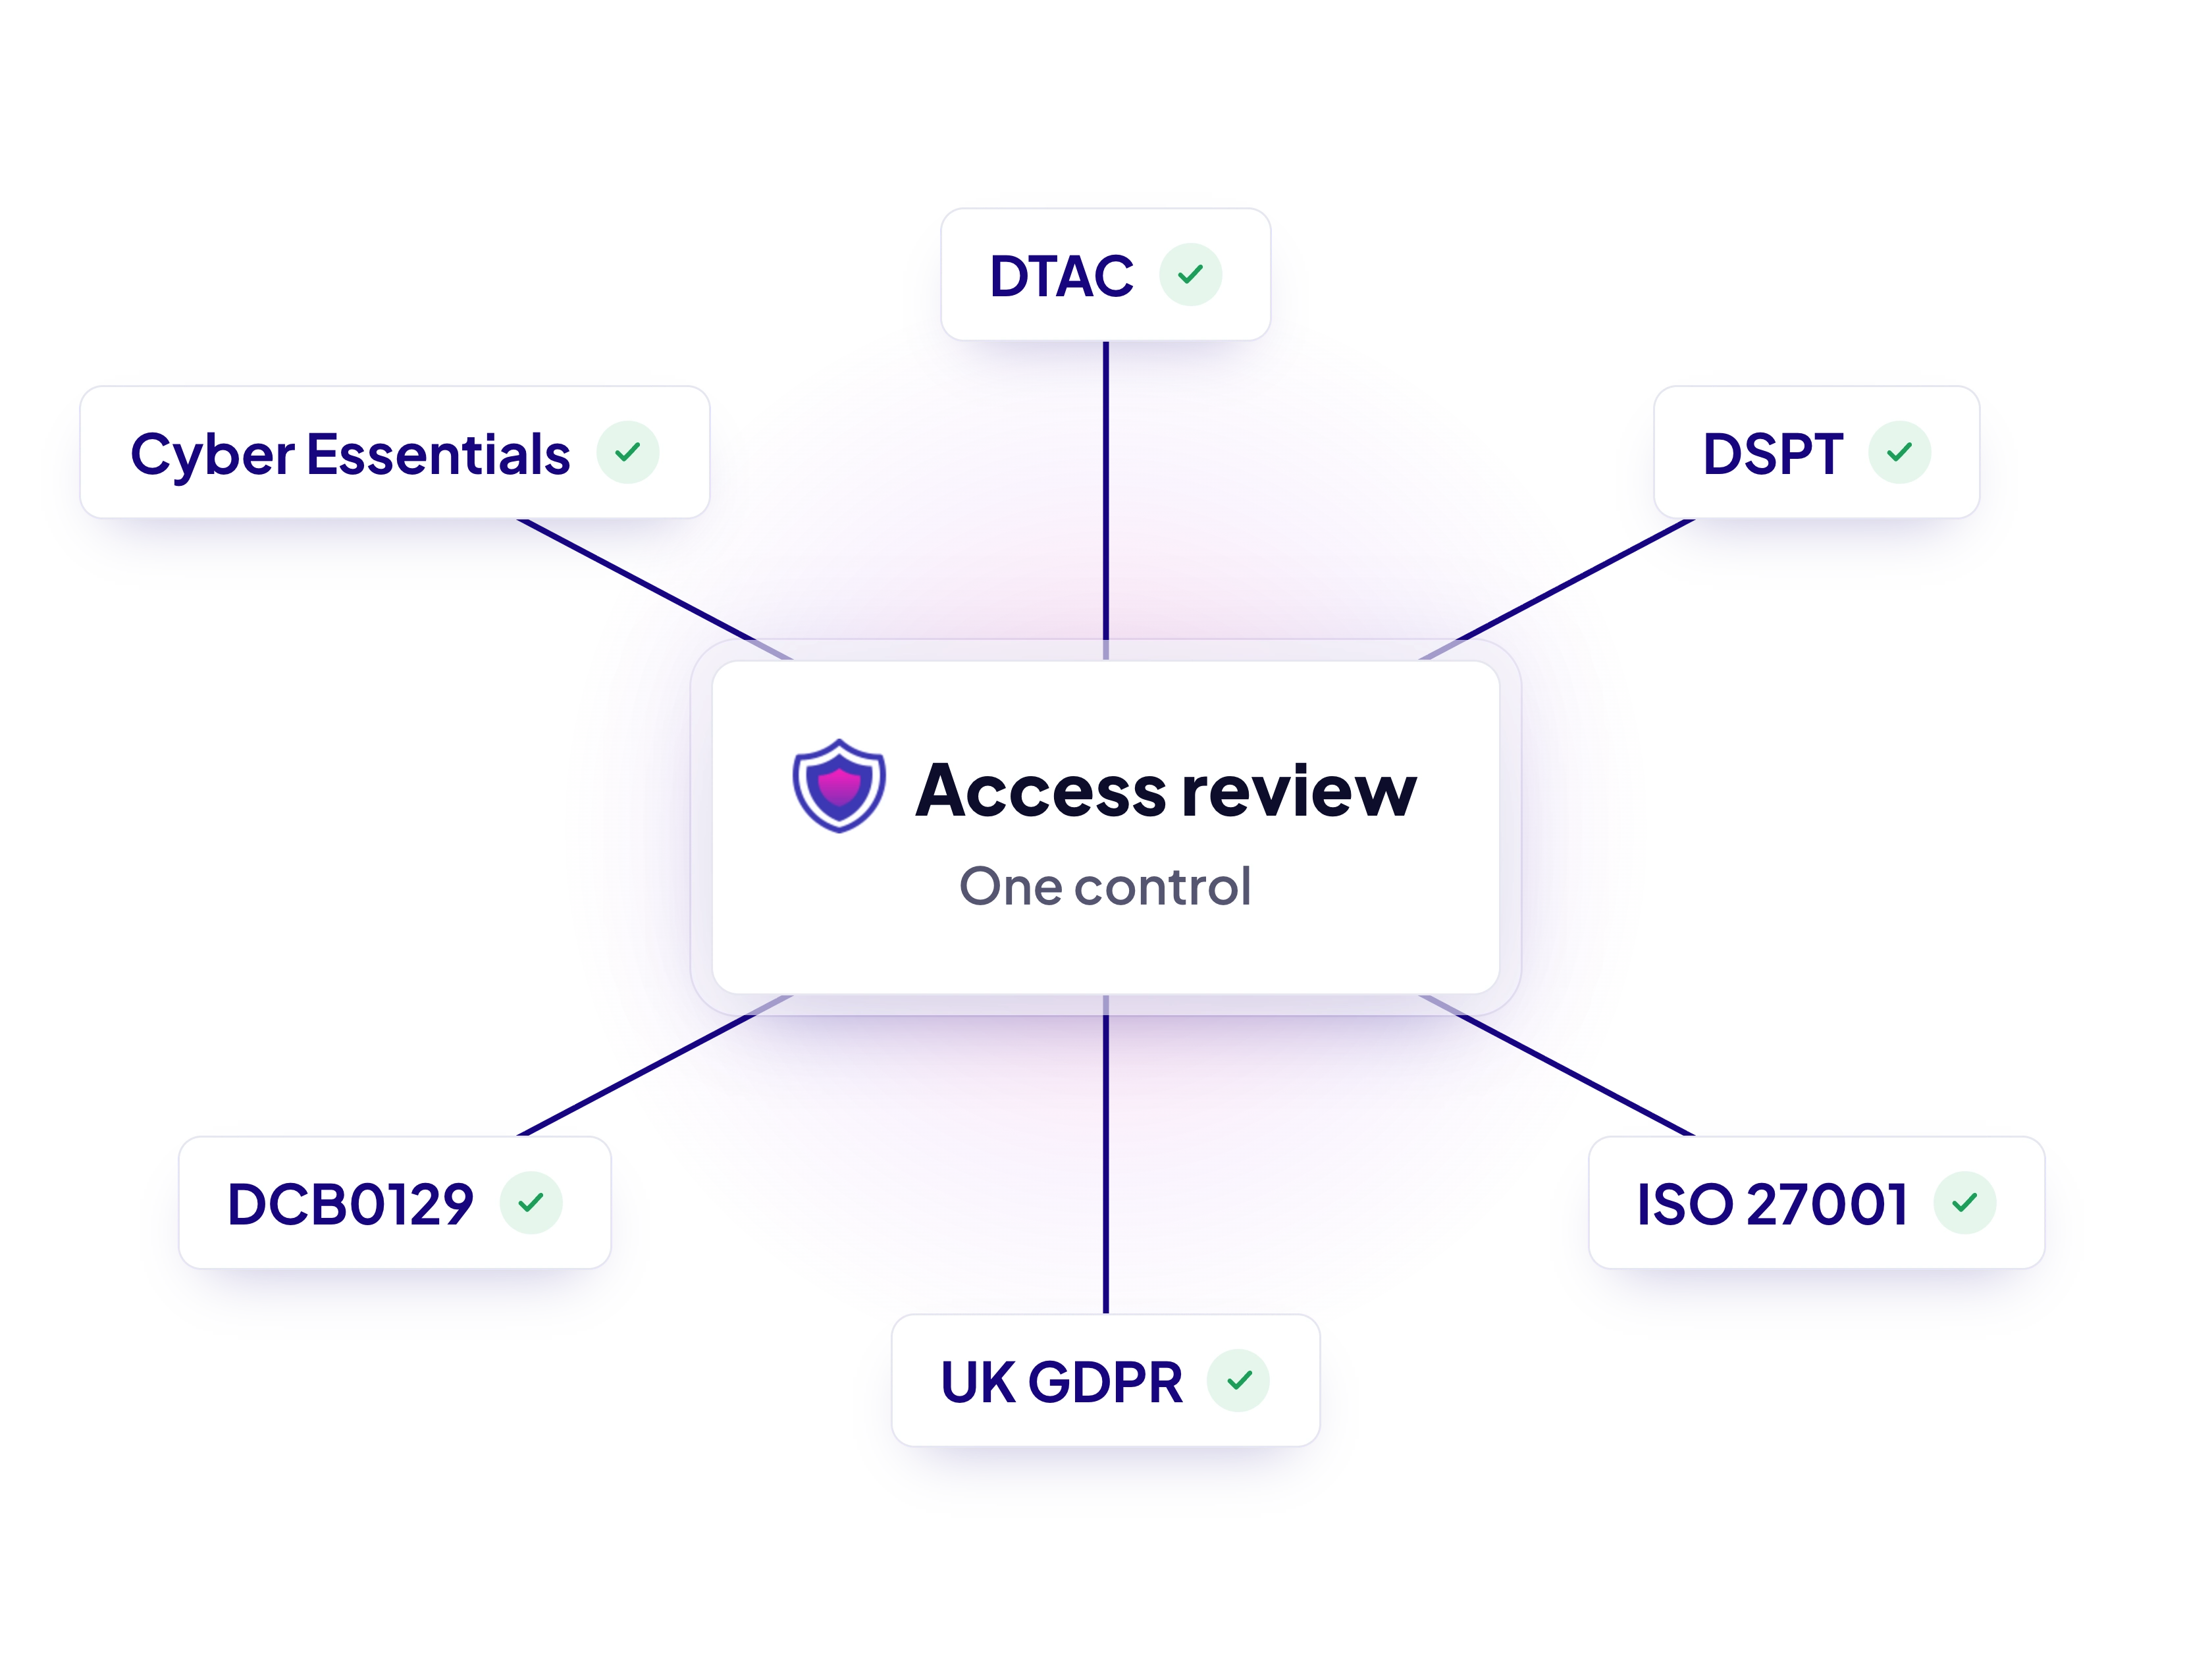
V02 — One control every standard

Your systems, suppliers and assets in one picture

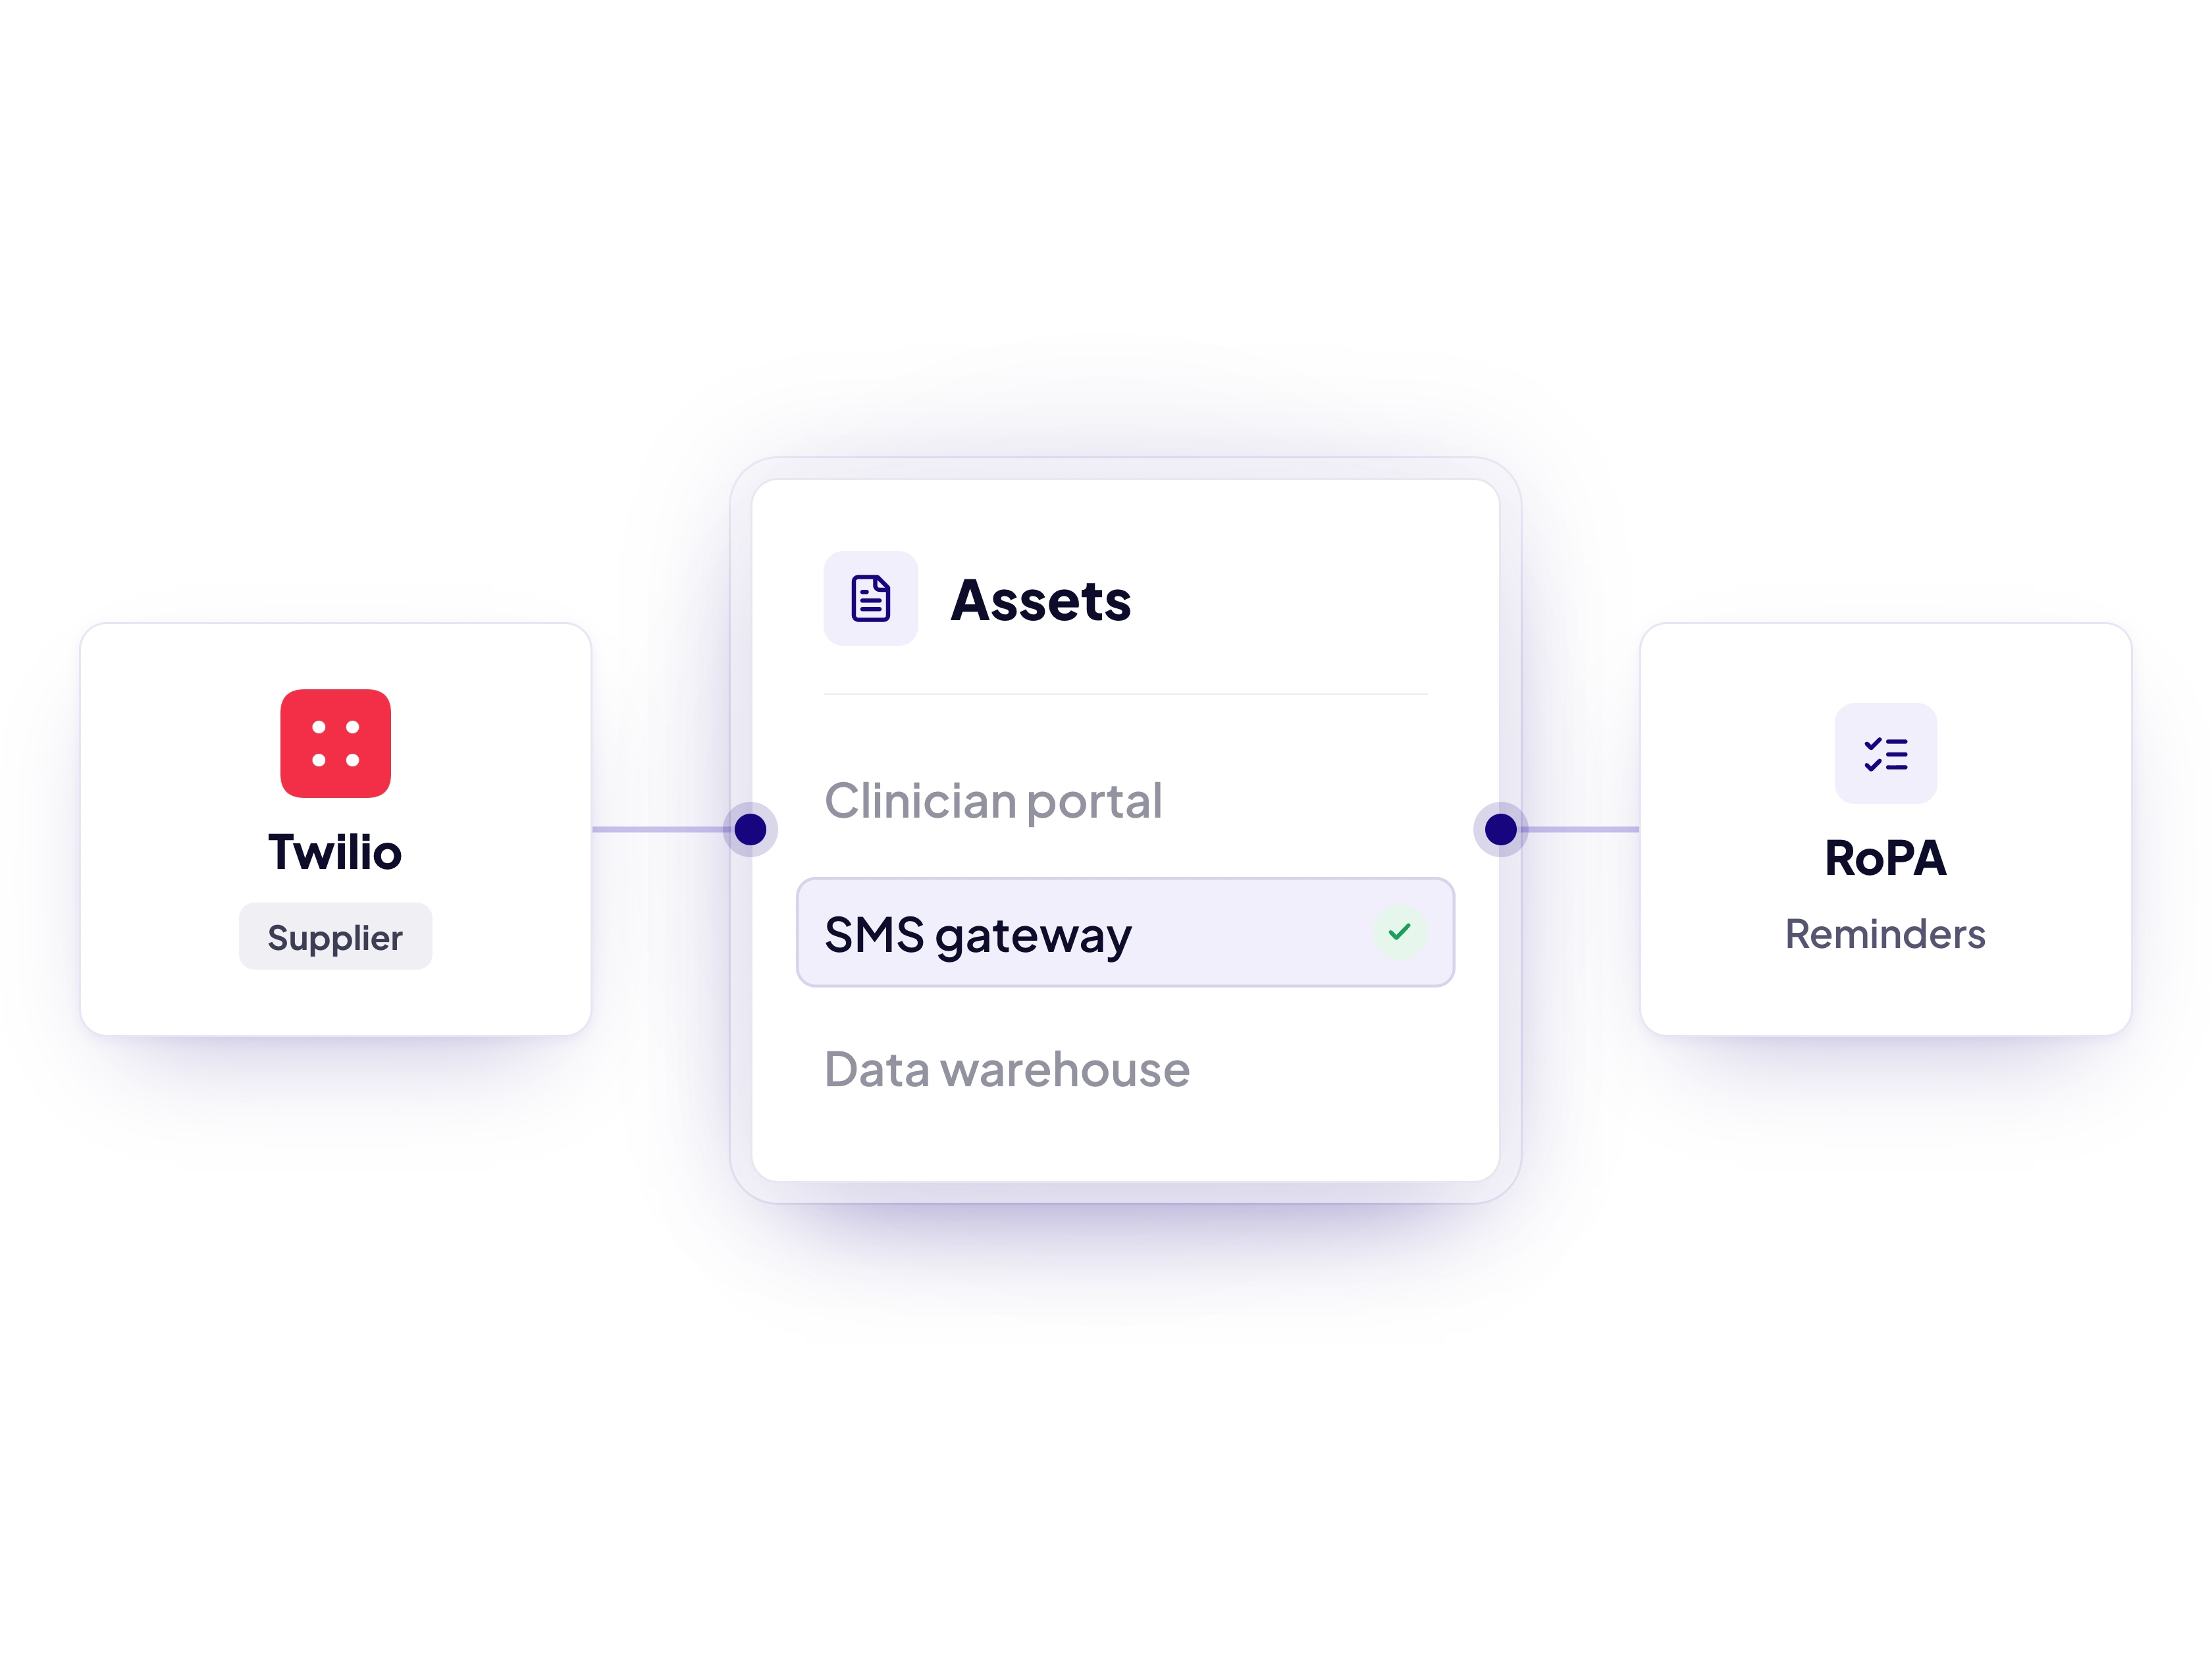
Your information assets link to the suppliers that provide them, the controls that protect them and the risks they carry, so following any one of them leads to the rest, and nothing sits in isolation.

Asset management 06

You're not starting from a blank page

Over 100 suppliers come pre-assessed, with a risk library, control set and policy templates already written to the standard. You're adapting what's there to your business rather than researching each control and drafting from nothing.

N8 — Not starting from blank

Facilitated internal audits

ISO 27001 requires internal audits and a management review before a certification body will look at you, and most teams have nobody qualified to run them independently. We connect you with audit partners who work directly in your workspace, so there's no evidence pack to assemble and findings land as tracked actions.

S12 — Control set and its audit

Frameworks

Mapped to other frameworks

Overlapping requirements and evidence are mapped across frameworks automatically, so you never do the same work twice.

What our customers say

VitVio

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”

Maks Kozarzewski

COO, VitVio

Accenture

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”

Paul Llewellyn

CCIO, Accenture

Tandem Health

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”

Katie Baker

Director UK & Ireland, Tandem

Frequently asked questions

Get in touch if we haven't answered your question below. We are always happy to help!

ISO 27001 is a globally recognised and industry leading information security framework. It provides a framework for establishing, implementing, maintaining and continually improving an Information Security Management System (ISMS).

ISO 27001 is important because it helps organisations: Protect the confidentiality, integrity, and availability of information assets. Reduce the risk of data breaches and cyber threats. Provide assurance to customers, partners, and stakeholders. Align security practices with global best practices.

By achieving ISO 27001 certification, organisations signal a serious commitment to safeguarding data and managing information security risks responsibly.

An ISMS is a set of policies, procedures, and controls designed to manage information security risks. It's the core component of ISO 27001.

No, ISO 27001 is not legally required, however compliance gives confidence of a high level of information security.

Any organisation that handles sensitive information can use ISO 27001. It is voluntary, so most teams pursue it because customers, partners or investors want proof of strong information security. For digital health companies handling patient data, it is a widely recognised way to give that assurance.

Improved Risk Management: Systematic identification, evaluation, and mitigation of information security risks. Trust and Reputation: Builds confidence among stakeholders, clients, and partners. Operational Efficiency: Encourages process standardisation and internal accountability. Incident Preparedness: Enhances response plans for security incidents and data breaches. Competitive Advantage: Certification can differentiate you in a crowded marketplace.

The process includes a gap analysis, implementation of controls, internal audits, and an external certification audit conducted by an accredited certification body.

Gap Analysis: Identify current practices vs. standard requirements. Planning & Scope Definition: Define the boundaries of the ISMS. Risk Assessment & Treatment: Identify threats and apply controls. Documentation & Policy Development: Formalise procedures and responsibilities. Training & Awareness: Ensure personnel are aware of policies and their roles. Internal Audit: Evaluate compliance with internal ISMS controls. Management Review: Review audit results and approve improvements. External Certification Audit: Conducted in two stages by an accredited body. Certification Issuance: Once approved, certification is issued for 3 years with annual surveillance.

Use the Assuric platform to achieve all of the above in record time.

An ISO 27001 certificate is valid for three years. Your certification body carries out a surveillance audit each year in between, then a recertification audit at the end of the cycle. Assuric keeps your controls, evidence and reviews in one place, so each audit builds on the work you have already done.

They overlap heavily. Many ISO 27001 Annex A controls also answer parts of Cyber Essentials, NHS DSPT and NHS DTAC, so the evidence you gather for one counts towards the others. In Assuric each control shows which frameworks it satisfies, so you can see what the next framework involves before you start.

All the necessary staff training you'll need (both basic and specialist), combined with automated tracking and reminders to ensure compliance.

Automate internal audits, sail through external audits, and attain all necessary certifications in record time.

Ready for ISO 27001?

Book a call and we'll help you scope your ISMS and plan your route to certification.