The faster, simpler way to get SOC 2 ready
Assuric is the fastest way for digital health companies to get SOC 2 ready, automating compliance busywork and helping you build trust as you expand internationally.
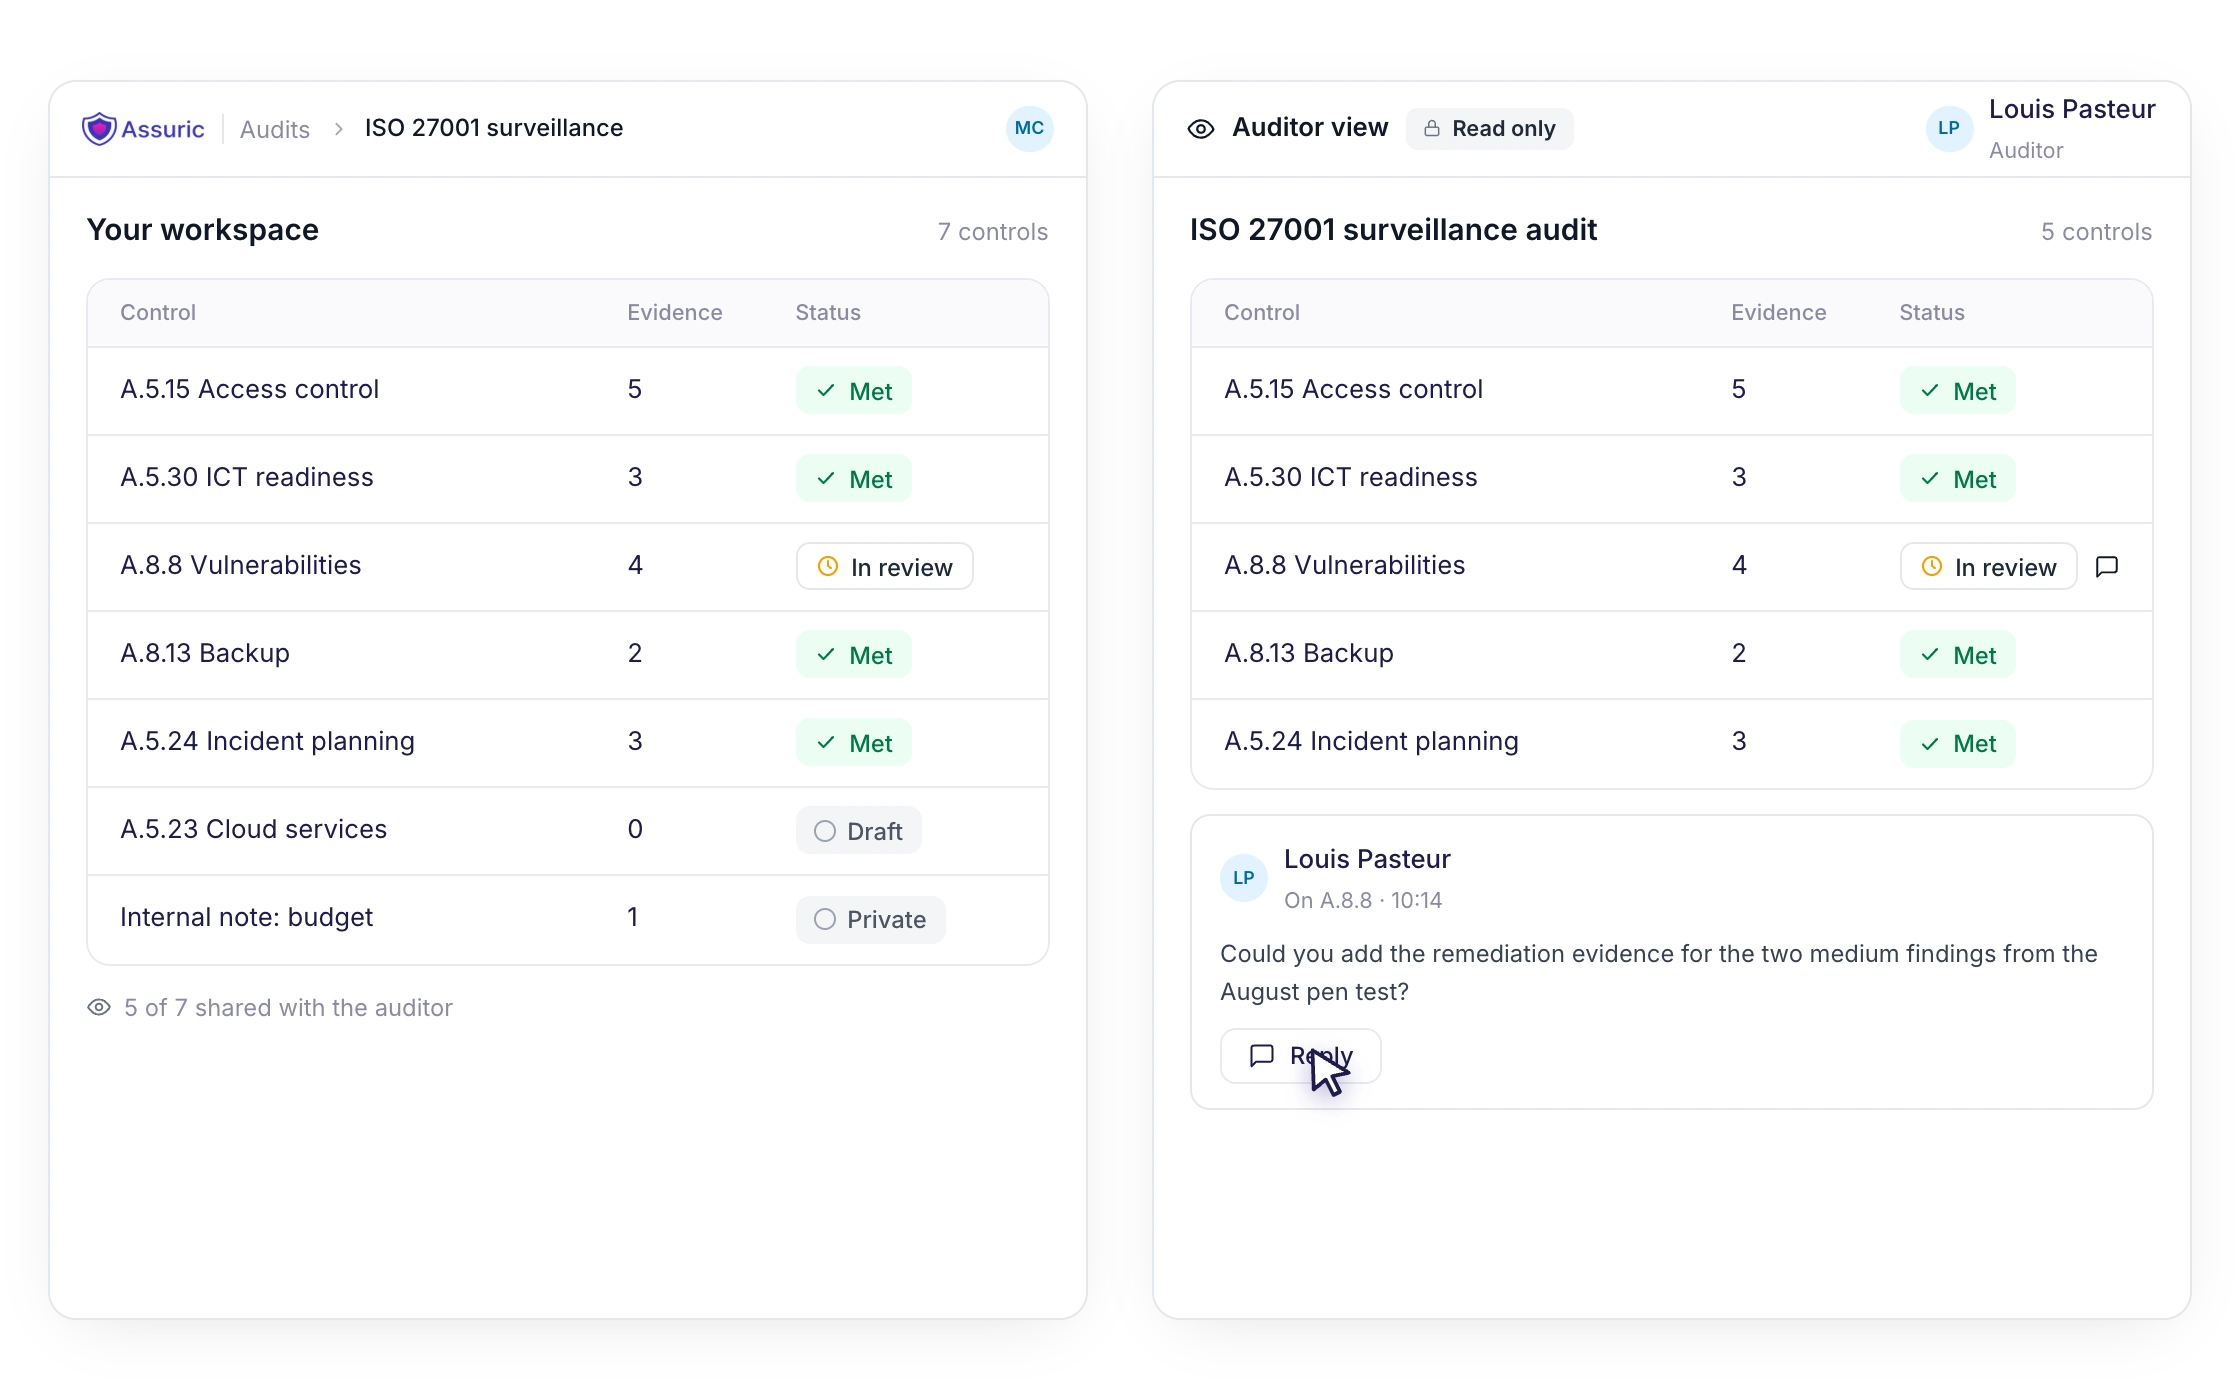
Assuric gives you the policies, controls and auditor access to get SOC 2 ready, all in one place.
Trusted bysecurity teams


Features
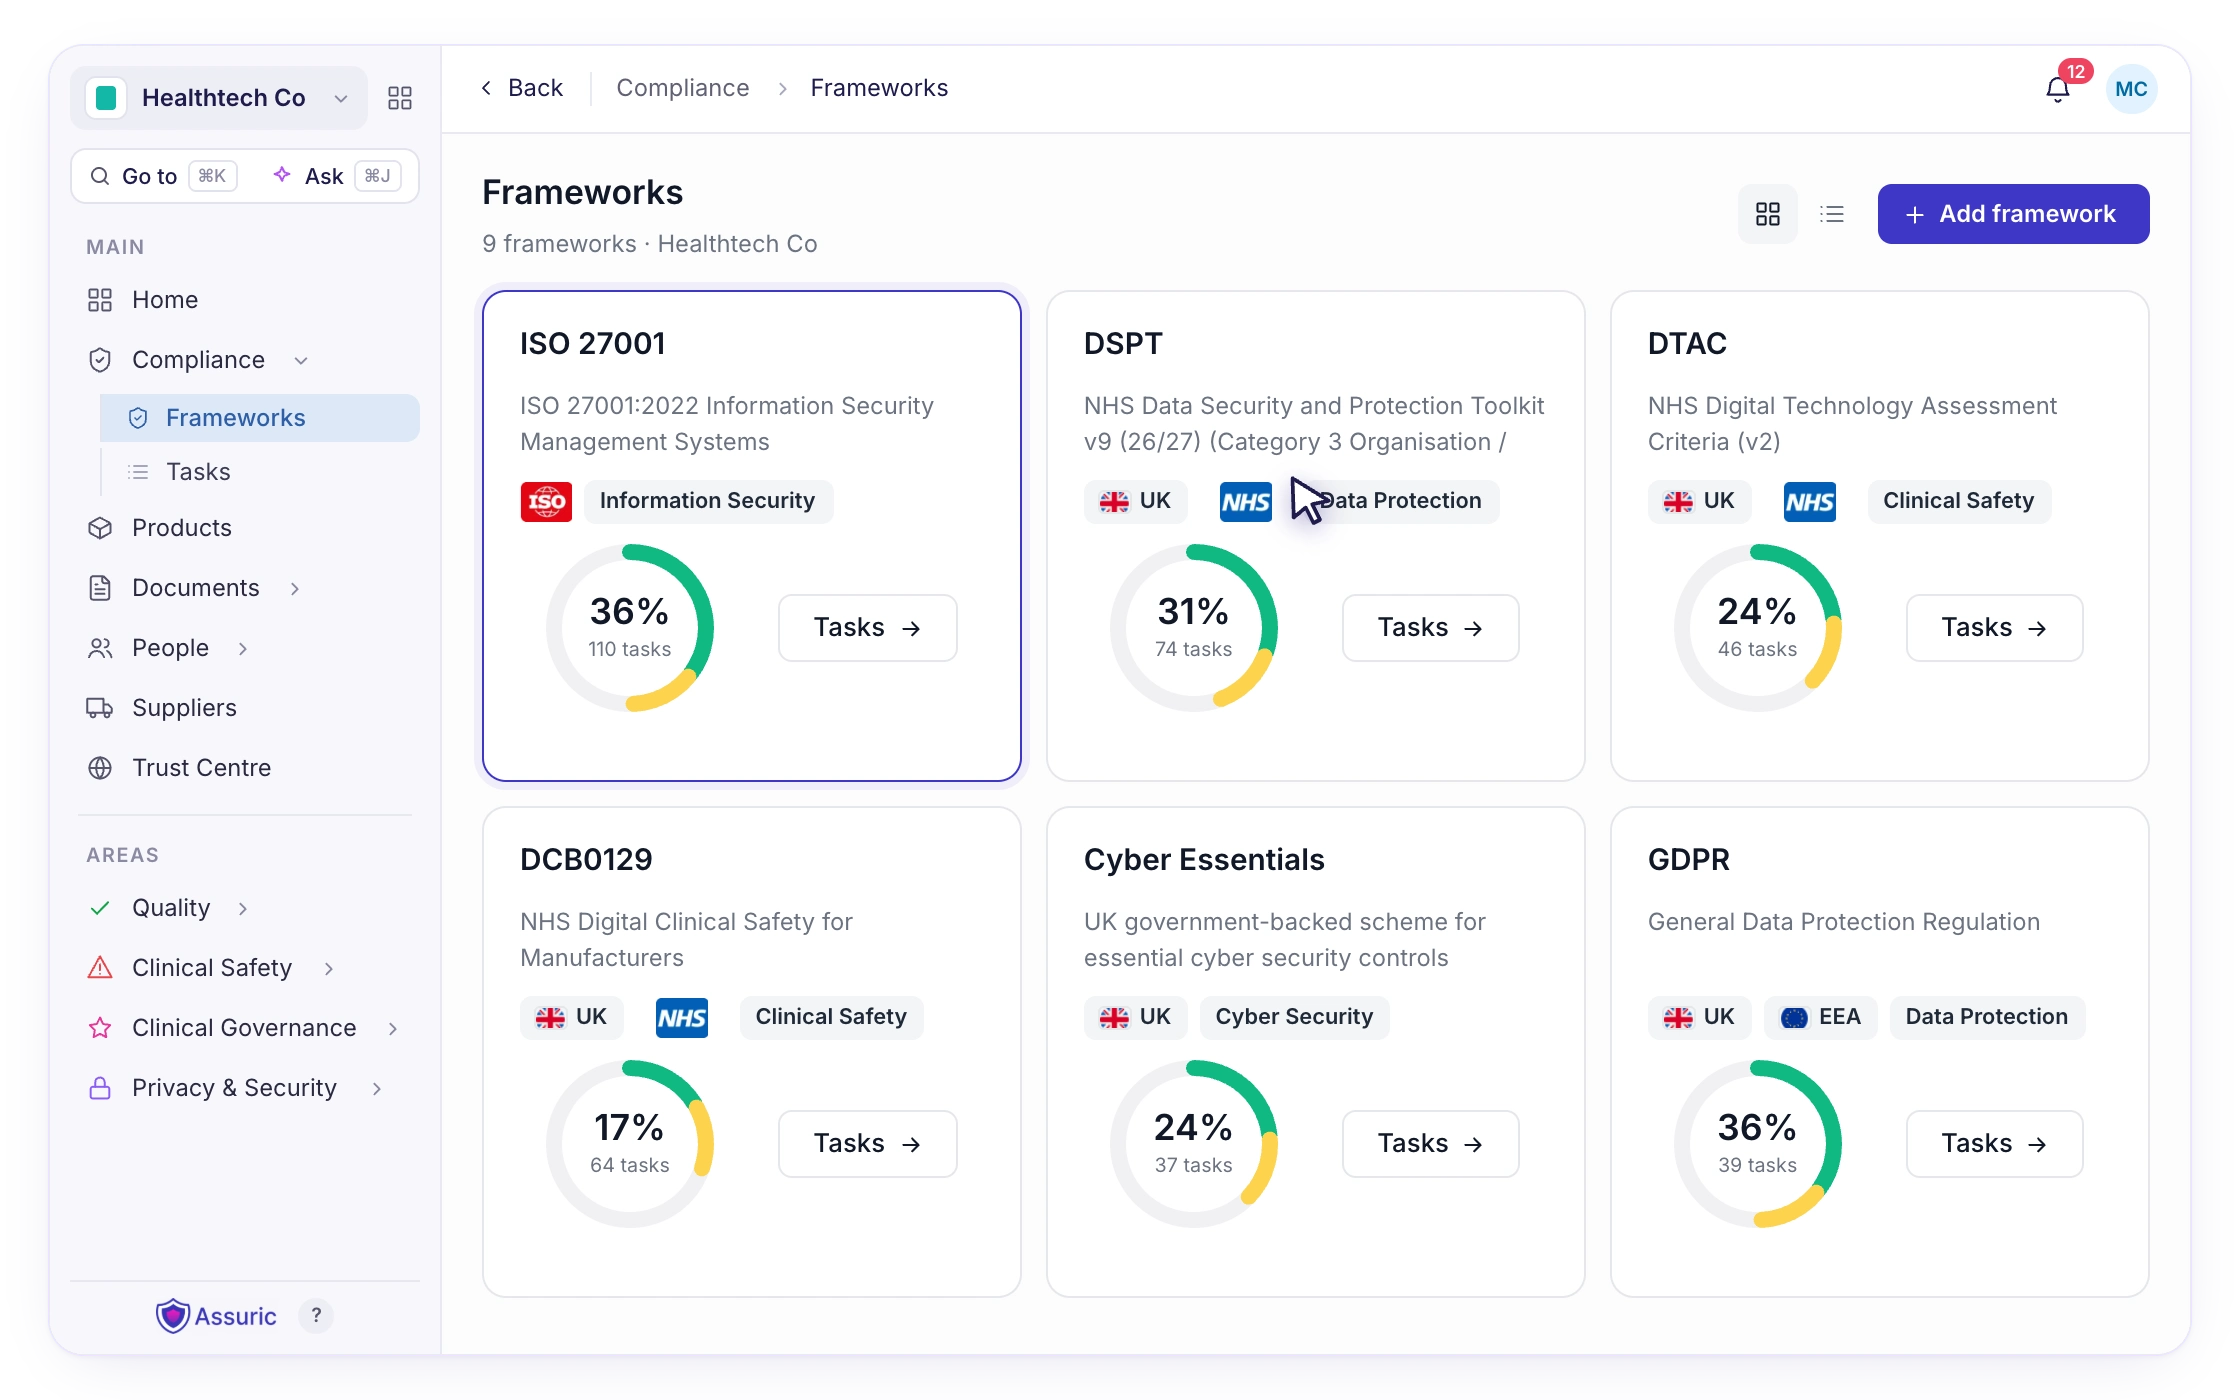
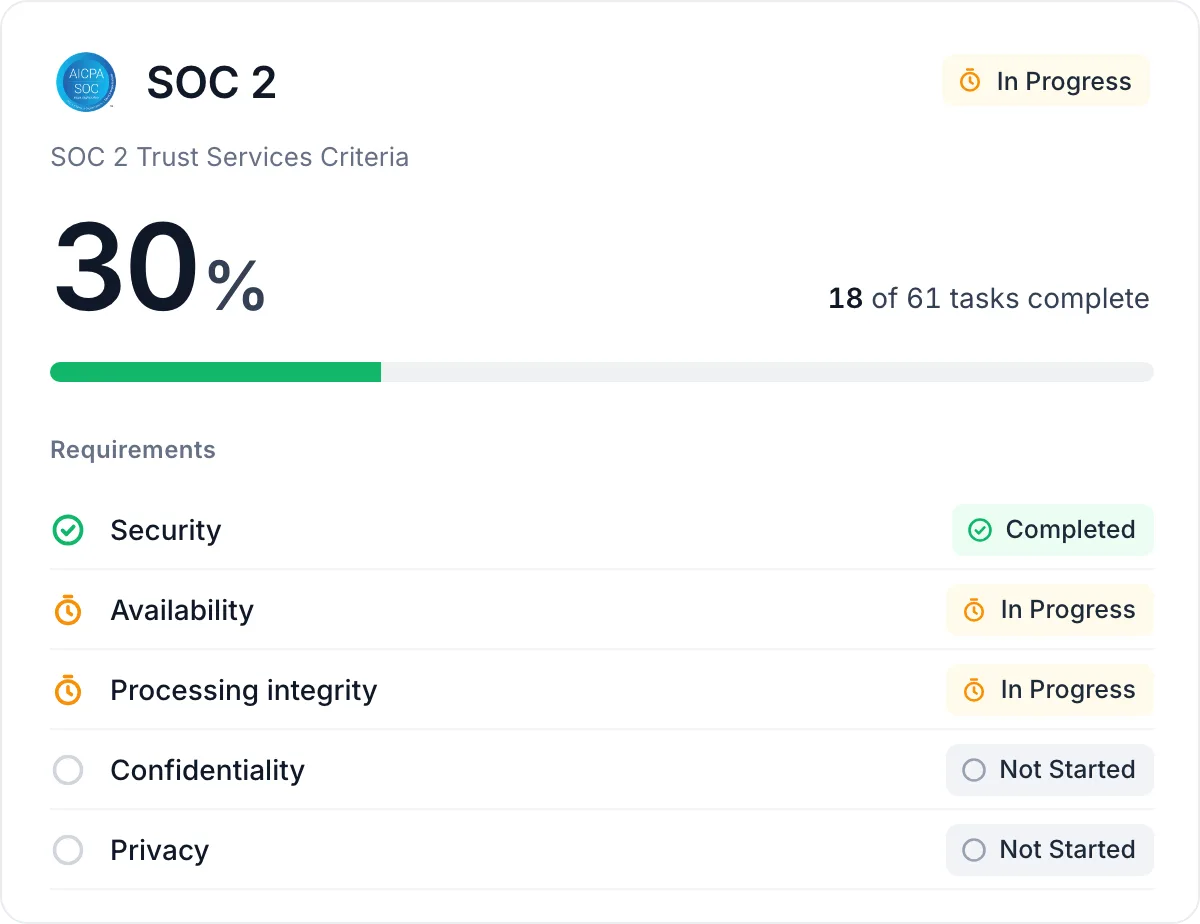
Automated compliance tracking
Easily fill any gaps, automate tasks, track compliance, and receive proactive alerts - ensuring requirements are met in record time.
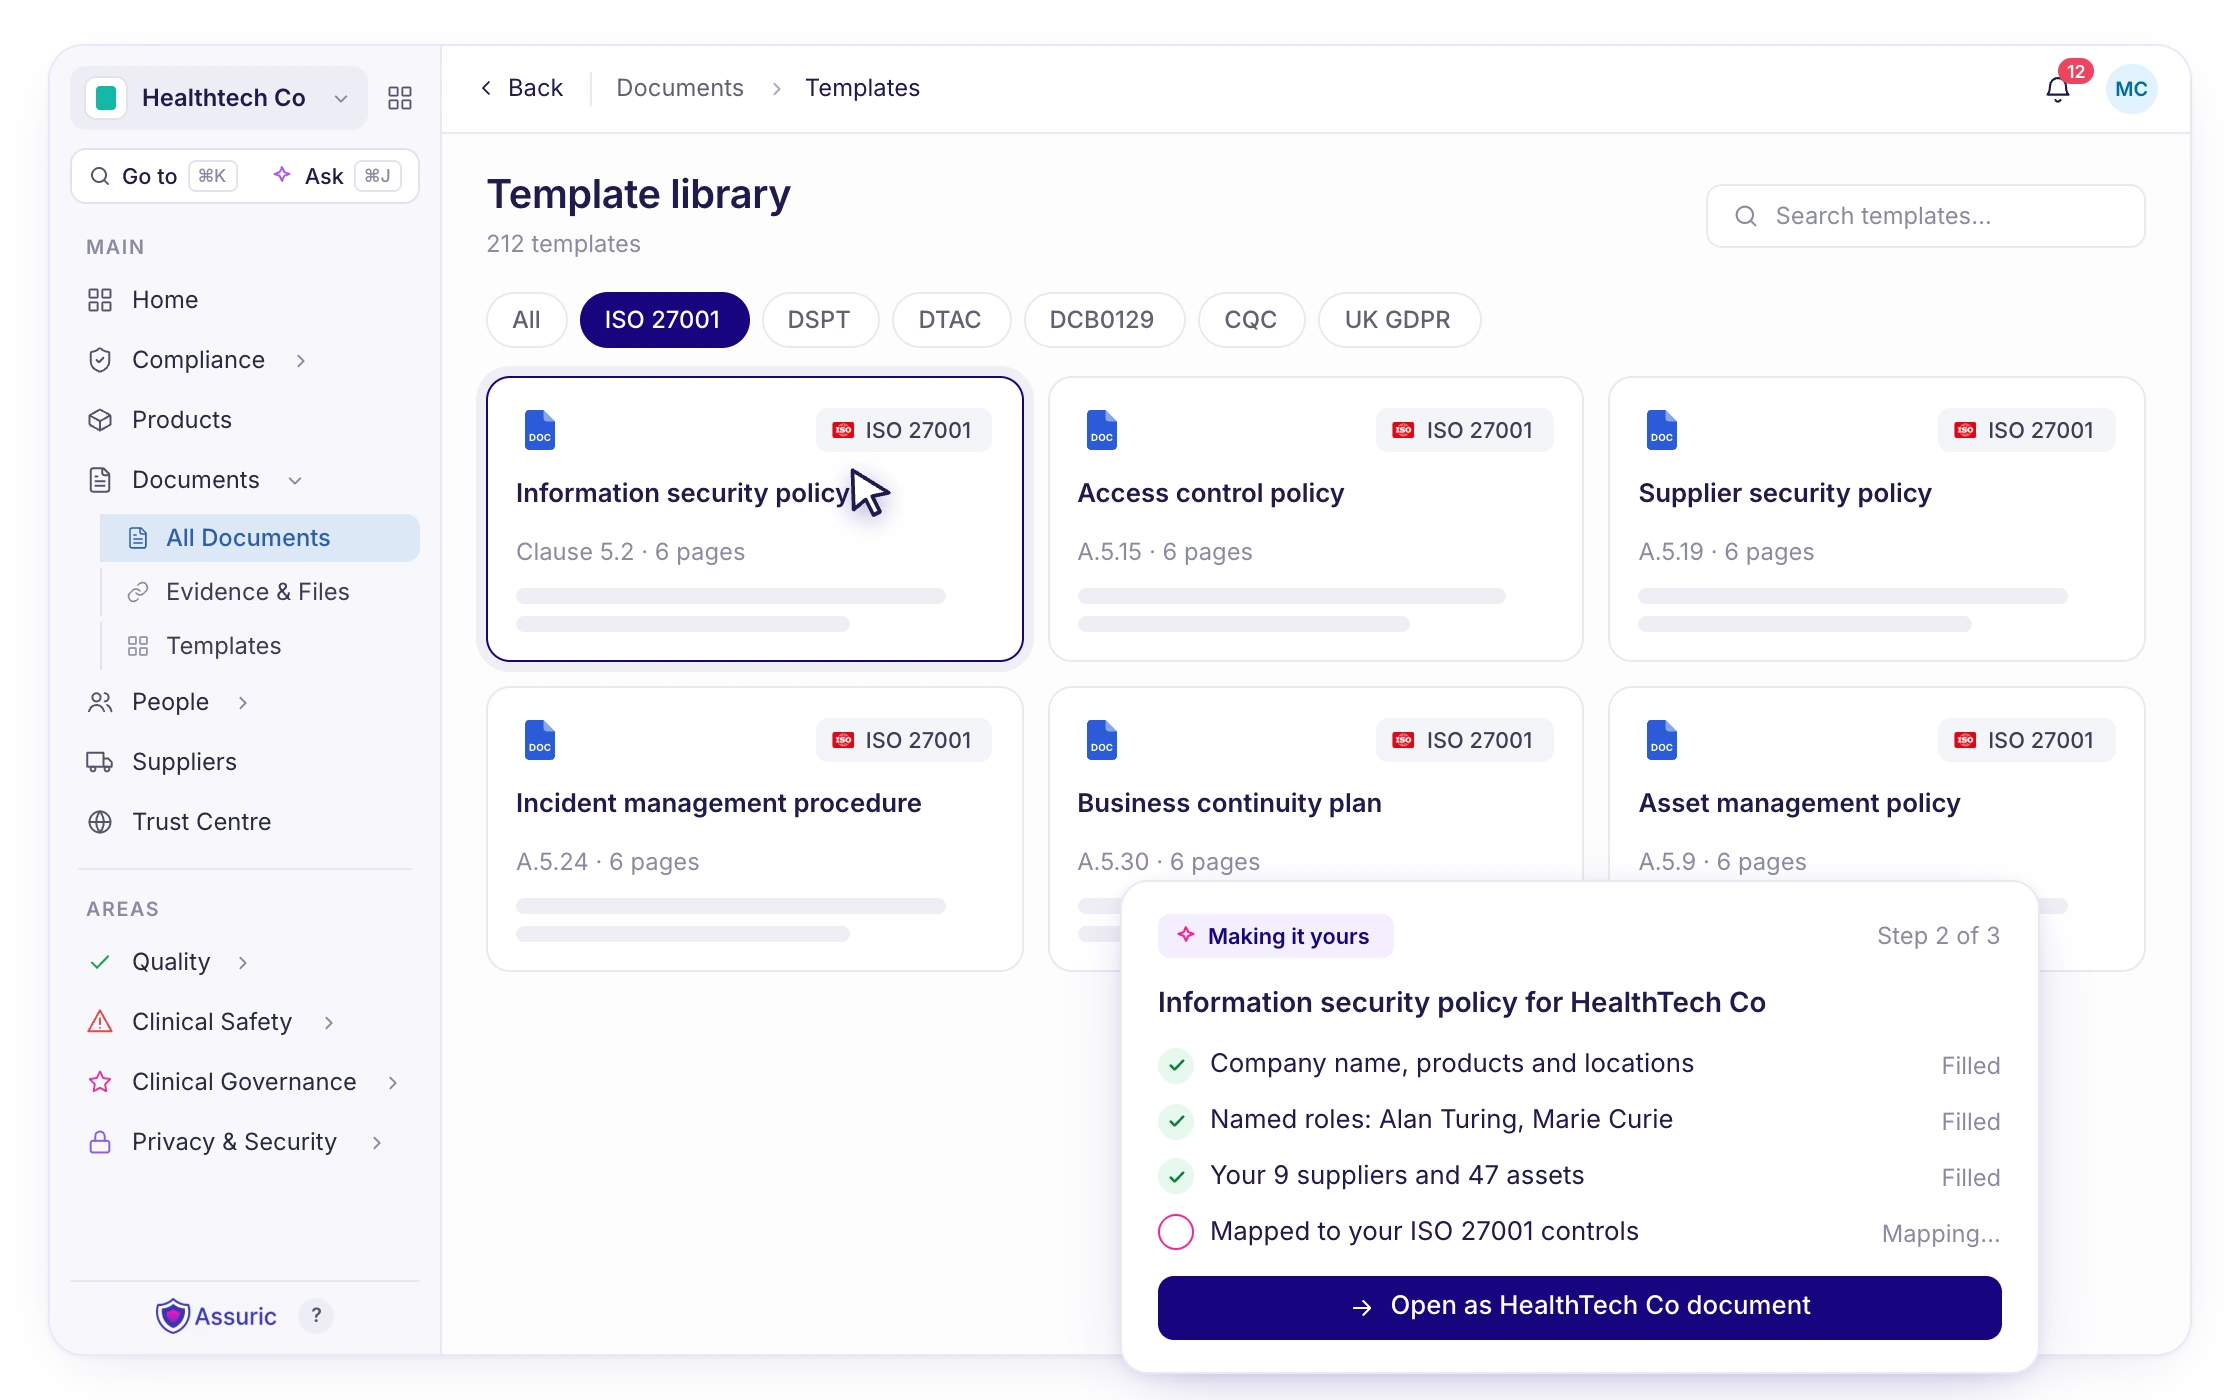
Document & policy management
Access our library of customisable templates, documents and procedures, including SOC 2 compliance policies, key procedures templates and more.

Third-party supplier management
Automate supplier security assessments and due diligence processes, including implementation and tracking of confidentiality agreements.
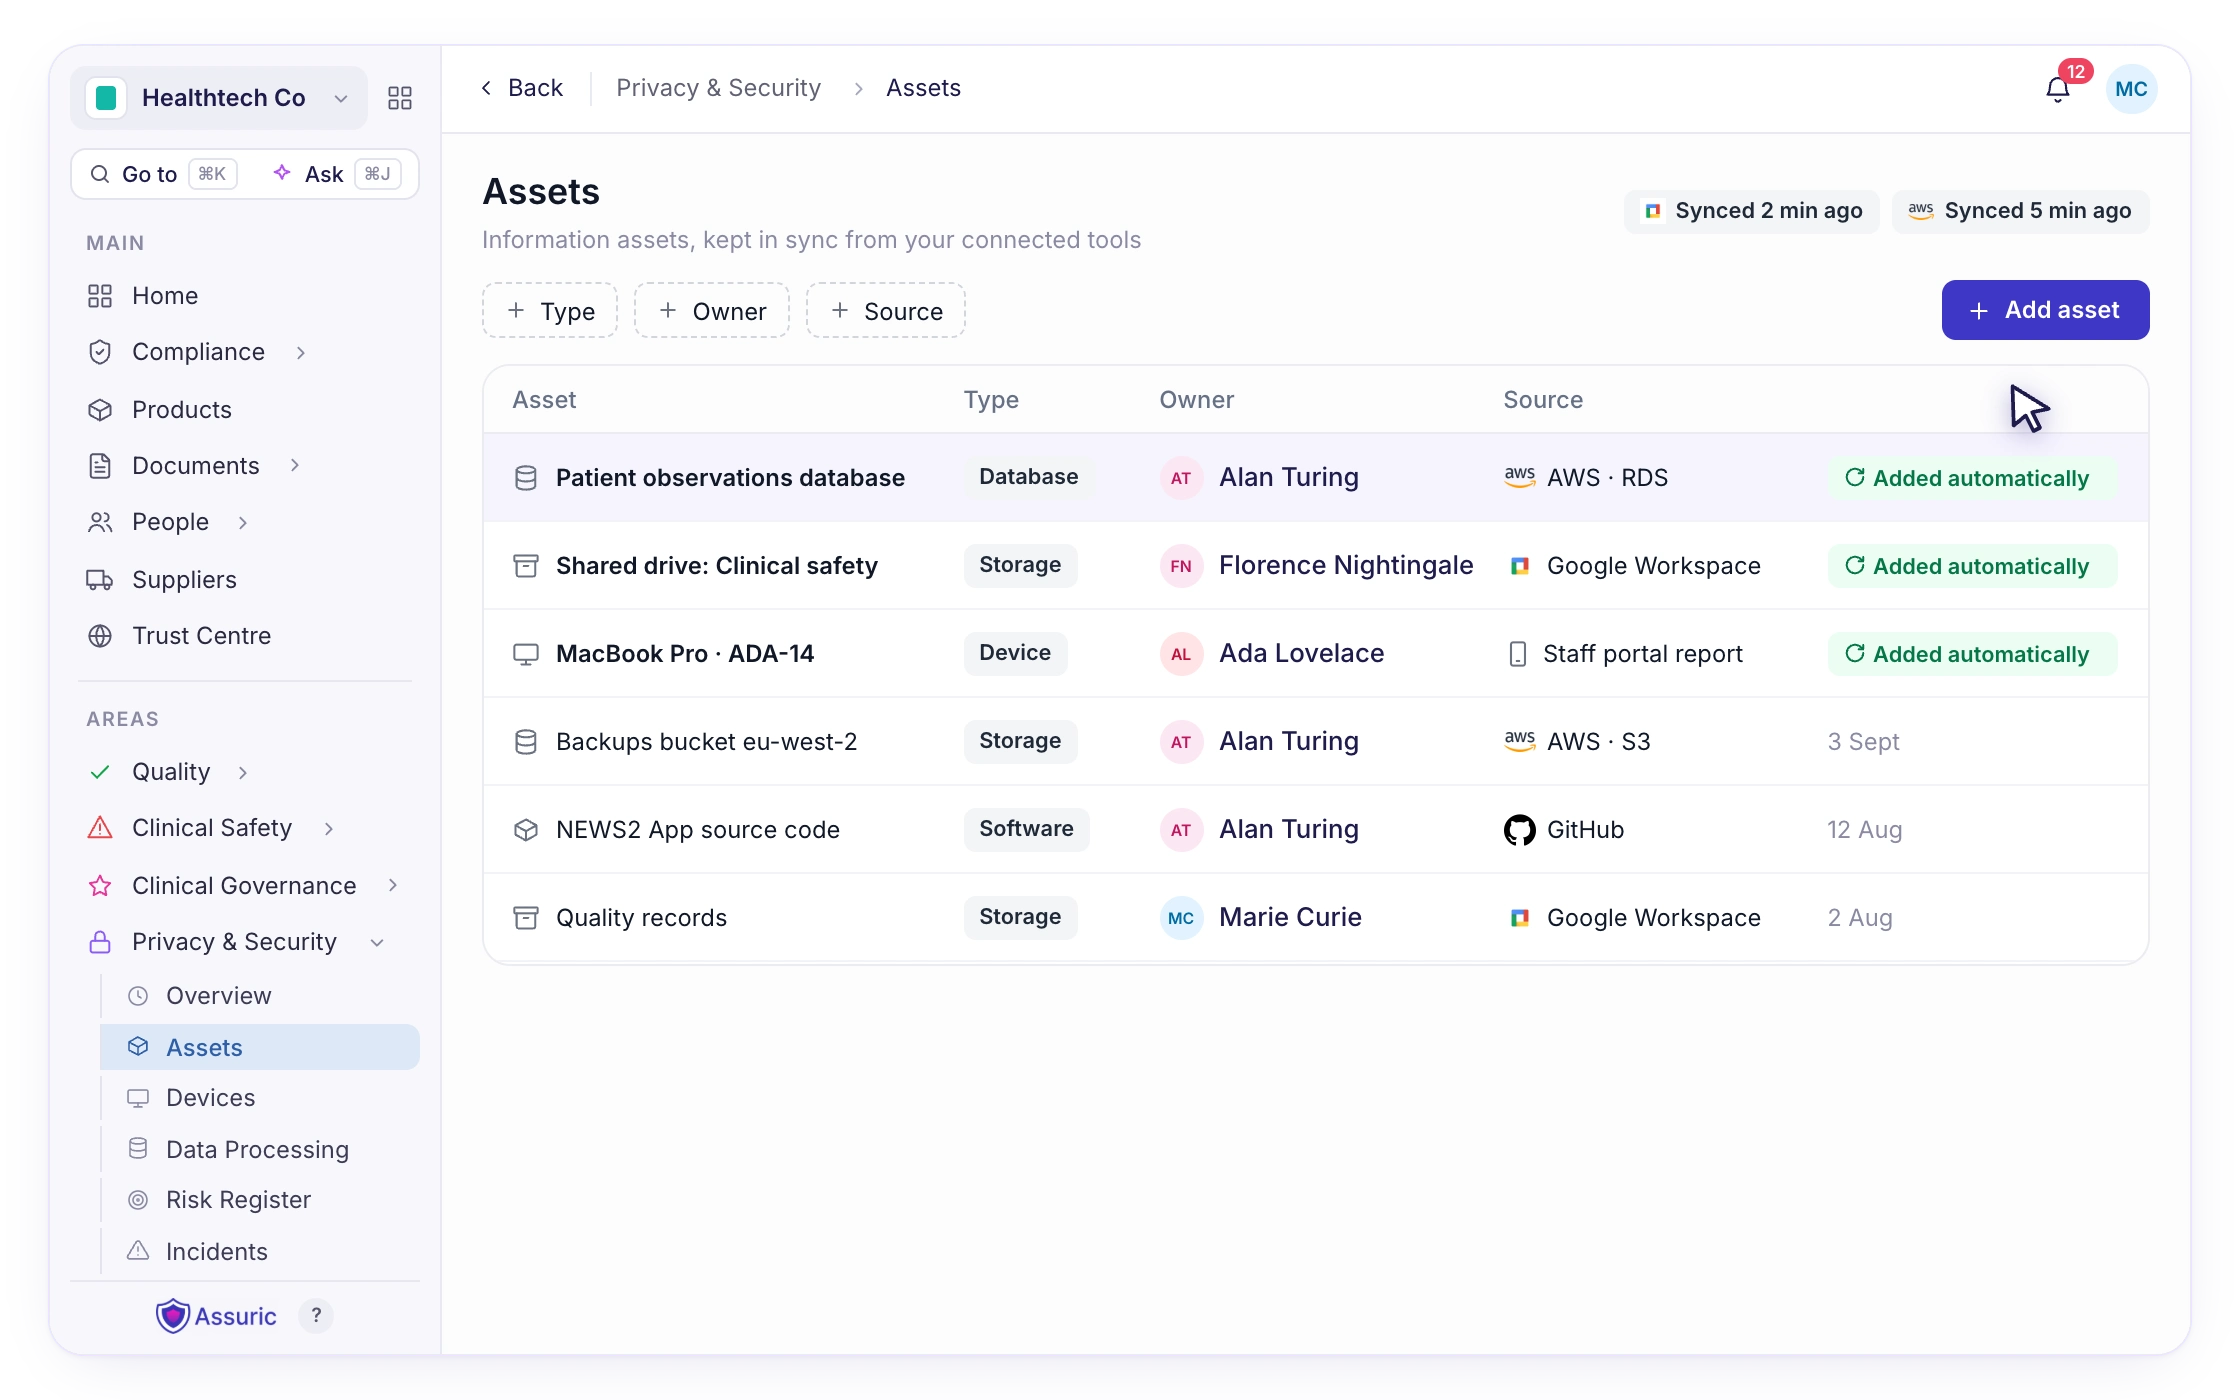
Asset & device management
Automatically identify and track all information assets including company devices, and link to suppliers and risks, maintaining auditable traceability.
Benefits
Assuric is the fastest way for digital health companies to get SOC 2 ready, automating compliance busywork and helping you build trust as you expand internationally.
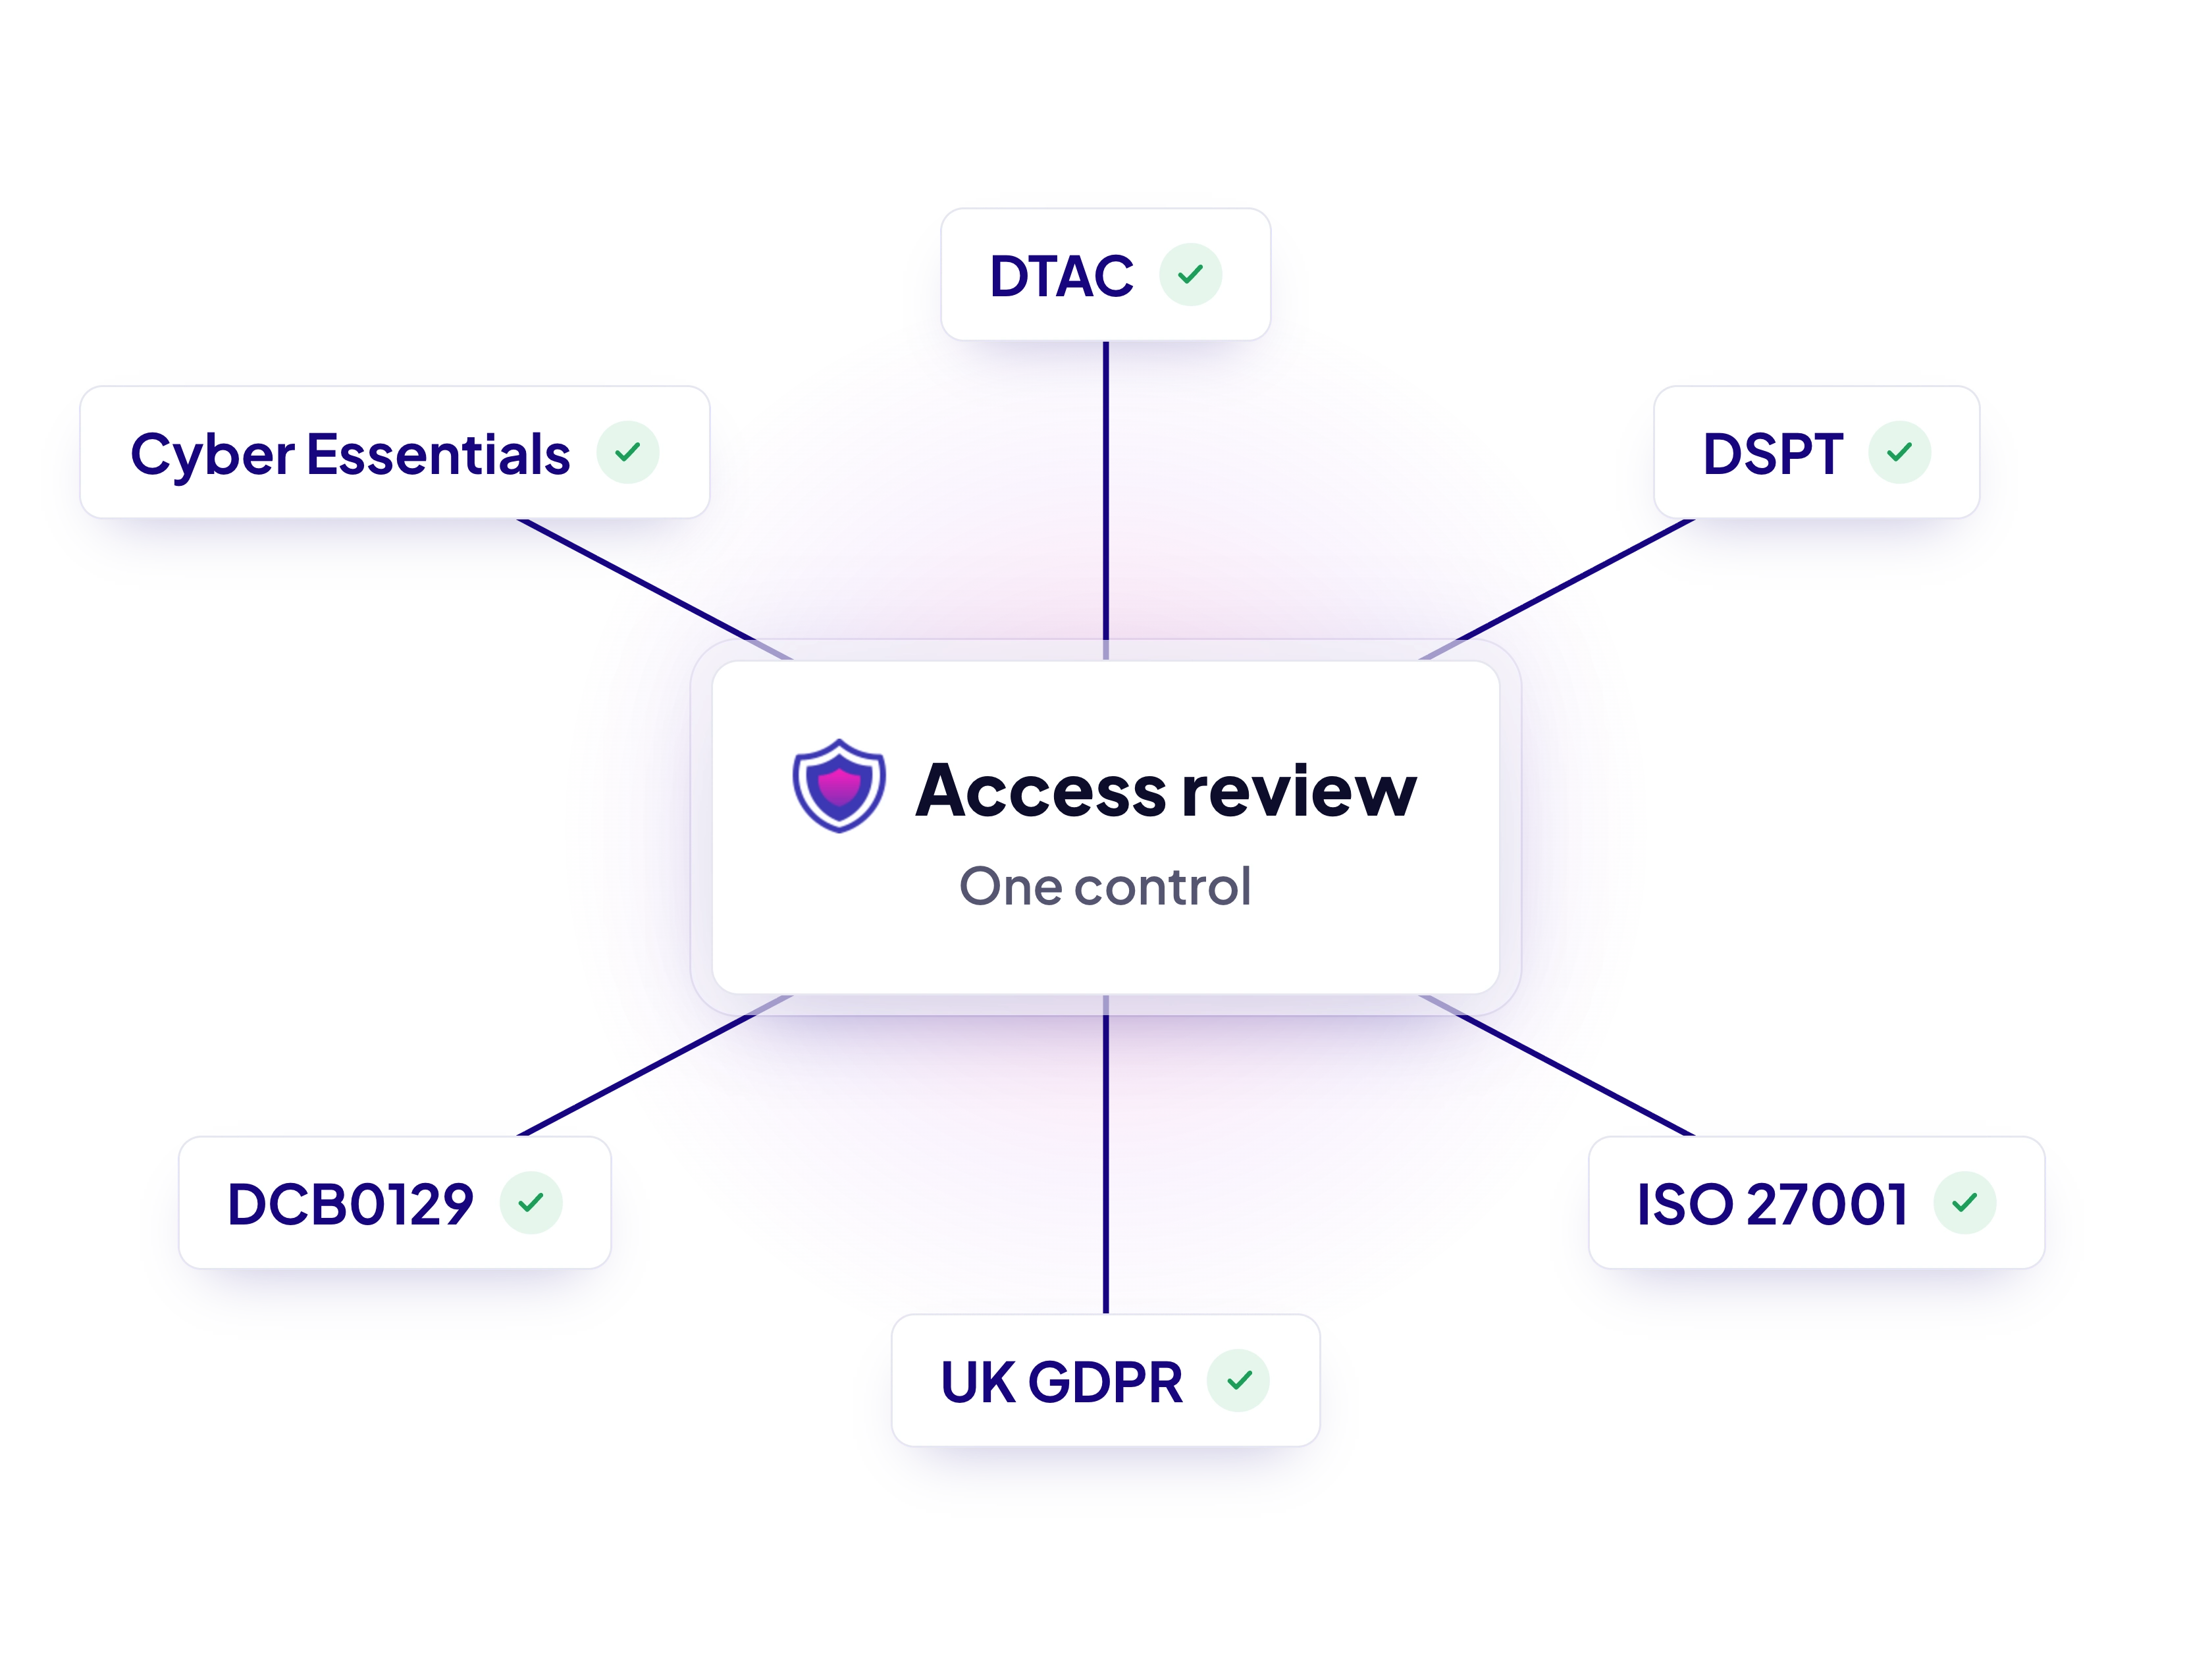
Use intelligent automation and AI to avoid duplication of work, using your HIPAA, Cyber Essentials, ISO 27001 documentation and evidence (and more) to fast track SOC 2.
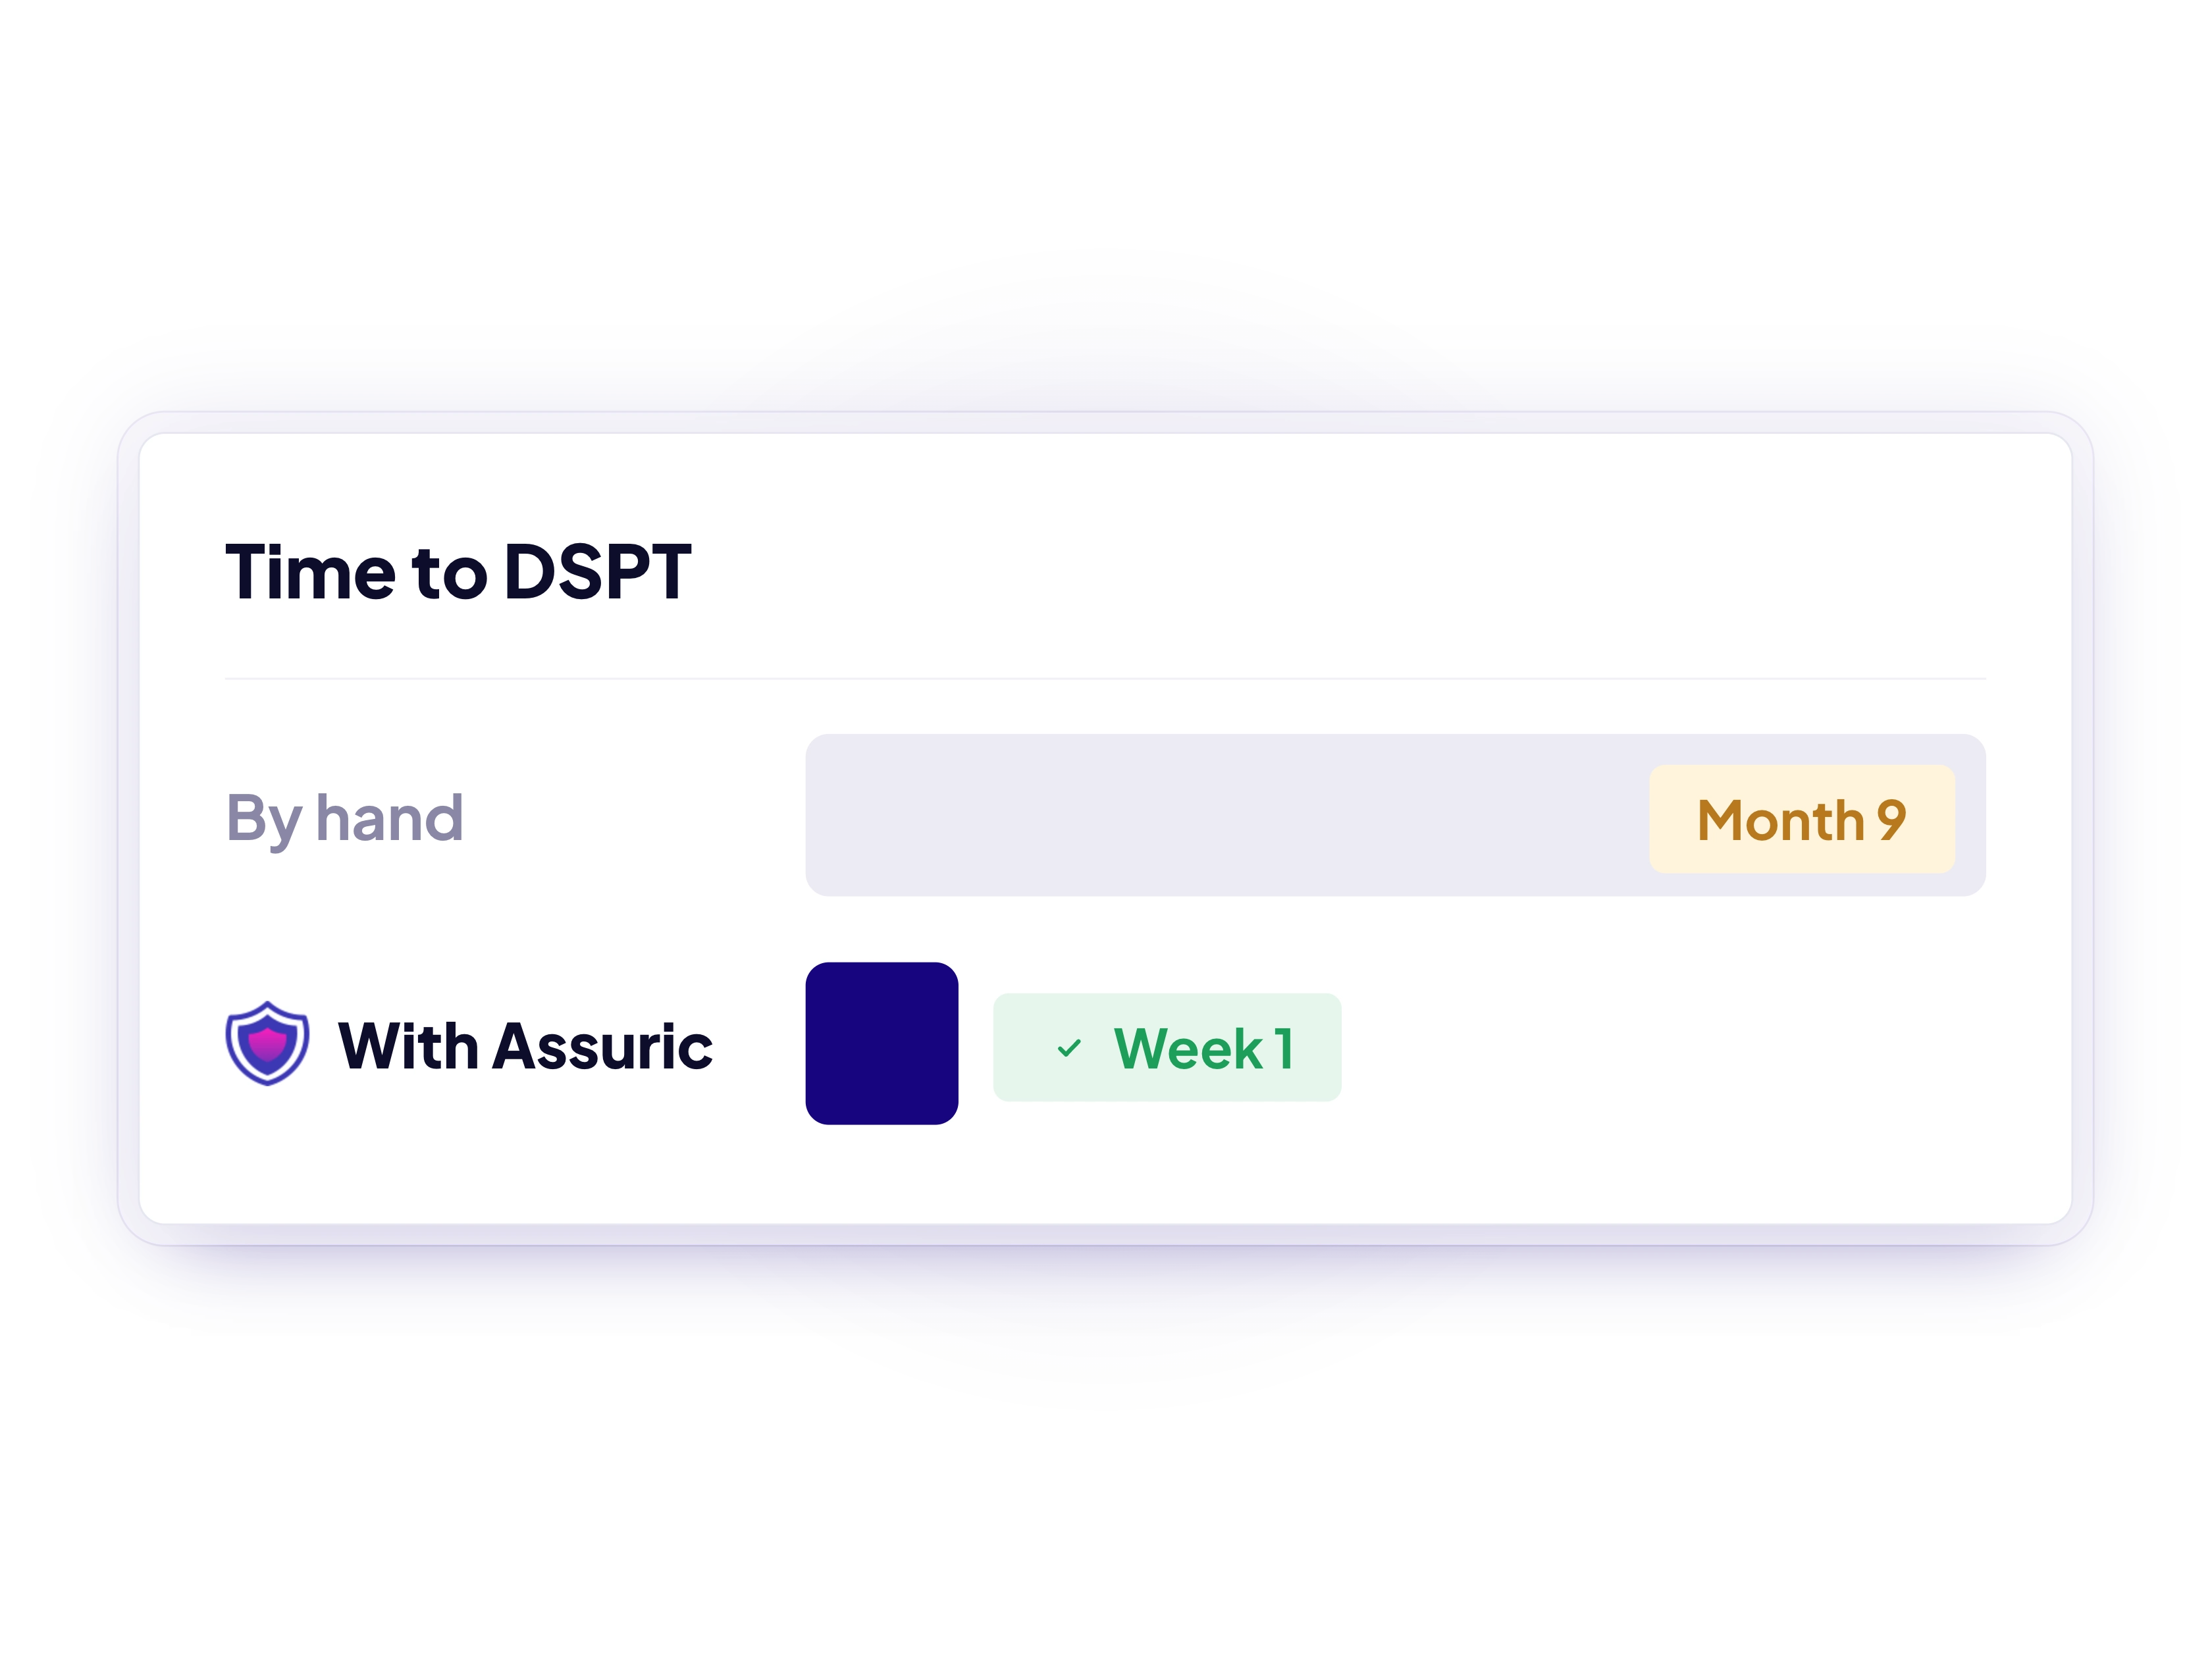
Automate internal audits, sail through external audits, and get your SOC 2 attestation report in record time.
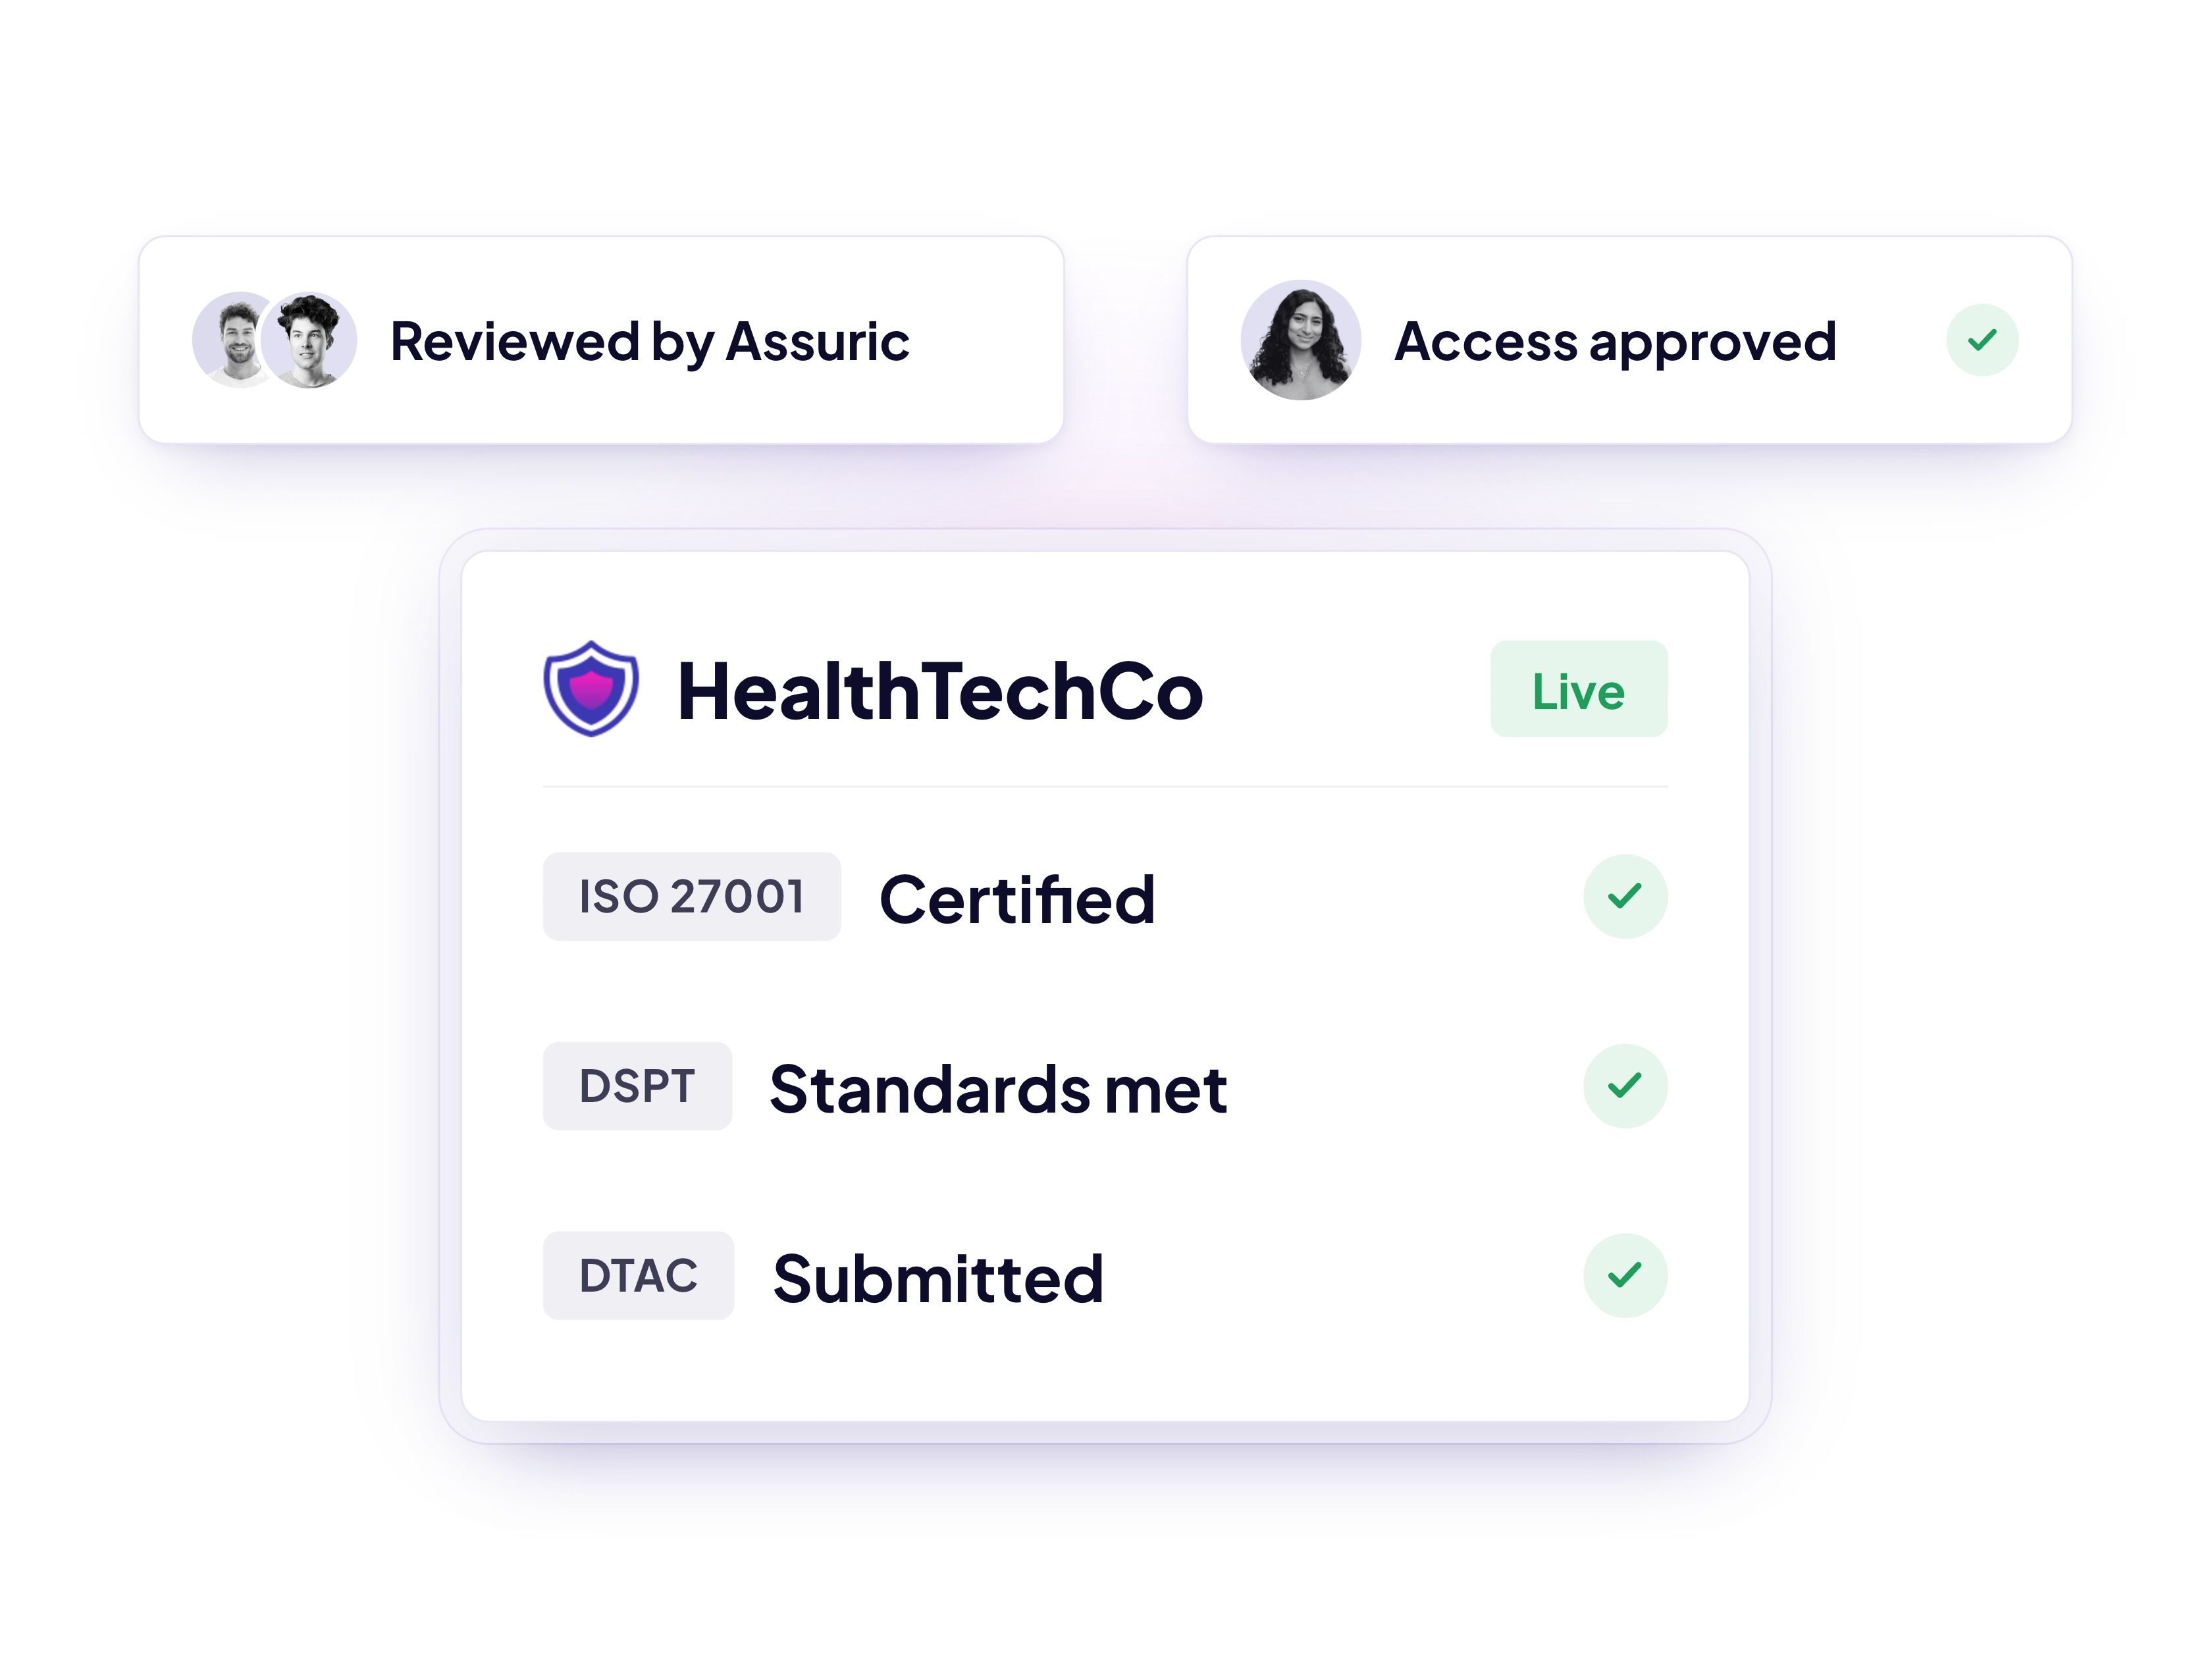
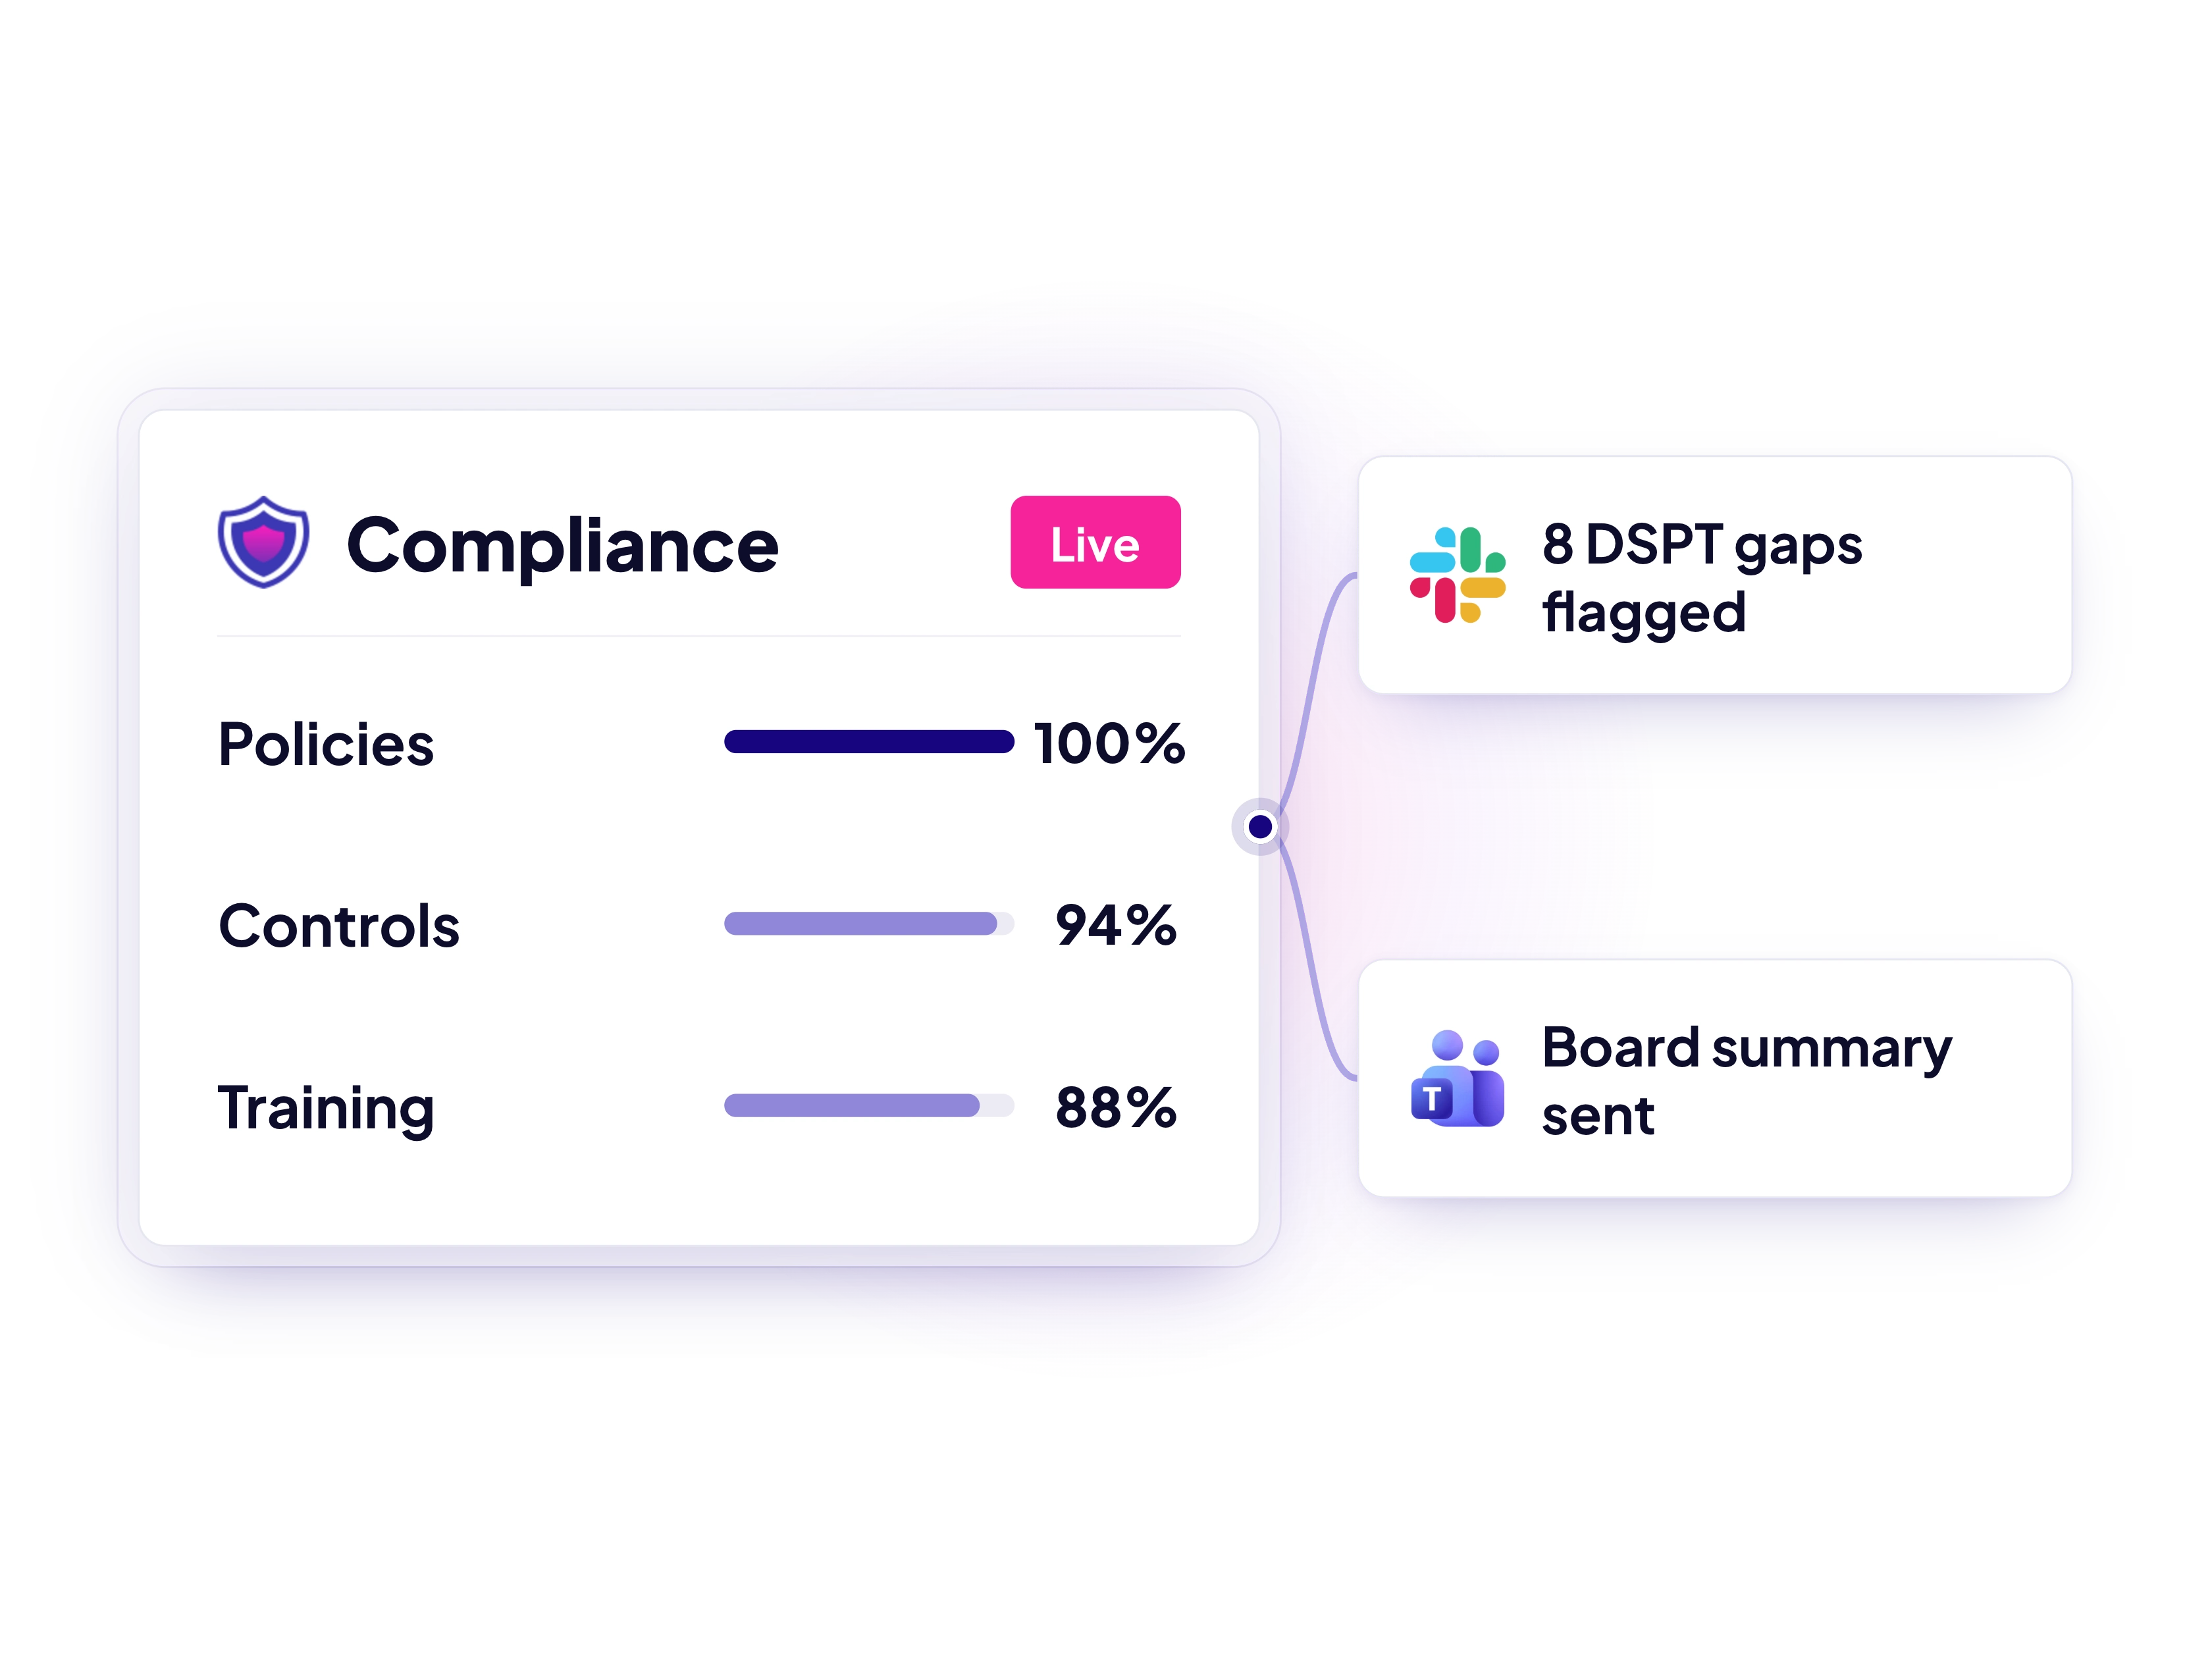
Keep compliance on track beyond your SOC 2 report. Assuric continuously monitors your systems and highlights issues that need your attention.
Frameworks
Overlapping requirements and evidence are mapped across frameworks automatically, so you never do the same work twice.

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”
Maks Kozarzewski
COO, VitVio

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”
Paul Llewellyn
CCIO, Accenture

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”
Katie Baker
Director UK & Ireland, Tandem
Get in touch if we haven't answered your question below, we are always happy to help!
SOC 2 is a widely recognised information security and data protection framework developed by the American Institute of Certified Public Accountants (AICPA). It provides a framework for designing, implementing and operating controls that protect customer data based on defined Trust Services Criteria.
SOC 2 is important because it helps organisations: Protect customer data from unauthorised access and security incidents. Demonstrate strong security and risk management practices. Provide assurance to customers, partners and stakeholders. Meet procurement and compliance expectations, particularly in the US market.
By achieving a SOC 2 report, organisations demonstrate a strong commitment to protecting customer data and operating effective, well governed security controls.
Customer Confidence: Compliance demonstrates that your organisation follows recognised controls to protect sensitive data.
Demonstrates Mature Security Governance: SOC 2 shows that your policies, processes, and controls are not ad hoc but formally designed, implemented, and operating effectively.
Process Transparency: Provides clear visibility into how data is handled, stored, and processed.
Supports compliance with other frameworks: SOC 2 aligns closely with other security standards, including HIPAA, ISO 27001, GDPR, and Cyber Essentials, making it a strong foundation for broader compliance efforts.
Business Growth Opportunities: Many US based enterprise customers require SOC 2 as part of vendor due diligence. Having a SOC 2 report ready can significantly reduce security questionnaires and sales cycle time.
The process includes a gap analysis, implementation of controls, internal audits, and an independent audit by a licensed CPA firm, which issues your SOC 2 attestation report.
Define Scope and Trust Services Criteria - Determine which systems, services and Trust Services Criteria will be included. From the criteria, Security is required and others are included based on your business needs.
Readiness Assessment and Gap Analysis - Compare current controls and practices against the selected criteria to identify missing or weak controls. Plan remediation and documentation.
Implement Controls and Document Policies - Put in place the technical and procedural controls needed and formalise policies and procedures. Begin collecting evidence of how controls operate in practice.
Observation Period (for Type II only) - For SOC 2 Type II reports, operate and monitor controls over a defined period (typically 3-12 months) to produce evidence of their ongoing effectiveness. Type I does not require this period and focuses on design.
Audit and Evidence Review - A CPA firm or agency accredited by the AICPA conducts the audit, reviews collected evidence, tests controls, and may interview personnel to ensure documentation aligns with practice.
Report Issuance - The auditor finalises the SOC 2 report, which includes the management assertion, system description and auditor's opinion. This report is shared with stakeholders as proof of compliance.
Use the Assuric platform to achieve all of the above in record time.
A SOC 2 Type I report looks at whether your controls are designed properly at a single point in time. A Type II report also tests whether those controls worked in practice over an observation period. Some teams start with Type I, then move to Type II once their controls have been running for a while.
Although ISO 27001 is widely recognised as a leading standard for information security, some enterprise customers (particularly in the US) may still require SOC 2. SOC 2 provides an independent assessment of operational controls and data protection practices. This is why larger tech companies often aim to have both ISO 27001 and SOC 2 compliance.
No, SOC 2 is not legally required. It is a voluntary compliance framework designed to demonstrate that an organisation has effective controls to protect customer data. However, it can be requested by customers, particularly in the US.
Yes. Assuric helps you implement and track the SOC 2 security controls you need, including encryption, backups, access controls, screen locking and more.
Assuric gives you a risk library to start from. You build mitigation plans and track each risk through treatment, so you stay in line with SOC 2 requirements.
Assuric gives you SOC 2 policy templates, control tracking and evidence in one platform. You can reuse documentation and evidence from frameworks you already hold, such as ISO 27001, Cyber Essentials and the NHS DSPT, so you're not starting from scratch. When it's time for your audit, your auditor can review everything in one place.
Book a call and we'll plan your route to a SOC 2 report alongside your NHS frameworks.