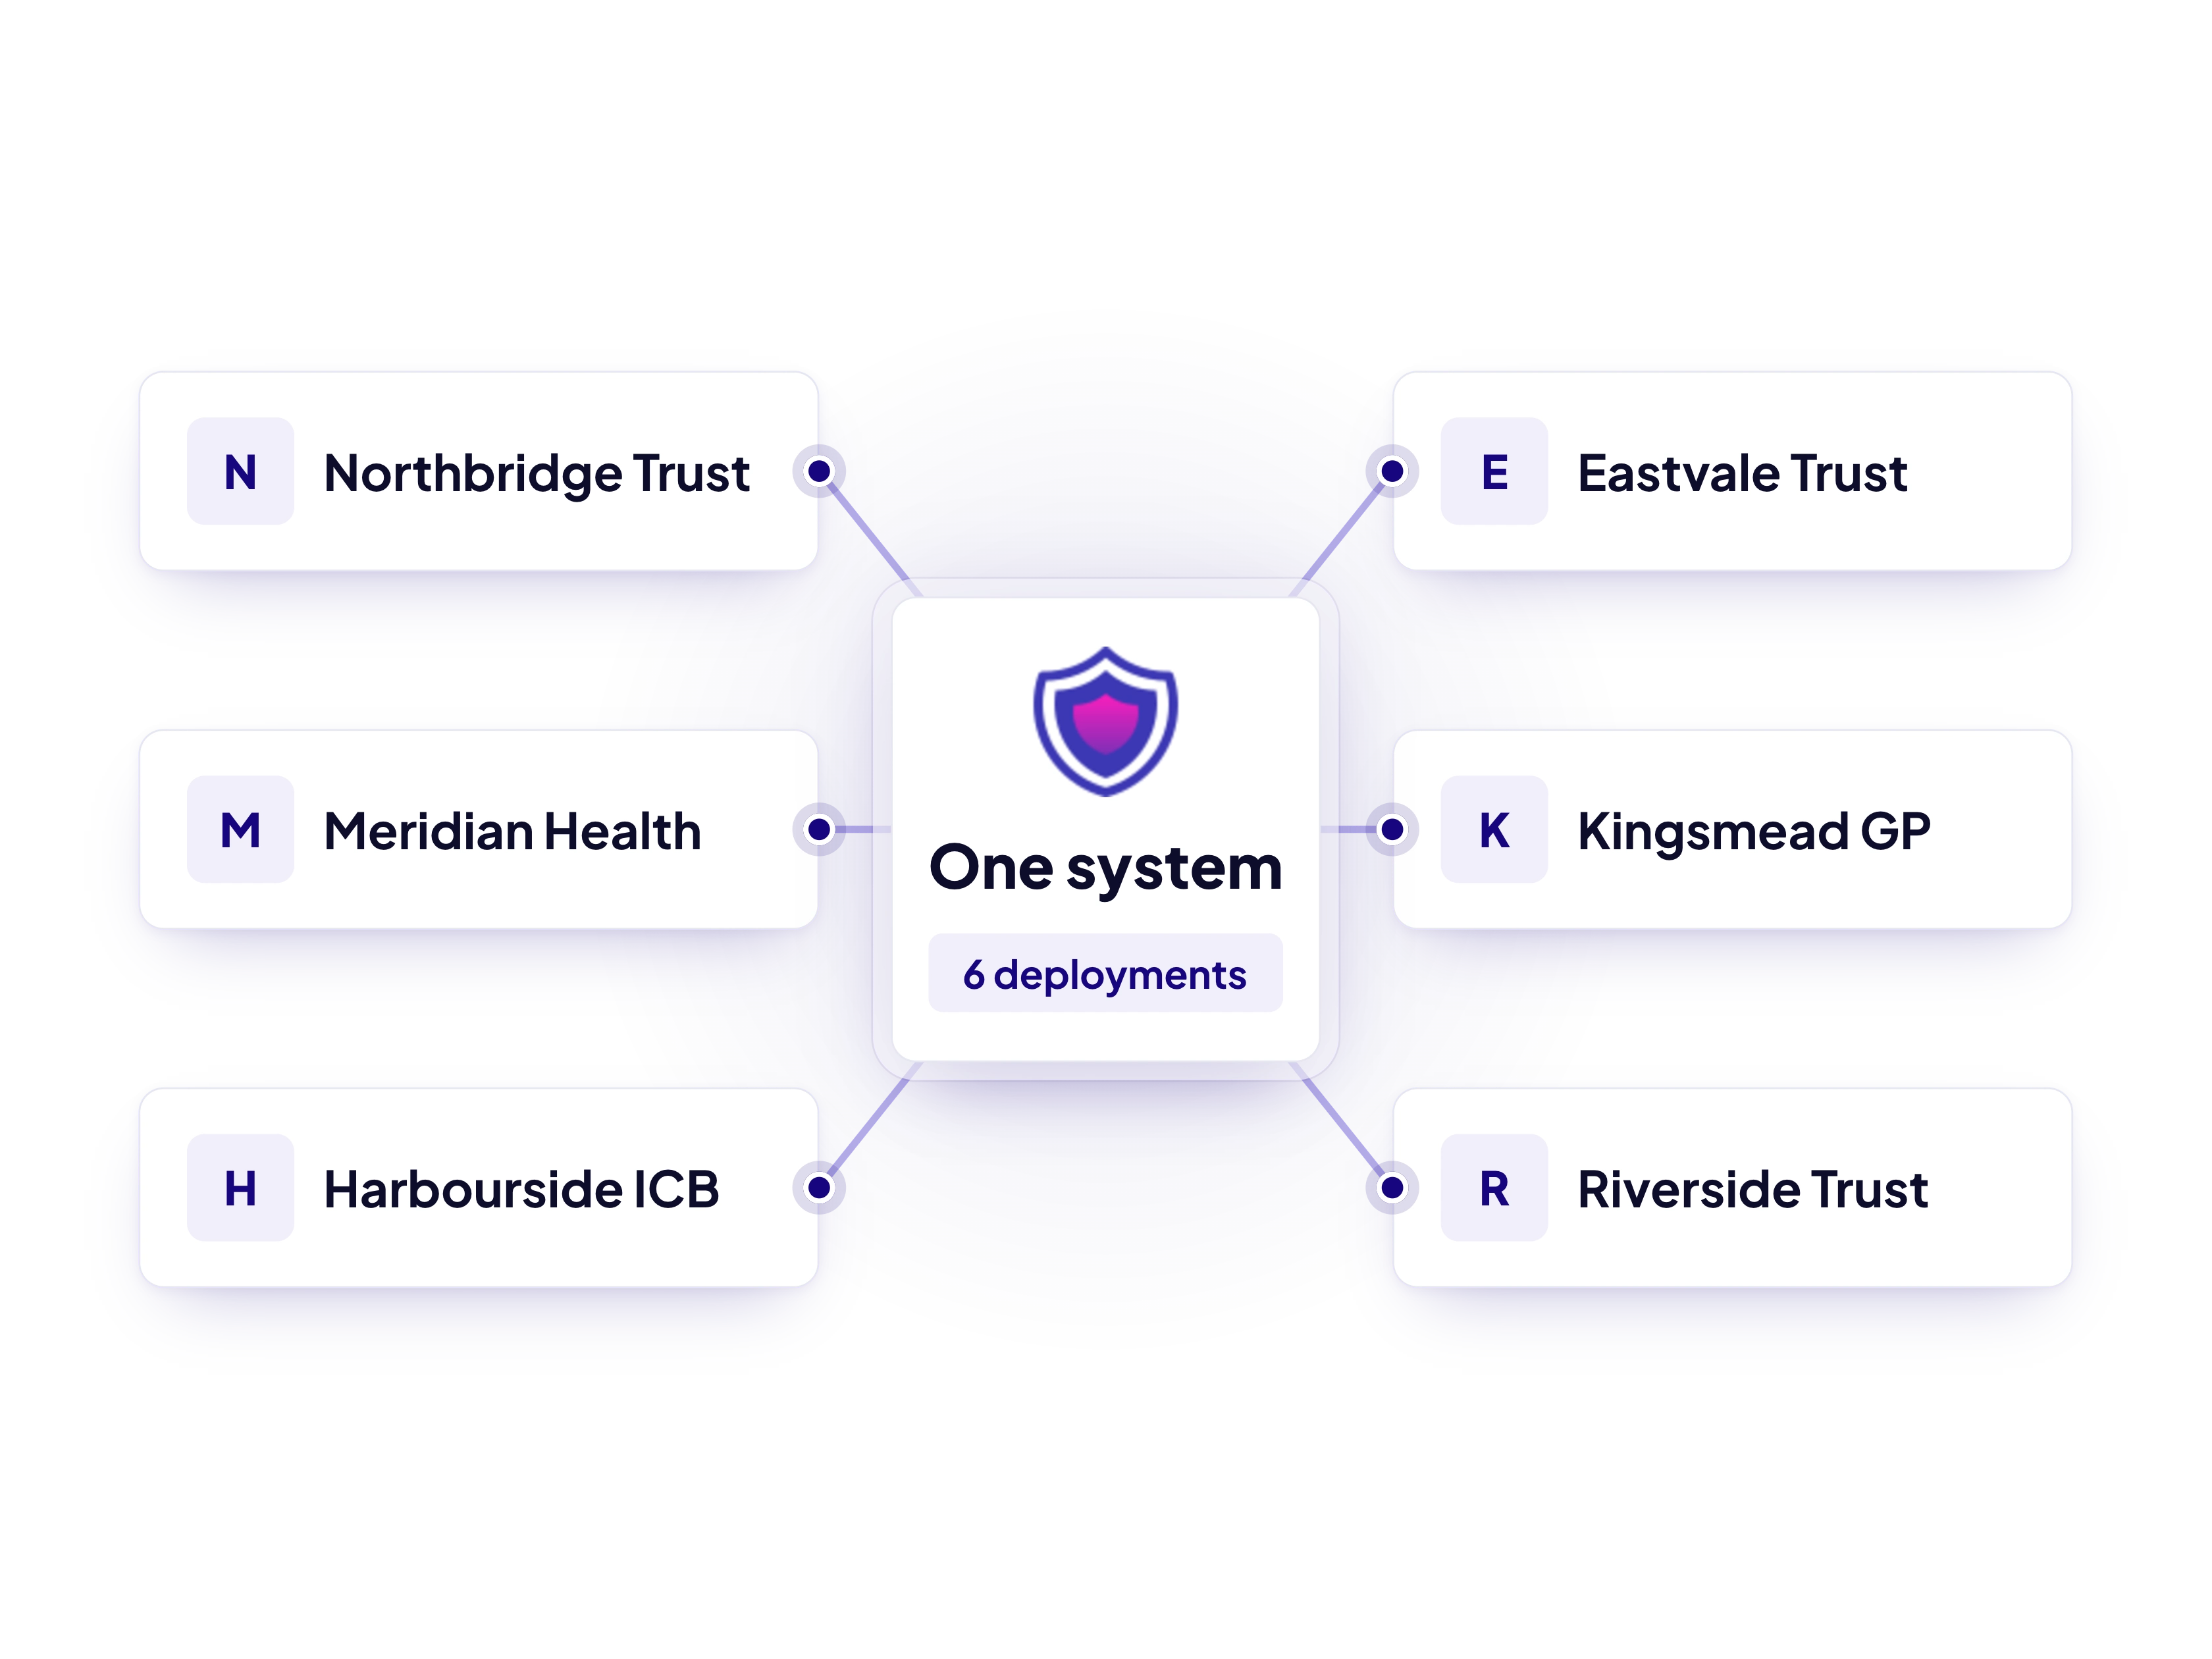
Every supplier, system and deployment in one view
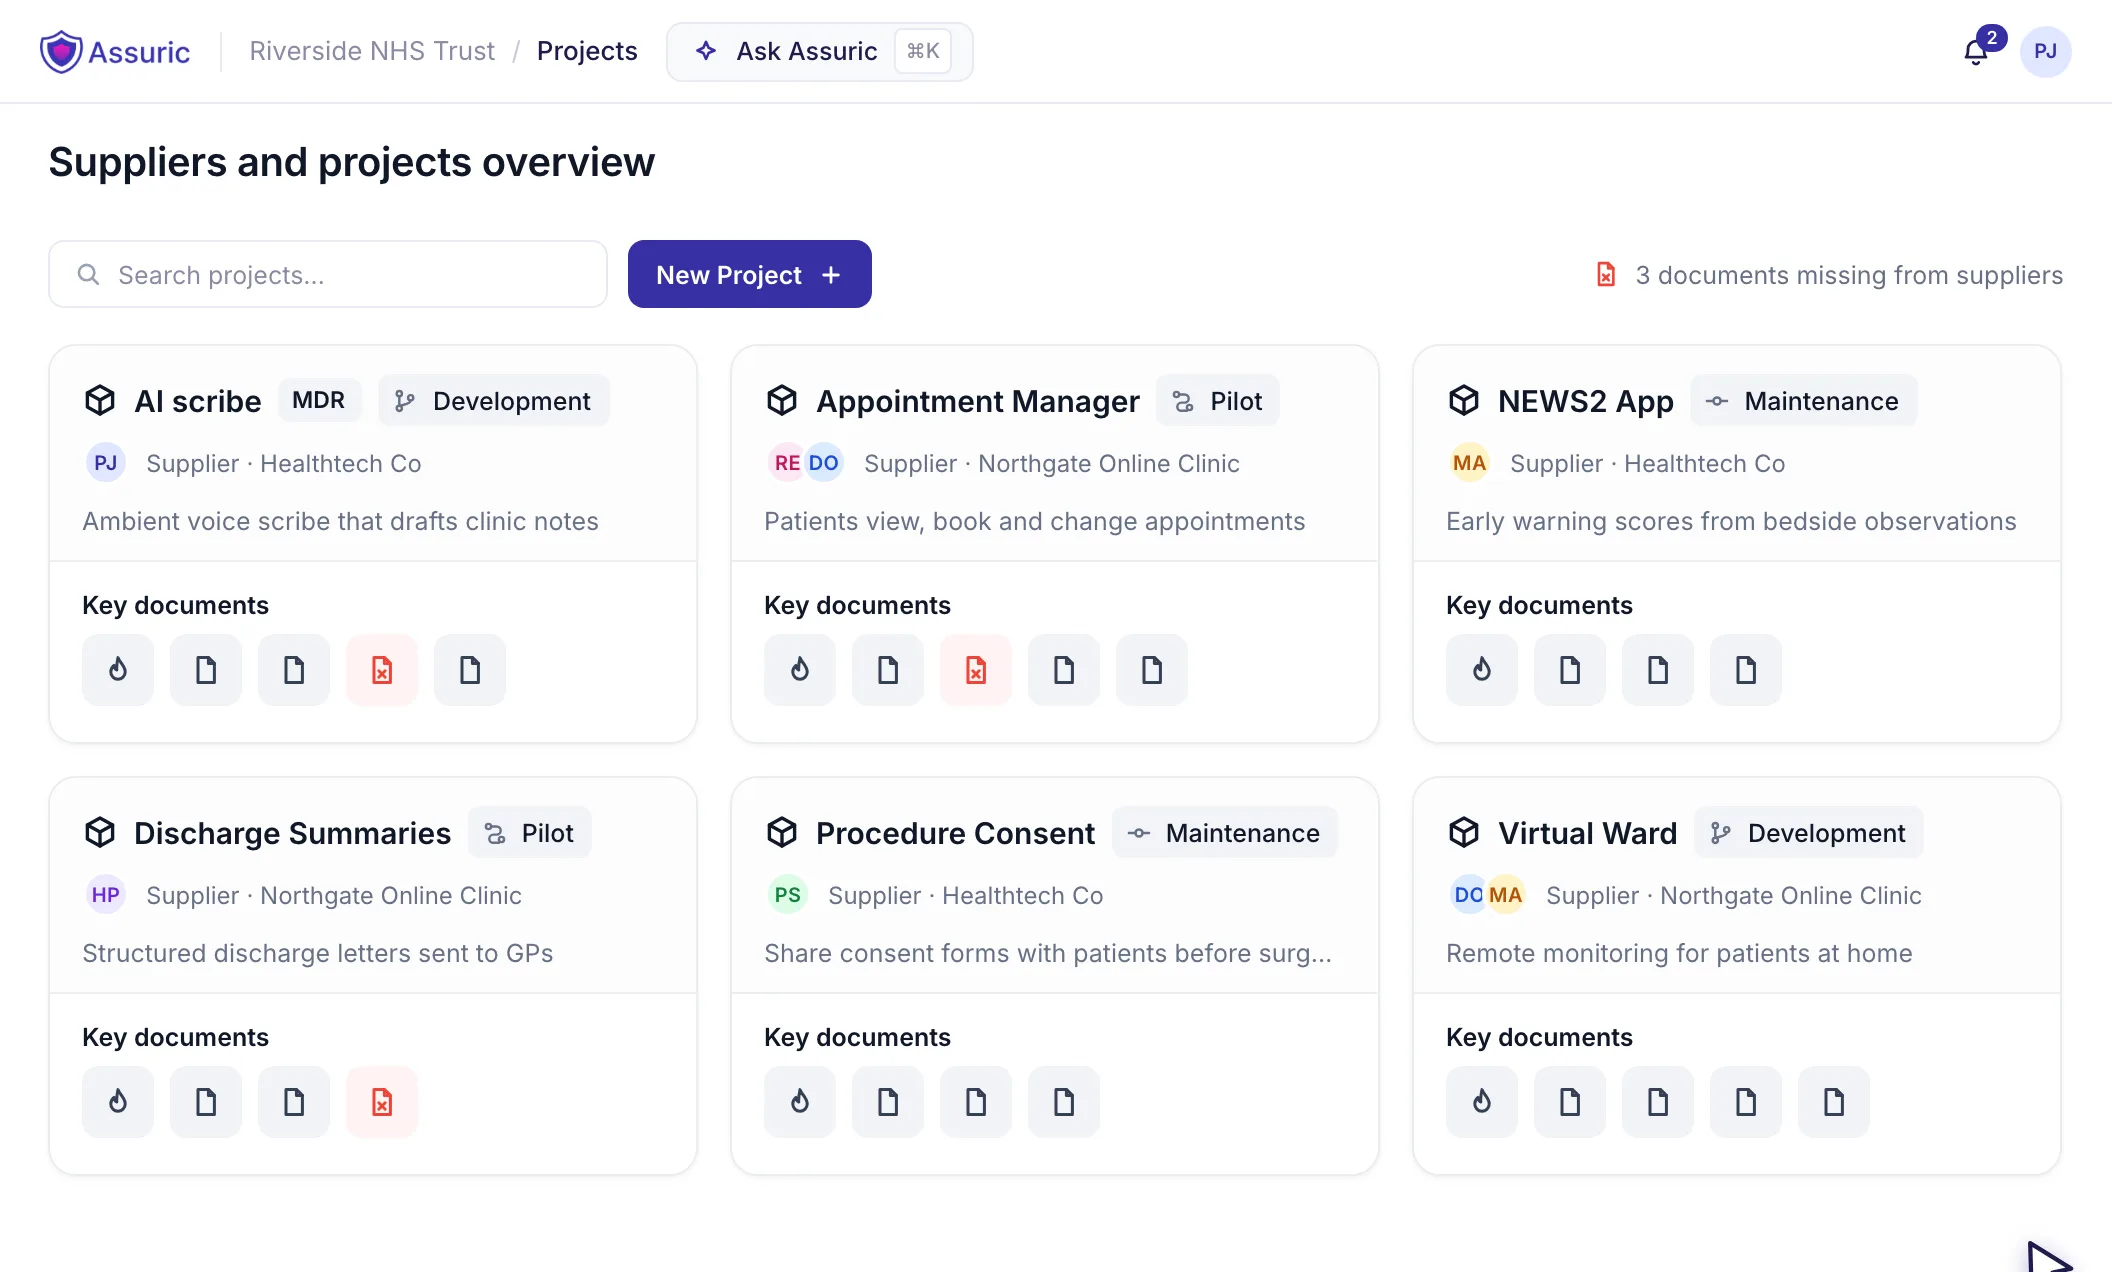
See every supplier, system and deployment with its hazards, owners, evidence and status, so your team spots issues early, reduces risk and always knows where attention is needed.
Clinical safety, information governance, DTAC assurance and CQC compliance in one system, built by clinical safety, digital health and clinical governance experts.
Trusted byhealthcare organisations


Benefits
See every supplier, system and deployment with its hazards, owners, evidence and status, so your team spots issues early, reduces risk and always knows where attention is needed.
Collect suppliers’ DTAC responses, DCB0129 documents and information governance evidence in one place, review them against a consistent standard, and close gaps early so deployments are not held up.
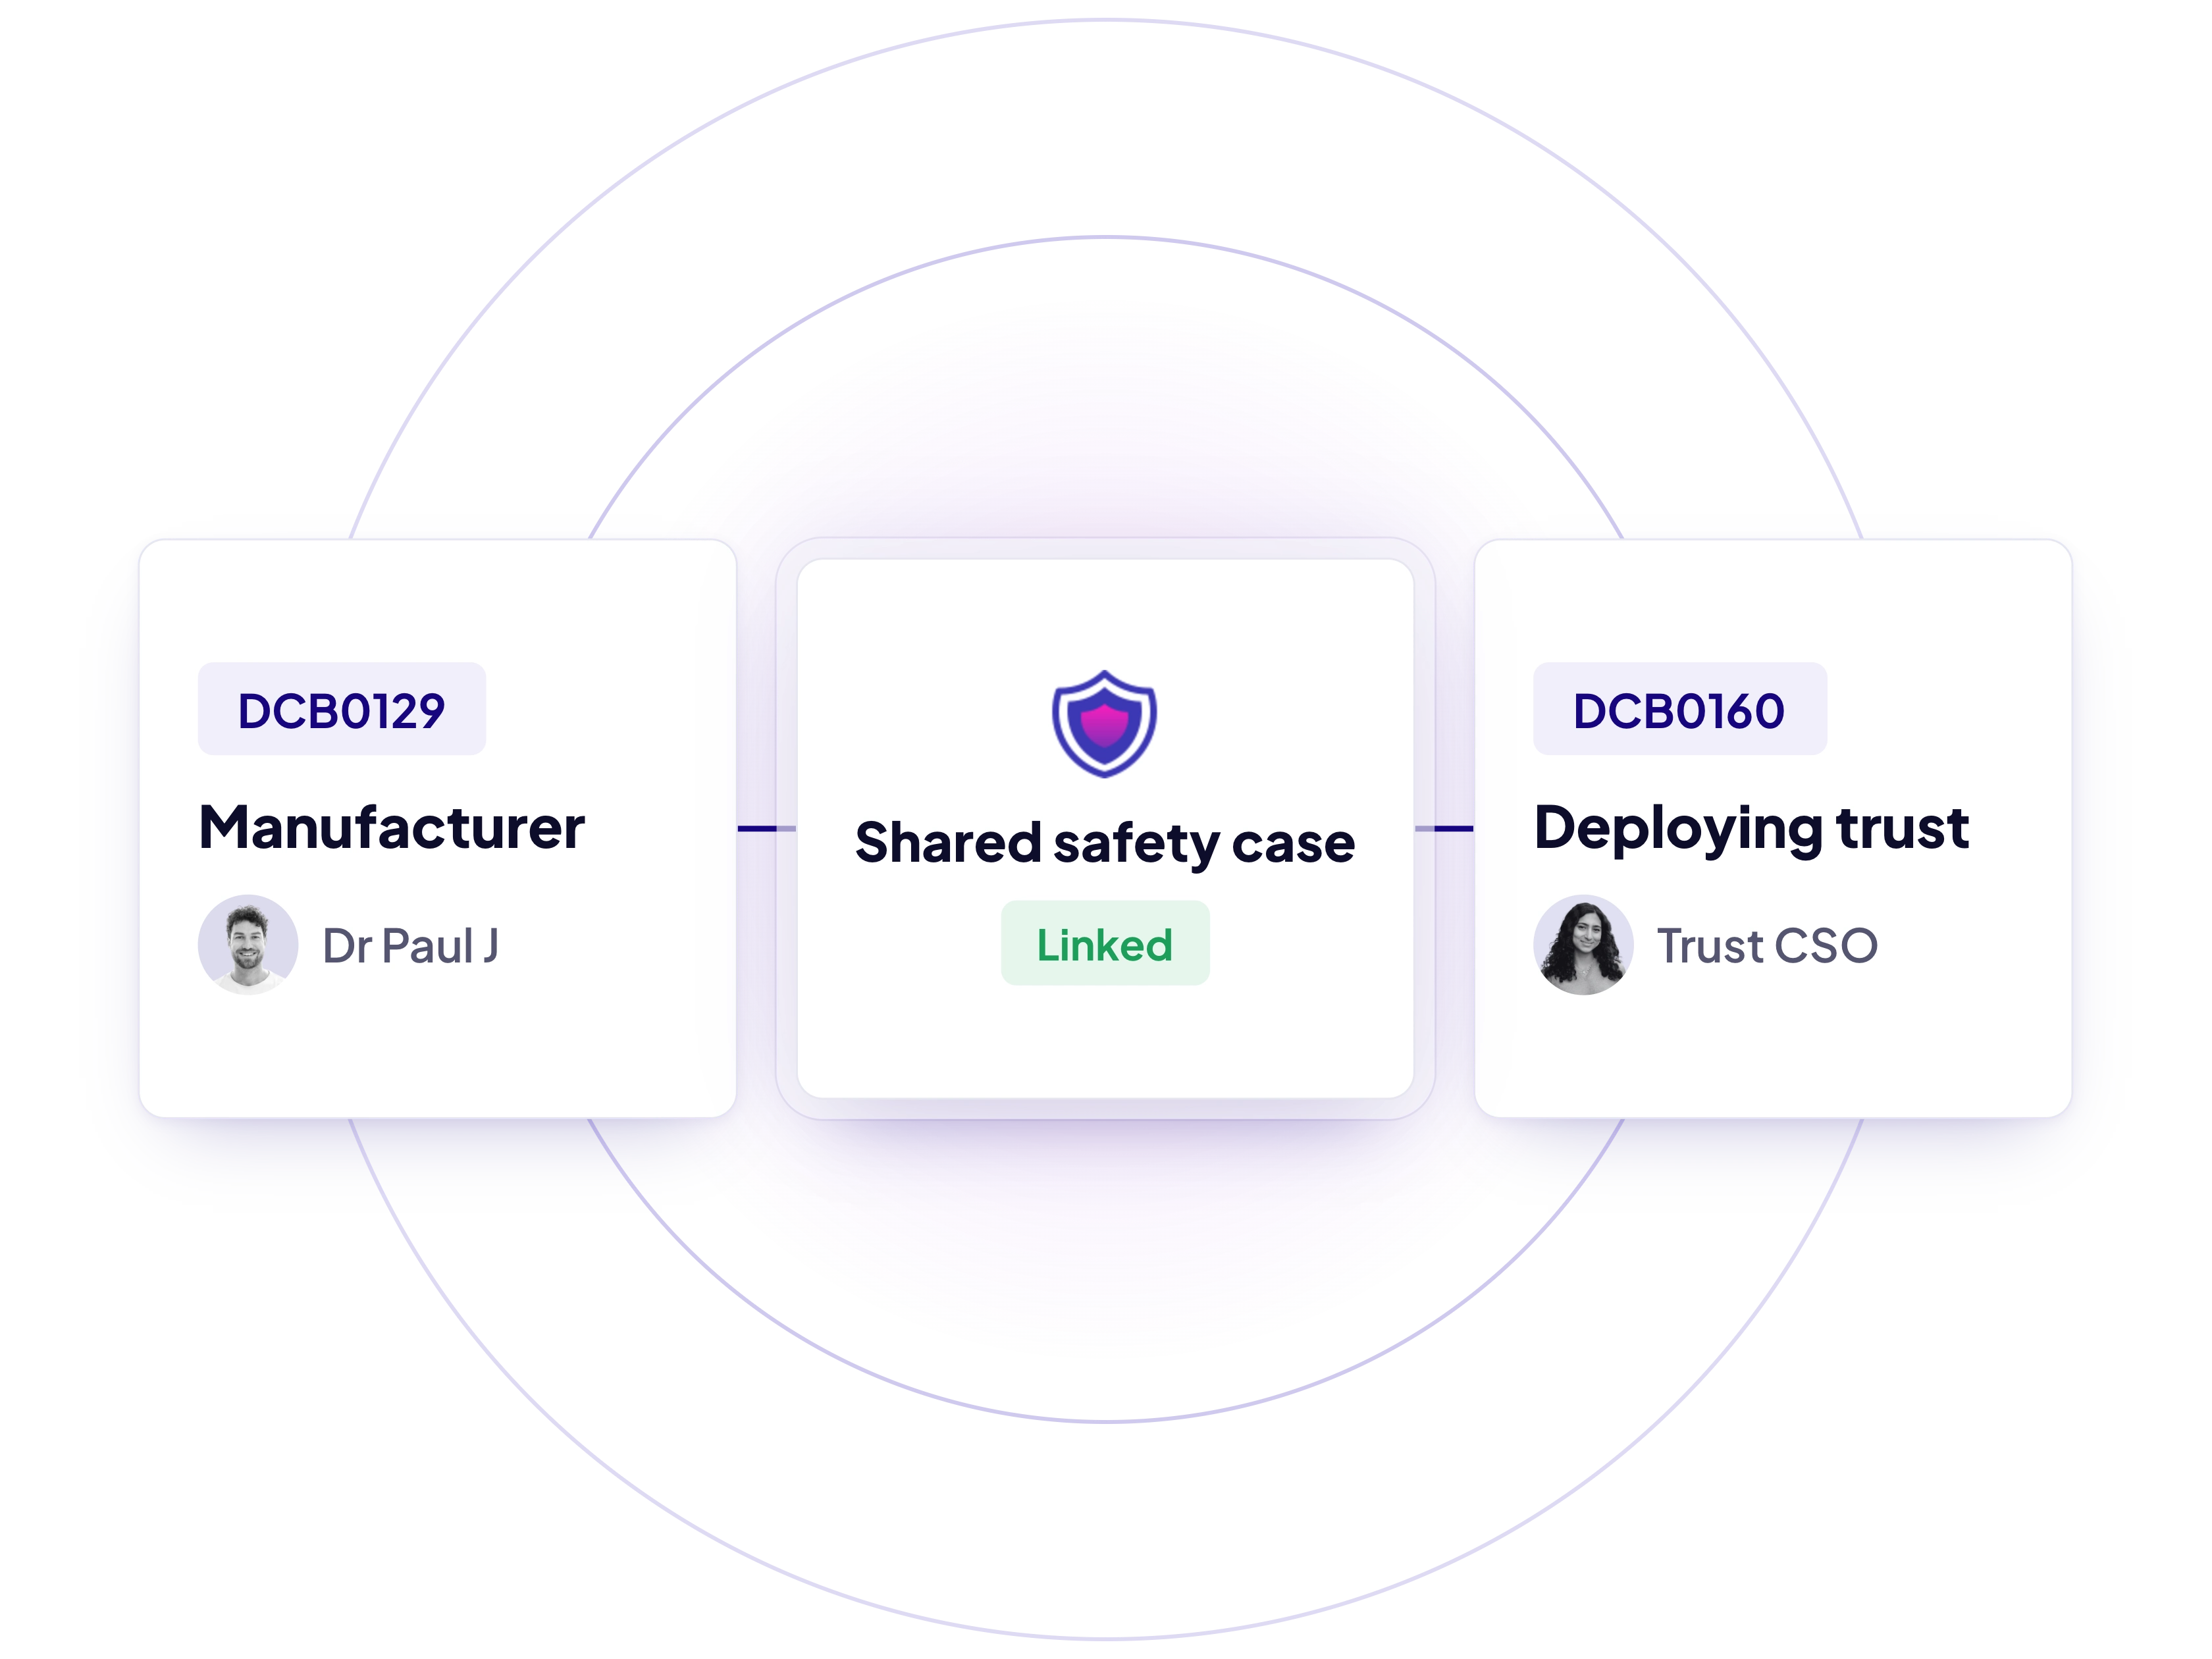
Hazard logs and safety cases built from live records for each deployment, reviewed and signed off by a named Clinical Safety Officer.
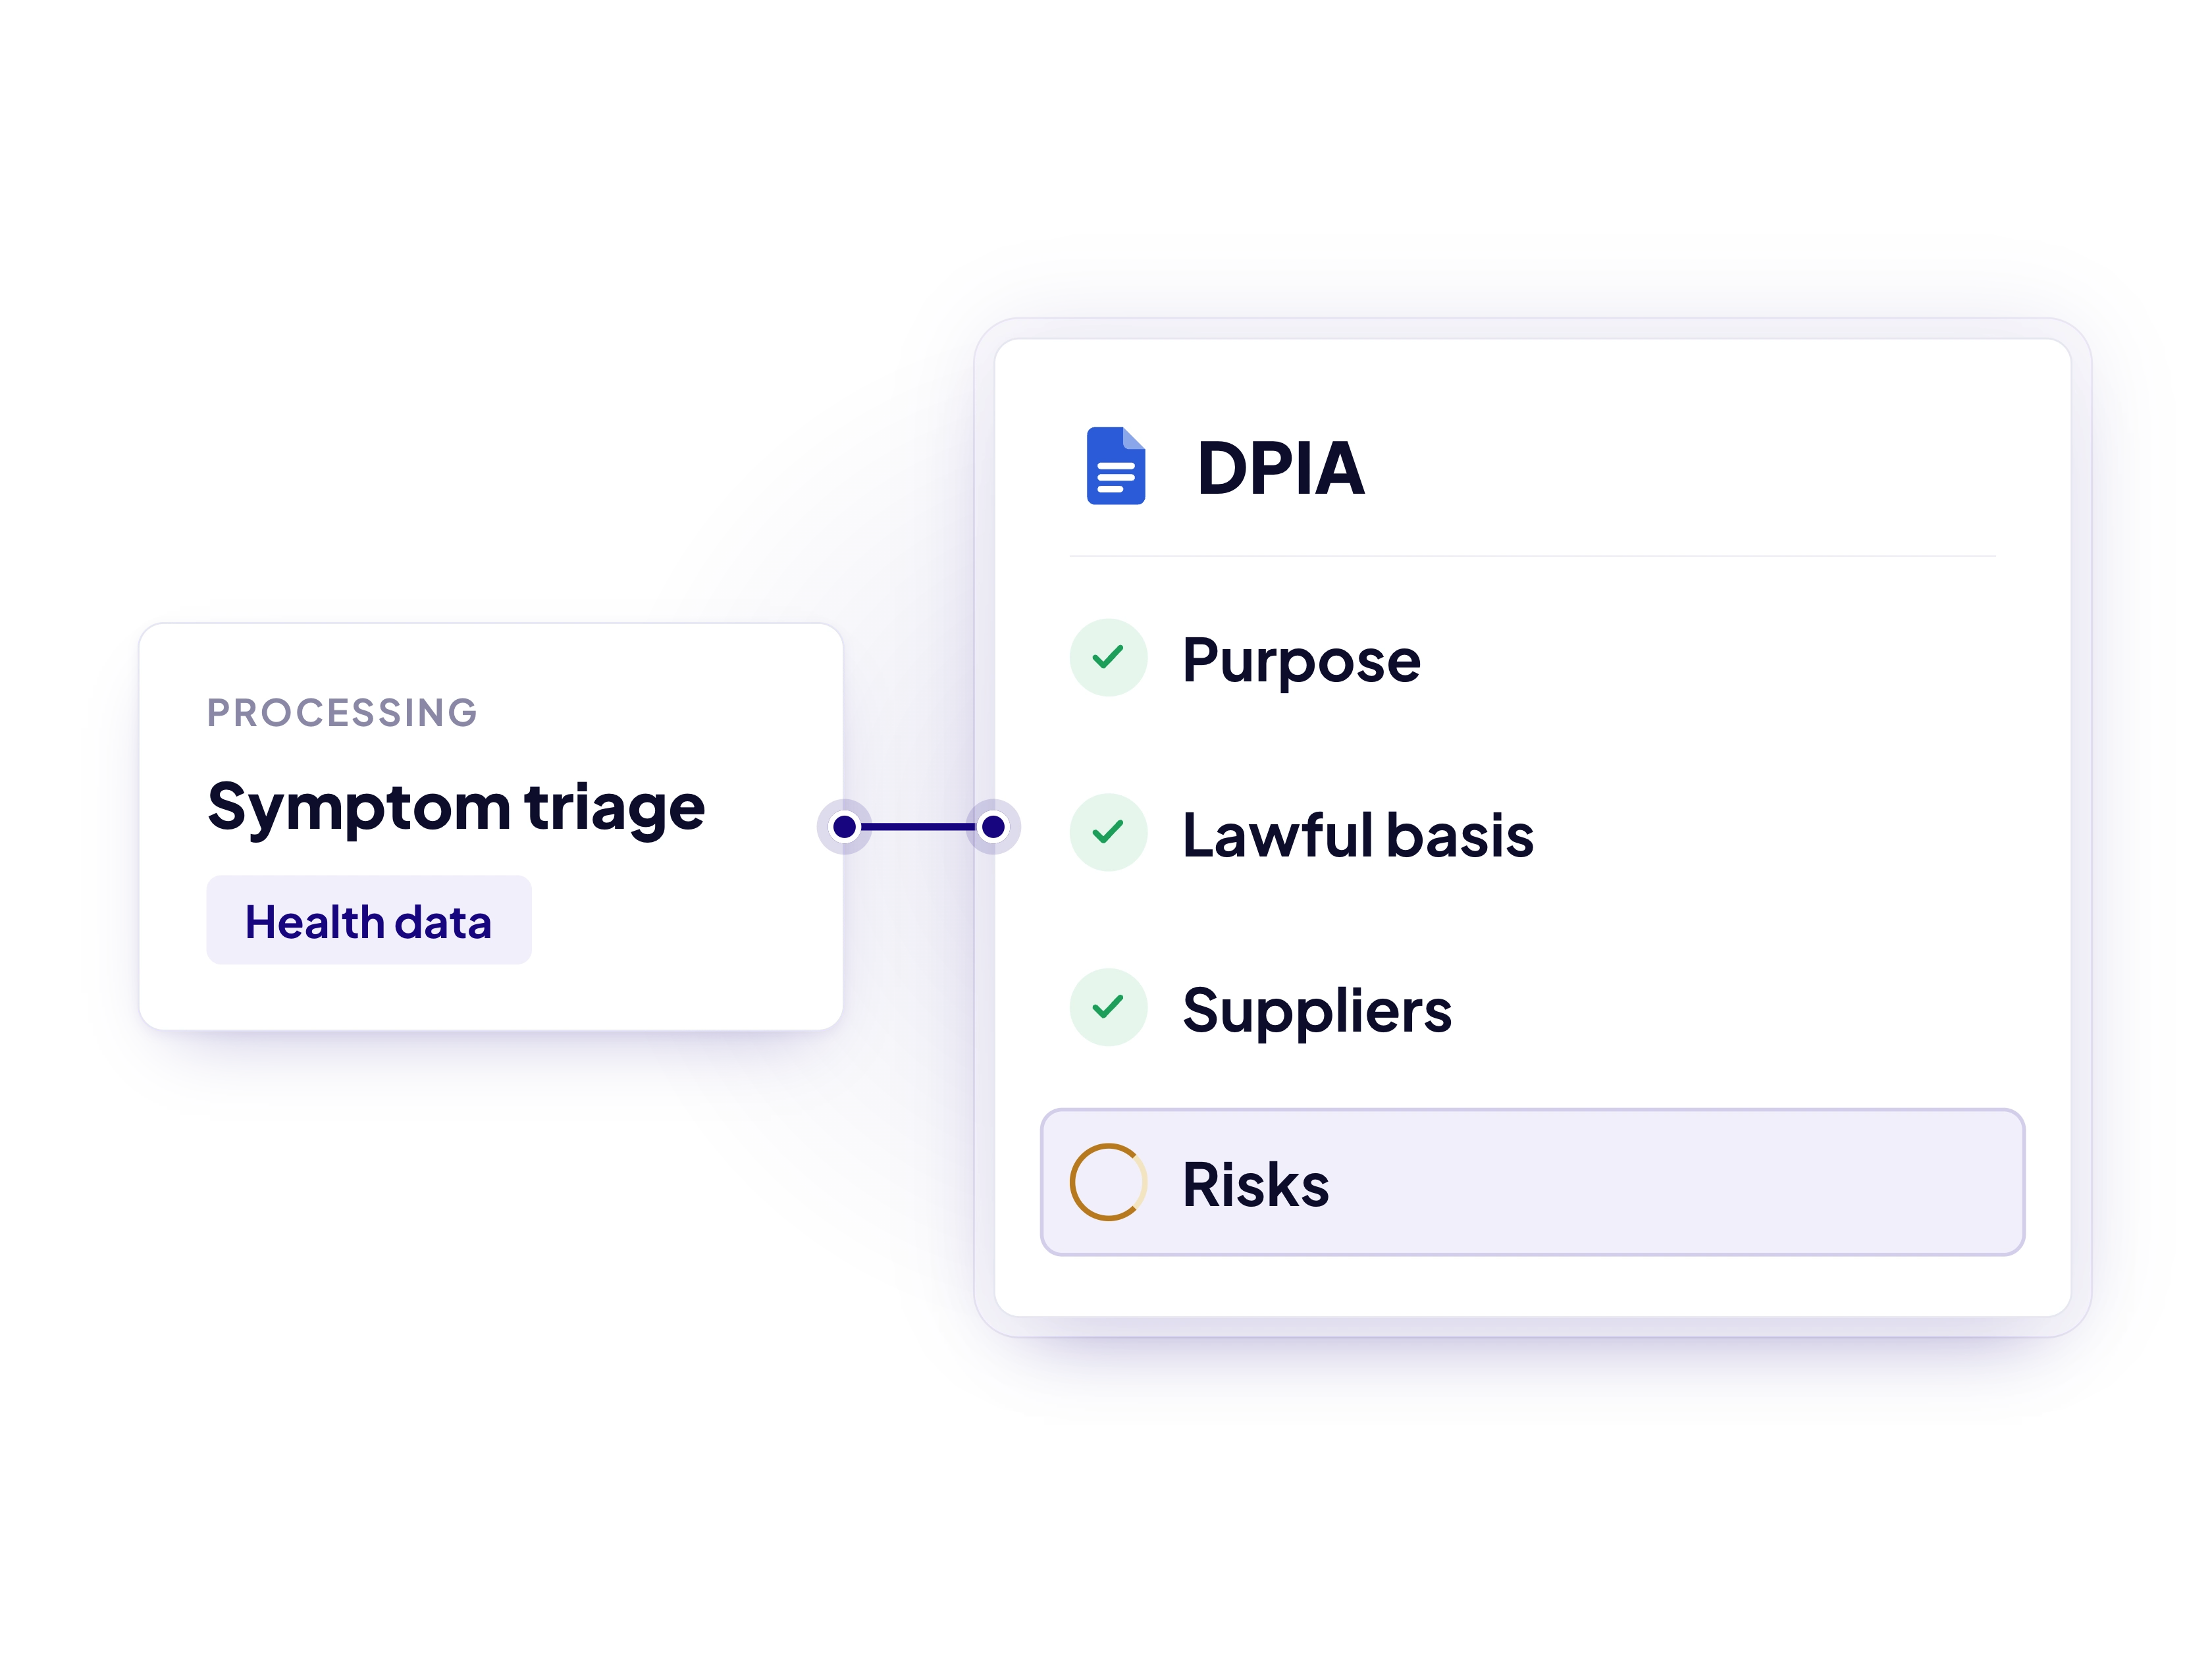
Draft DPIAs from templates, keep your record of processing and information asset register up to date, and evidence every DSPT assertion as you go.
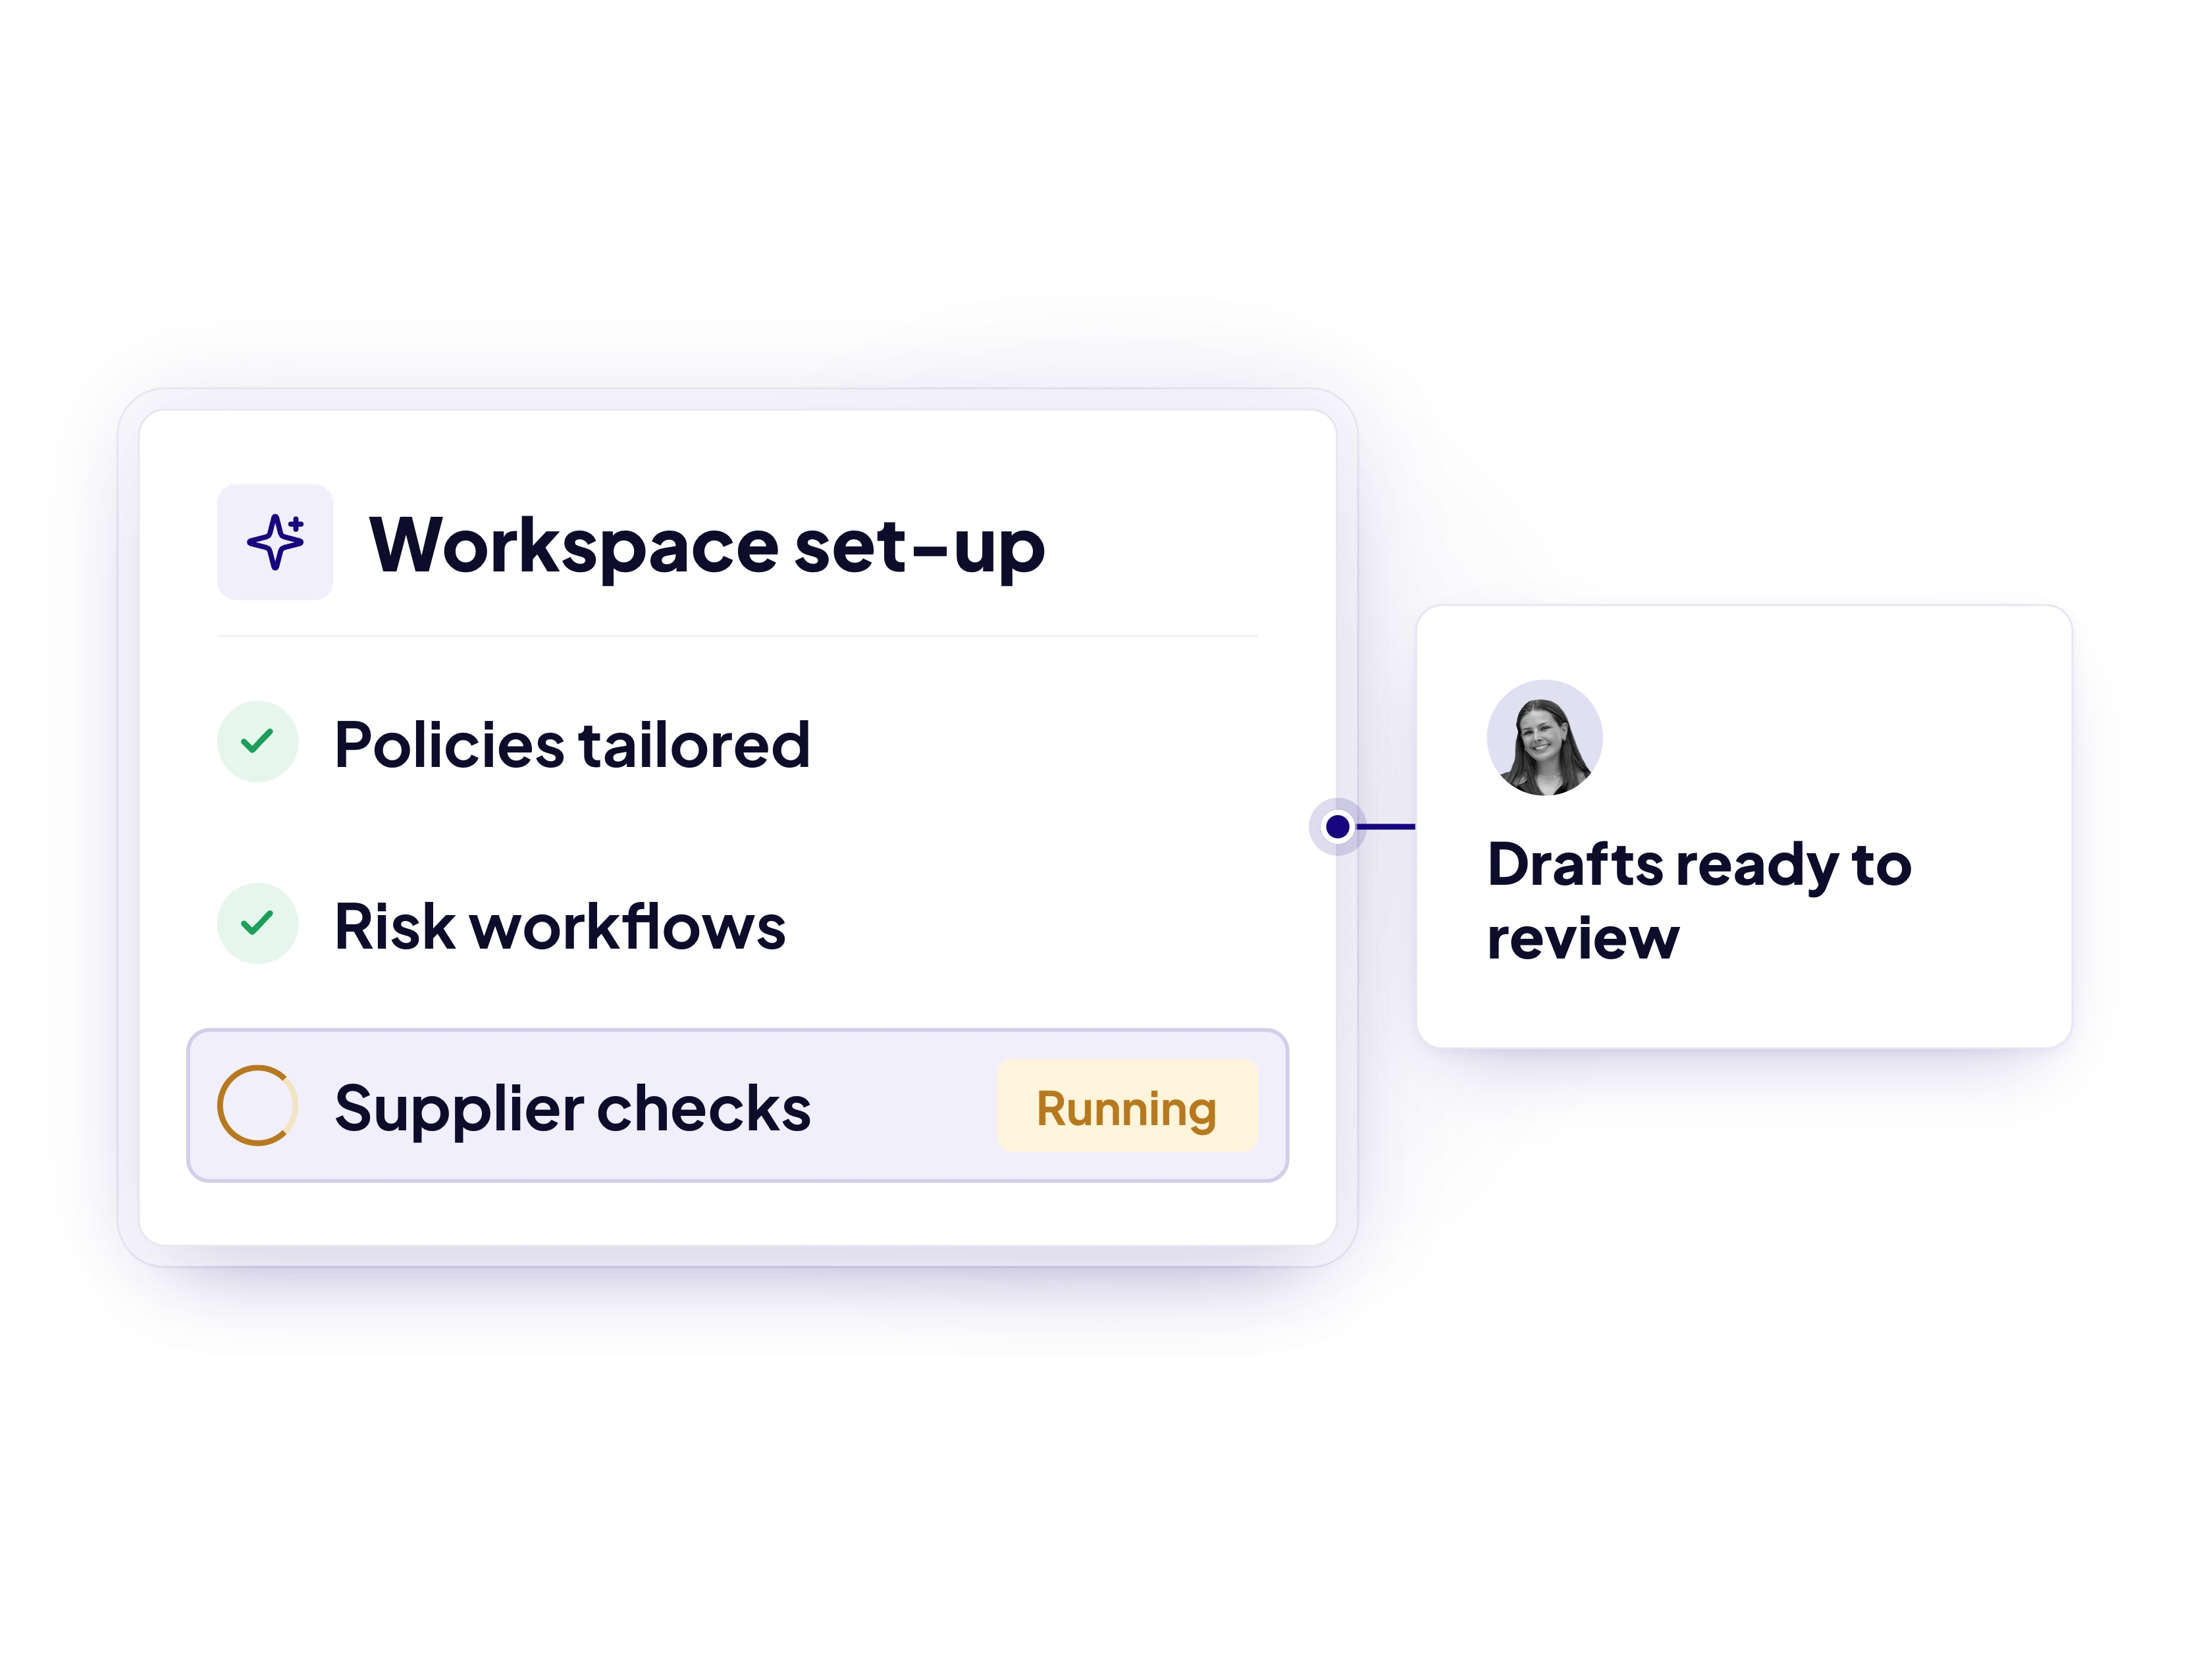
Assuric AI drafts documents, reviews evidence and finds information across your workspace, cutting the manual work for your team, with every change approved by a named person.
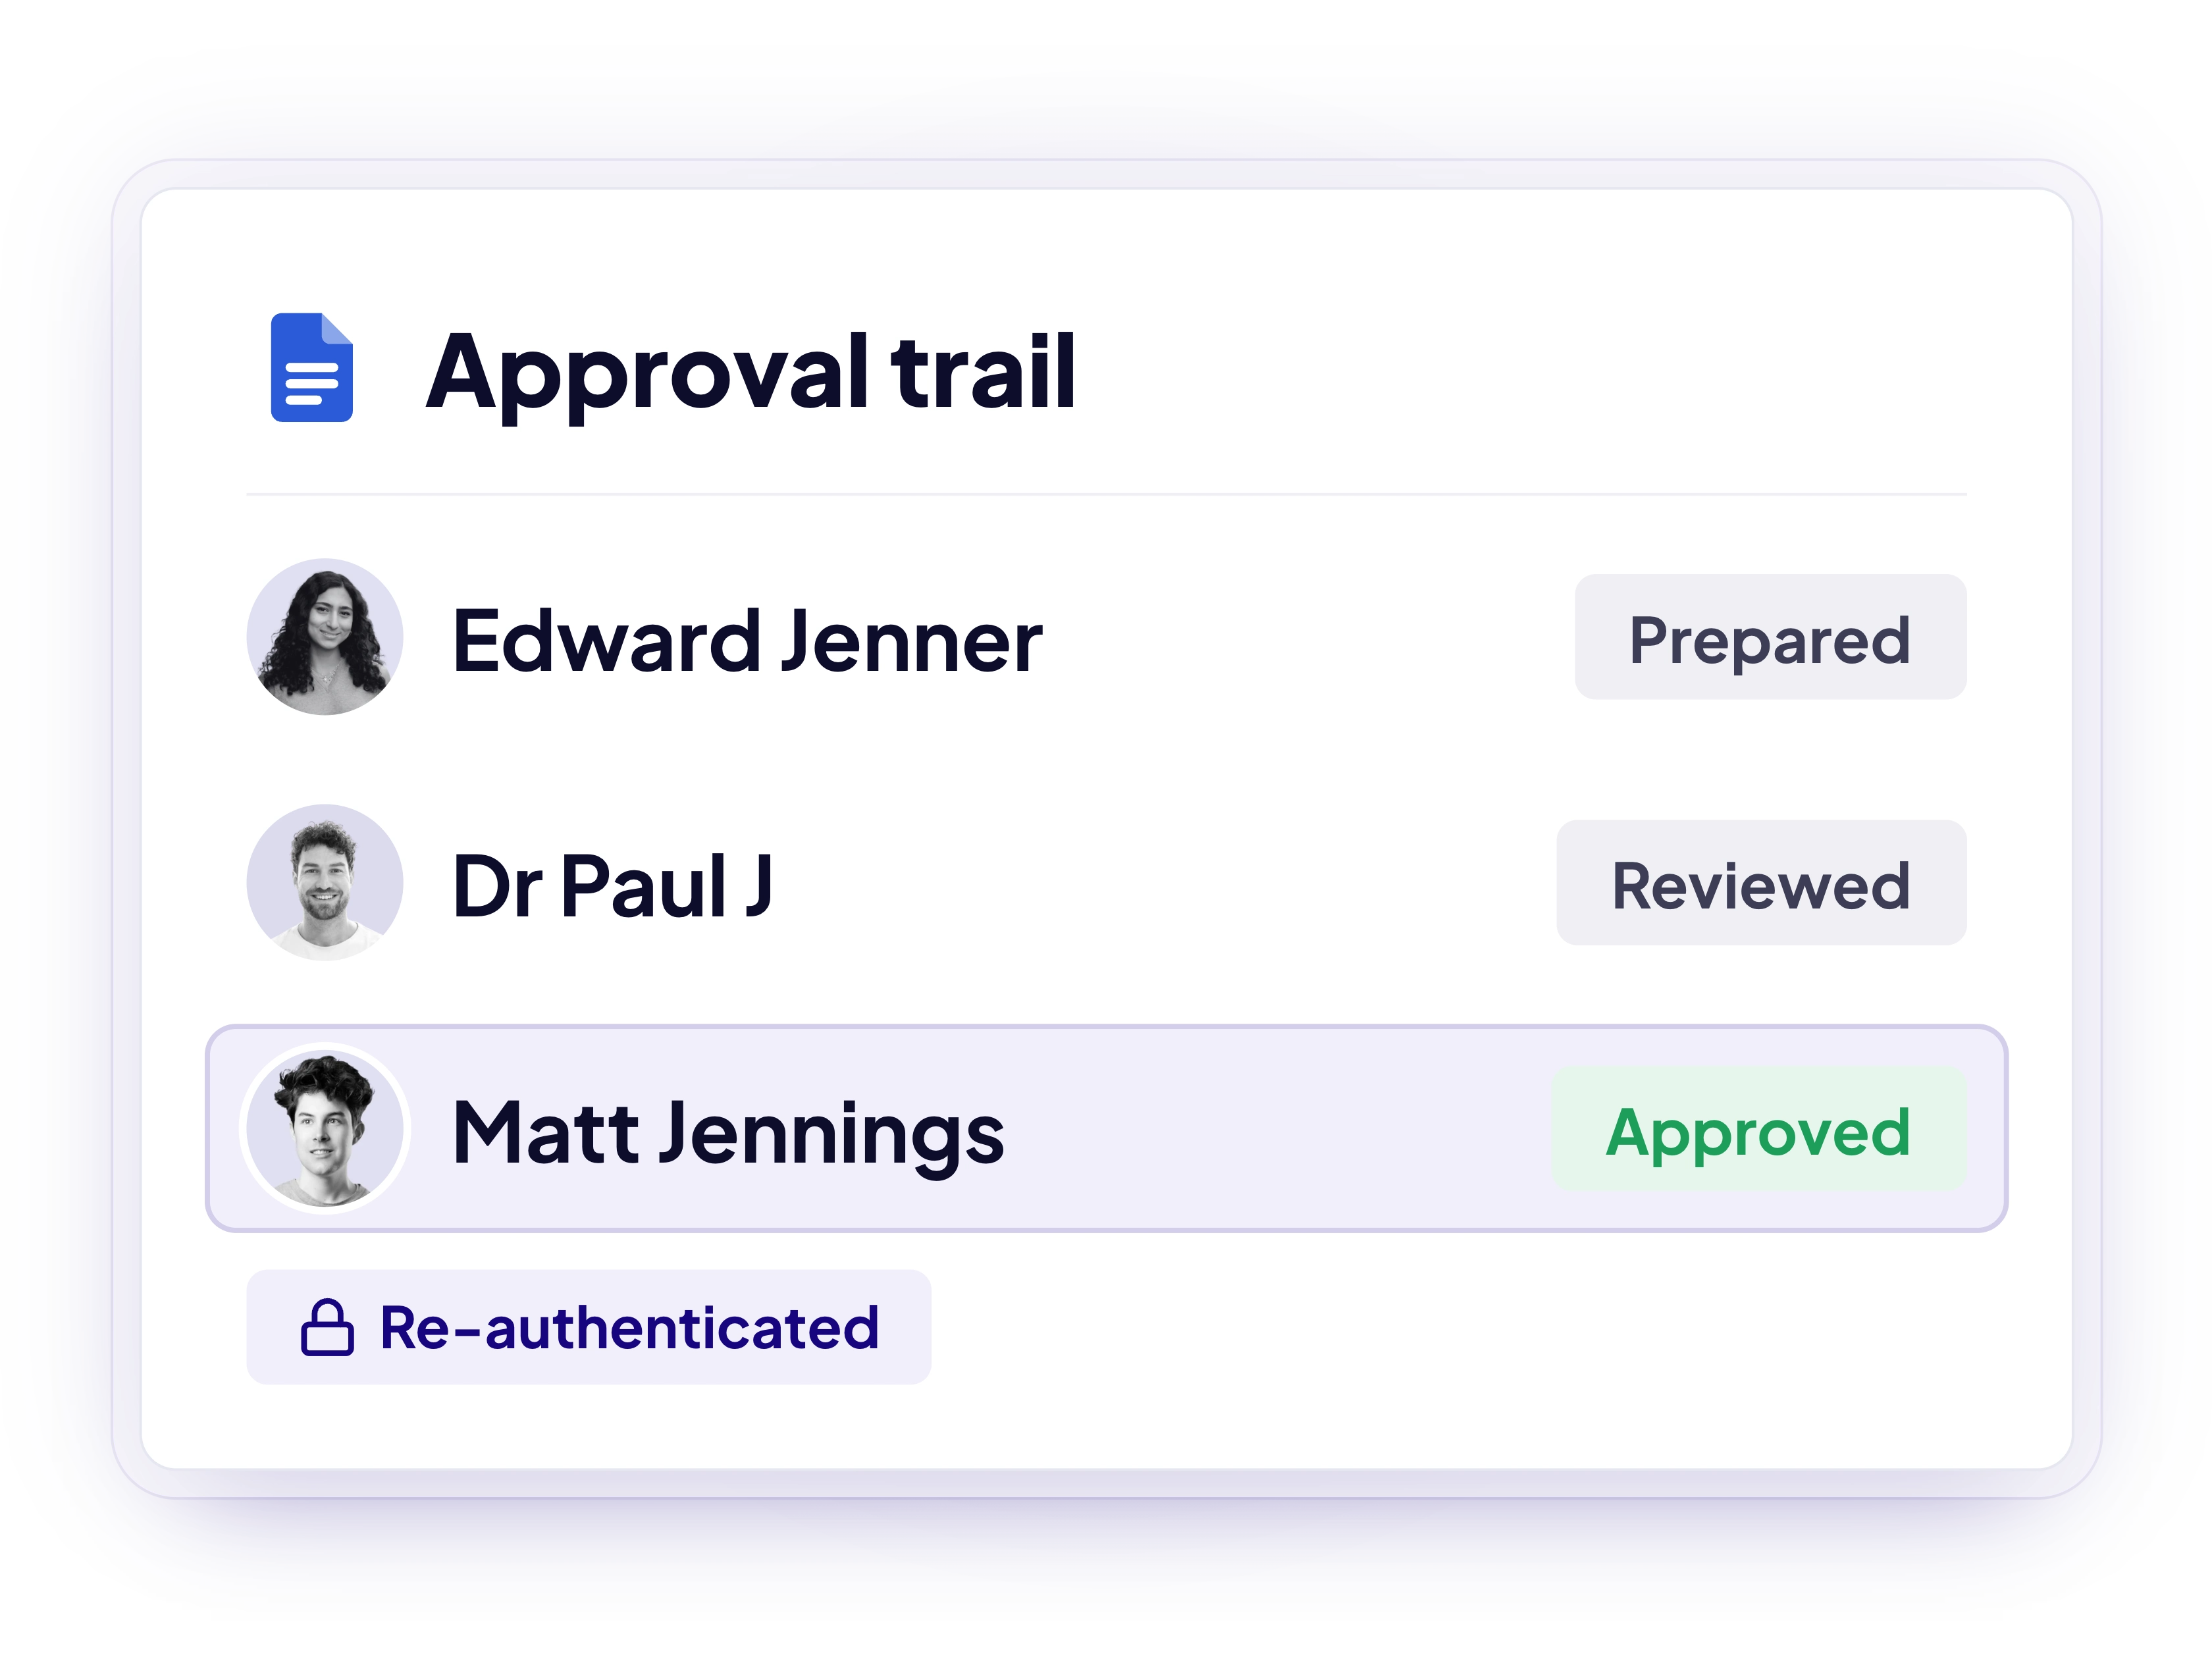
Every change, approval and decision is timestamped and attributable, with single sign-on and role-based access, so you can show exactly who did what, and when.
Features
Everything healthcare teams need to deploy digital technology safely, in one system with one audit trail.
Hazard log
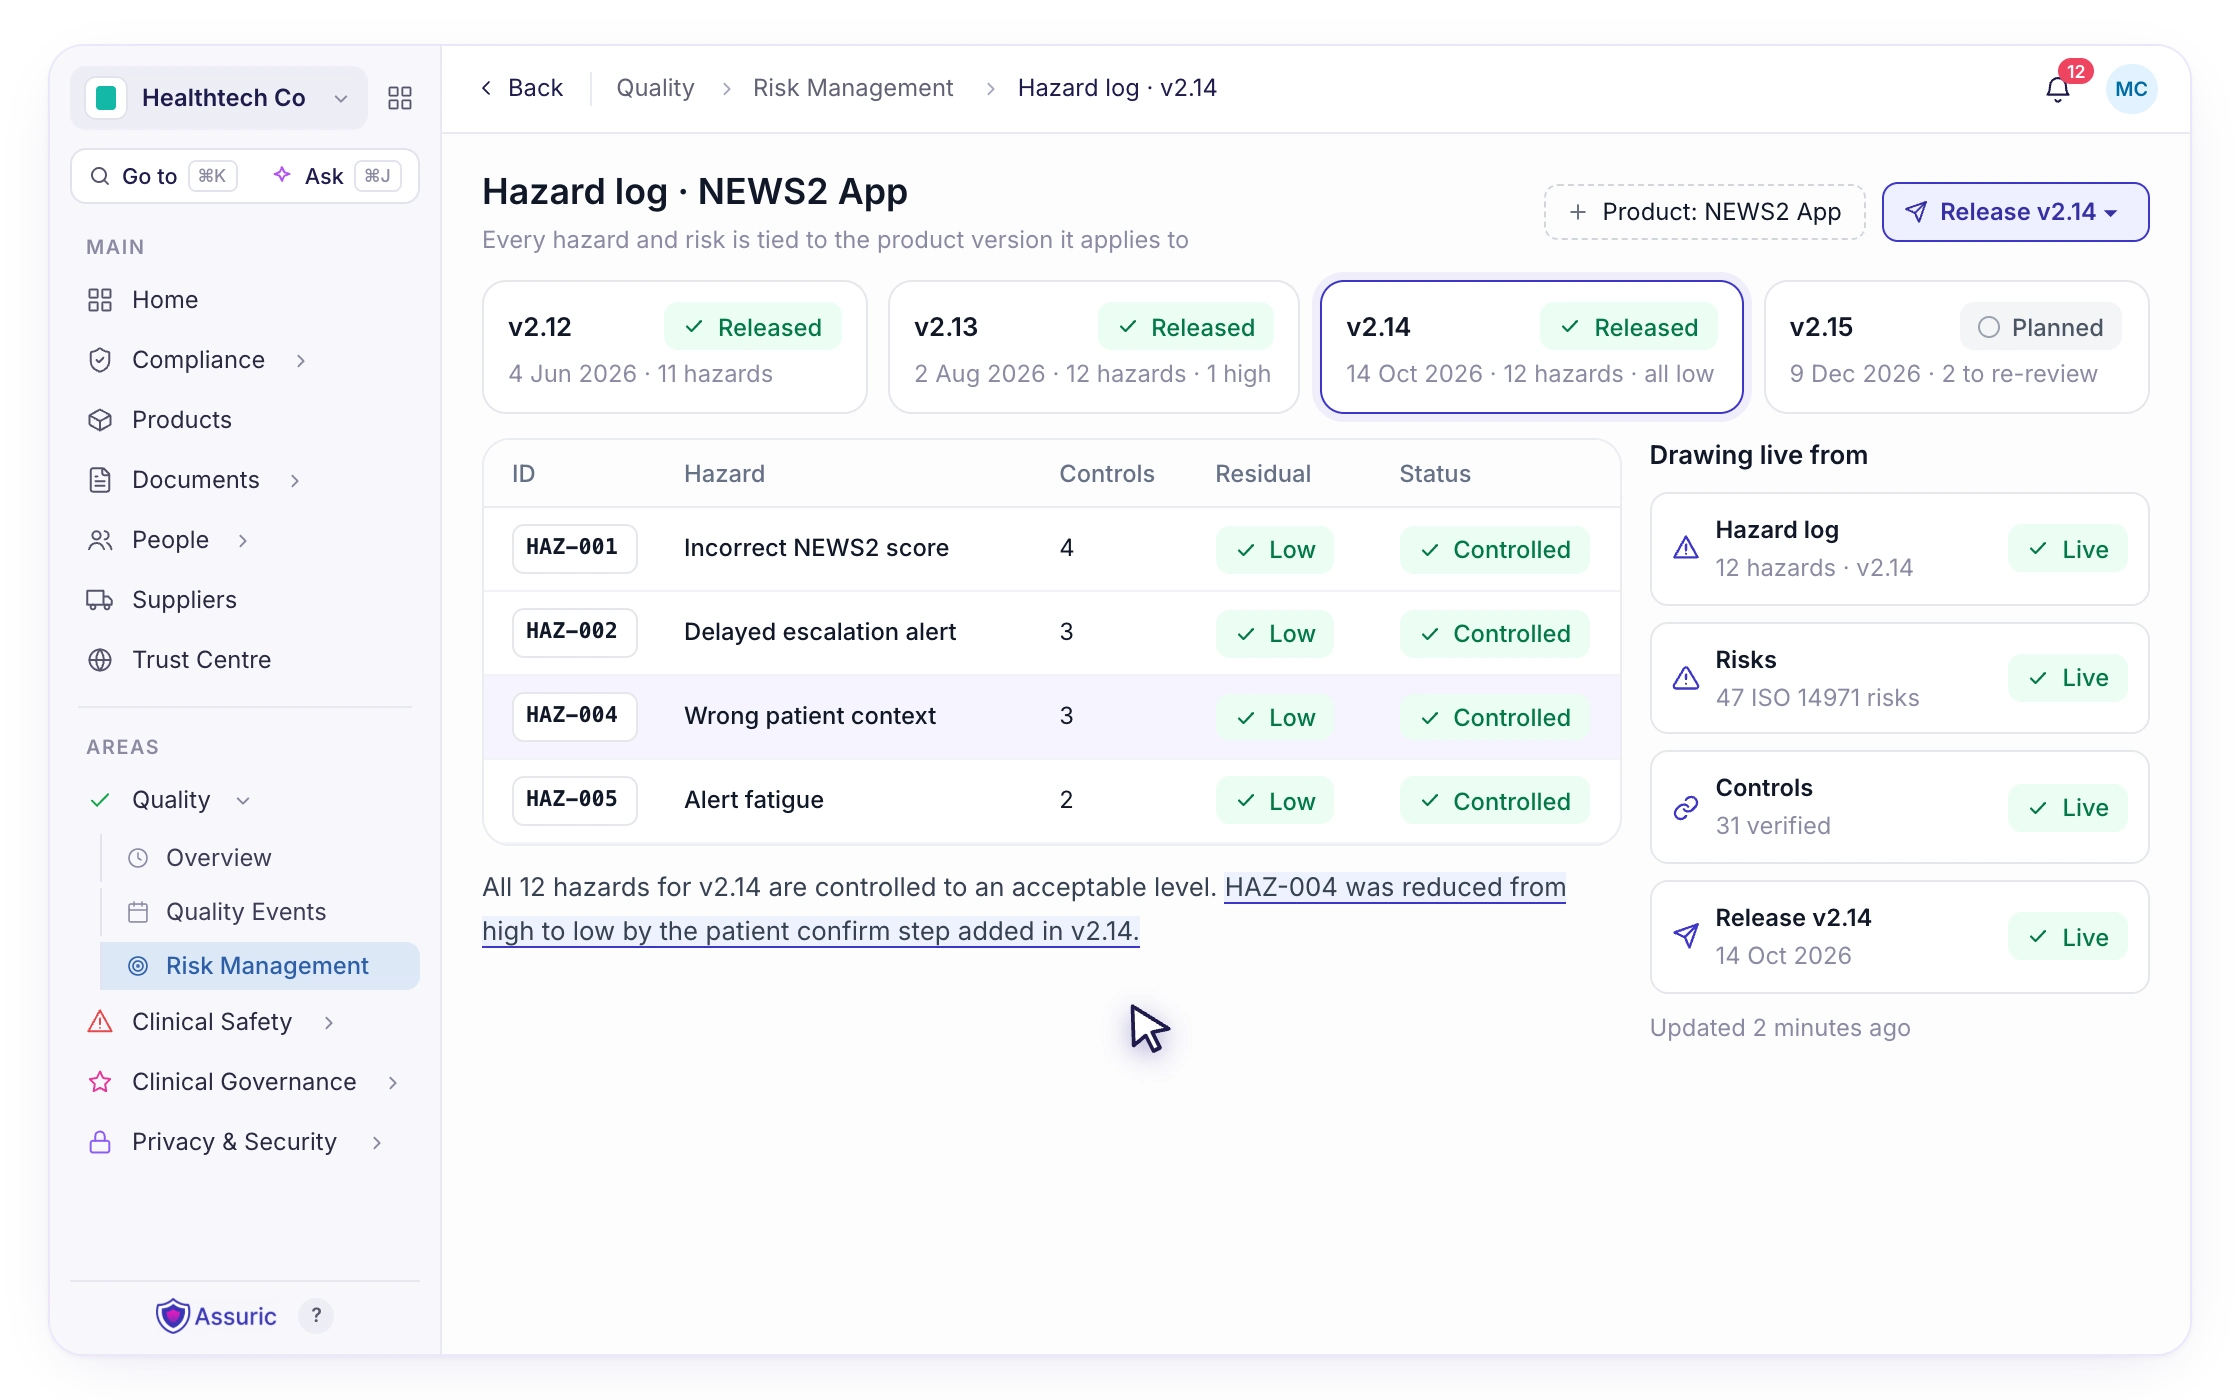
Record hazards, the controls that reduce them and the evidence that proves they work, all linked in one place instead of spread across separate documents.
Safety case reports
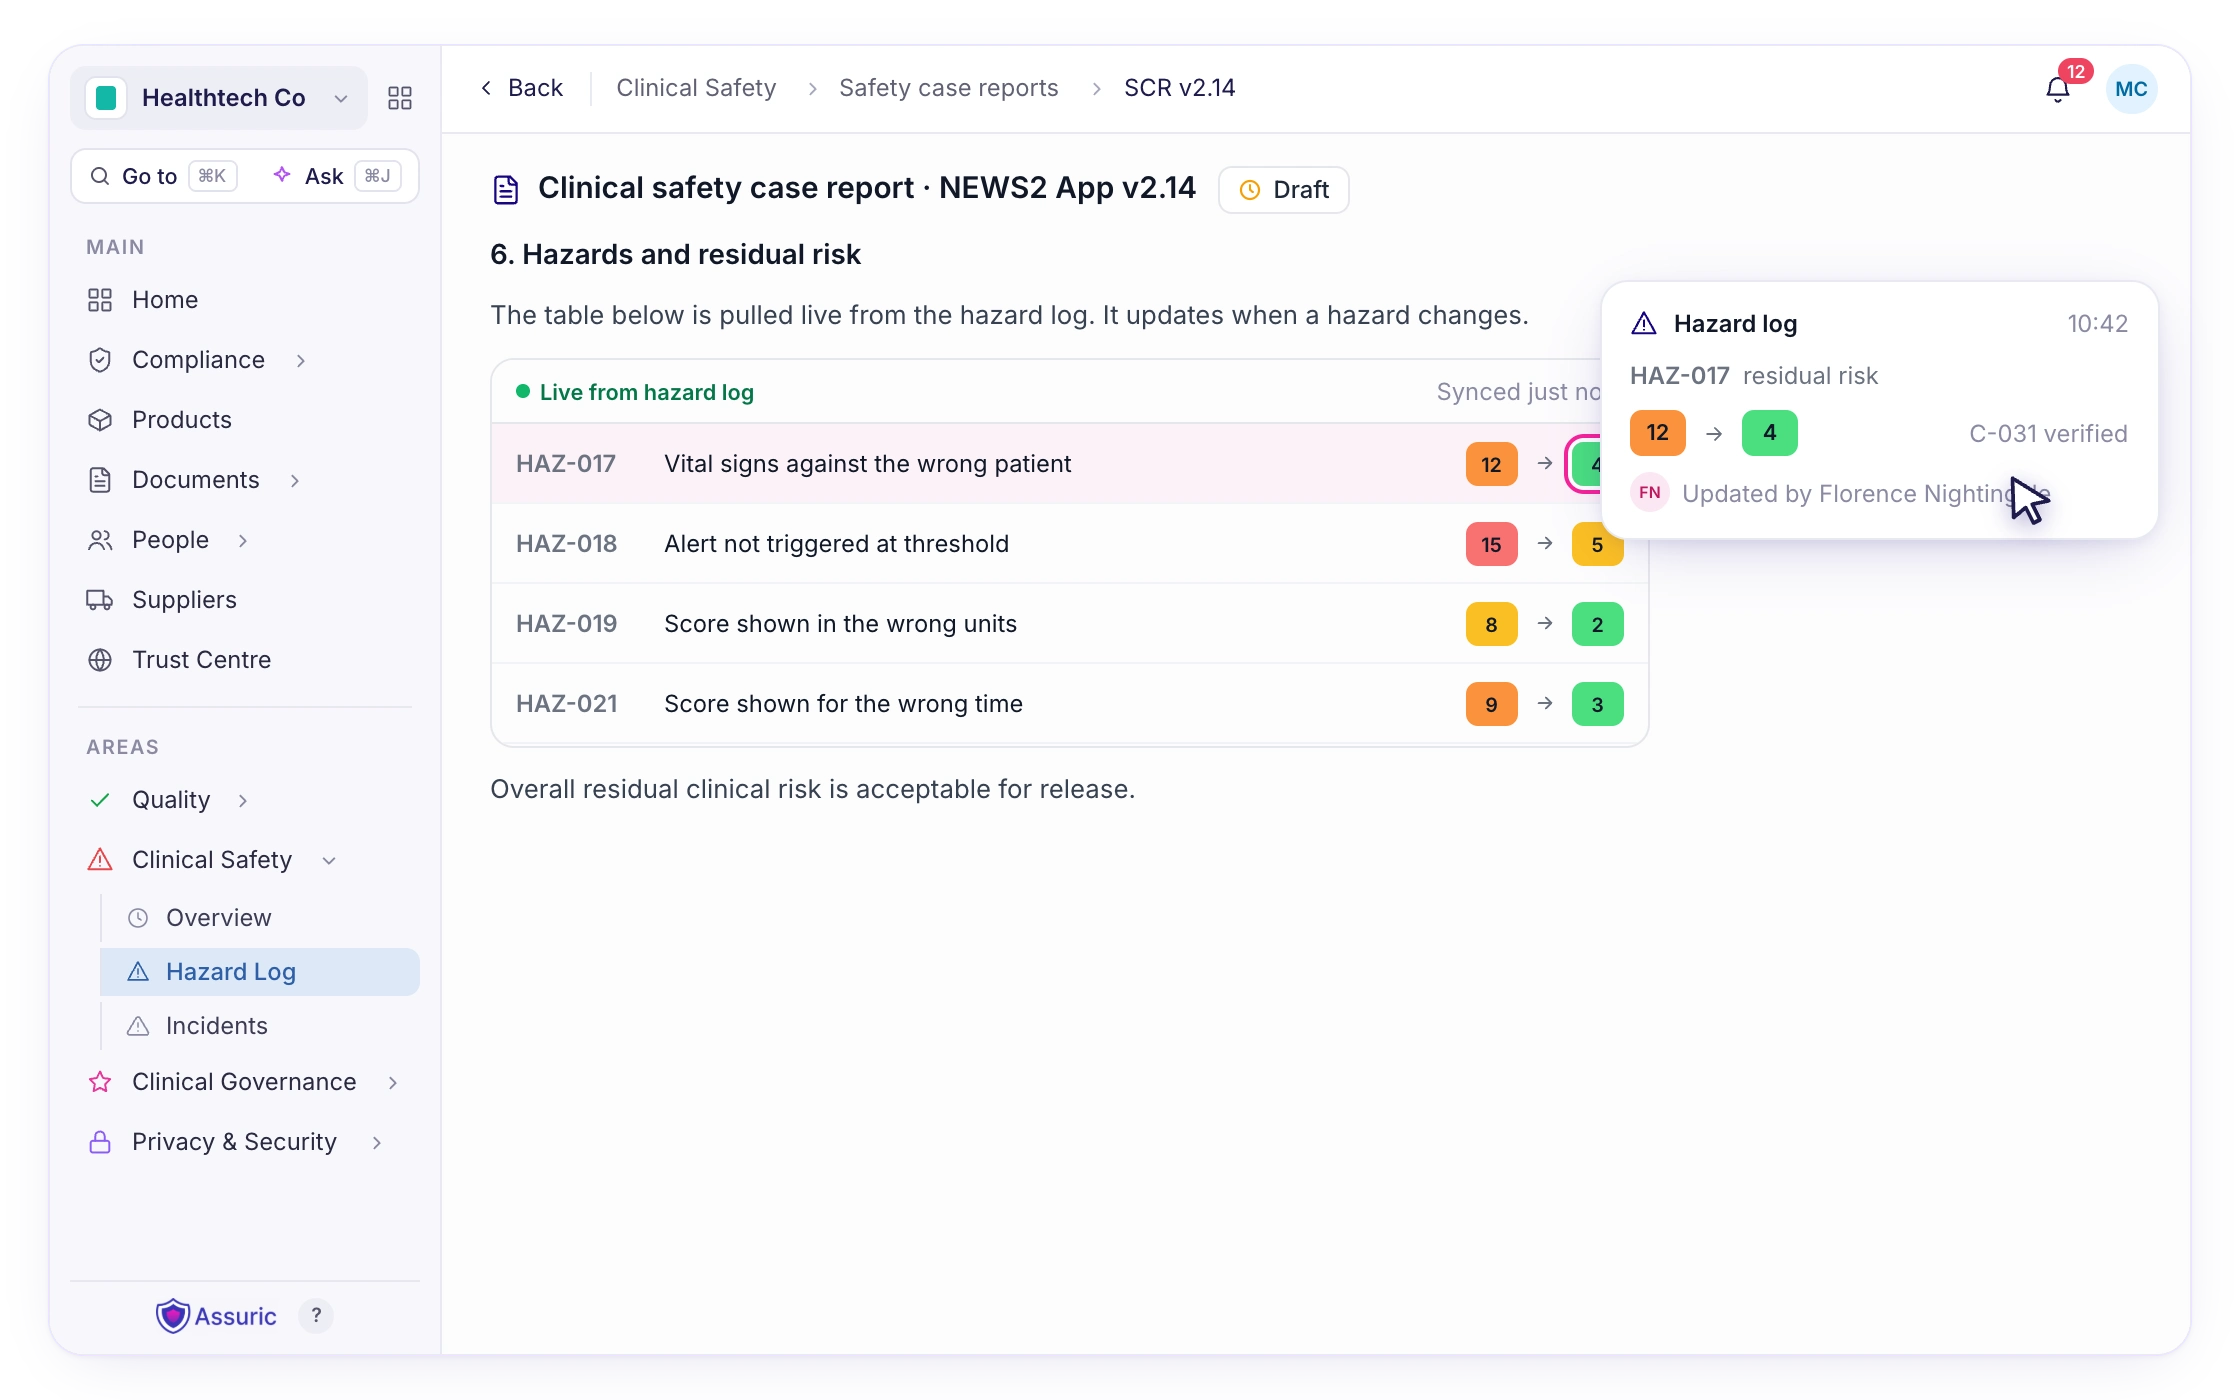
Generate DCB0160 safety case reports from your live hazard log, with reviews, approvals and version control built in, so each report reflects the latest position.

Supplier management
Keep a register of every supplier, send DTAC and information governance questionnaires through a supplier portal, manage the DPIA for each one, and track their evidence, agreements and risks in one place.

Clinical governance & CQC
Policies, incidents and governance records organised against the CQC quality statements, so you can see gaps well before an inspection.

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”
Maks Kozarzewski
COO, VitVio

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”
Paul Llewellyn
CCIO, Accenture

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”
Katie Baker
Director UK & Ireland, Tandem
DCB0160 is the NHS clinical risk management standard for health and care organisations that deploy and use health IT systems. If you are rolling out digital technology that supports patient care, you need a clinical risk management process, a named Clinical Safety Officer, a hazard log and a clinical safety case for each deployment.
Assuric brings supplier evidence, DCB0129 outputs and your own DCB0160 work into one place, so assessments start from what you already have rather than a blank template. Hazards, controls and evidence are reused across deployments, AI helps draft and review documents, and our fractional Clinical Safety Officers add capacity when your team is stretched, so new systems reach patients sooner without cutting corners on safety.
Send DTAC and information governance questionnaires to suppliers through a supplier portal, and collect their DTAC responses, DCB0129 documents and security evidence in one place. Your team reviews every supplier against the same standard, sees gaps straight away, and keeps agreements, risks and review dates with each supplier, so assurance does not hold up deployment.
Yes. Start each Data Protection Impact Assessment from a template, pre-filled from the supplier, data and processing information already in Assuric, then track it through review and approval. Every DPIA is kept with the supplier and system it relates to, can be shared with external stakeholders, and can be reviewed by one of our Data Protection Officers if you need extra capacity.
Yes. Alongside clinical risk, you can run your corporate, operational, information governance and security risk registers in Assuric. Each risk has an owner, a score and a treatment plan on a risk matrix that fits your organisation, with review dates and reminders, and links to the assets, suppliers and controls it relates to. You can start from a library of common risks, let AI suggest ones you might have missed, and report on every register from one place.
Each deployment gets its own hazard log and safety case, while shared hazards, controls and evidence are reused across them. Your clinical safety team sees every deployment, owner and outstanding action in one register, instead of a folder of separate documents.
Yes. DCB0160 requires a named, suitably qualified Clinical Safety Officer to oversee clinical risk management. If you do not have the capacity in-house, our fractional CSOs work inside your Assuric workspace and support your team with assessments, sign-off and incidents.
Yes. Every DSPT assertion has its evidence attached and an owner named, with reminders before your annual deadline, so the submission is a review of work you have already done rather than a scramble at the end.
Yes. Assuric maps your policies, incidents, audits and staff records to the CQC quality statements, so you can see where you stand and close gaps well before an inspection. Our CQC specialists can also support you with registration and inspection preparation. See CQC compliance.
NHS trusts, health boards, integrated care systems, GP practices and independent providers. Our customers include NHS trusts, GP practices, and private healthcare, from large groups to small clinics.
Yes. Assuric is ISO 27001 certified by a UKAS-accredited certification body, holds Cyber Essentials Plus, and exceeds the NHS DSPT standards, with single sign-on and granular access controls for your team.
See how Assuric helps your team deploy digital technology safely, with every hazard log and safety case in one place.