Every entity, product and jurisdiction in one place
Give each entity, department and product its own space, with its own evidence, documents and releases, then see where compliance stands across the whole group in one view.
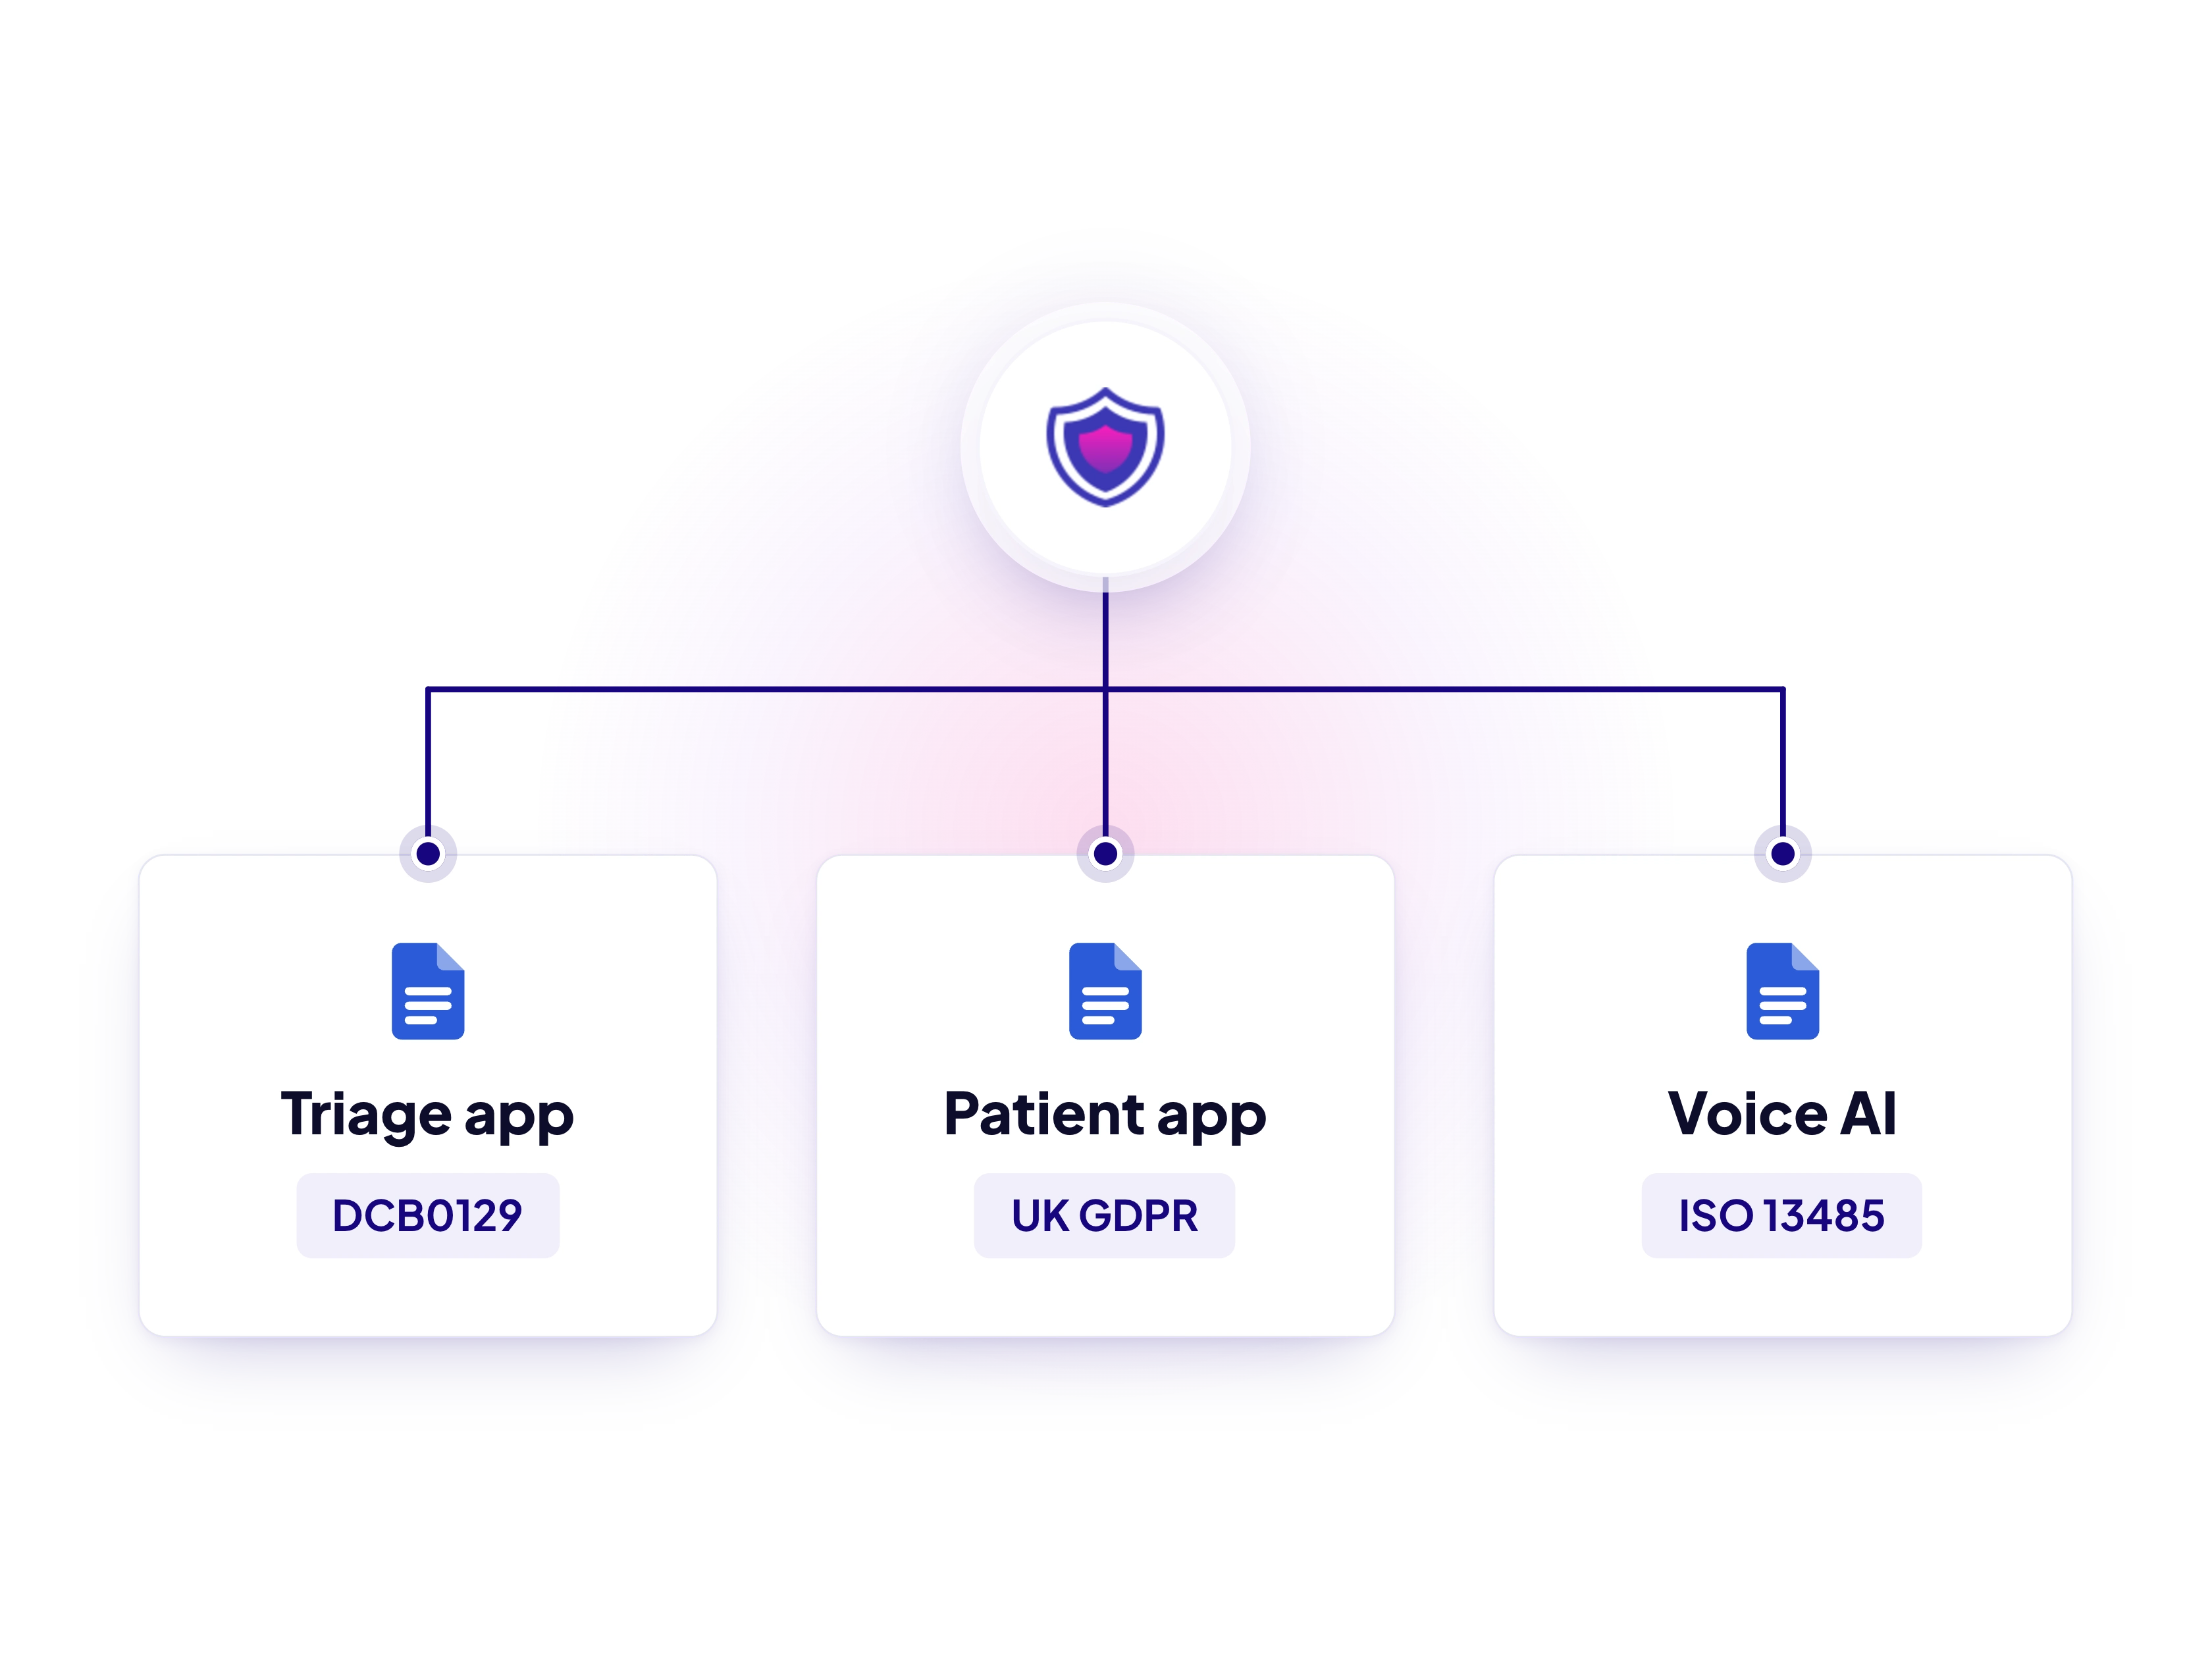
Run every entity, department, product and market from one secure system, with a comprehensive framework library, granular access controls and AI that takes on the manual work.
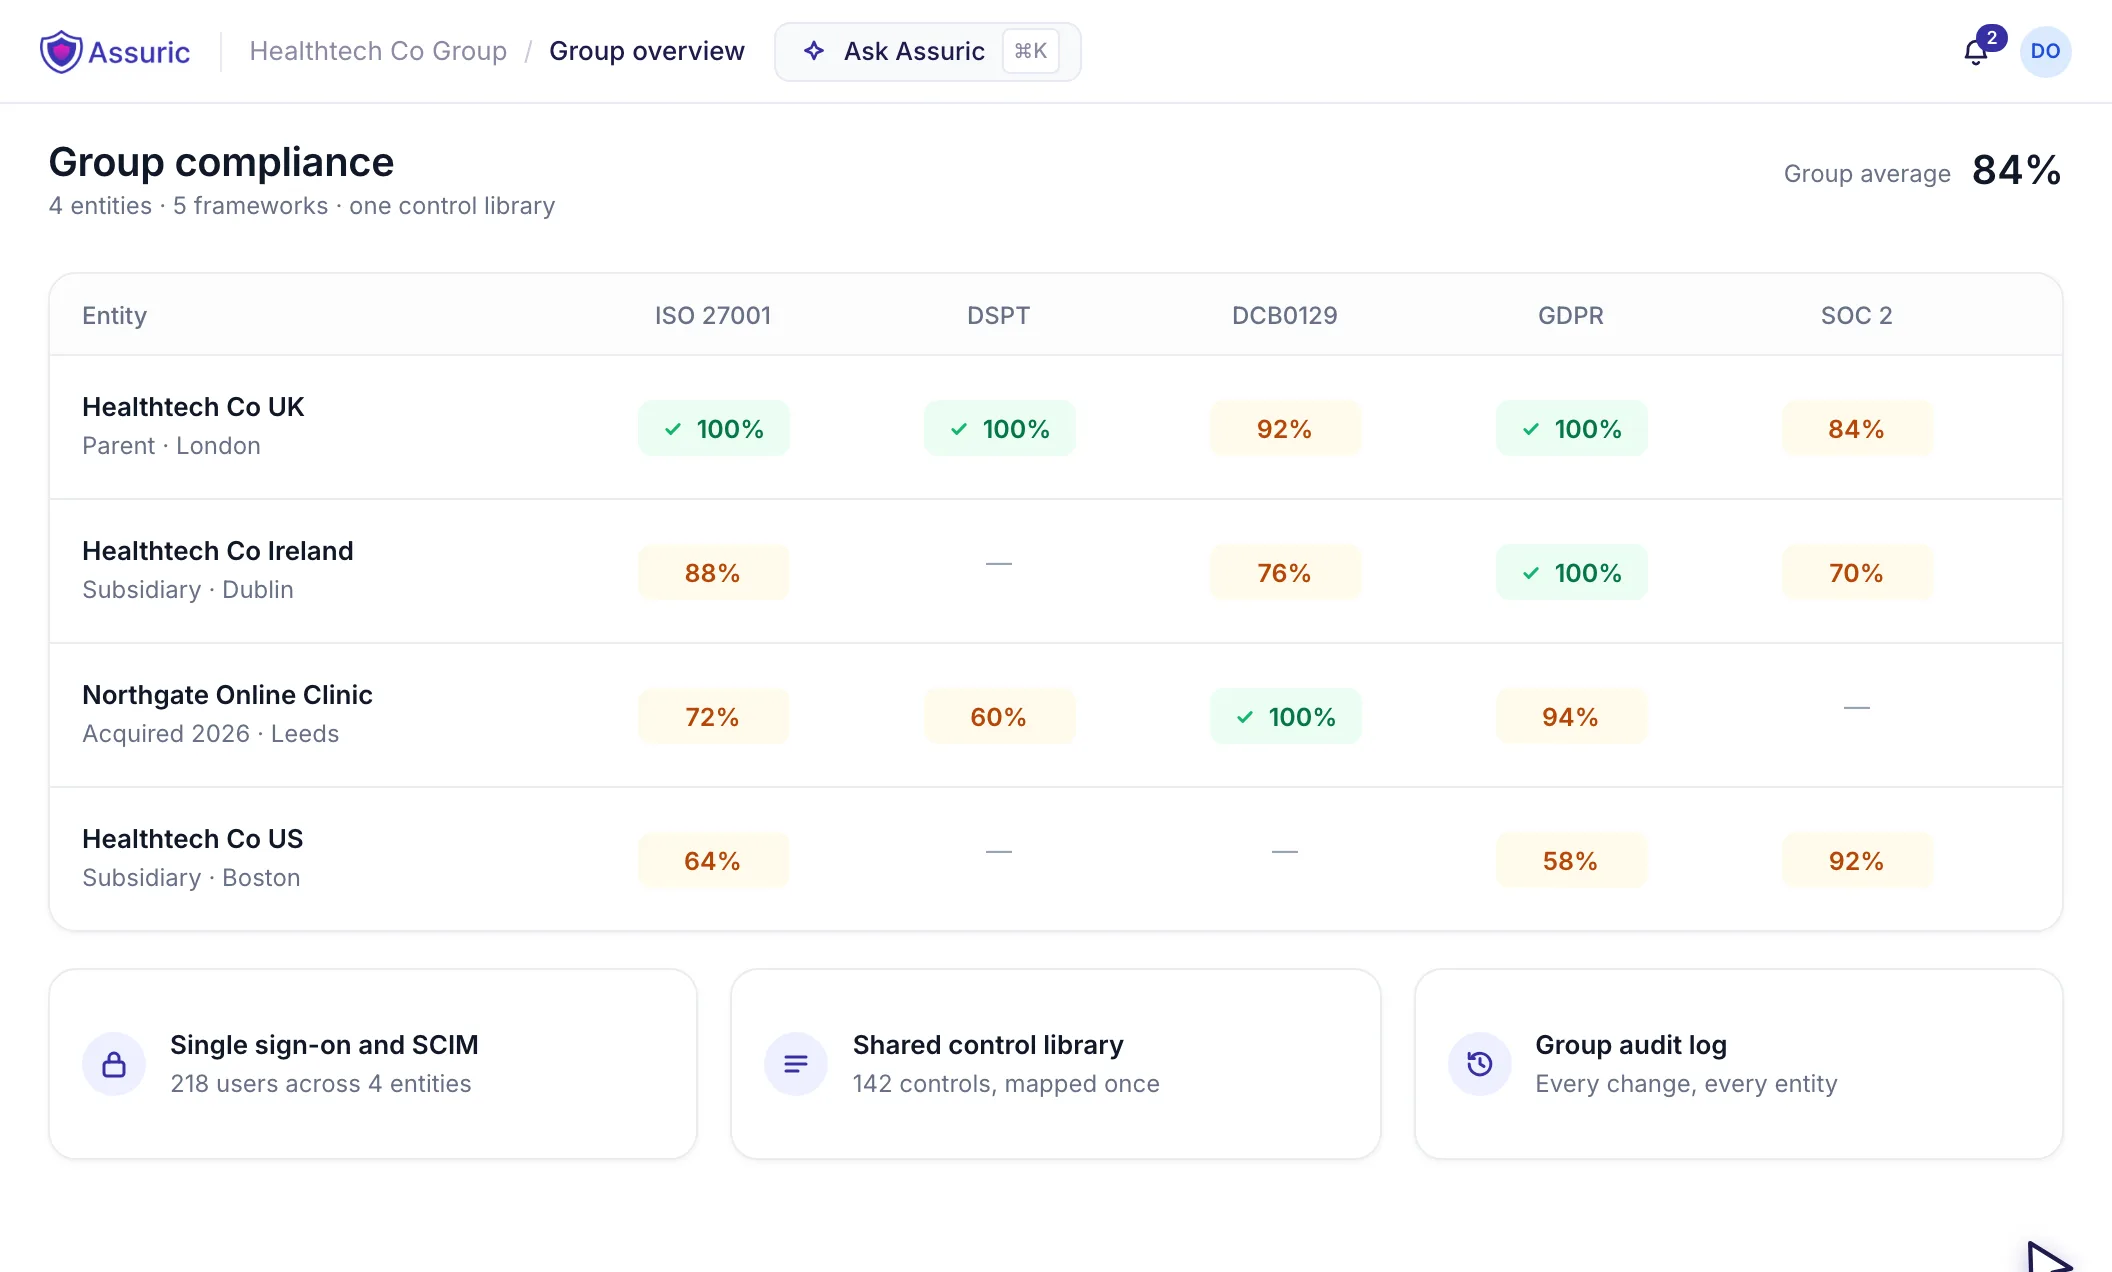
Trusted byenterprise healthtech teams


Benefits
Give each entity, department and product its own space, with its own evidence, documents and releases, then see where compliance stands across the whole group in one view.
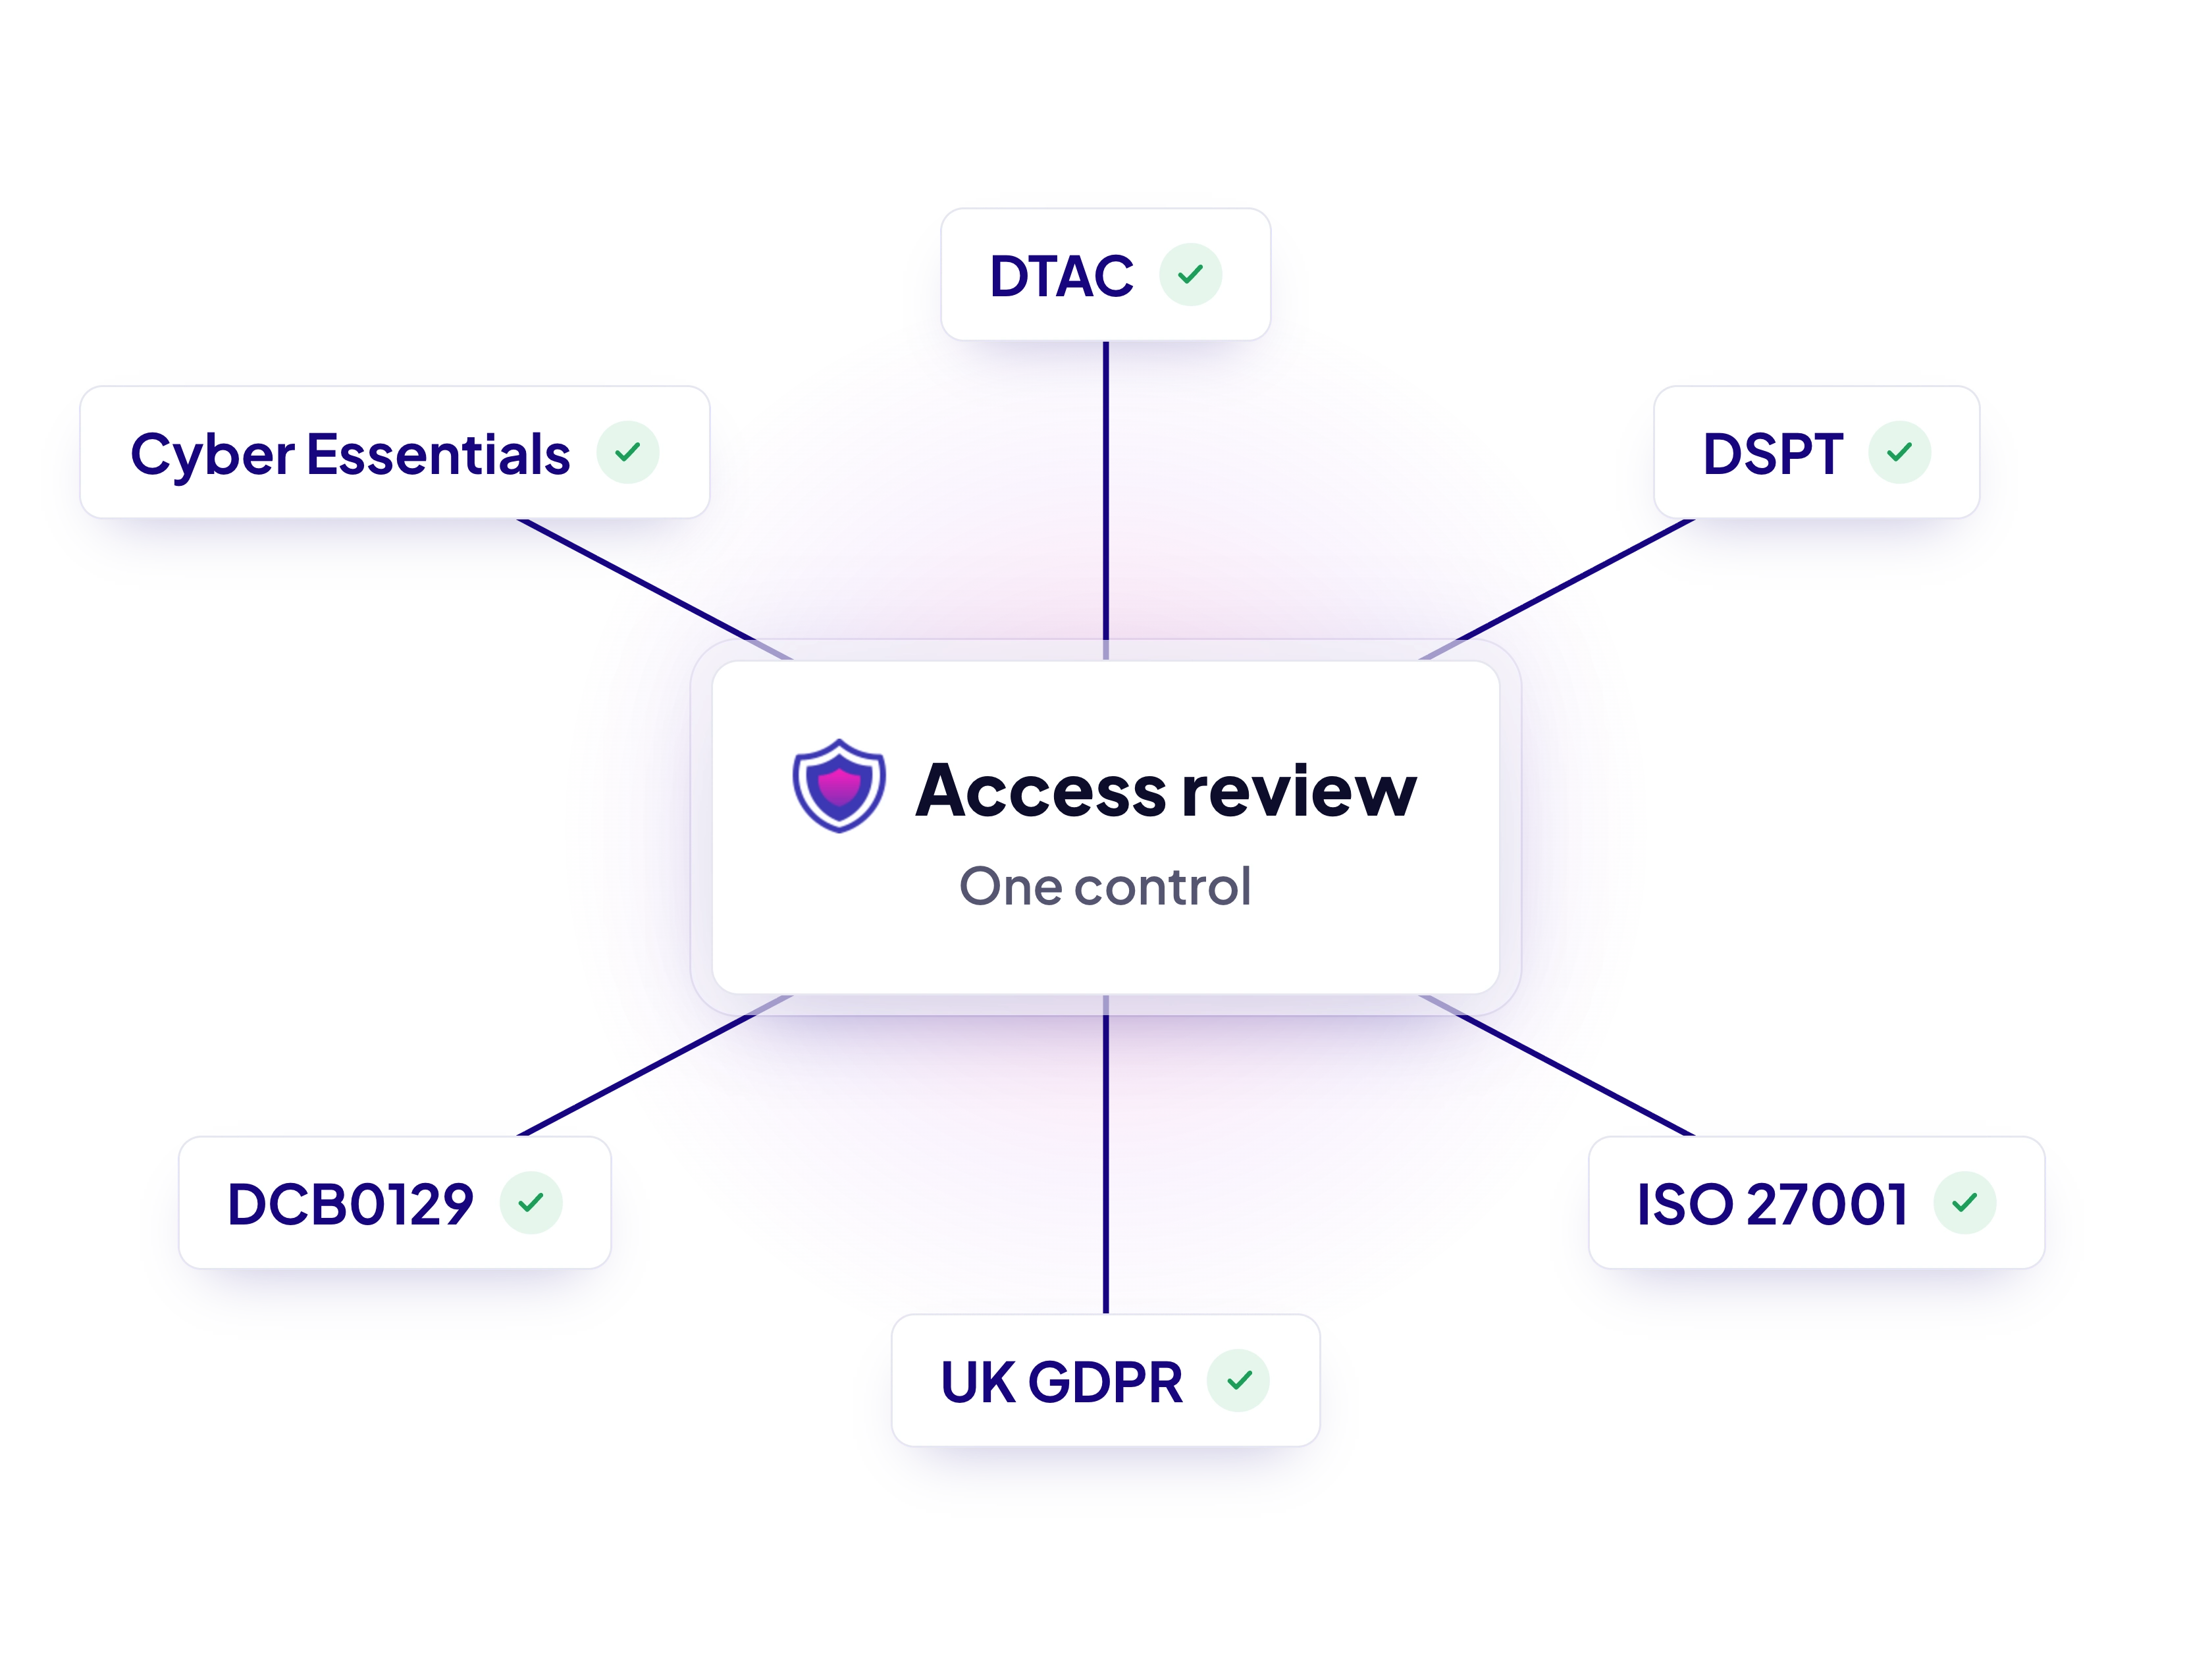
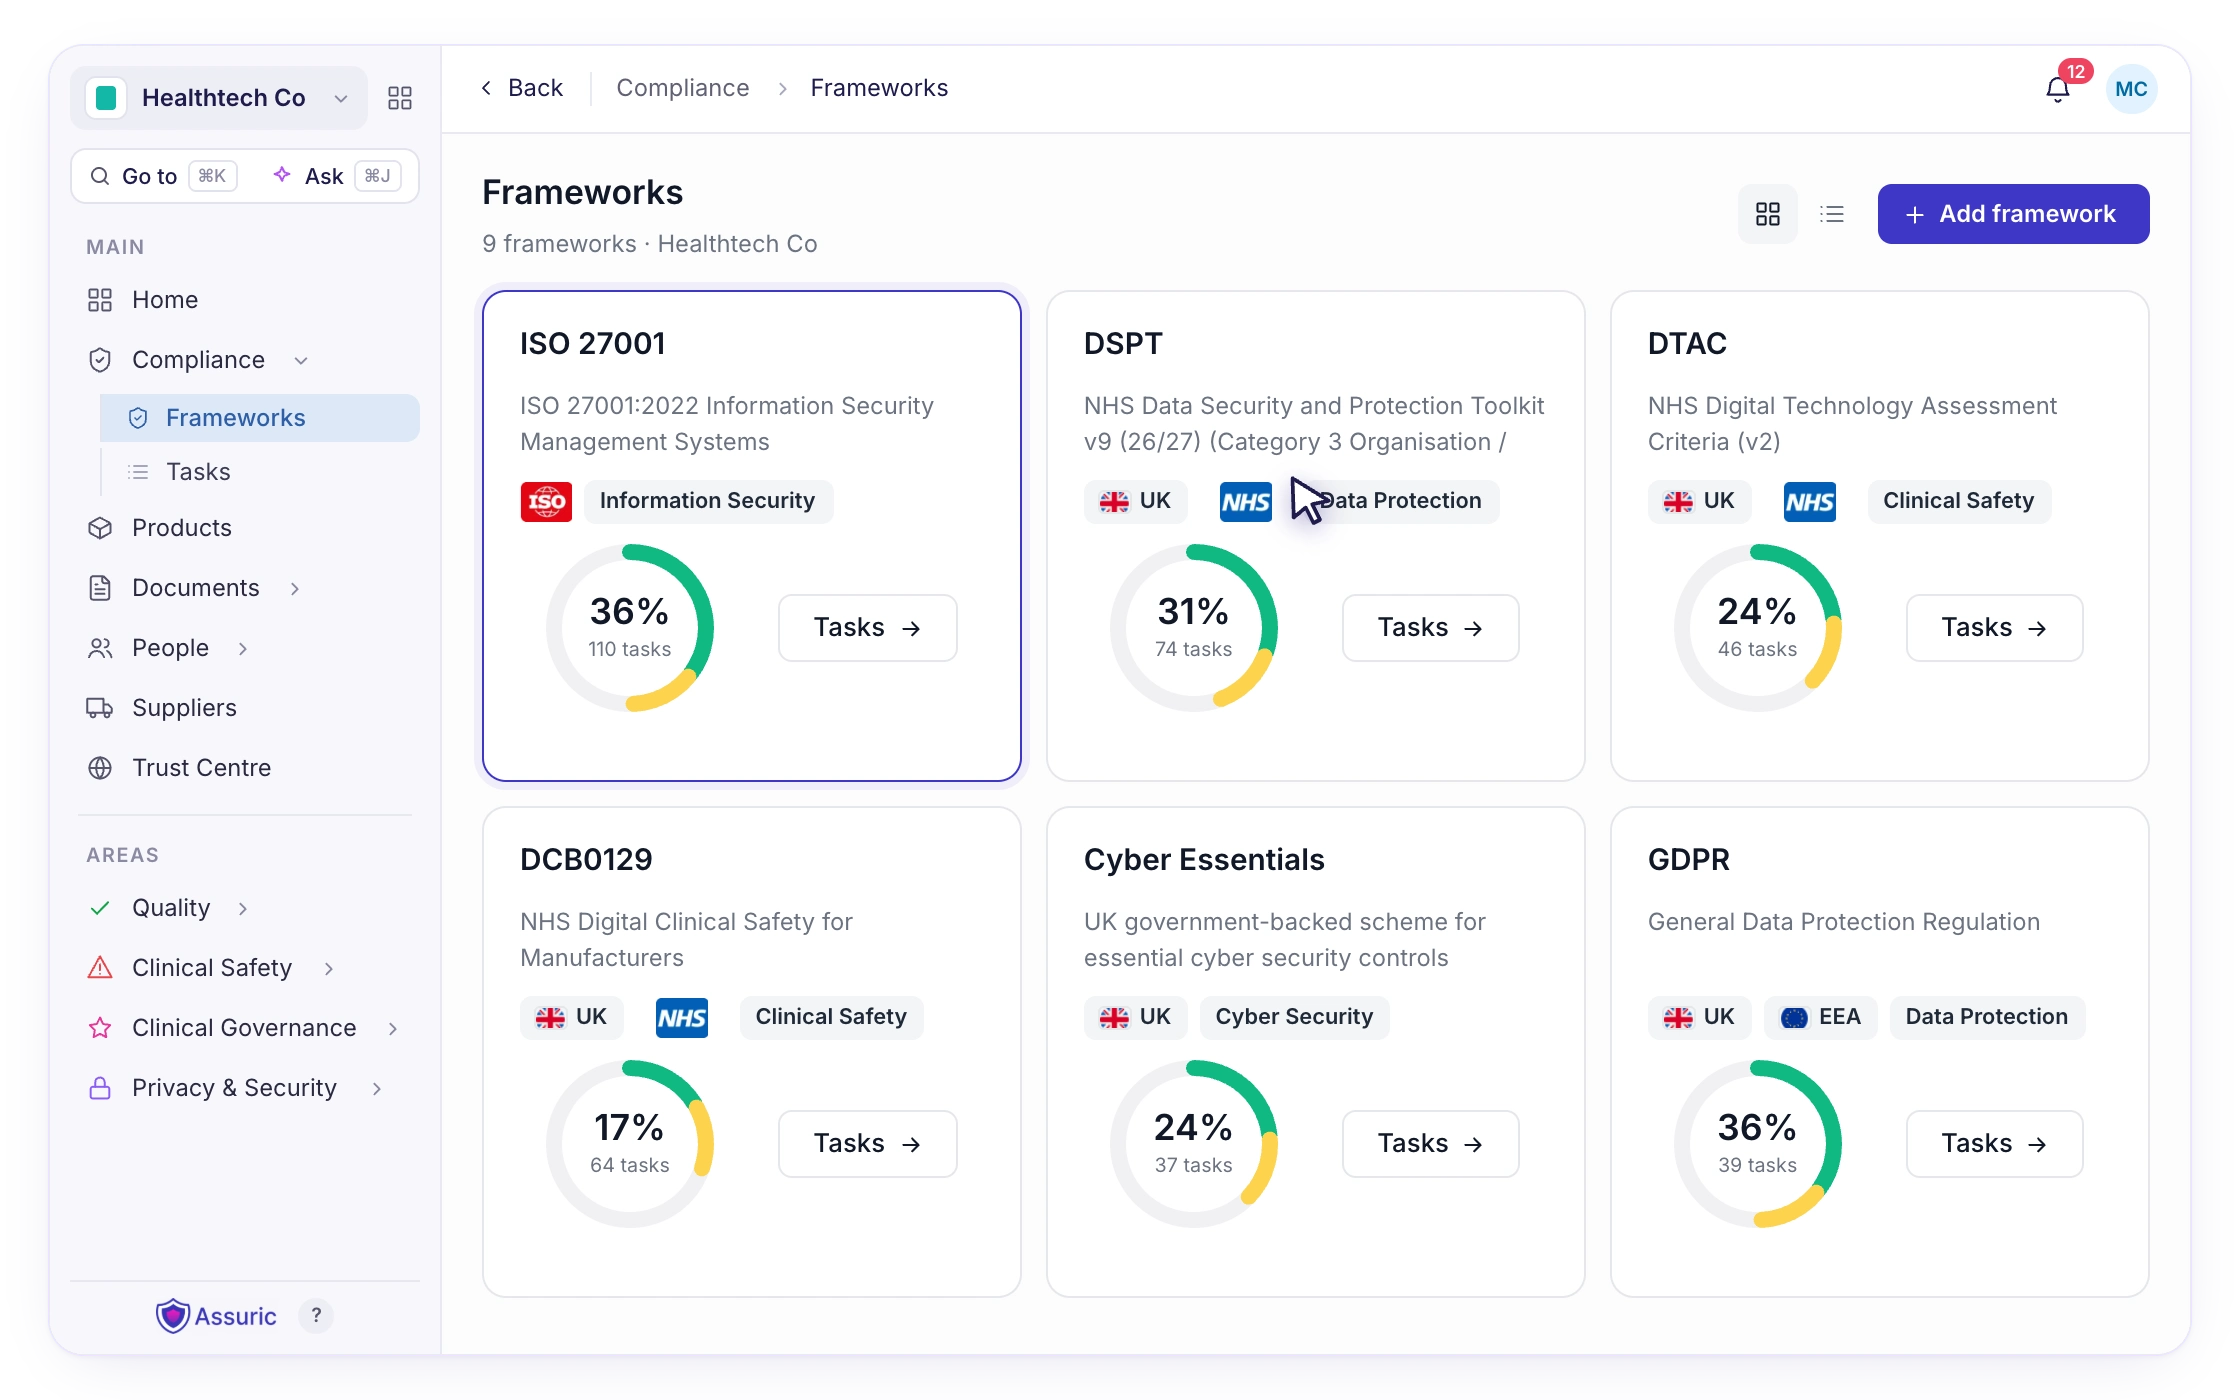
ISO, NHS, SaMD, data protection and international frameworks come cross-mapped, so one piece of evidence counts towards every standard that asks for it.
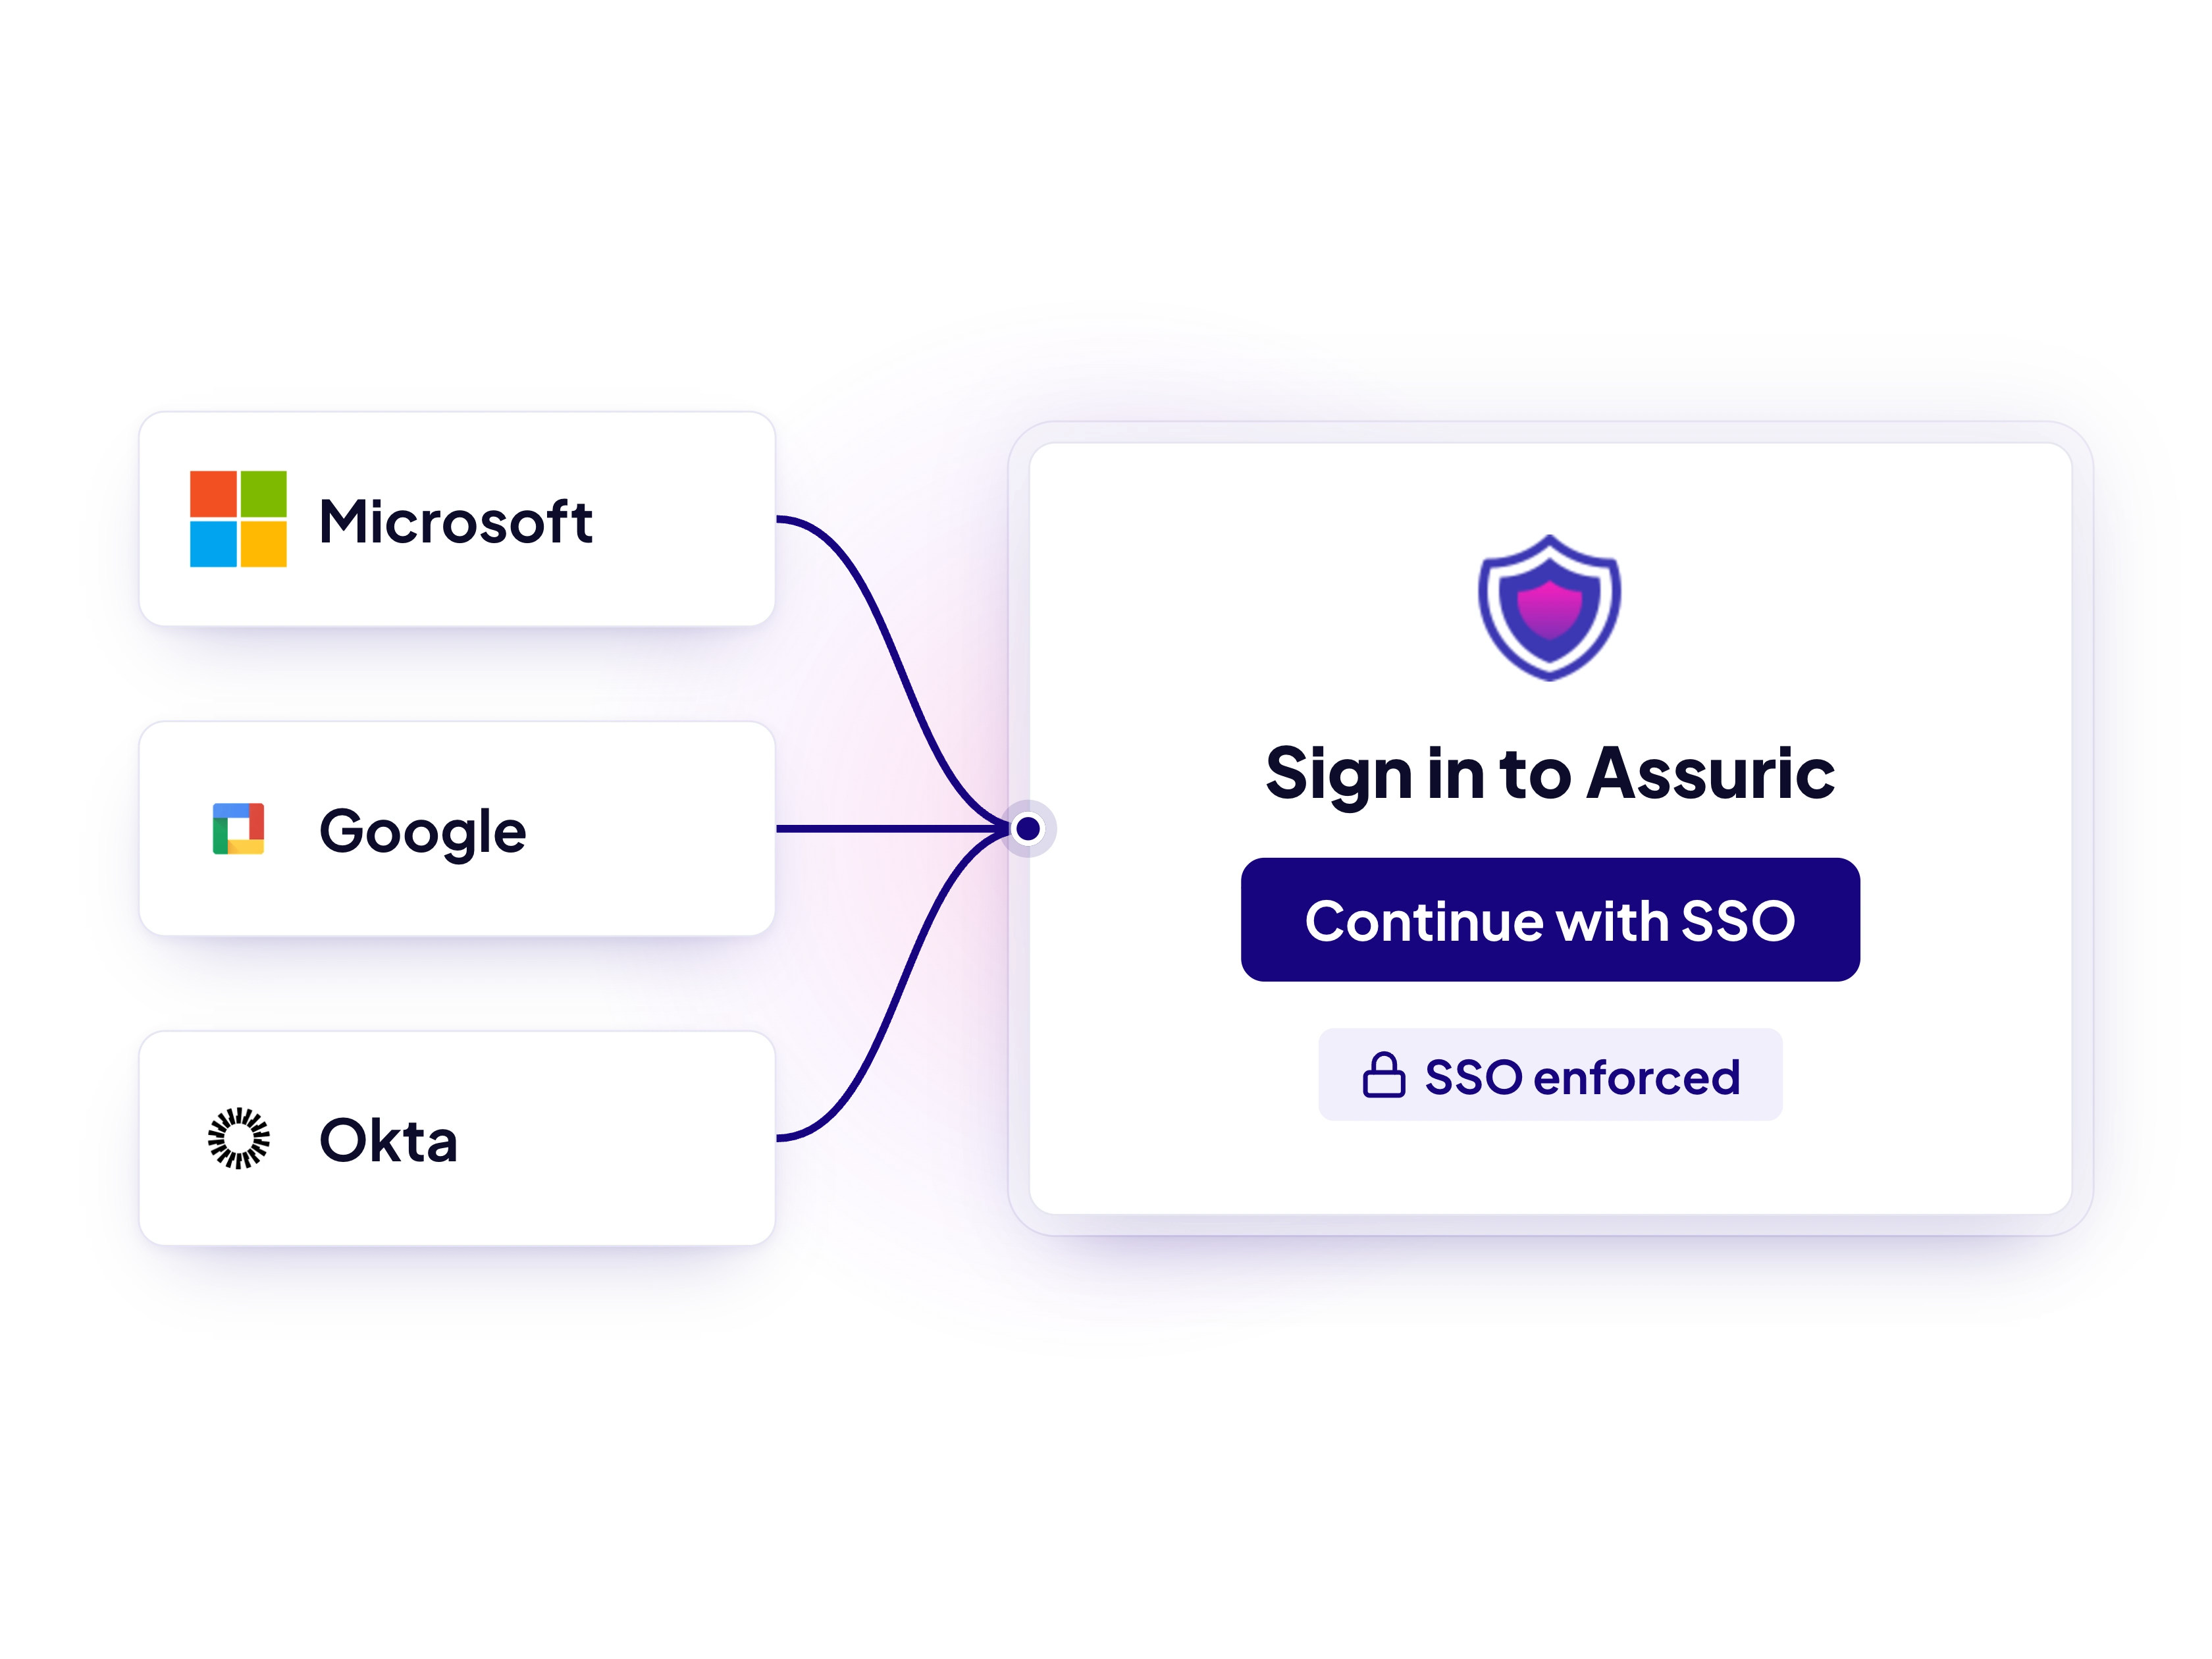
Connect your identity provider with single sign-on, and scope permissions by role, framework and record, so people only see, edit and approve what they own.
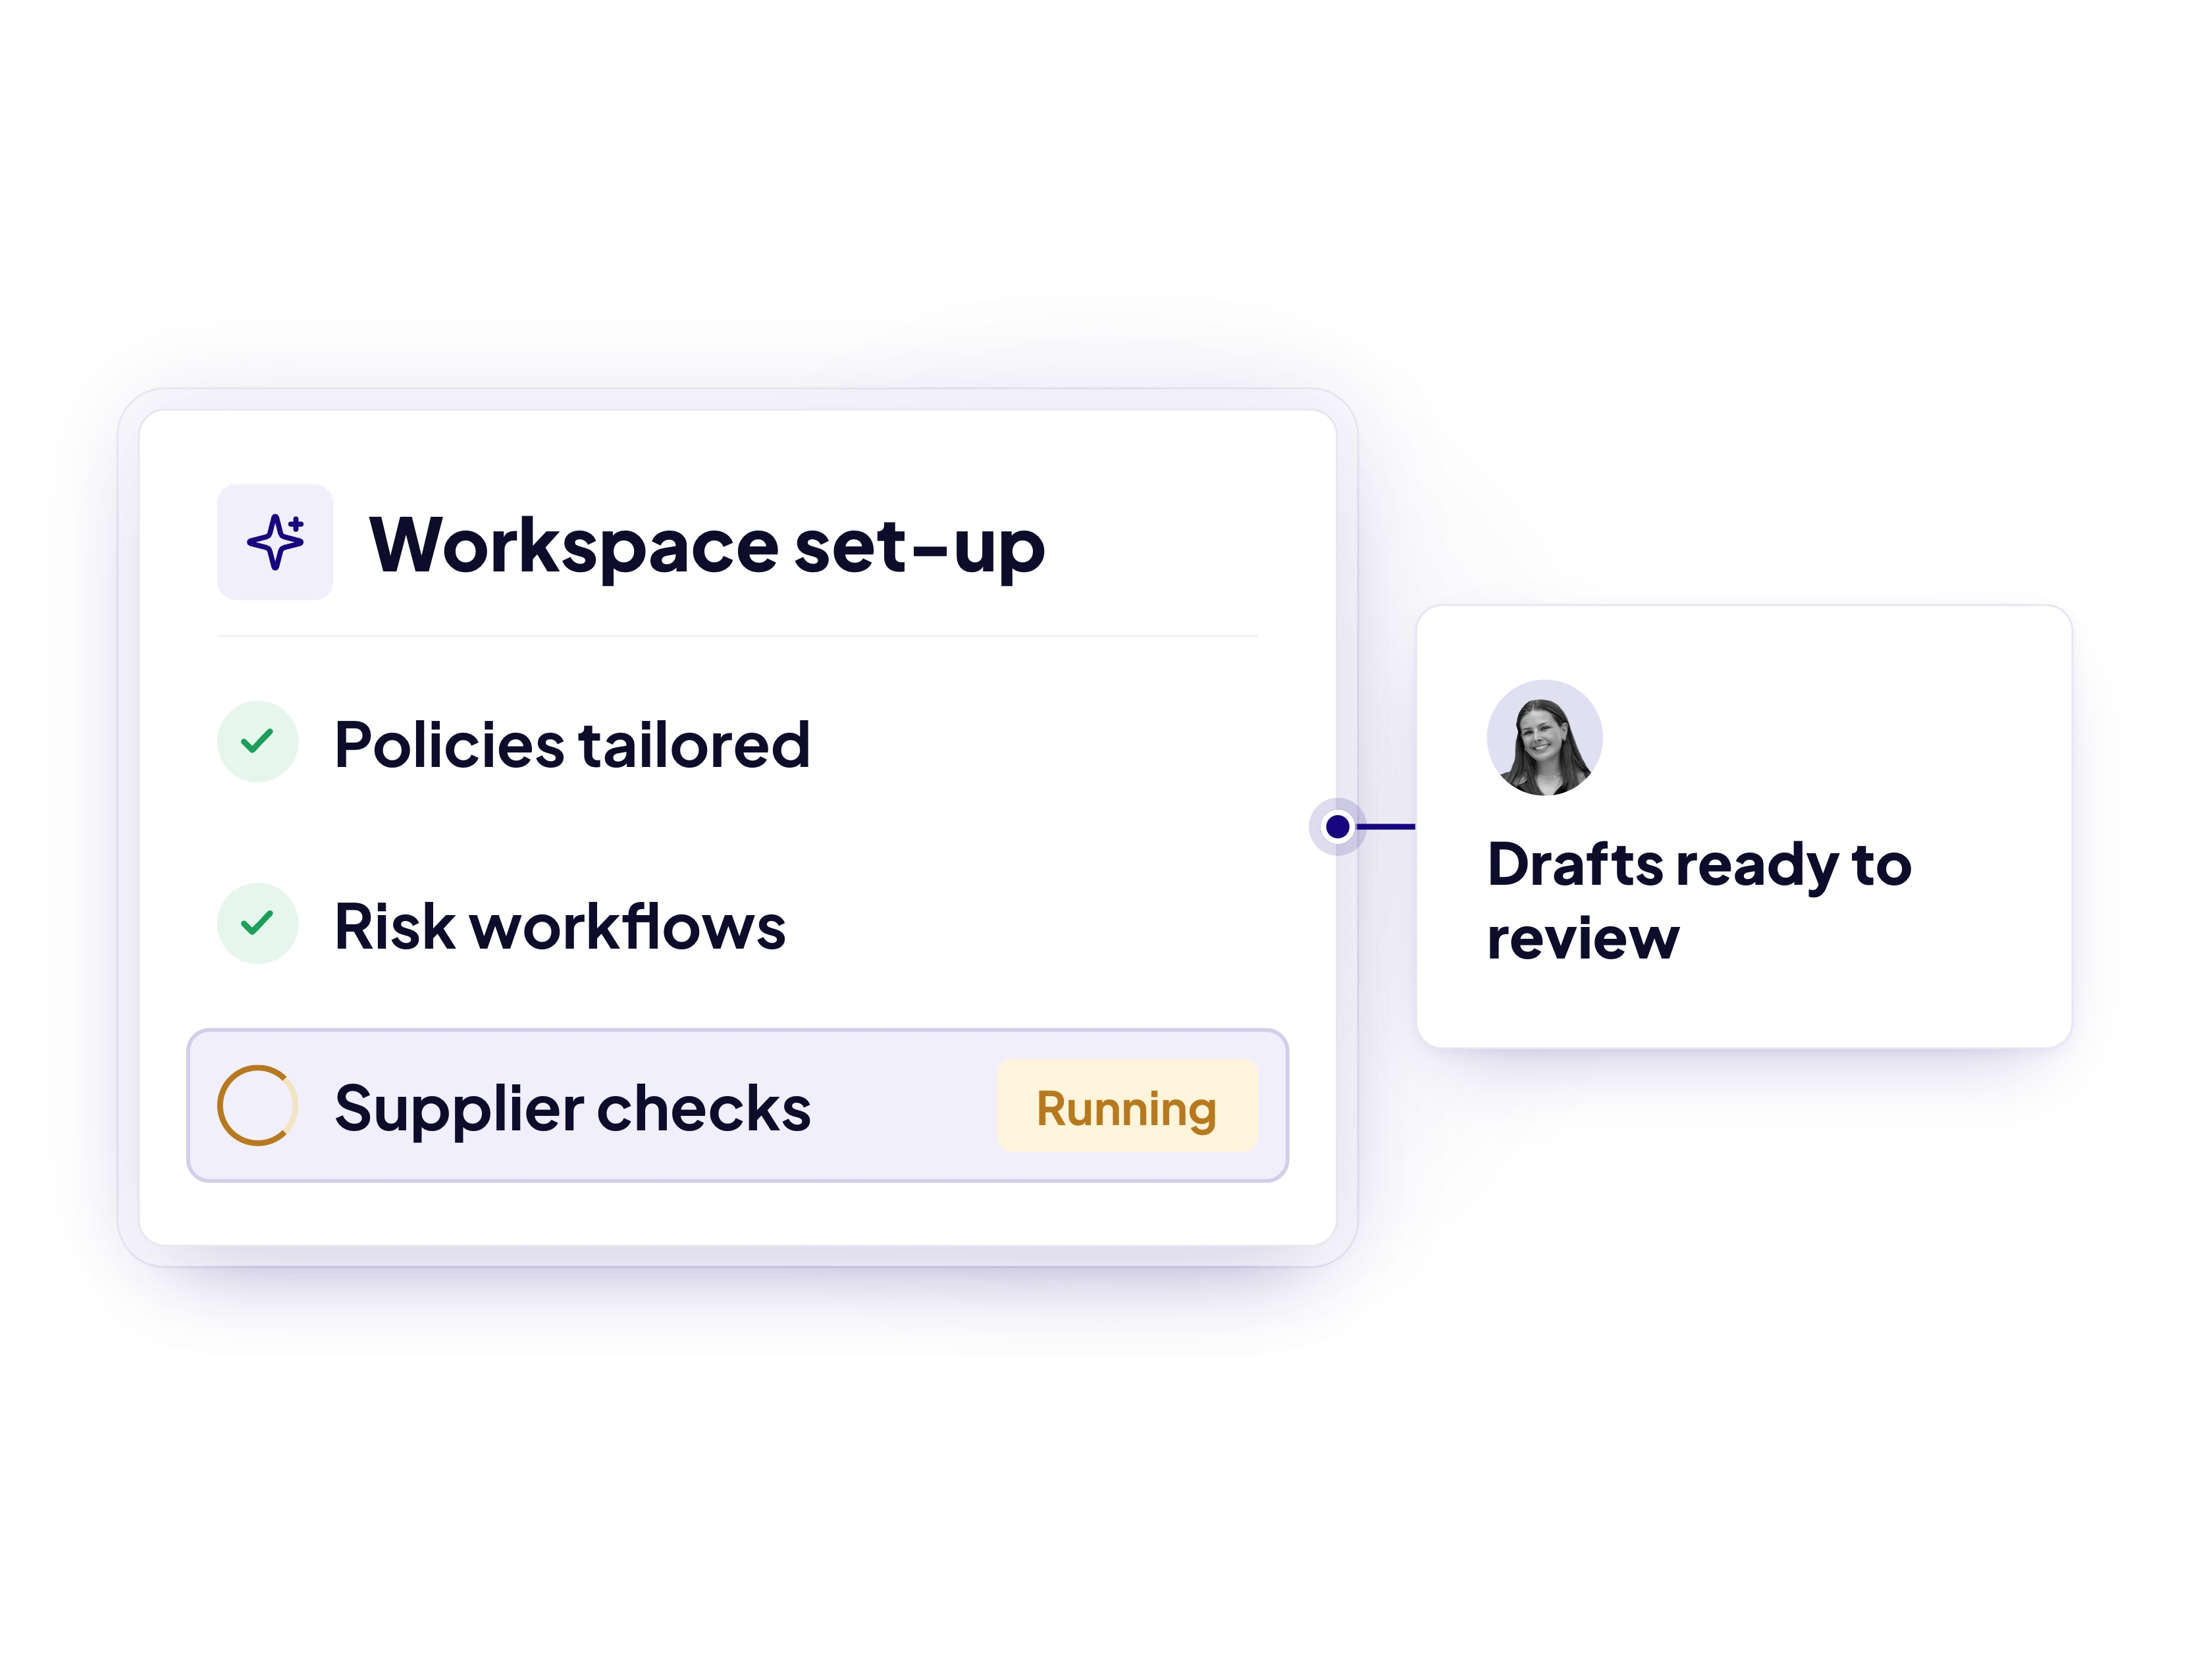
Agents review evidence, chase recurring tasks and keep records current, with every action approved by a named person and logged.
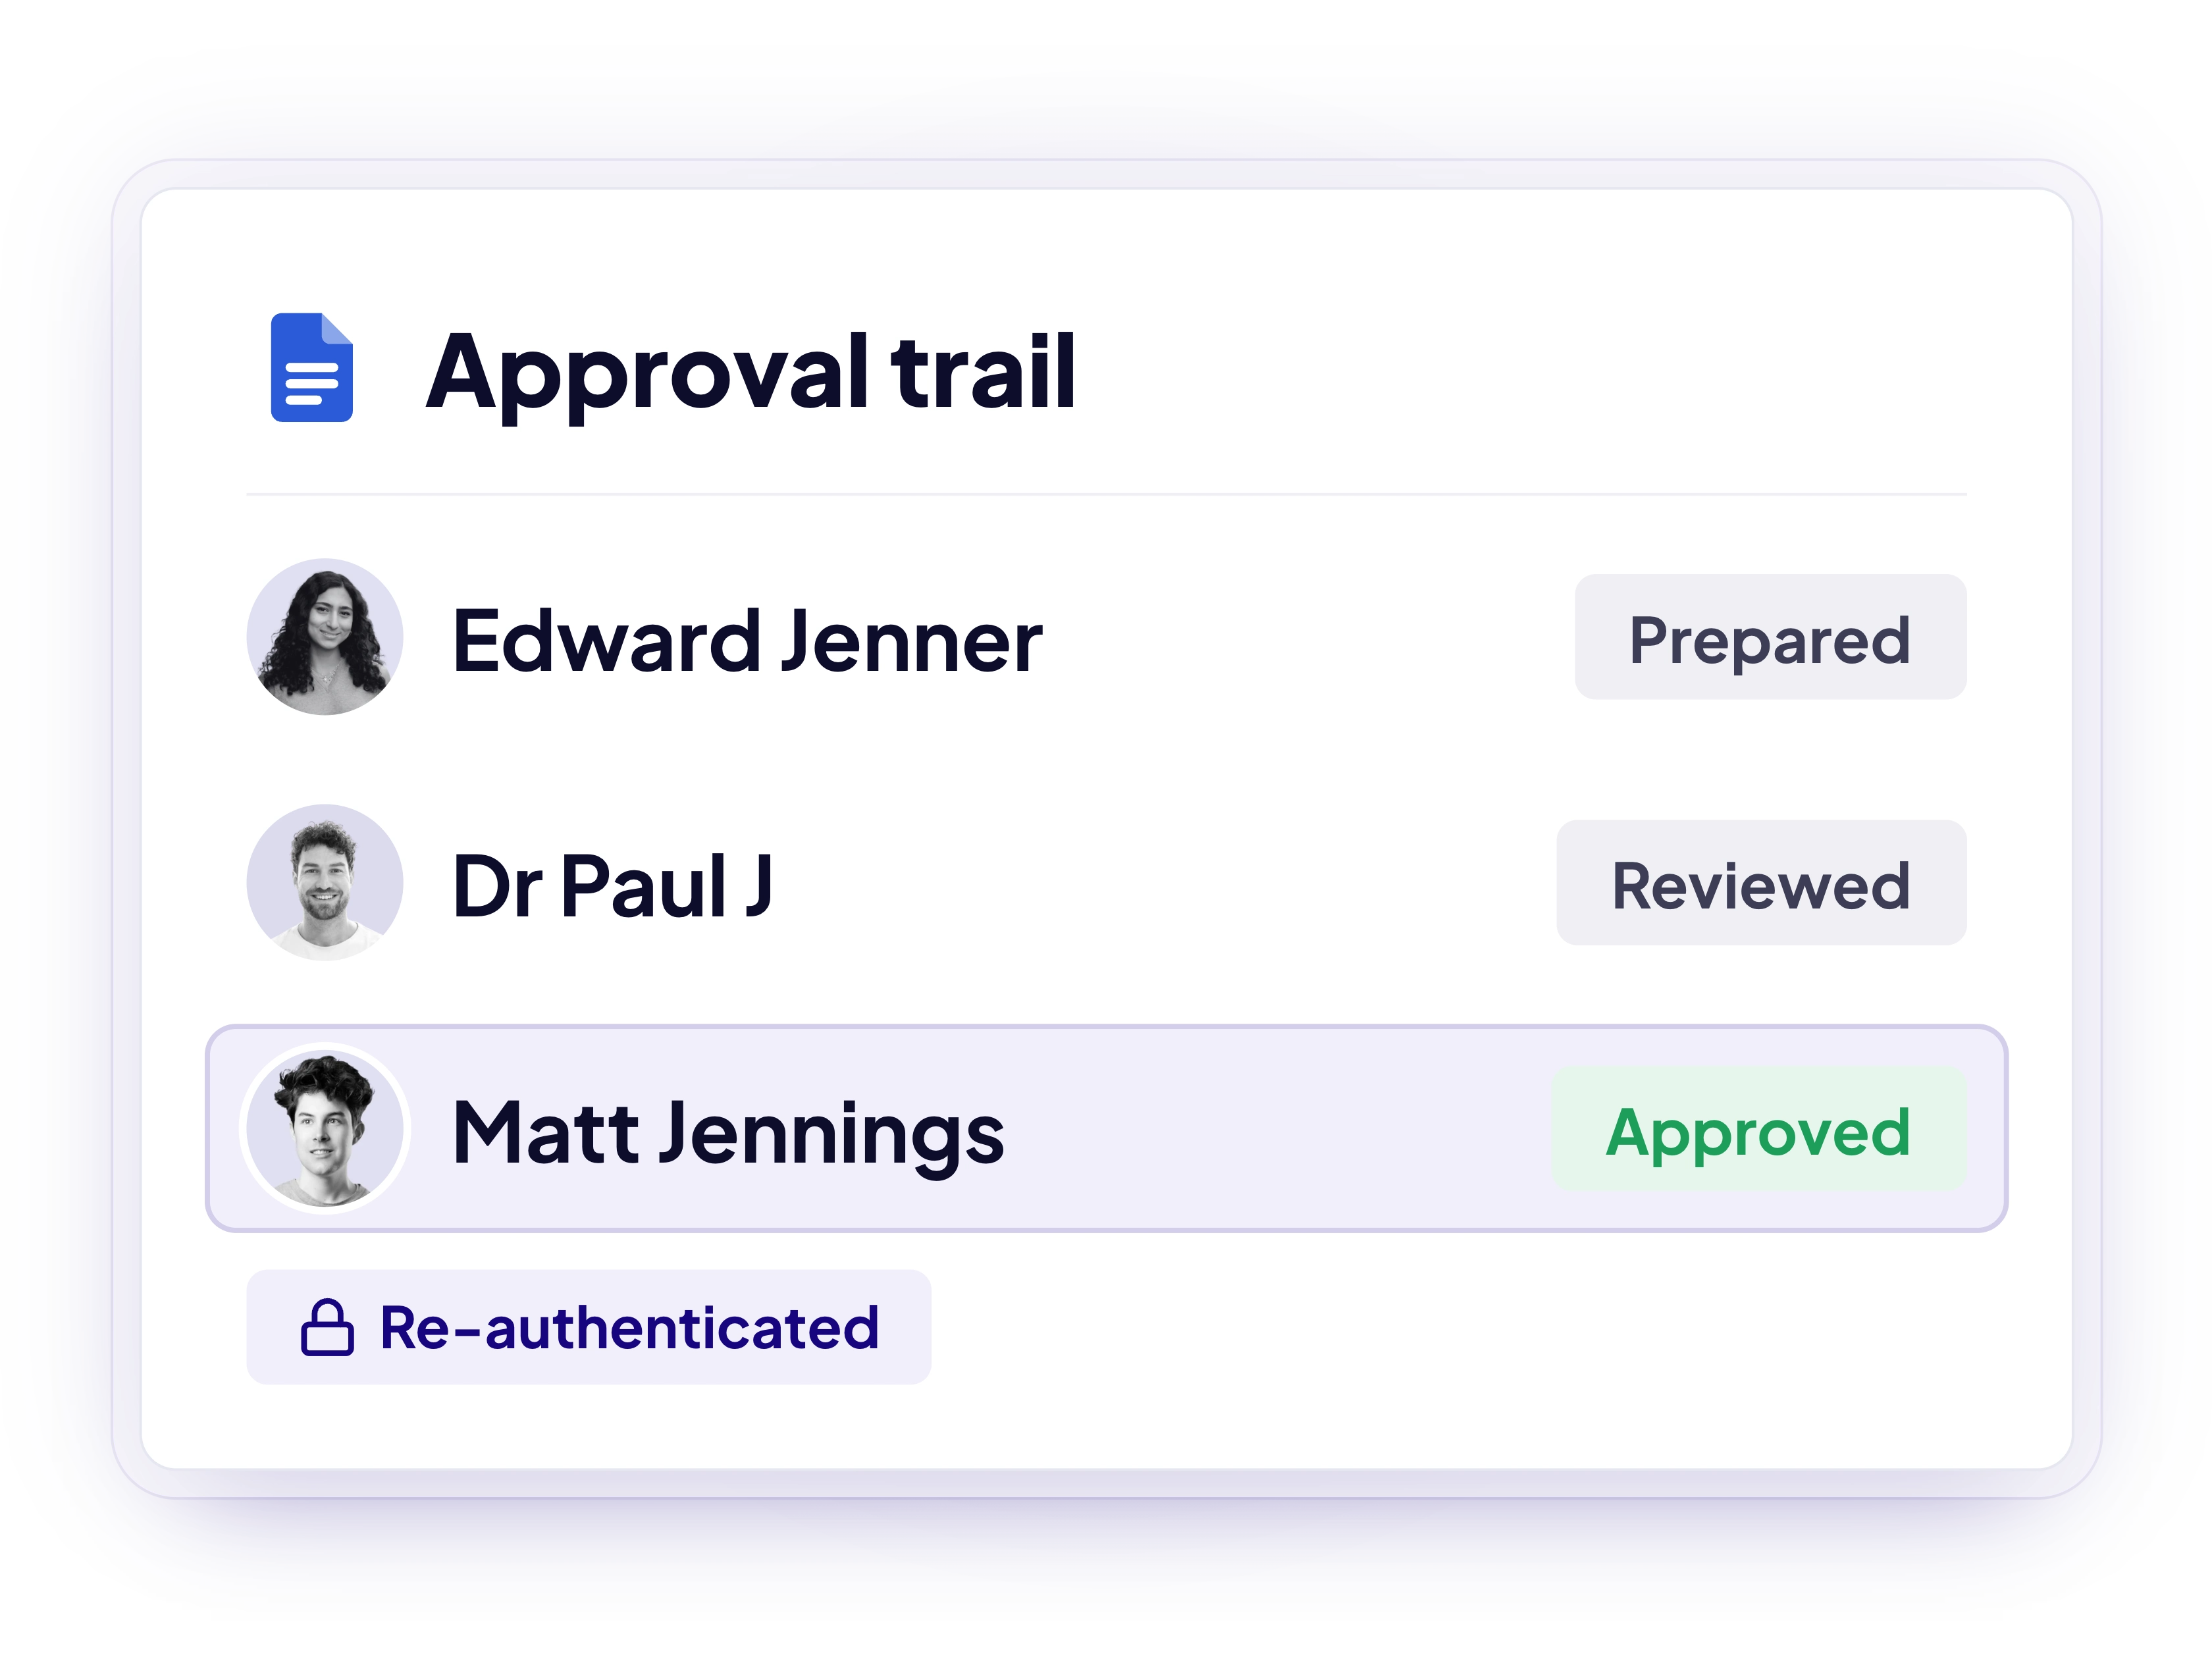
Every approval, change and signature is timestamped and attributable, so you can show auditors and regulated buyers exactly what happened and when.
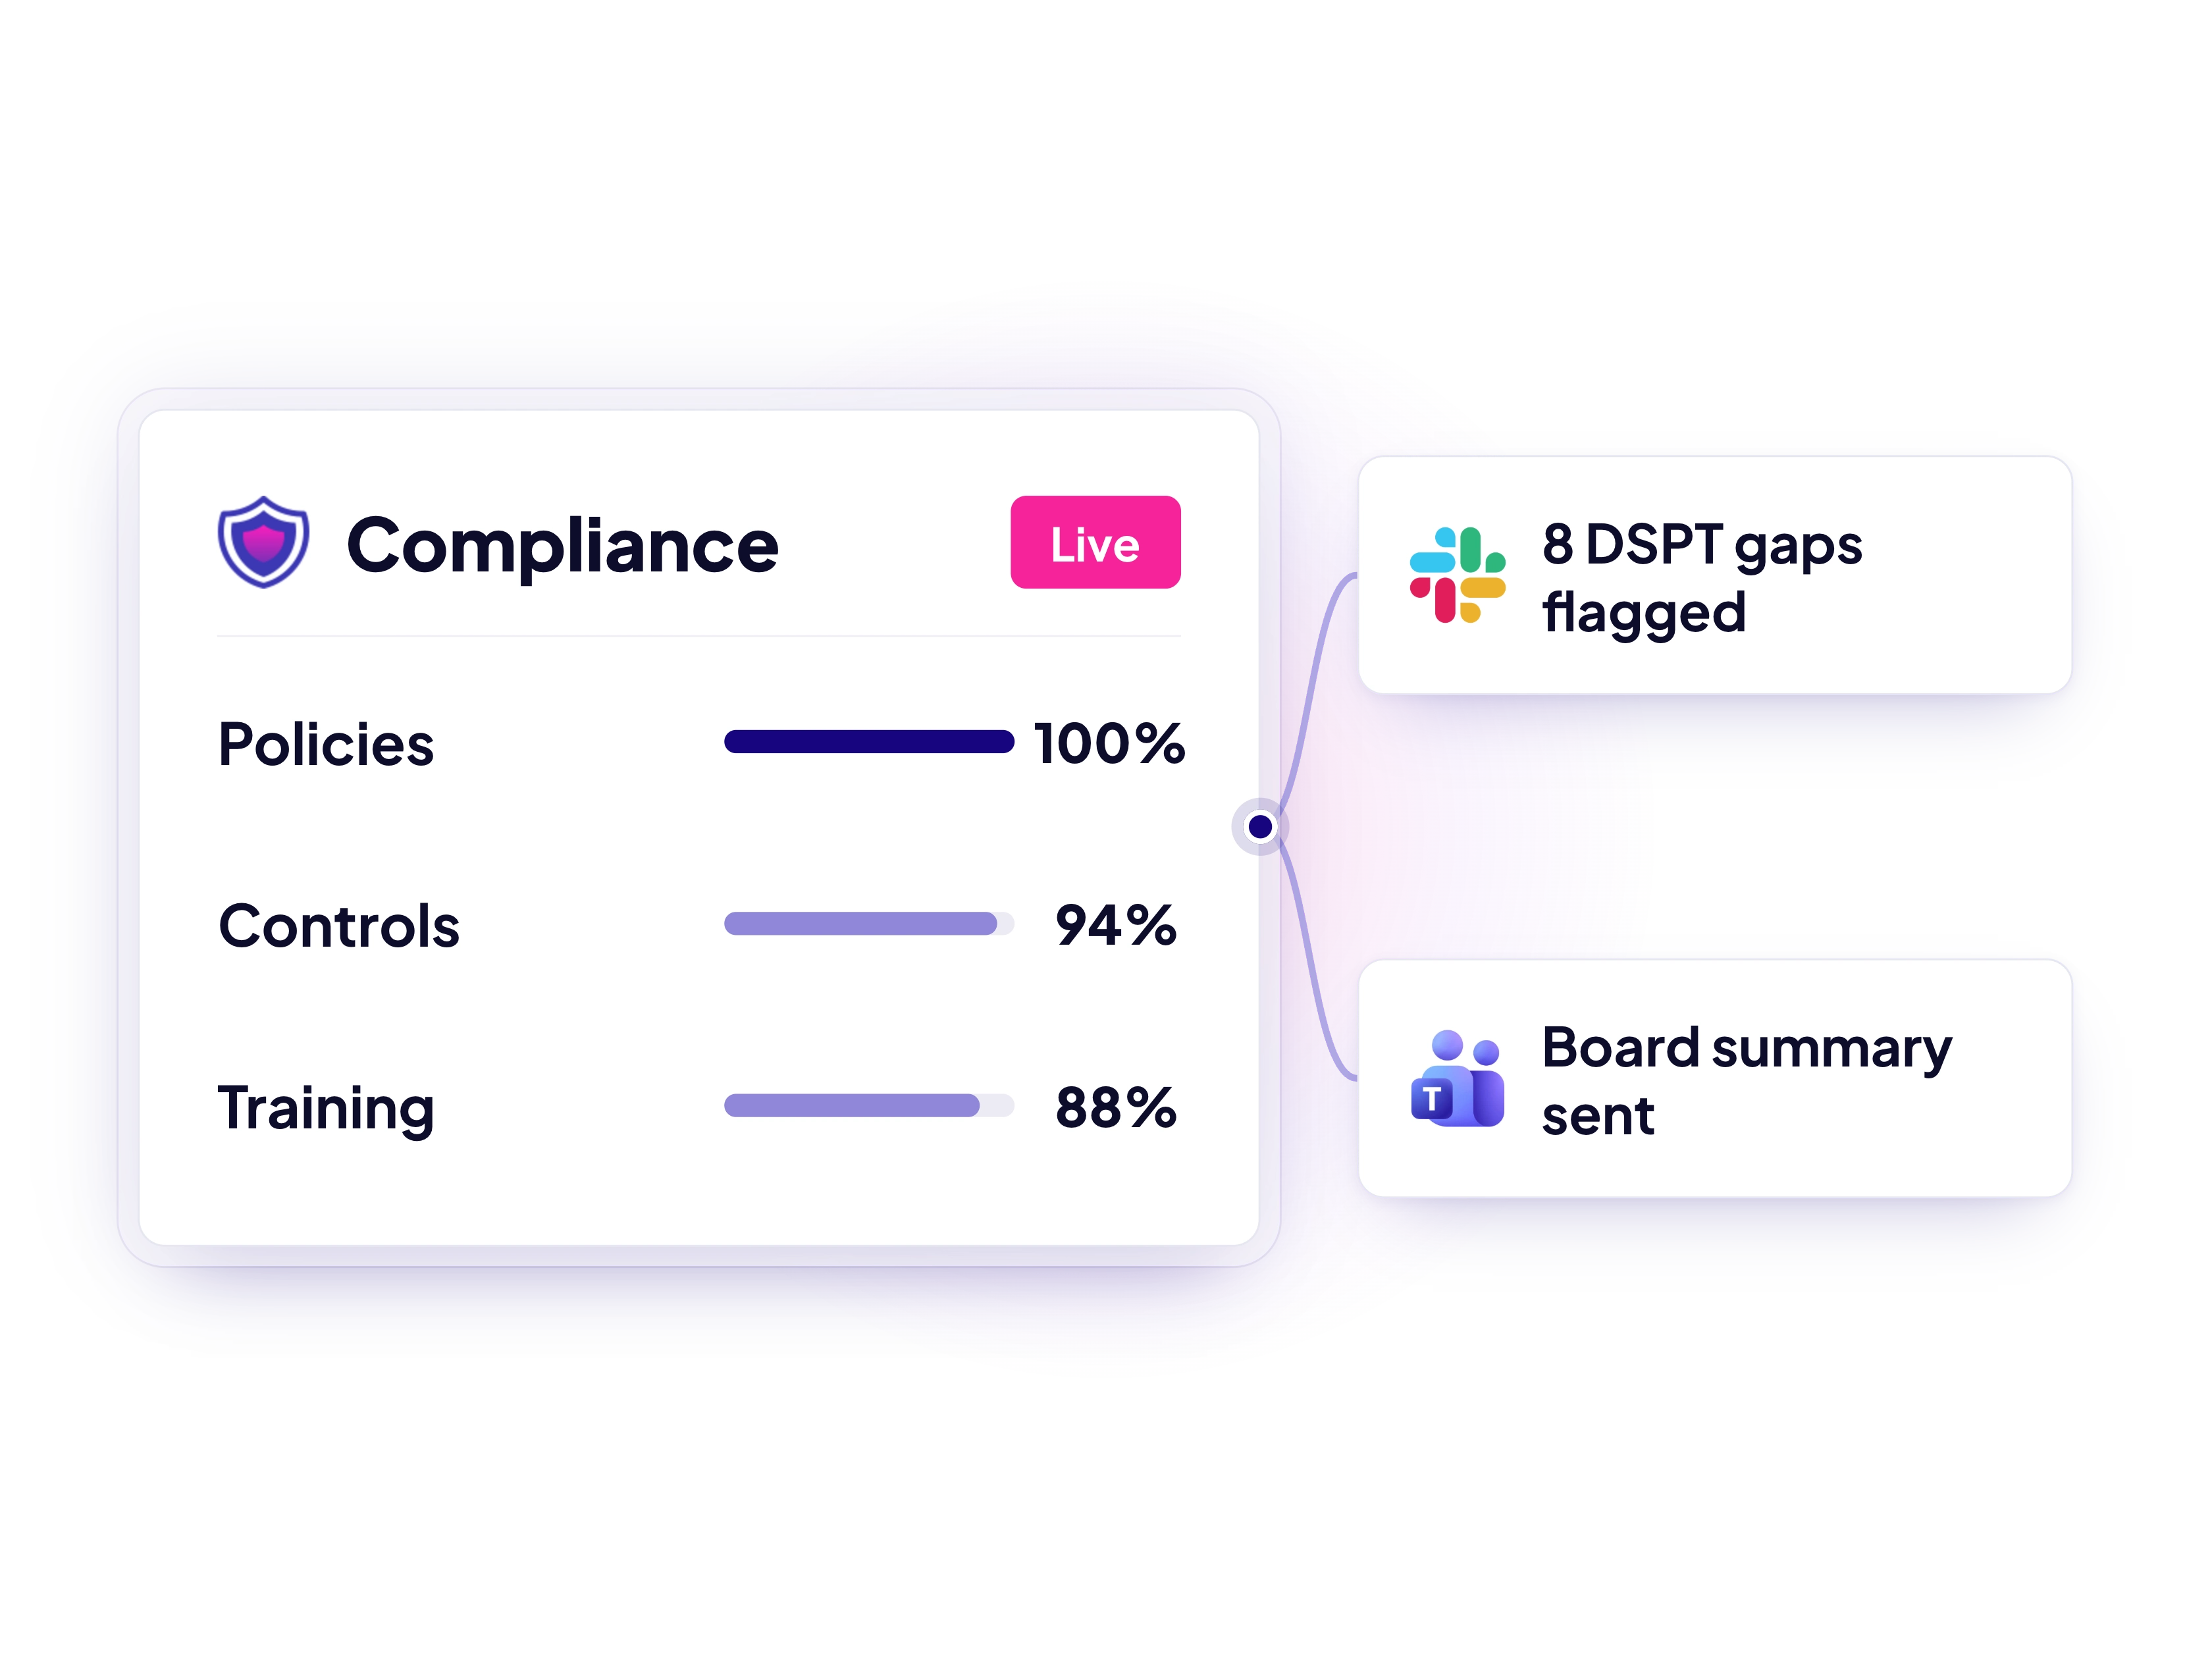
Turn live compliance data into clear reports for leadership, risk committees and buyers, without rebuilding spreadsheets each quarter.
Features
Every product your compliance, security and quality teams need, in one secure platform.
Automated compliance tracking
Control status, evidence and expiry dates across every framework and entity, with automatic alerts when something goes out of date, so nothing is found at audit time.

Document & policy management
Give each entity, department or product its own documents, owners, review dates and permissions, and share group-wide policies once, so everyone works from the right version.
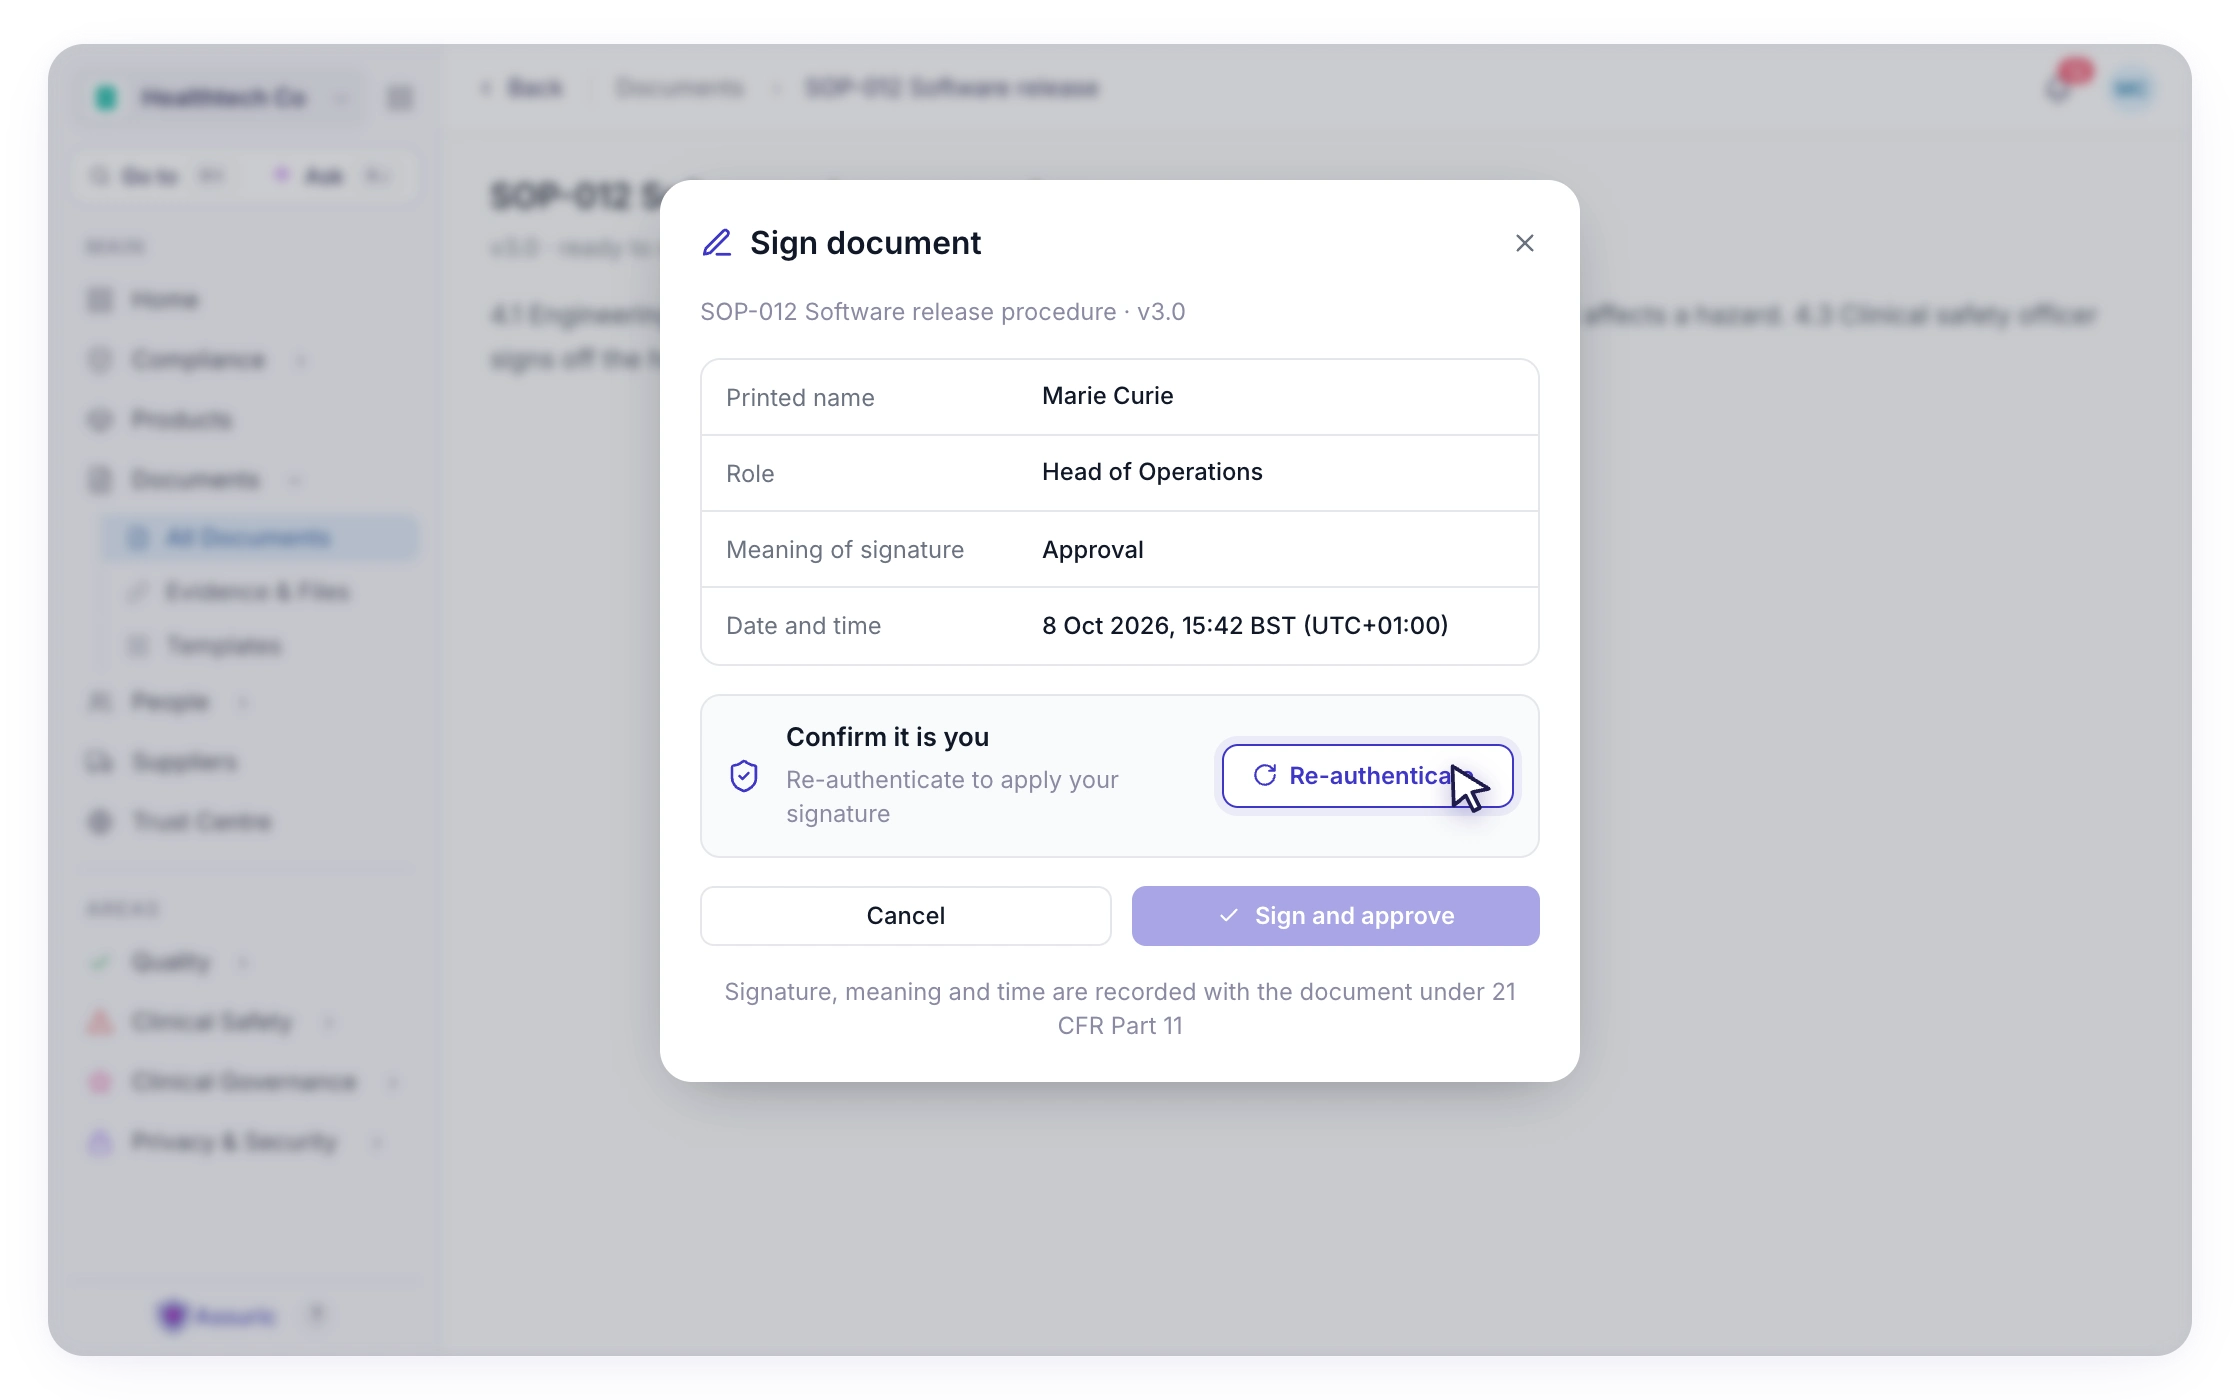
Electronic signatures
21 CFR Part 11 compliant e-signatures with custom approval flows for each document type, so regulated sign-offs happen in the platform, not in email.

Trust Centre
Publish certifications, policies and security documentation on your own branded Trust Centre, with gated access and automatic updates to subscribers.

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”
Maks Kozarzewski
COO, VitVio

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”
Paul Llewellyn
CCIO, Accenture

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”
Katie Baker
Director UK & Ireland, Tandem
Each product in Assuric has its own evidence, documents, releases and change management, while shared controls are evidenced once and inherited by every product that needs them. You get one view of compliance across every product, framework and market, instead of separate systems and spreadsheets for each.
Yes. Assuric is ISO 27001 certified by a UKAS-accredited certification body, holds Cyber Essentials Plus, and exceeds the NHS DSPT standards. The platform supports single sign-on (SSO) through your identity provider, granular roles and permissions for each framework, area and record type, and a full, timestamped audit trail of who did what and when, so teams only see, edit and approve the records they own. Our certifications and security documentation are published on our Trust Centre.
Yes. Assuric connects to Google Drive and SharePoint to import and manage your documents, supports working in Word and Google Docs, brings compliance updates into Slack, and links to your identity provider for single sign-on. Custom integrations with your own systems can be scoped with our team.
Yes. Assuric records who approved what, when, and against which version of the document, with 21 CFR Part 11 compliant electronic signatures and an audit trail that cannot be edited or deleted. That is the record auditors and regulated buyers ask for first.
Yes. Controls are mapped once across every framework, so a single piece of evidence counts towards ISO 27001, SOC 2, HIPAA and UK frameworks such as DSPT at the same time. That makes adding a new market a mapping exercise rather than a new project.
Yes. The Assuric MCP server lets Claude, ChatGPT, Copilot or Cursor read and update your compliance records from the tools your teams already use. Every action stays within each person’s permissions and is logged.
Yes. Our fractional CSO and DPO services give you named, experienced specialists on retainer. They work inside your Assuric workspace, so sign-offs, incidents and data protection questions are handled where the evidence lives.
Featured post
Learn how Model Context Protocol (MCP) enables AI-powered compliance, continuous monitoring, and secure access to regulatory data for digital health teams

See how Assuric brings every entity, department, product, framework and jurisdiction into one comprehensive system.


