All-in-one compliance
for NHS suppliers

Everything NHS procurement and assurance asks for, from DTAC and DSPT to DCB0129 and IG sign-off, prepared once and reused for every trust.

  • Complete NHS DTAC compliance
  • DCB0129 and named CSOs available
  • DPIAs, DSPT and Cyber Essentials
  • ISO standards needed for larger procurement

By continuing you agree to our privacy notice

AccurxTandemSembleLimbicBraiveDrDoctorCircle Health GroupNorthern Care Alliance NHS Foundation TrustCleo SystemsCorelineGuardantSanomePolyAIEolas MedicalChequpHeimDelfaHippo LabsInfixMegiNursebuddyOnion AIRhazesRosenfieldSurgery AIHealthnixThink DivergentHestaVitVioUniversity Hospitals of Derby and Burton NHS Foundation TrustAnimaAscentiAsterixEvergreen LifeHello PatientHealthtech-1Modality PartnershipNHS Wales Performance & ImprovementCwm Taf Morgannwg University Health BoardOperose HealthPatient Care Locally CIC (LLR)Theta SleepAccentureCareStackSouth Warwickshire University NHS Foundation TrustUniversity Hospitals of Leicester NHS TrustMersey and West Lancashire Teaching Hospitals NHS TrustWeymouth Bay Medical PracticeNottingham CityCare PartnershipMid Mersey Digital AlliancePenrose Health

Benefits

Be ready for NHS deployment

Complete DTAC from work you’ve already done

Clinical safety, data protection, technical security, usability and interoperability each draw on evidence you already hold for DSPT, Cyber Essentials, UK GDPR and DCB0129, so DTAC is assembled, not started from scratch.
F86 — Every answer cited

Get DCB0129 sign-off and NHS clinical safety approval

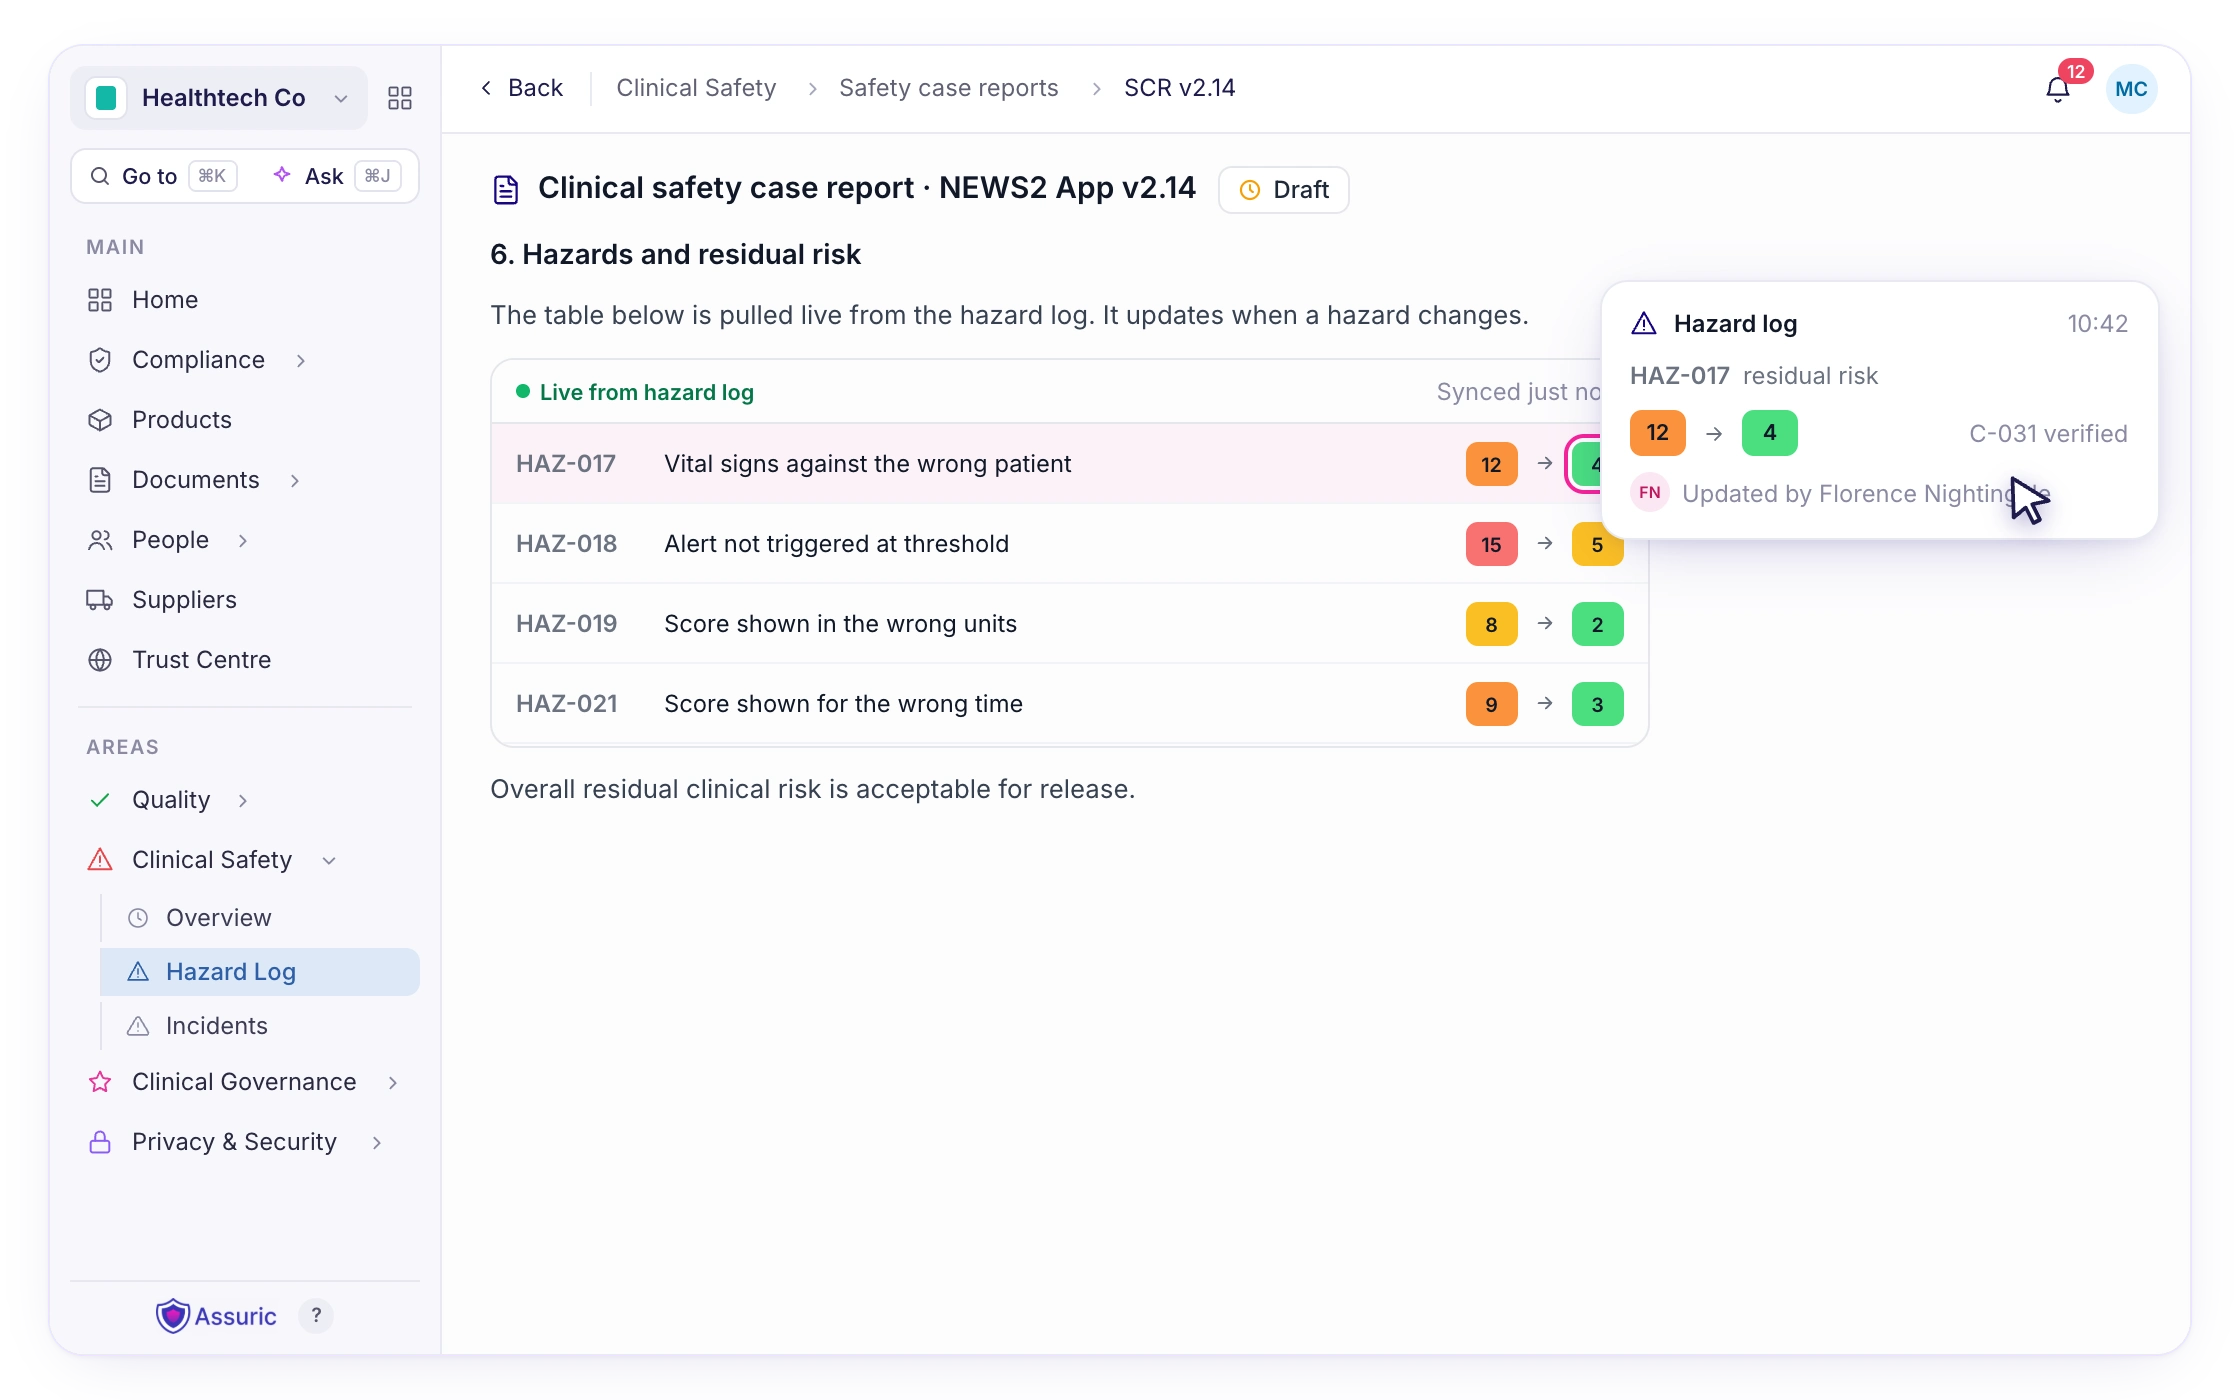
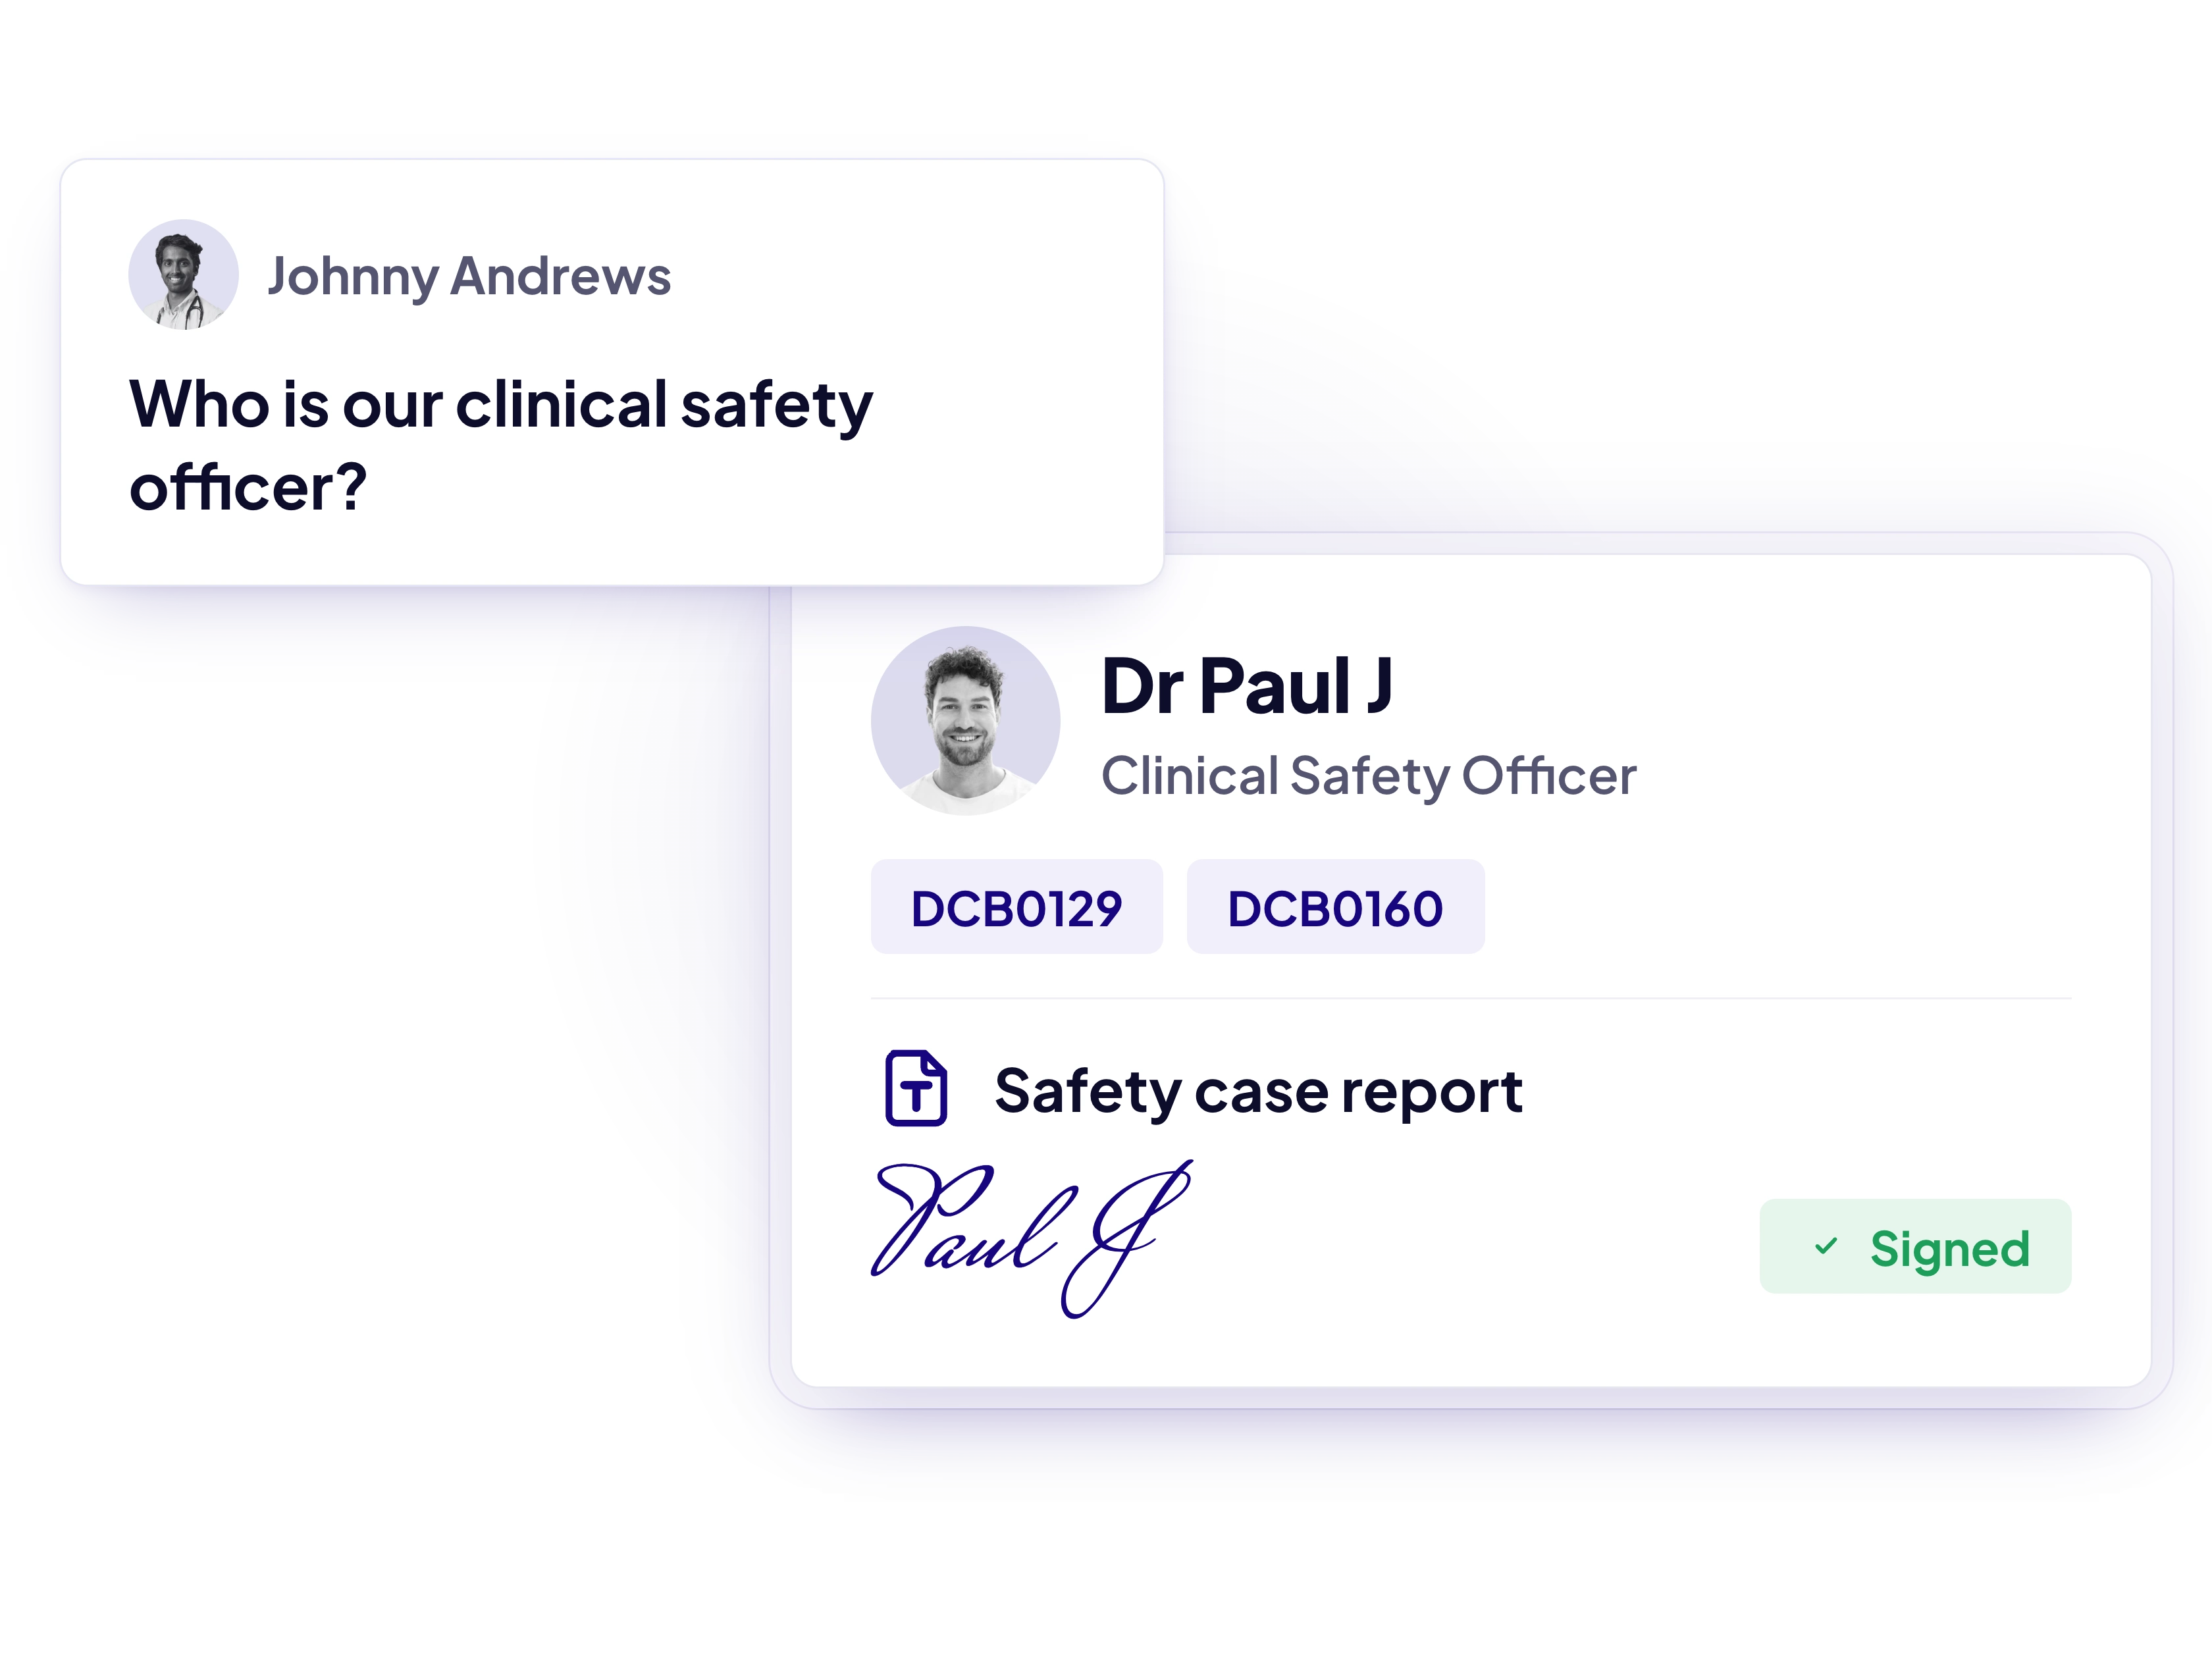
Your hazard log and safety case are kept current and signed off by a named Clinical Safety Officer, giving each trust what its own clinical safety team needs to approve deployment under DCB0160.

F087 — Safety case signed by CSO

Get NHS information governance sign-off

Prepare DPIAs and IG evidence the way NHS information governance teams expect, generated from the information already in Assuric and reviewed by our Data Protection Officers, so IG sign-off does not hold up deployment.

F49 — DPO review on a DPIA

Share evidence and build trust

Publish your DTAC, DSPT status, certifications and policies on your Trust Centre, so every trust can check your evidence in one place and procurement starts from what is already published, not a new request each time.

V36 — Trust Centre buyer view

AI that answers questionnaires and keeps records current

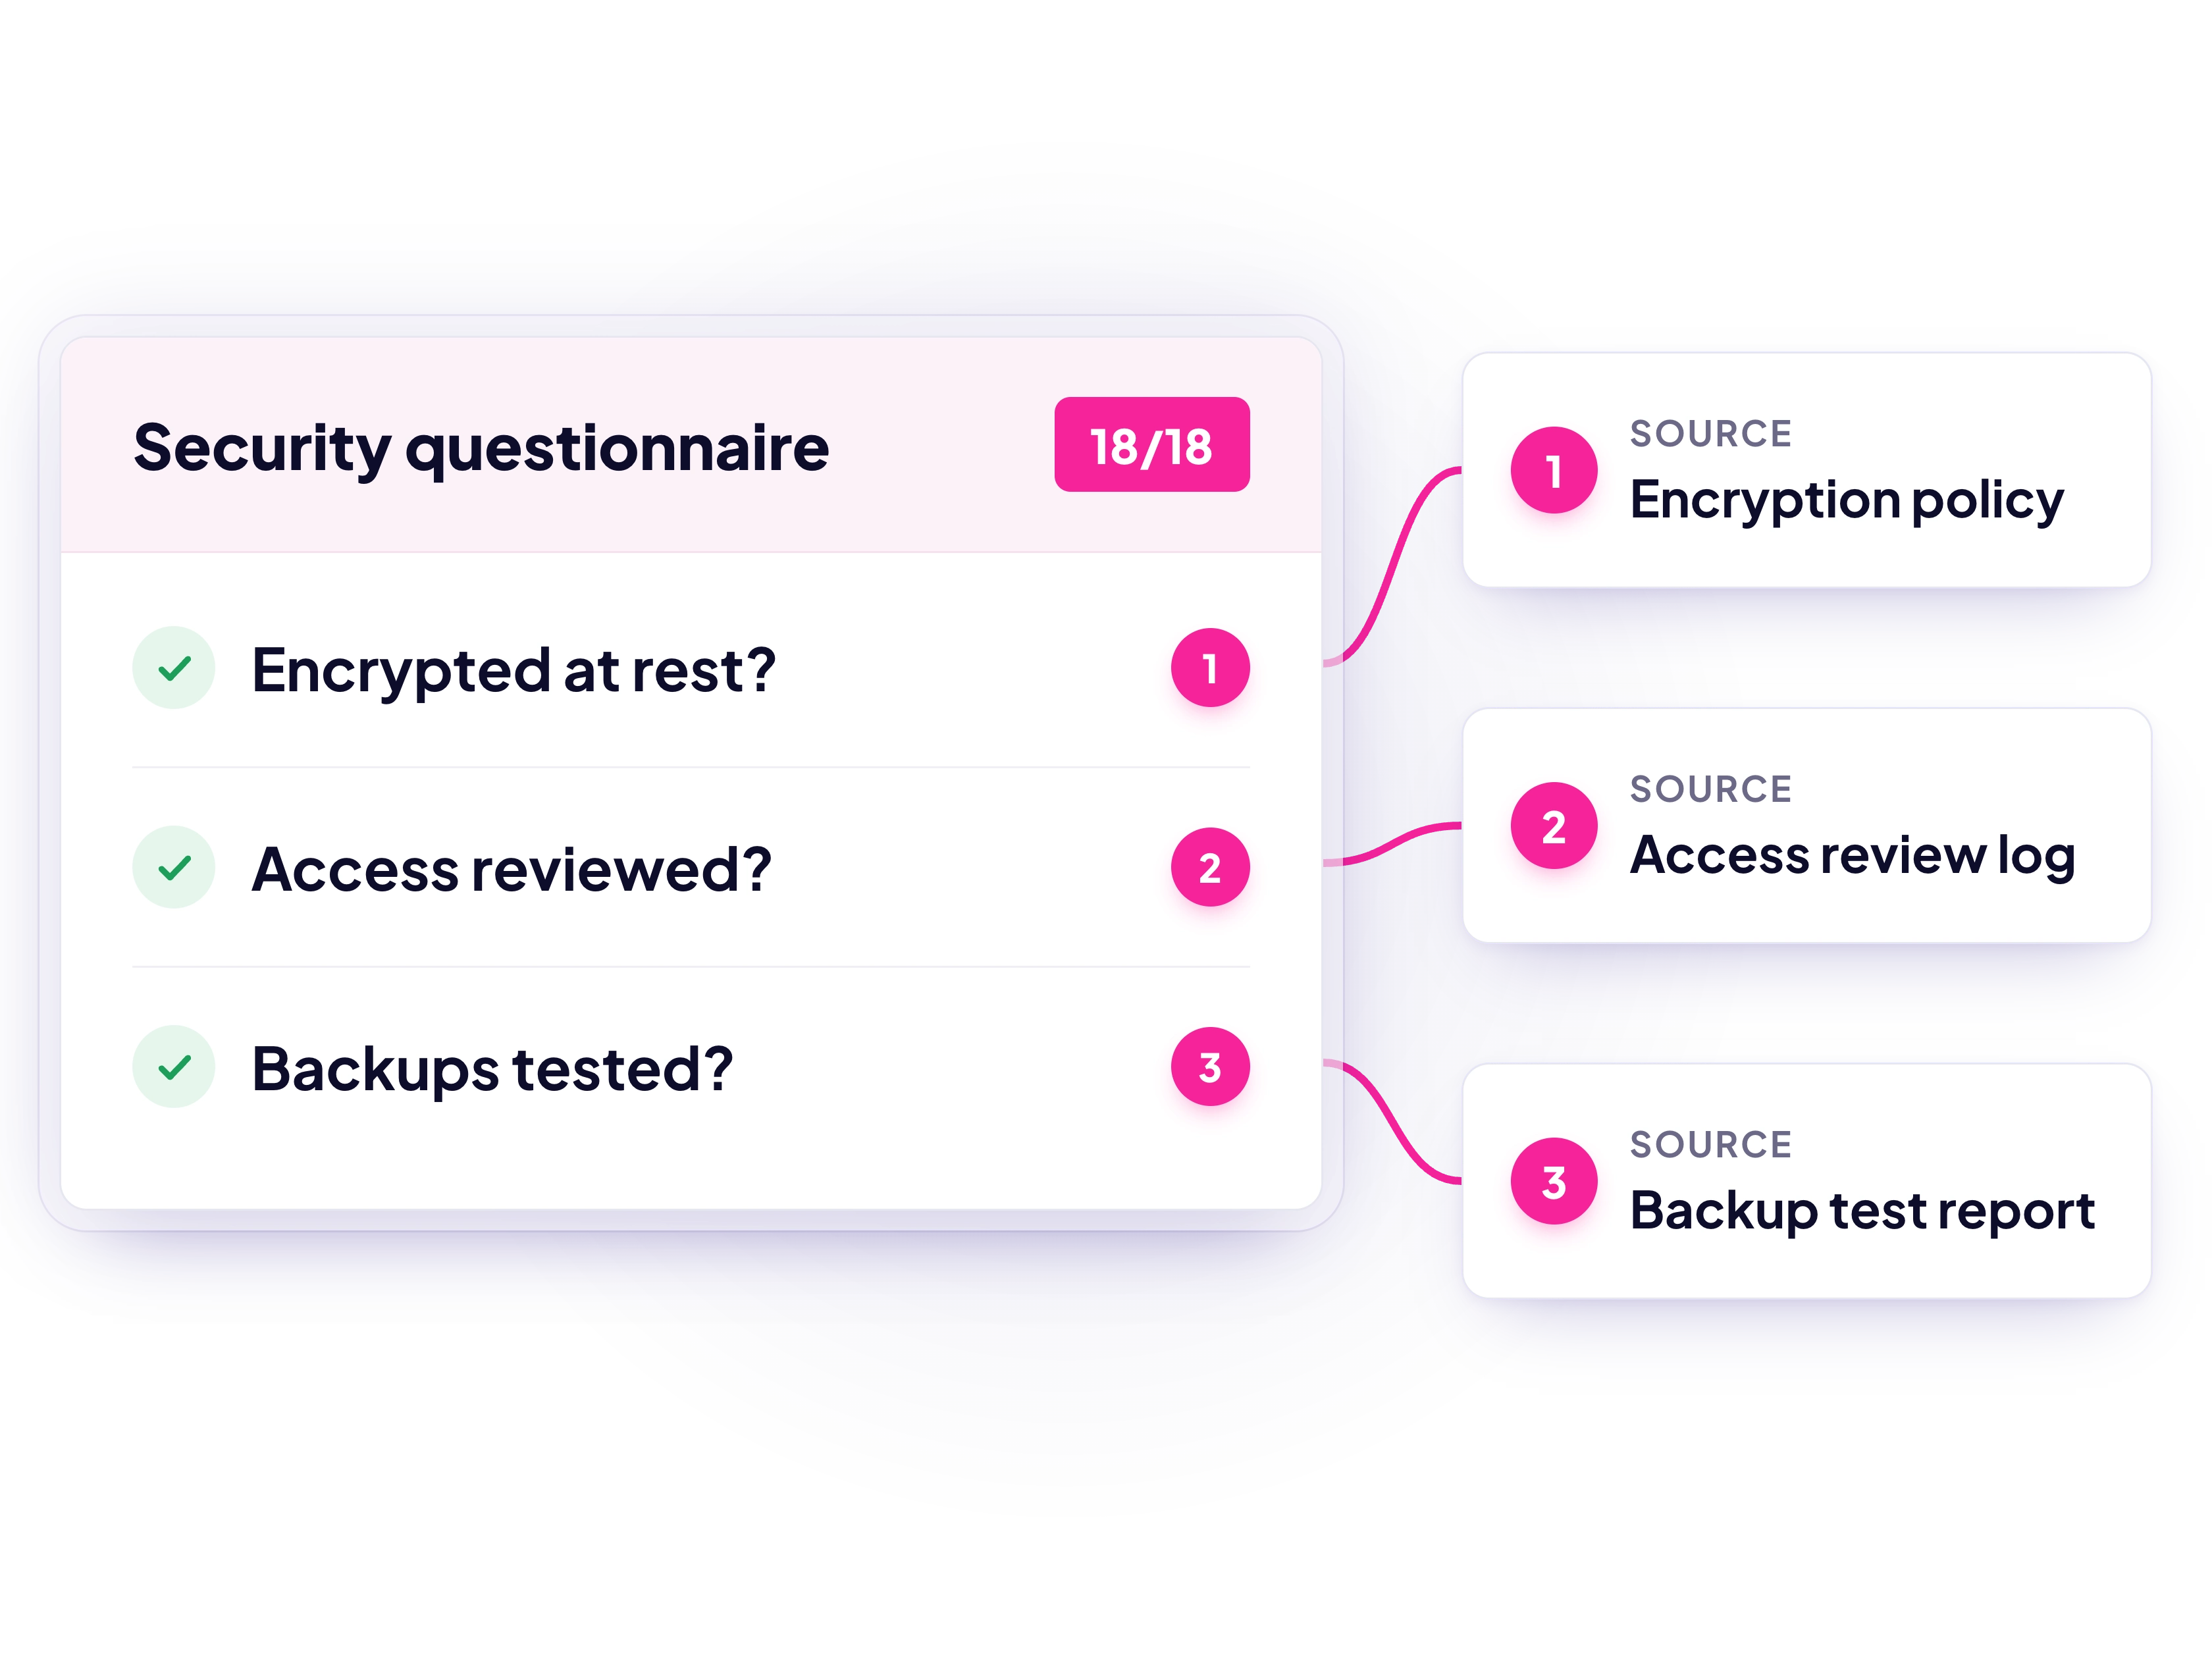
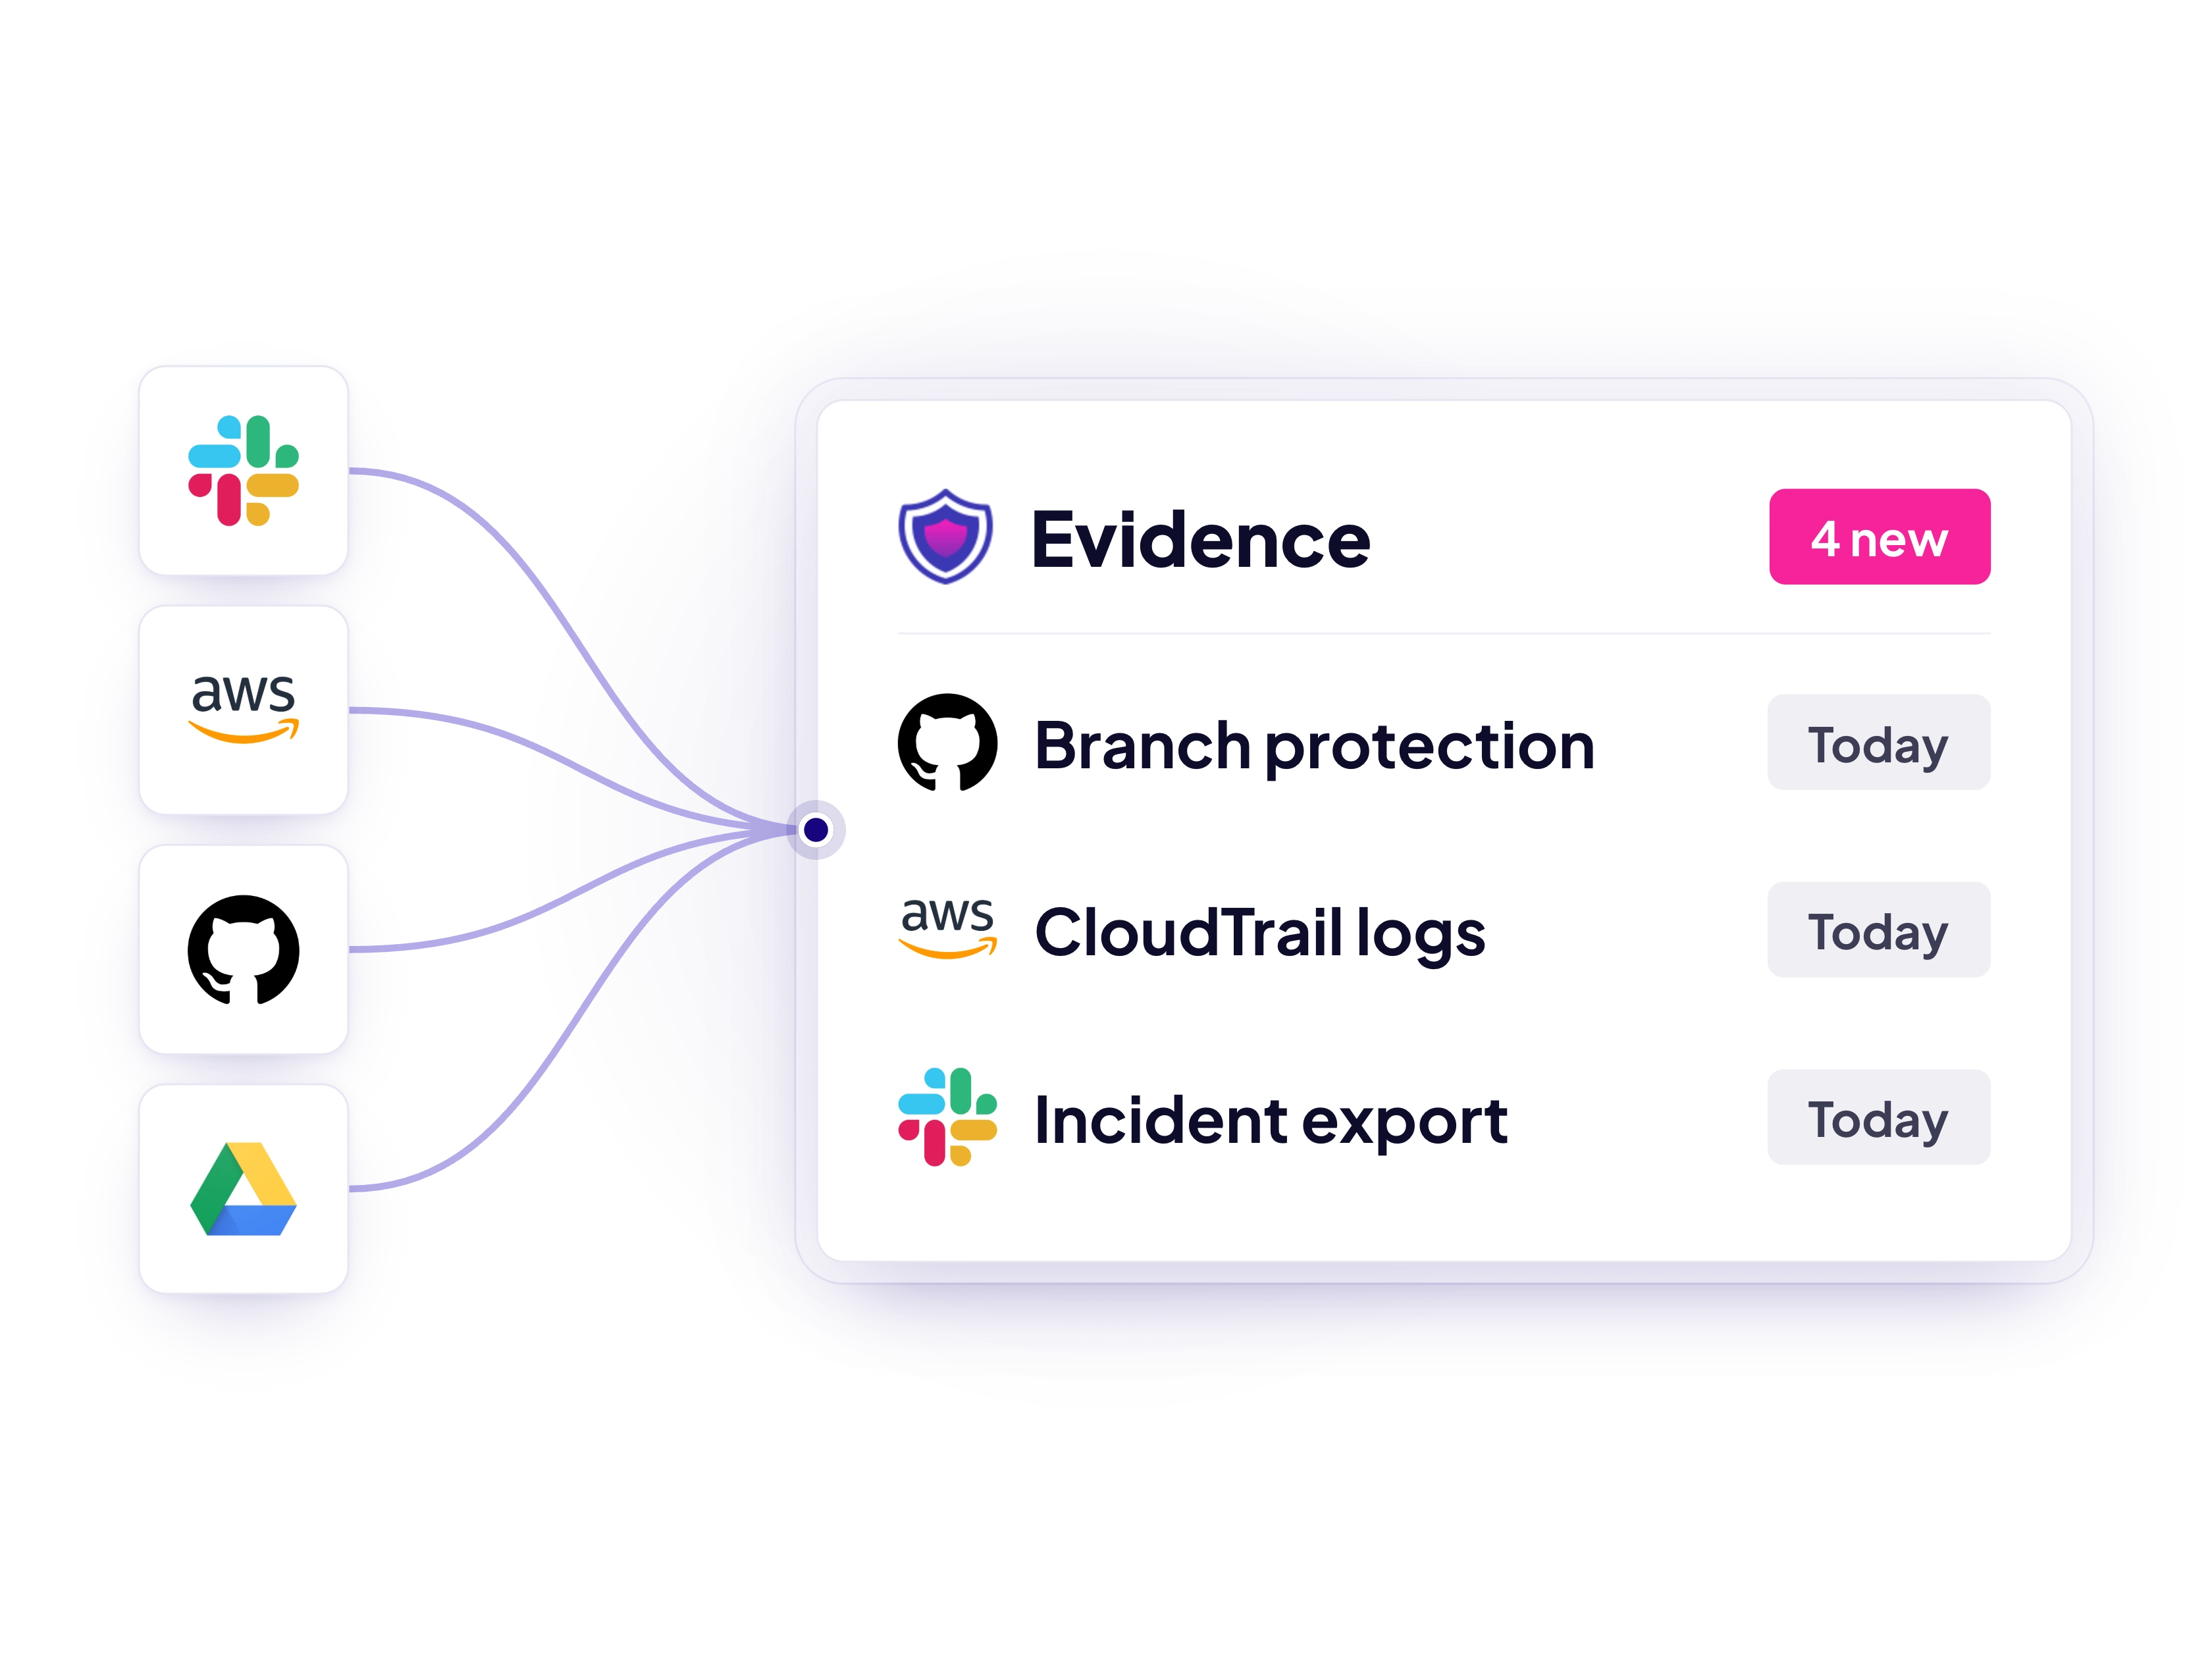
Trust security and IG questionnaires are drafted from your approved documents with every answer cited, and AI keeps your evidence up to date, so your team spends less time on paperwork.

V27 — Questionnaire with citations

Meet every requirement NHS frameworks ask for

Beyond DTAC, DSPT, DCB0129, Cyber Essentials and DPIAs, NHS procurement frameworks and tenders sometimes ask for ISO 9001 or ISO 14001. Add them alongside the evidence you already hold, so you can bid for more opportunities.

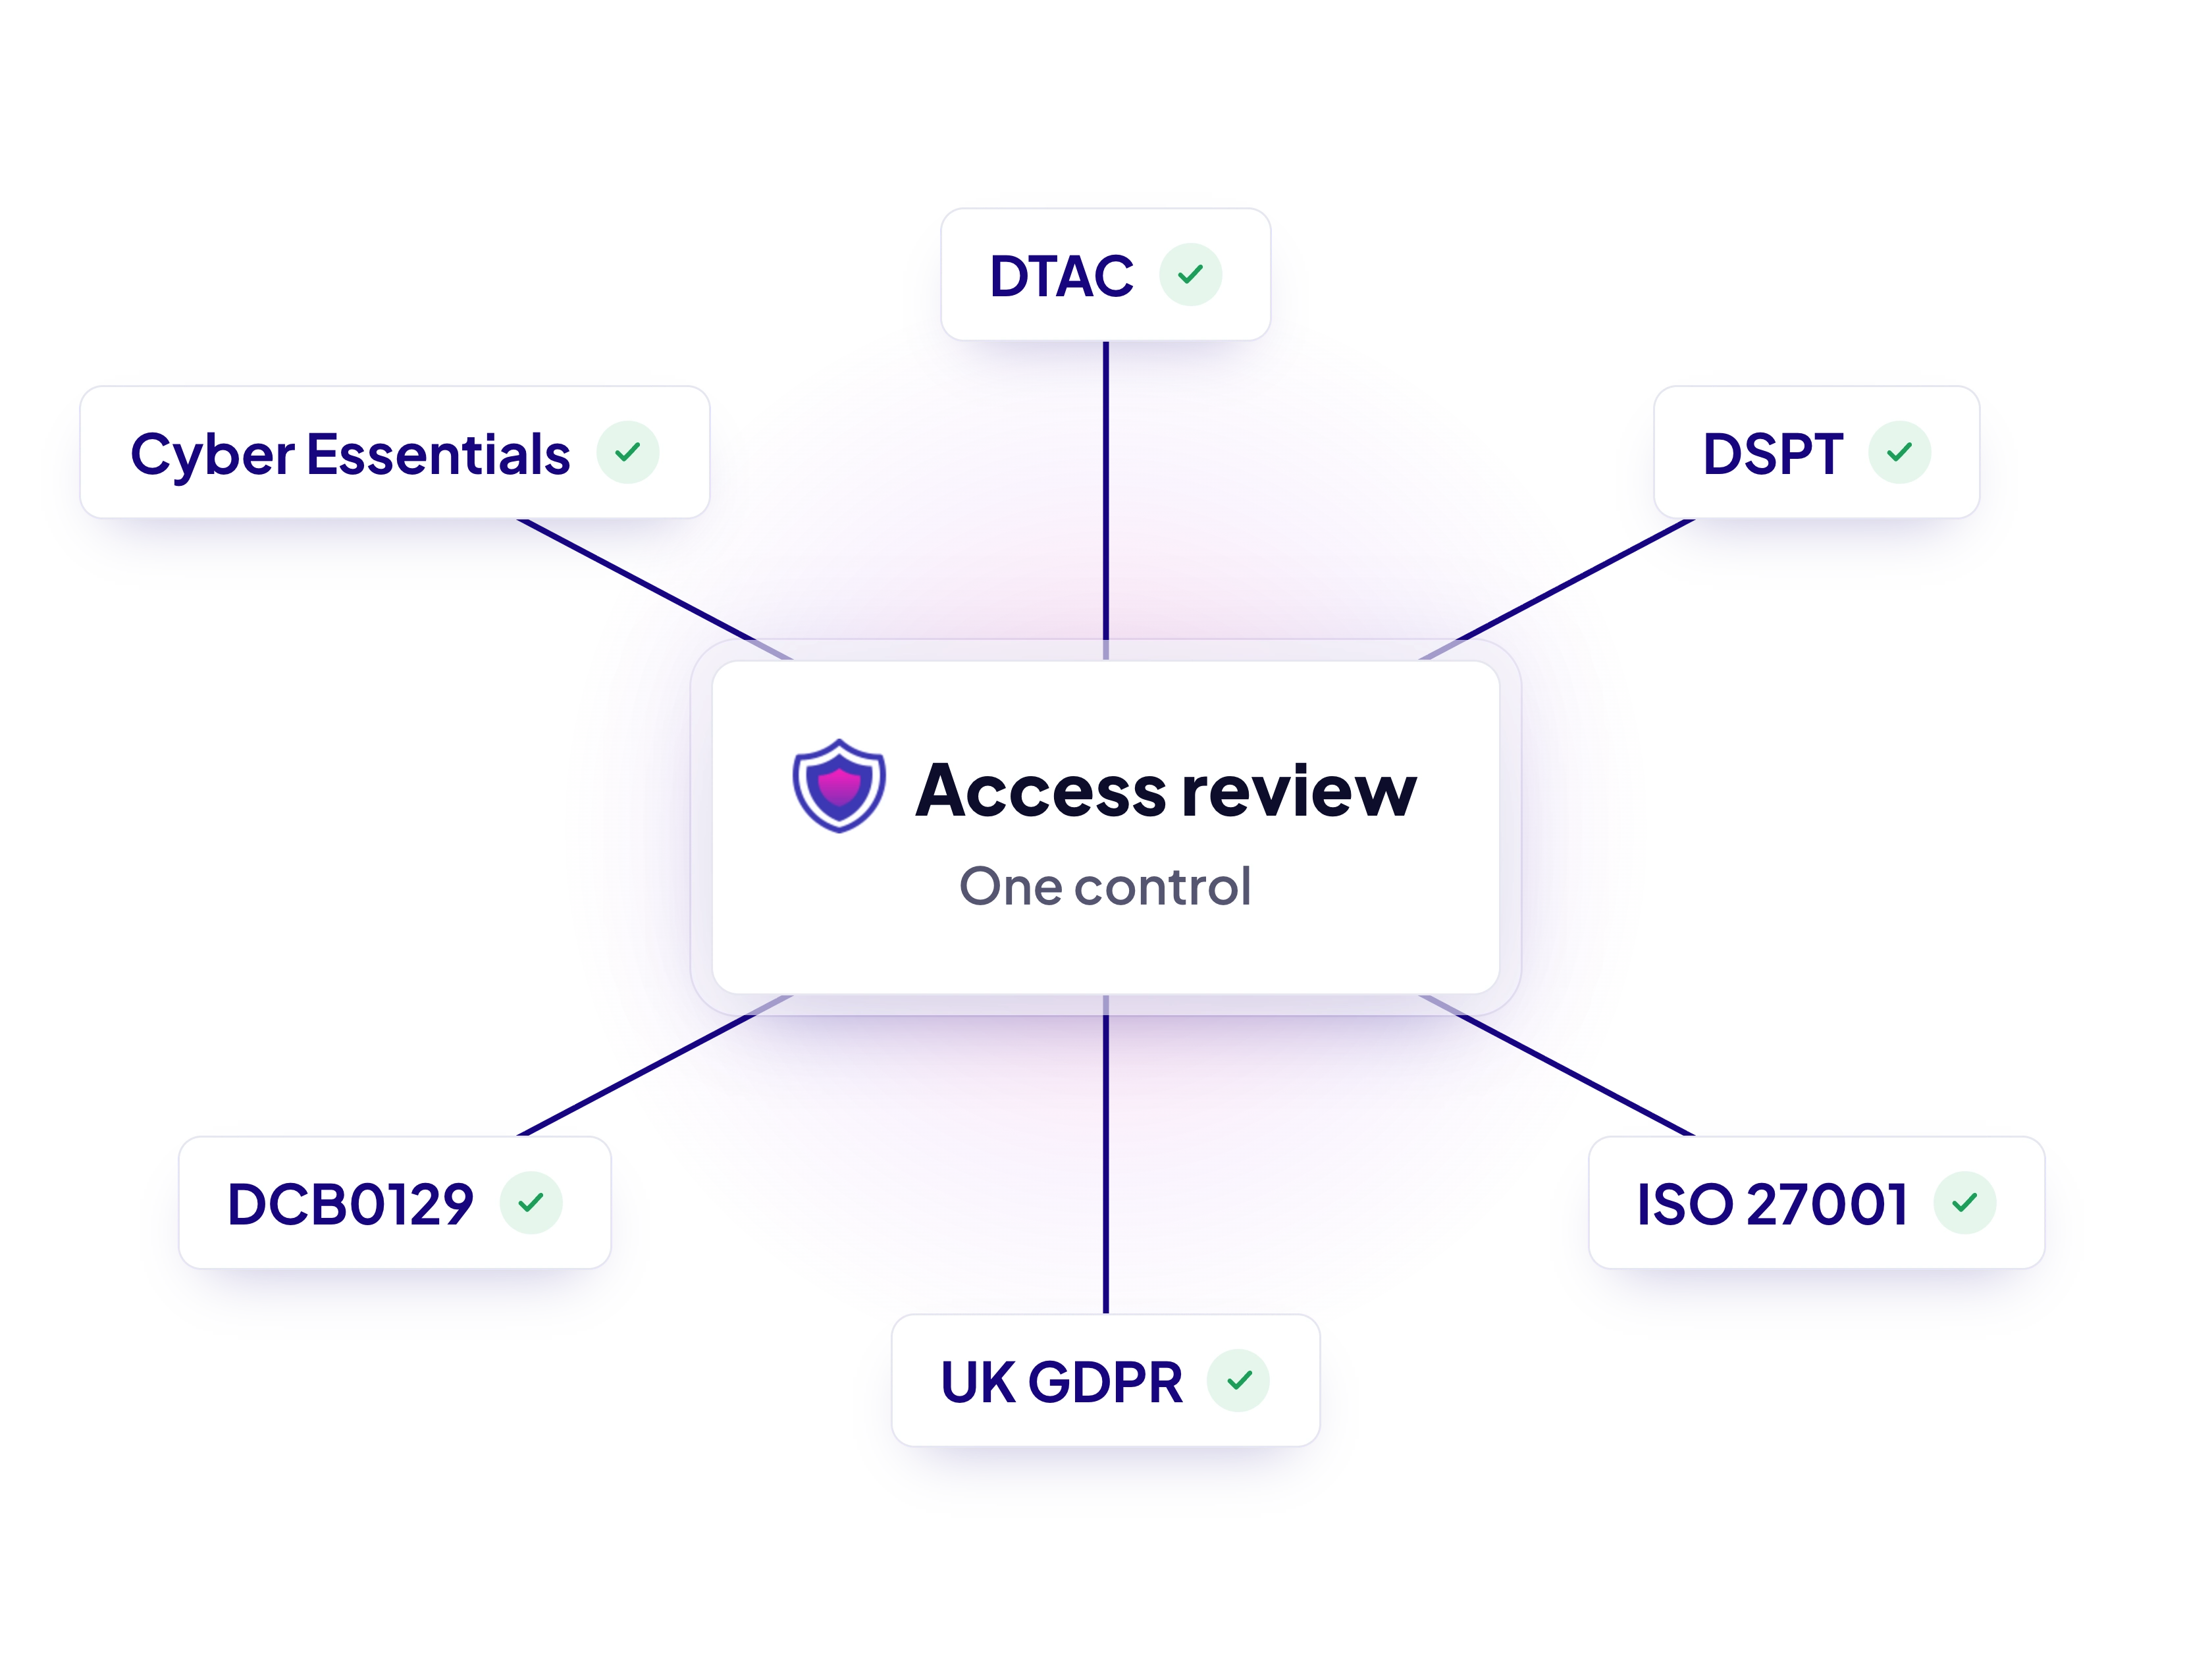
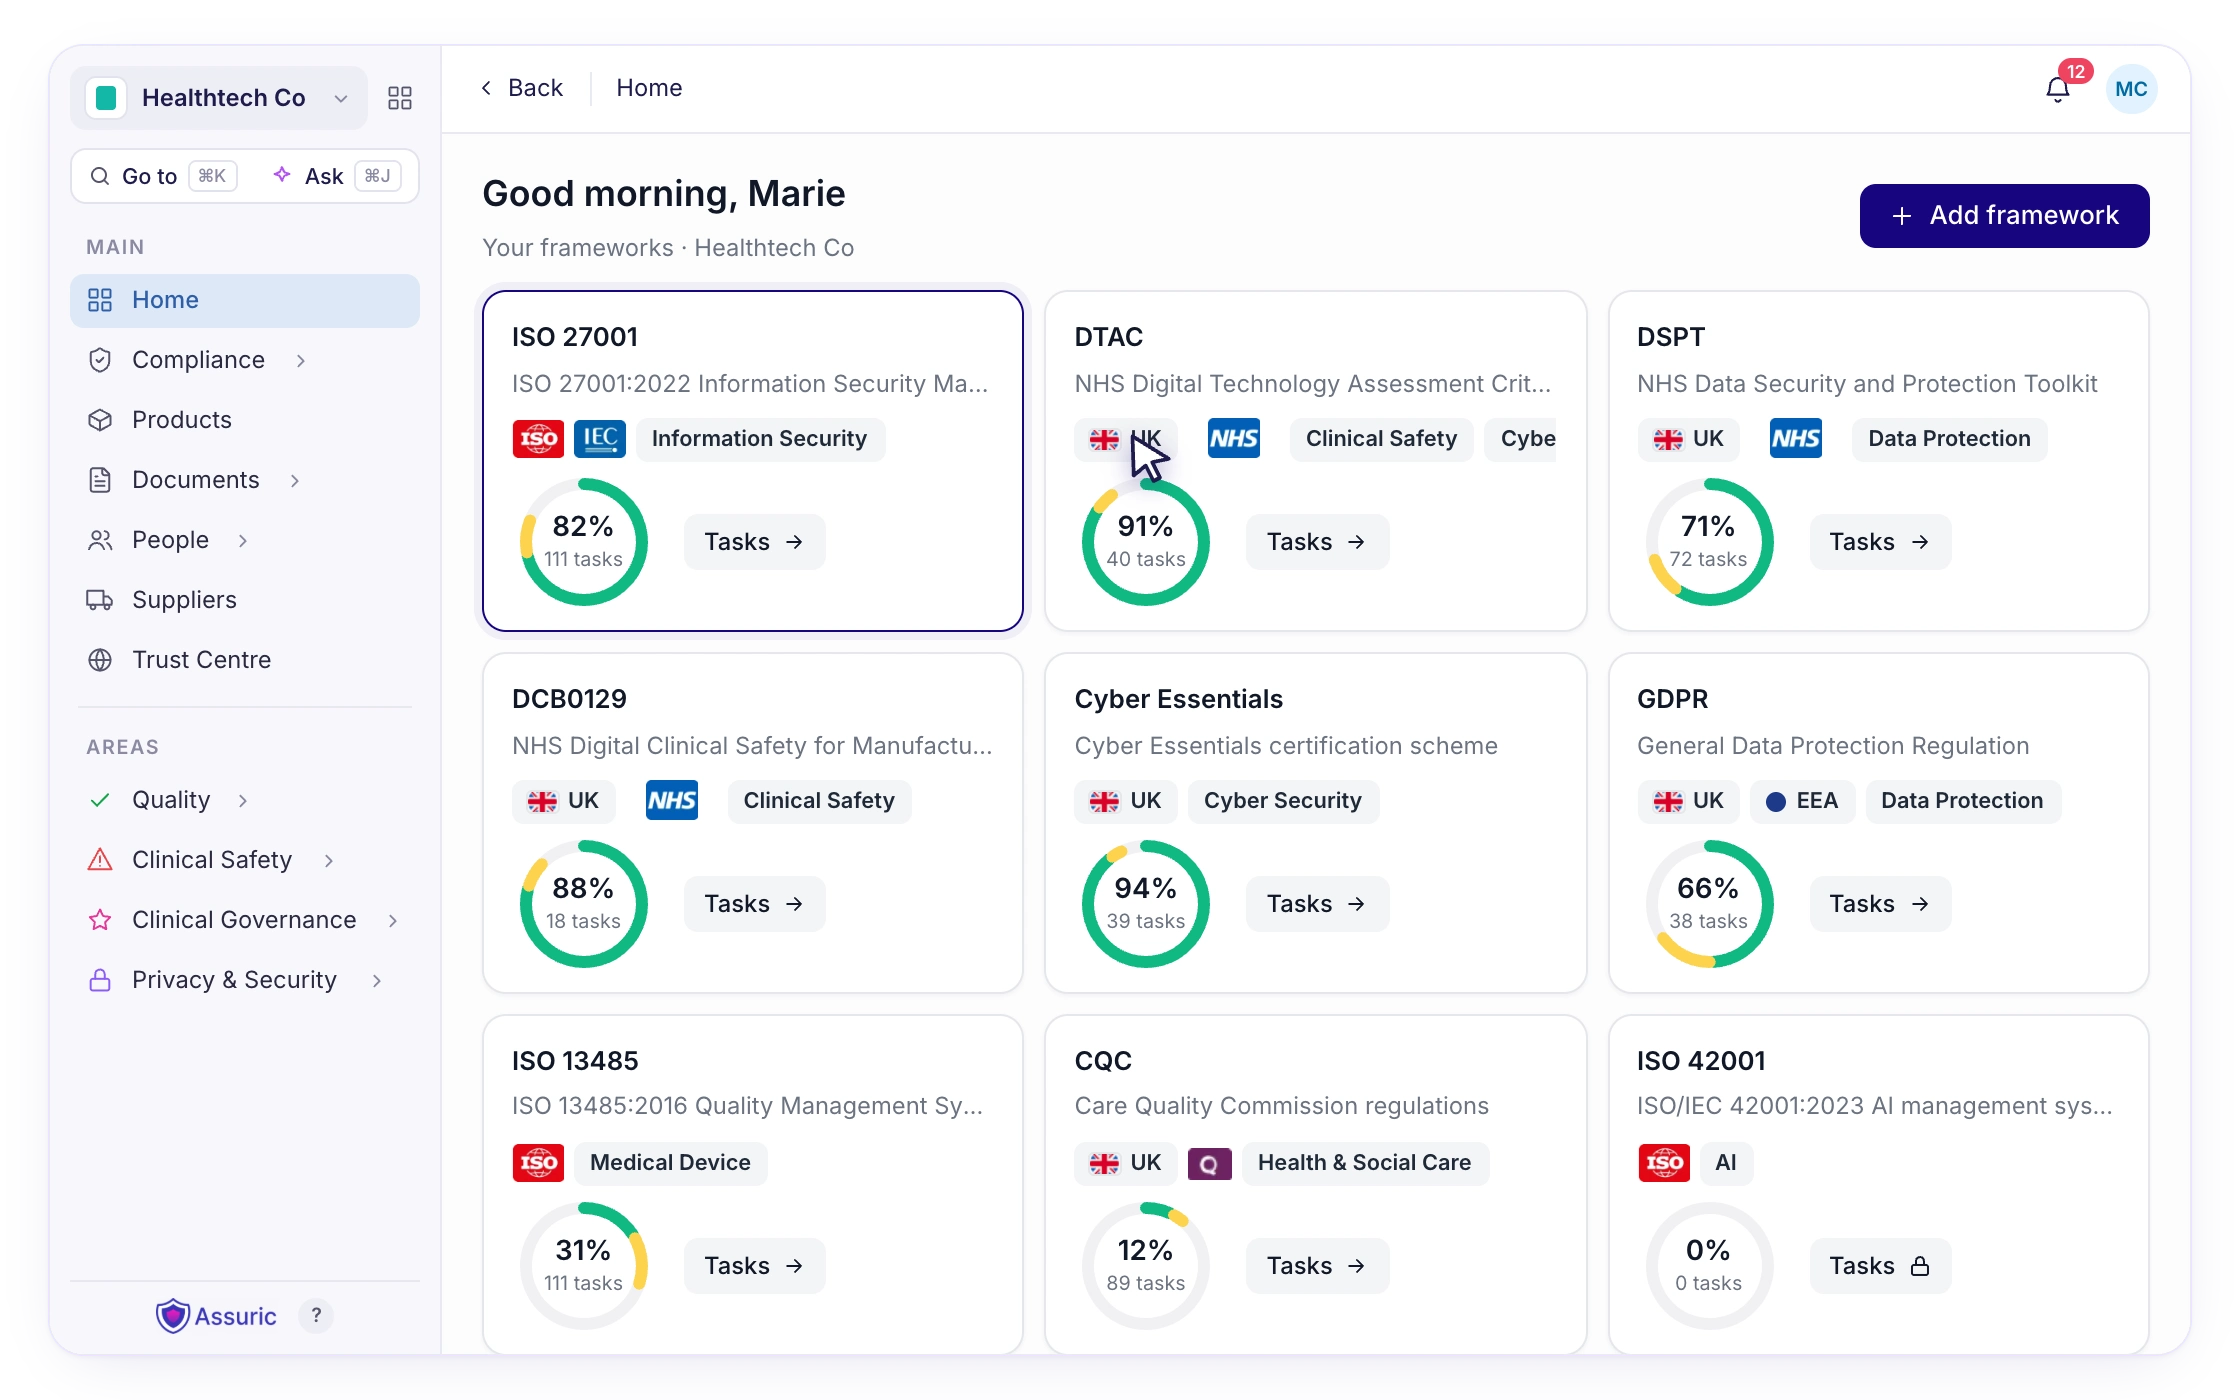
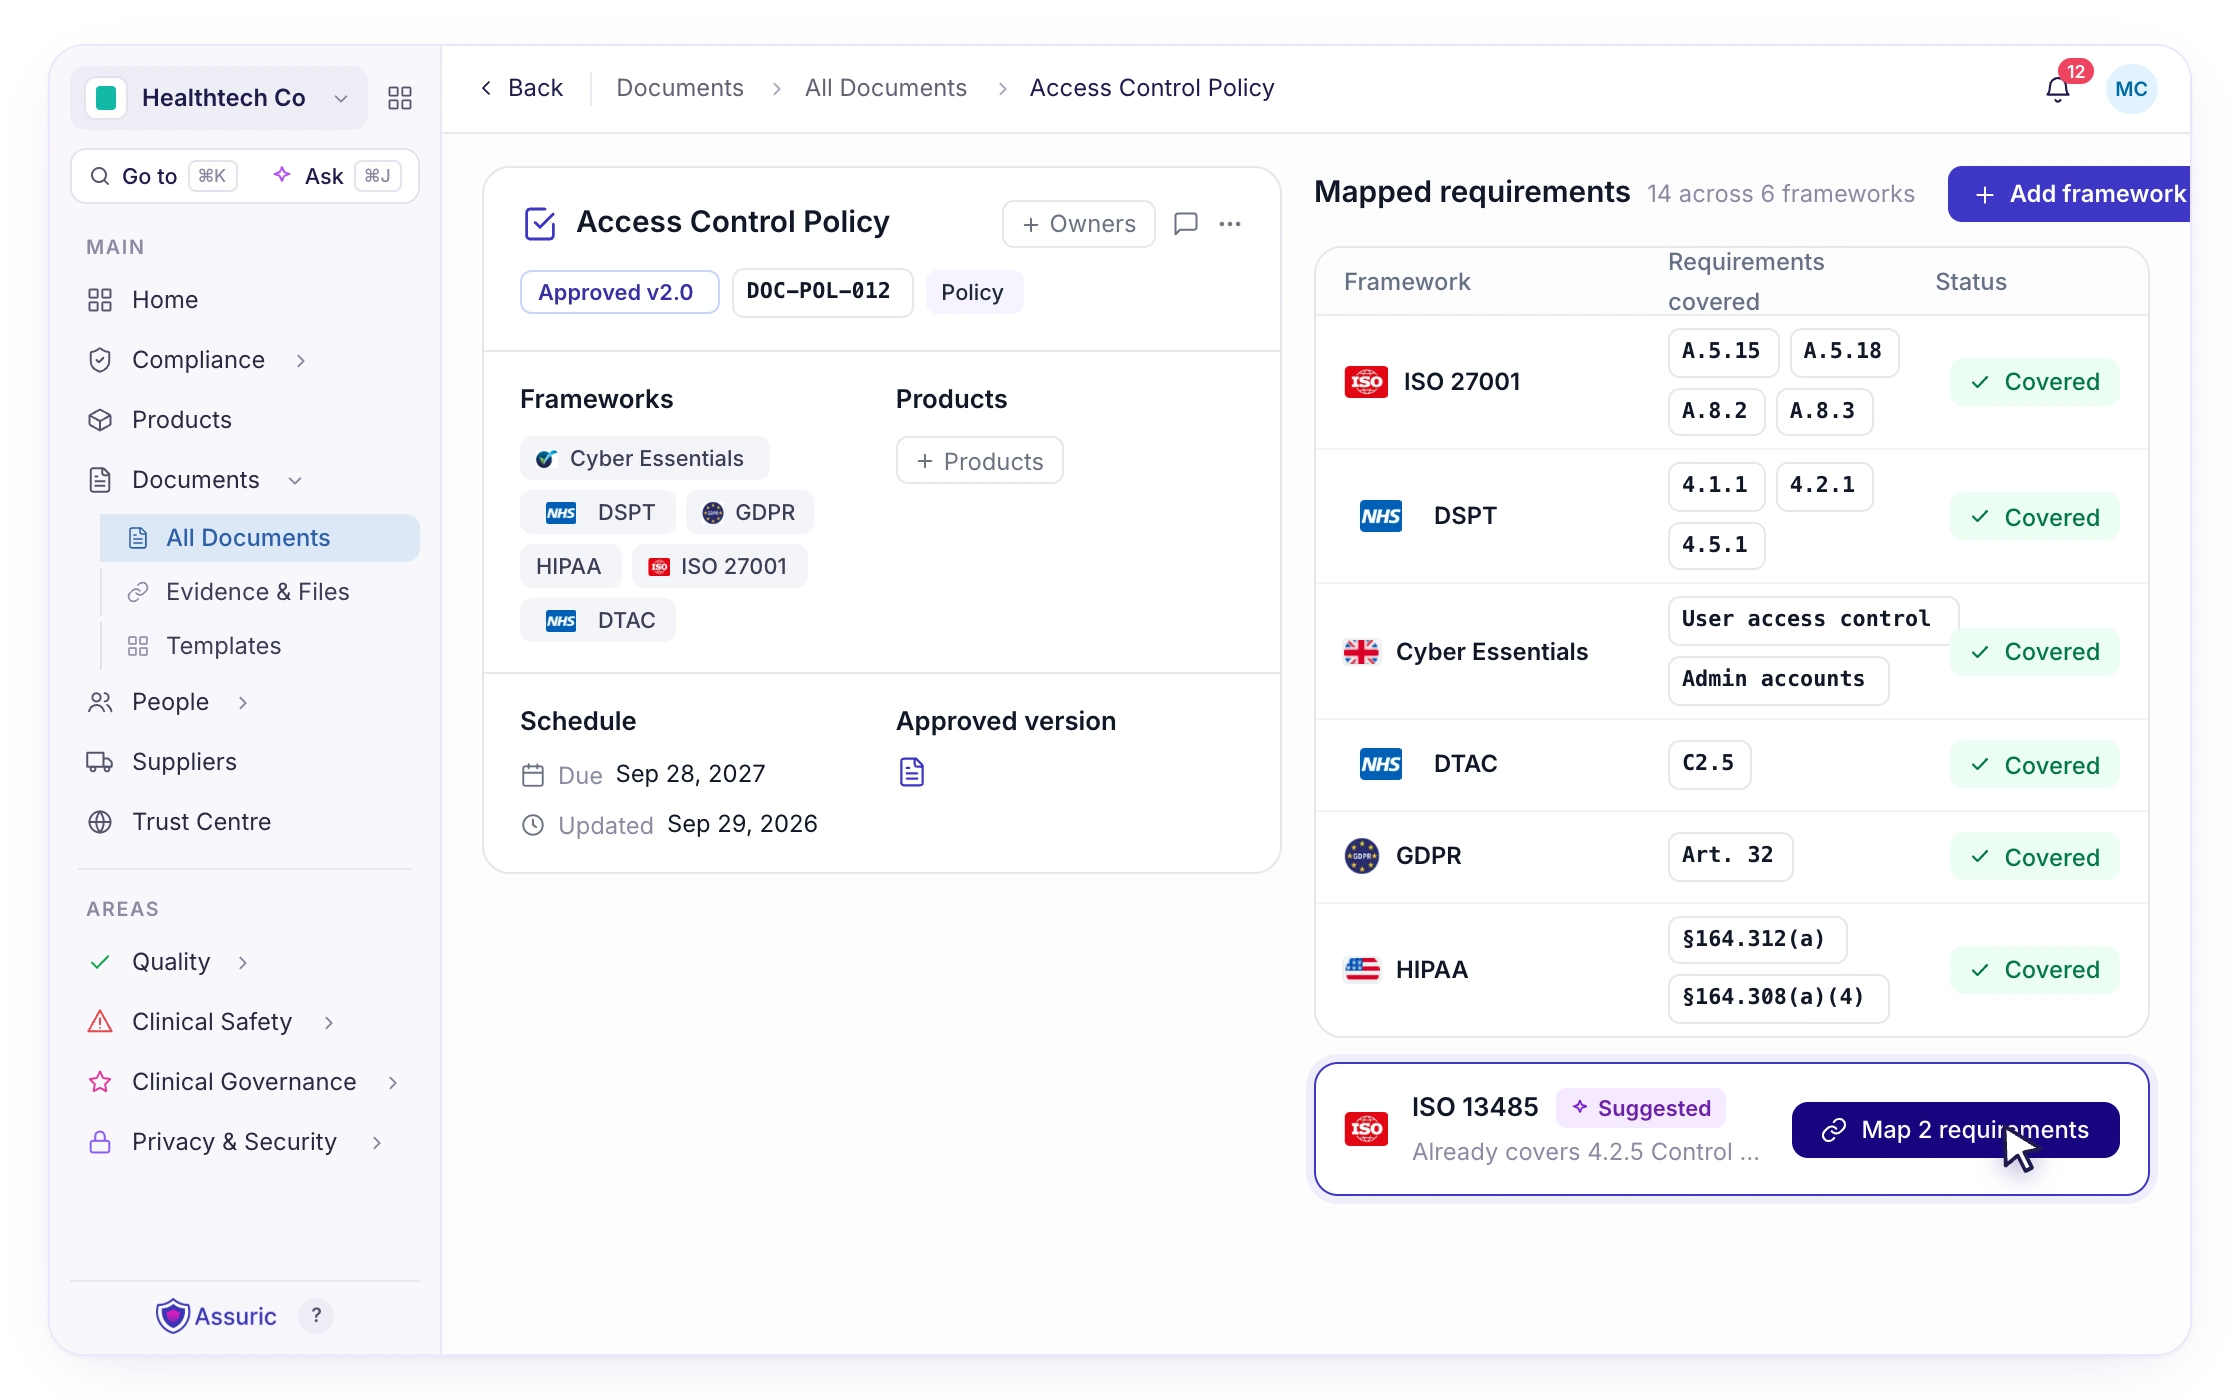
F006 — Evidence mapped across every framework

Features

One platform for all NHS requirements

Everything a trust asks a supplier for, evidenced in one place.

All-in-one compliance

One system for all your frameworks

One platform that covers all your digital health compliance as you grow, including NHS compliance, UK and EU MDR, CQC, information security and more.

Explore

Safety case reports

DCB0129 safety cases built from live records

Generate your clinical safety case report from your live hazard log, with reviews, approvals and version history built in, so every release has a current safety case.

Explore

Compliance tracking

One piece of evidence, every NHS standard

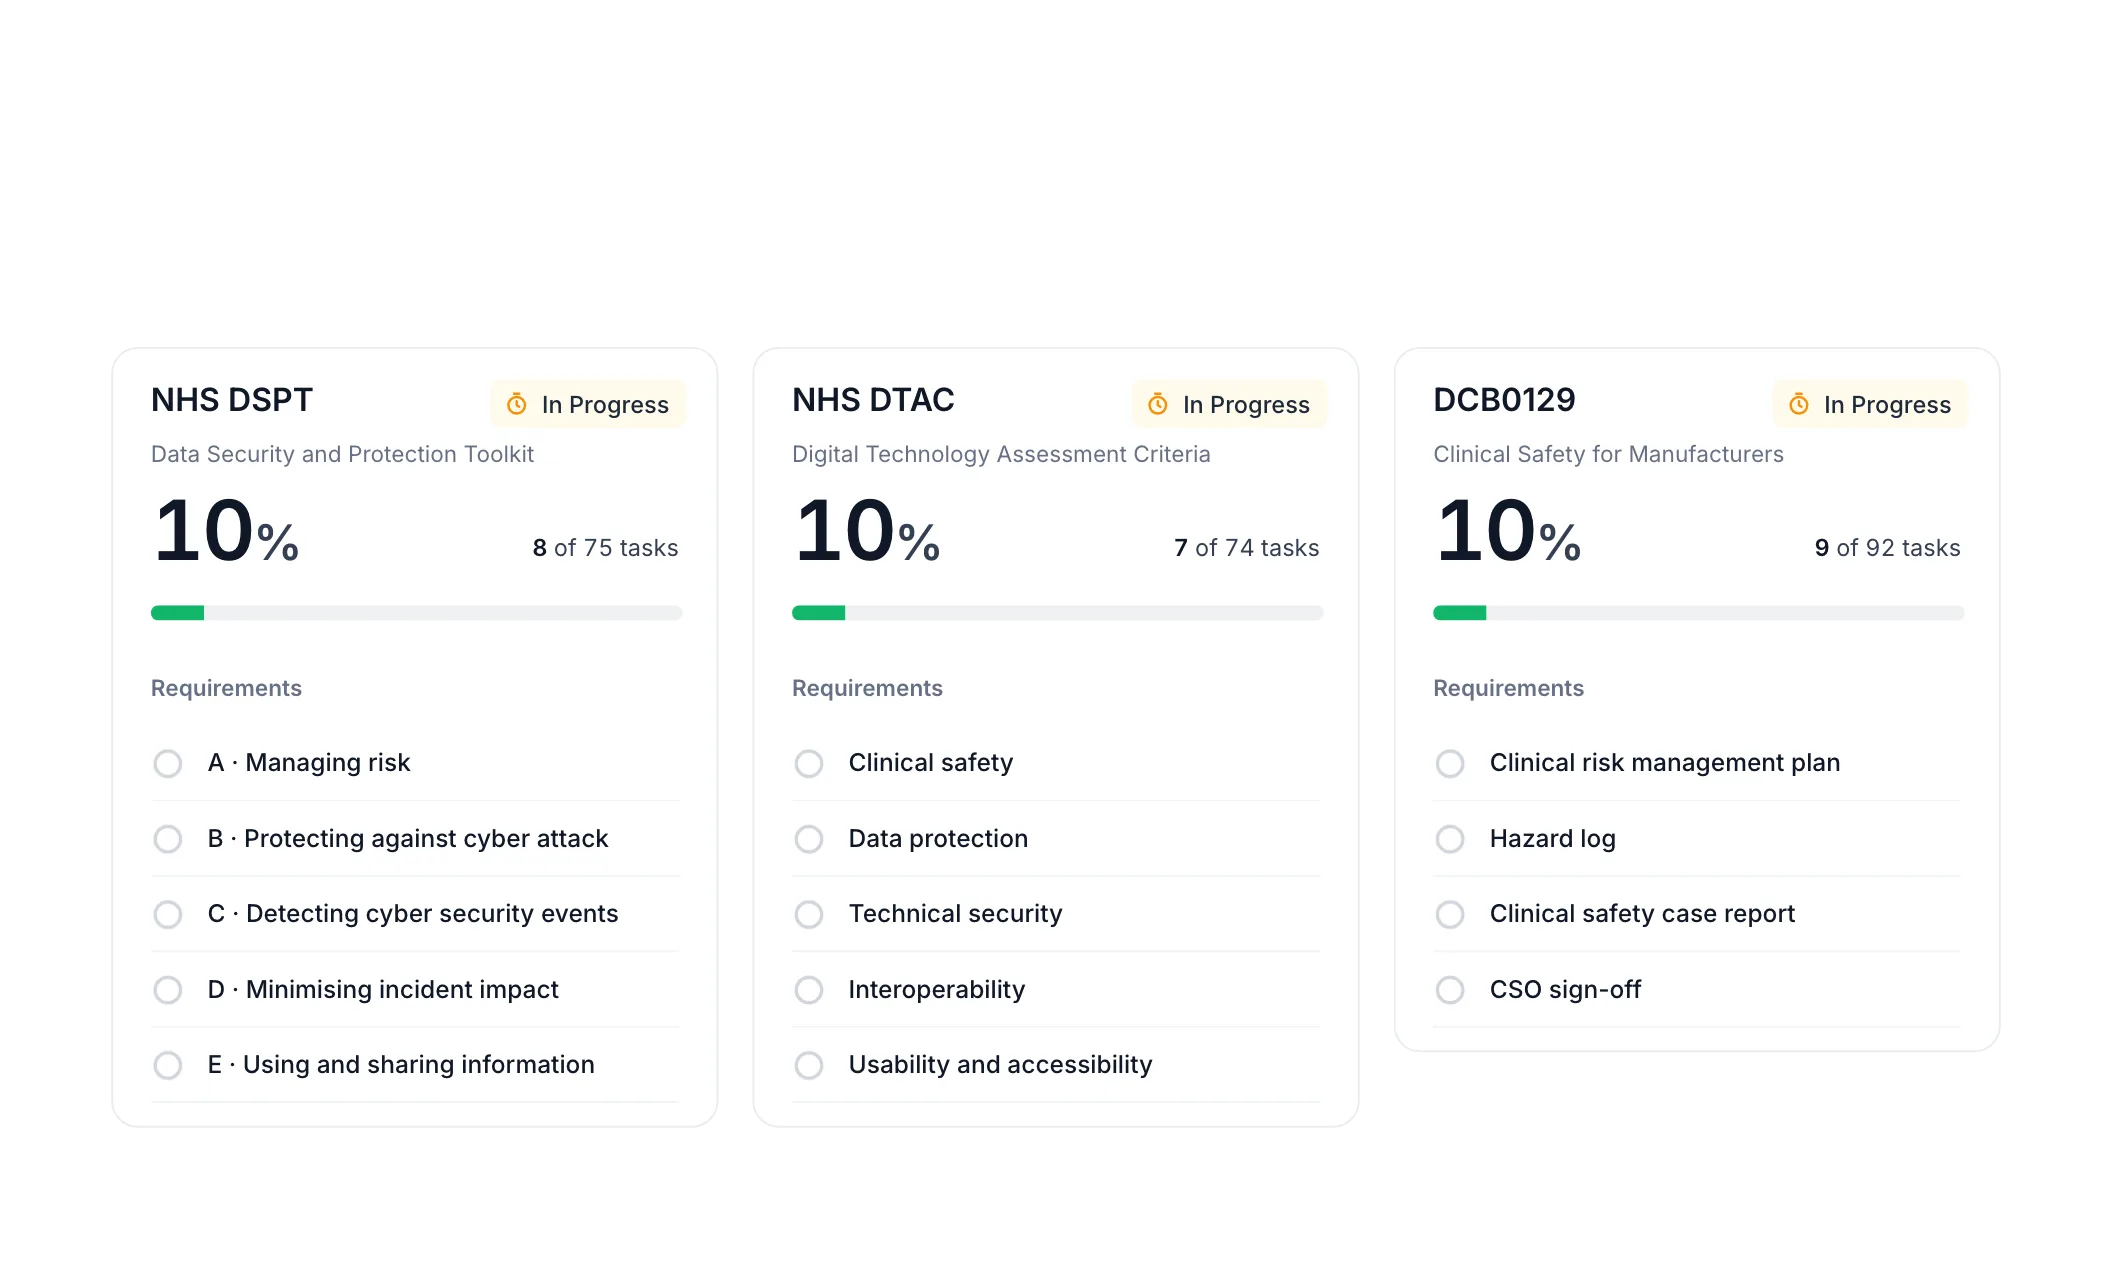
Each control is evidenced once and counts towards DTAC, DSPT, Cyber Essentials and ISO 27001 at the same time, so adding a new framework is a mapping exercise, not a rewrite.

Explore

Document & policy management

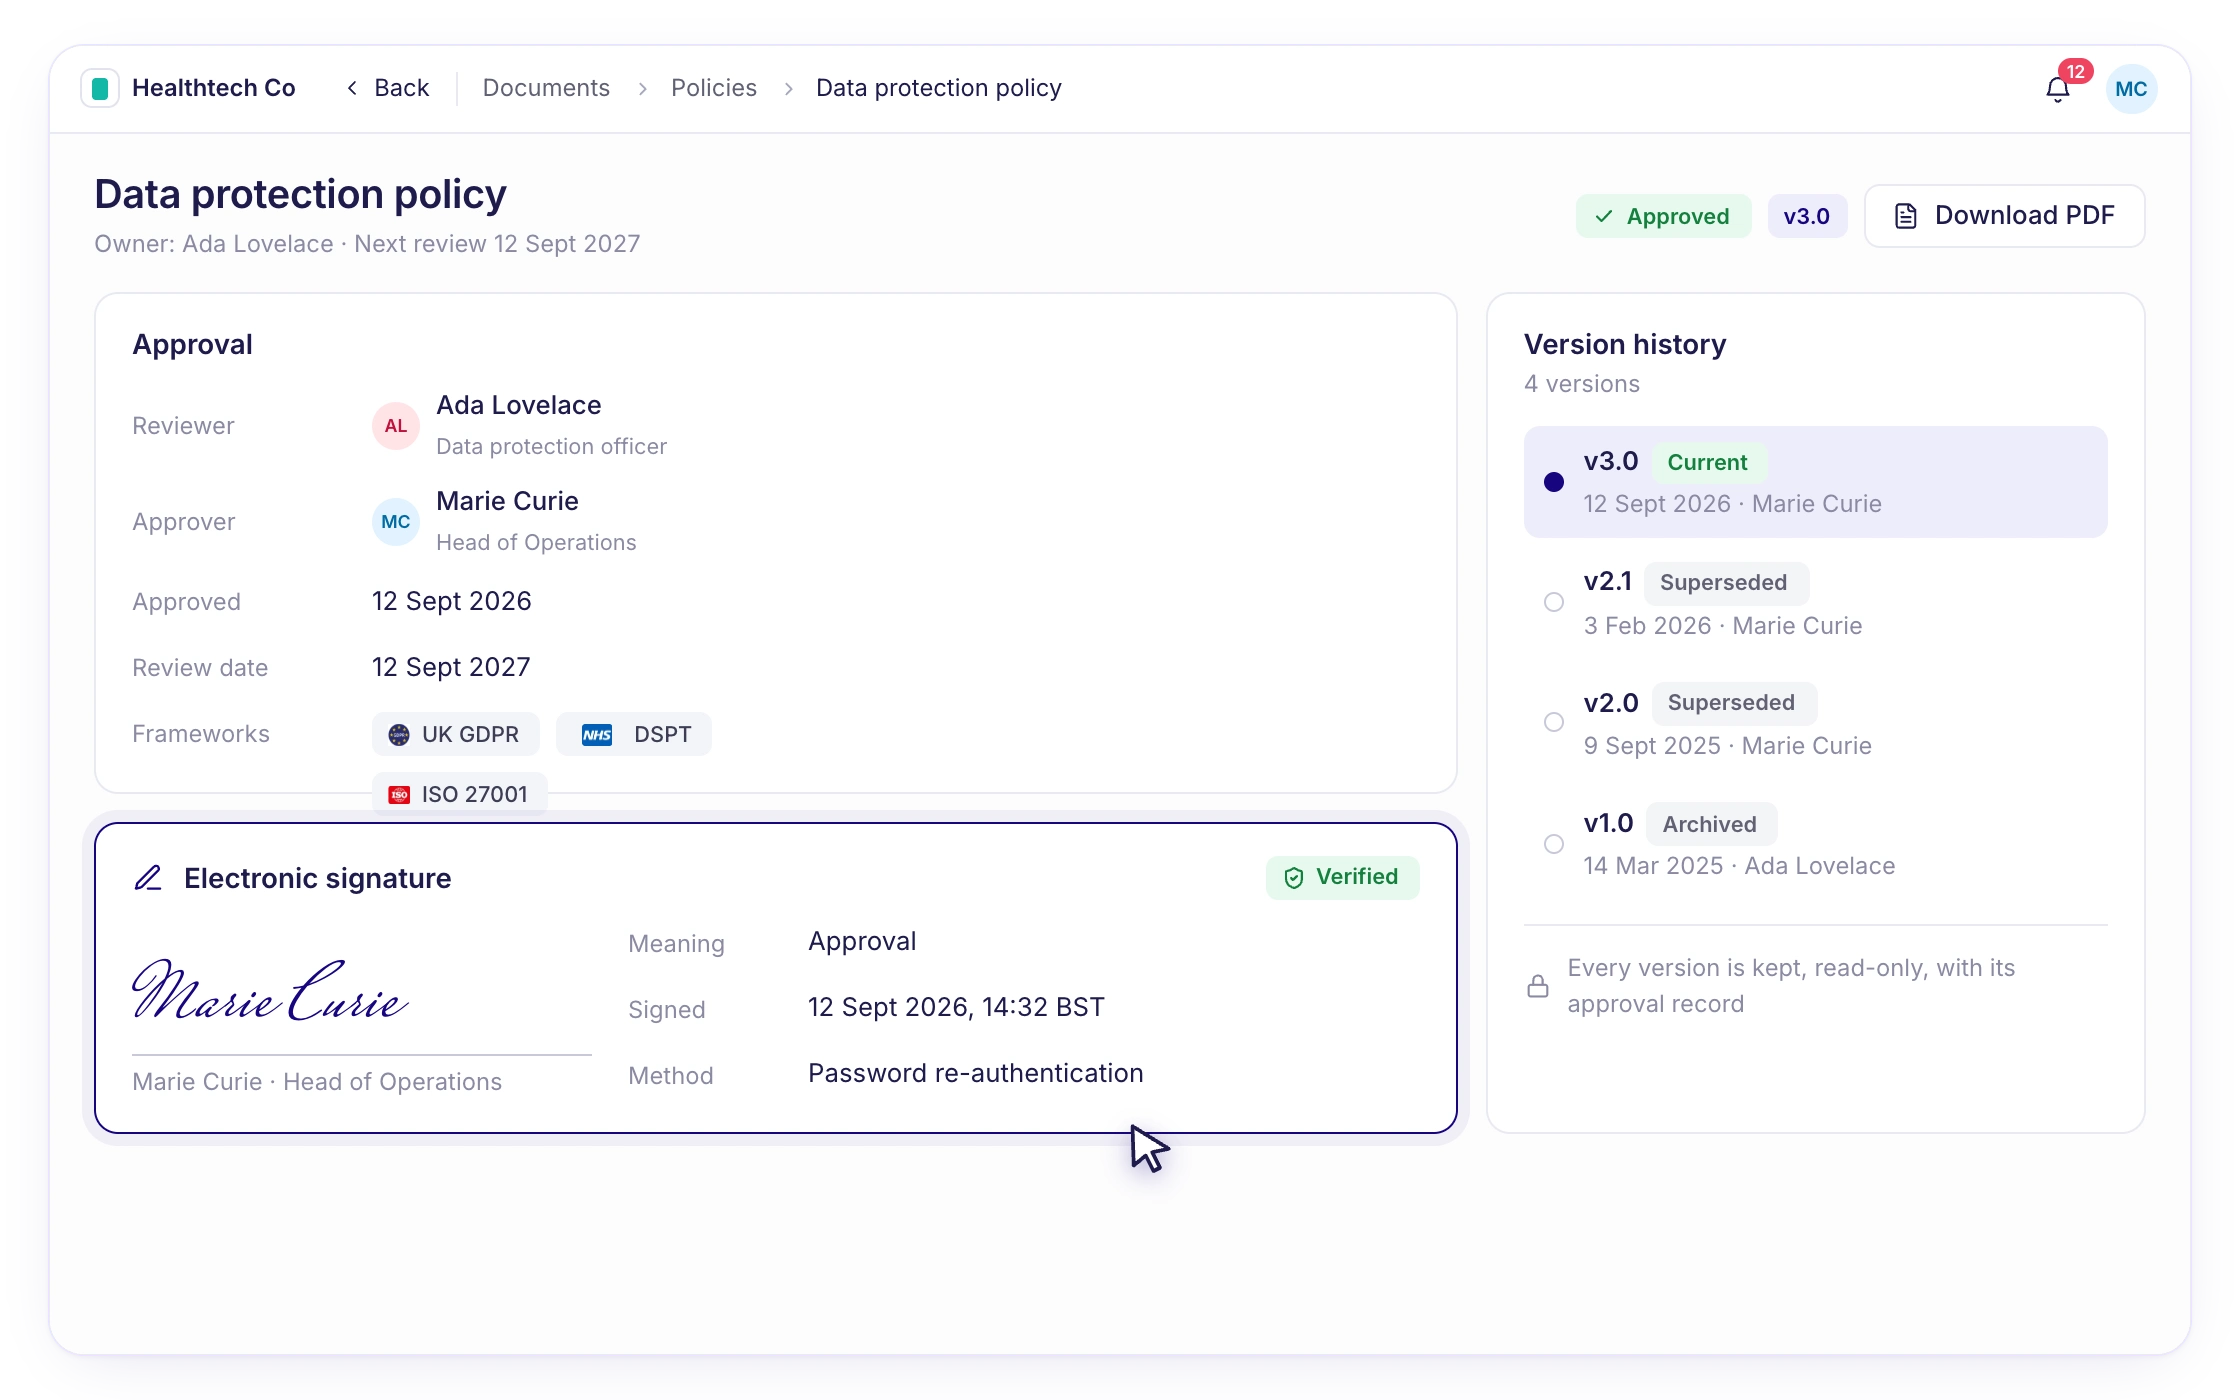
Policies trusts ask for, version-controlled

Every policy has its owner, approver, review date and version history, so you always send trusts the current version.

Explore

Audit and certification

Pass audits and certifications first time

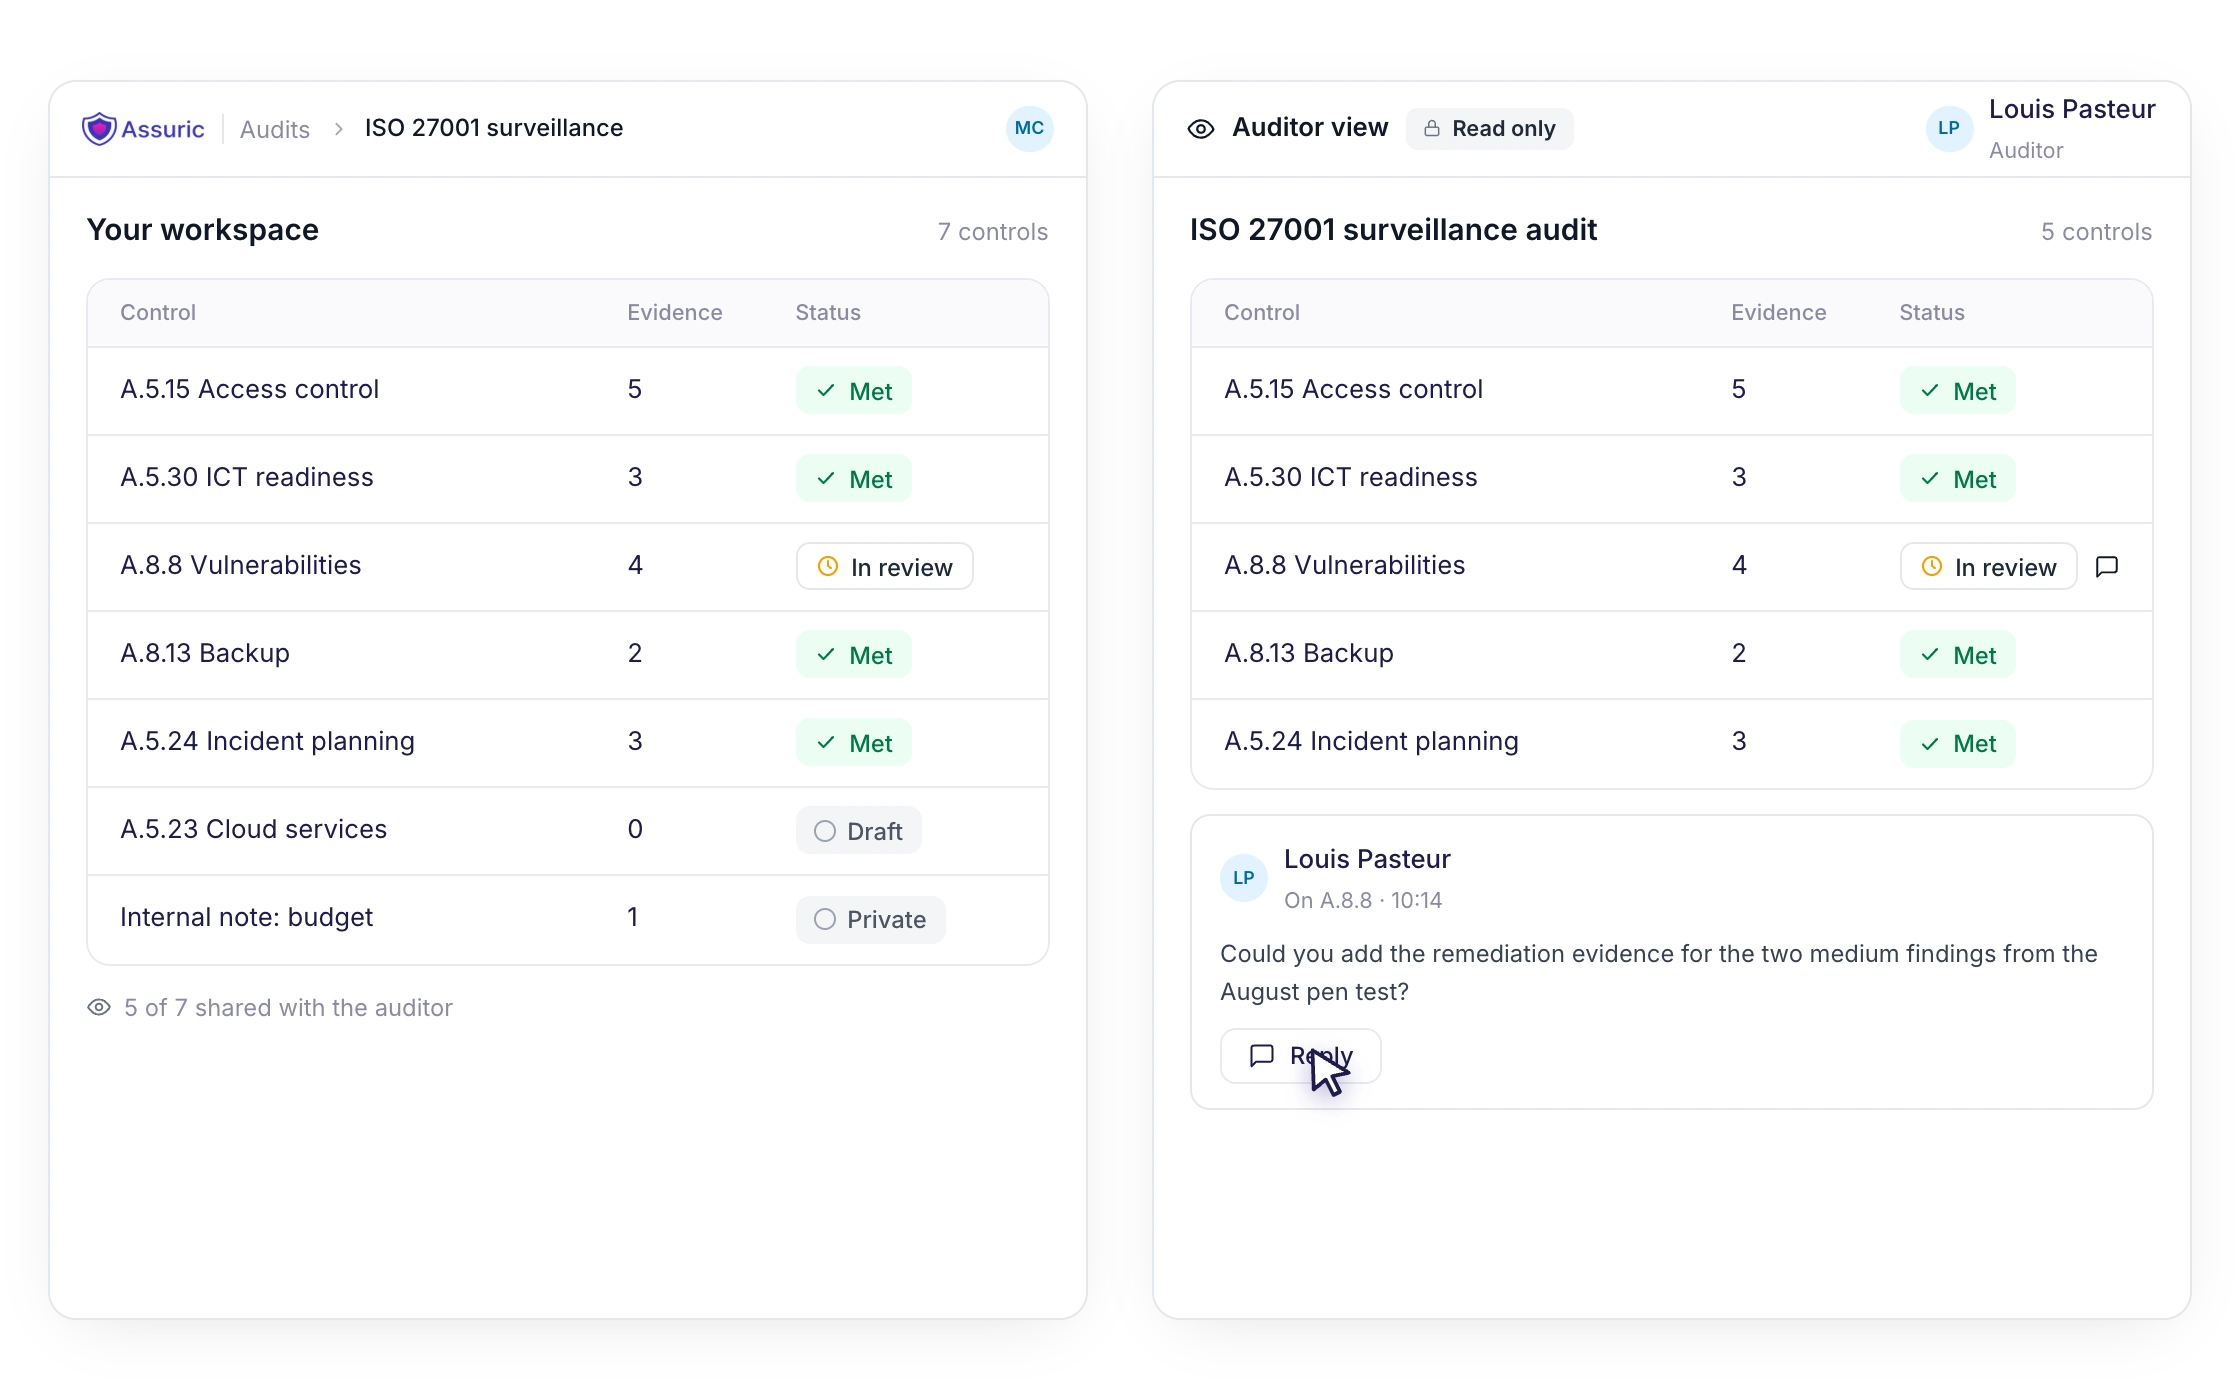
Plan internal audits, track findings to closure, and give assessors their own portal for Cyber Essentials and ISO 27001 assessments.

Explore

MCP

Use Assuric from your AI tools

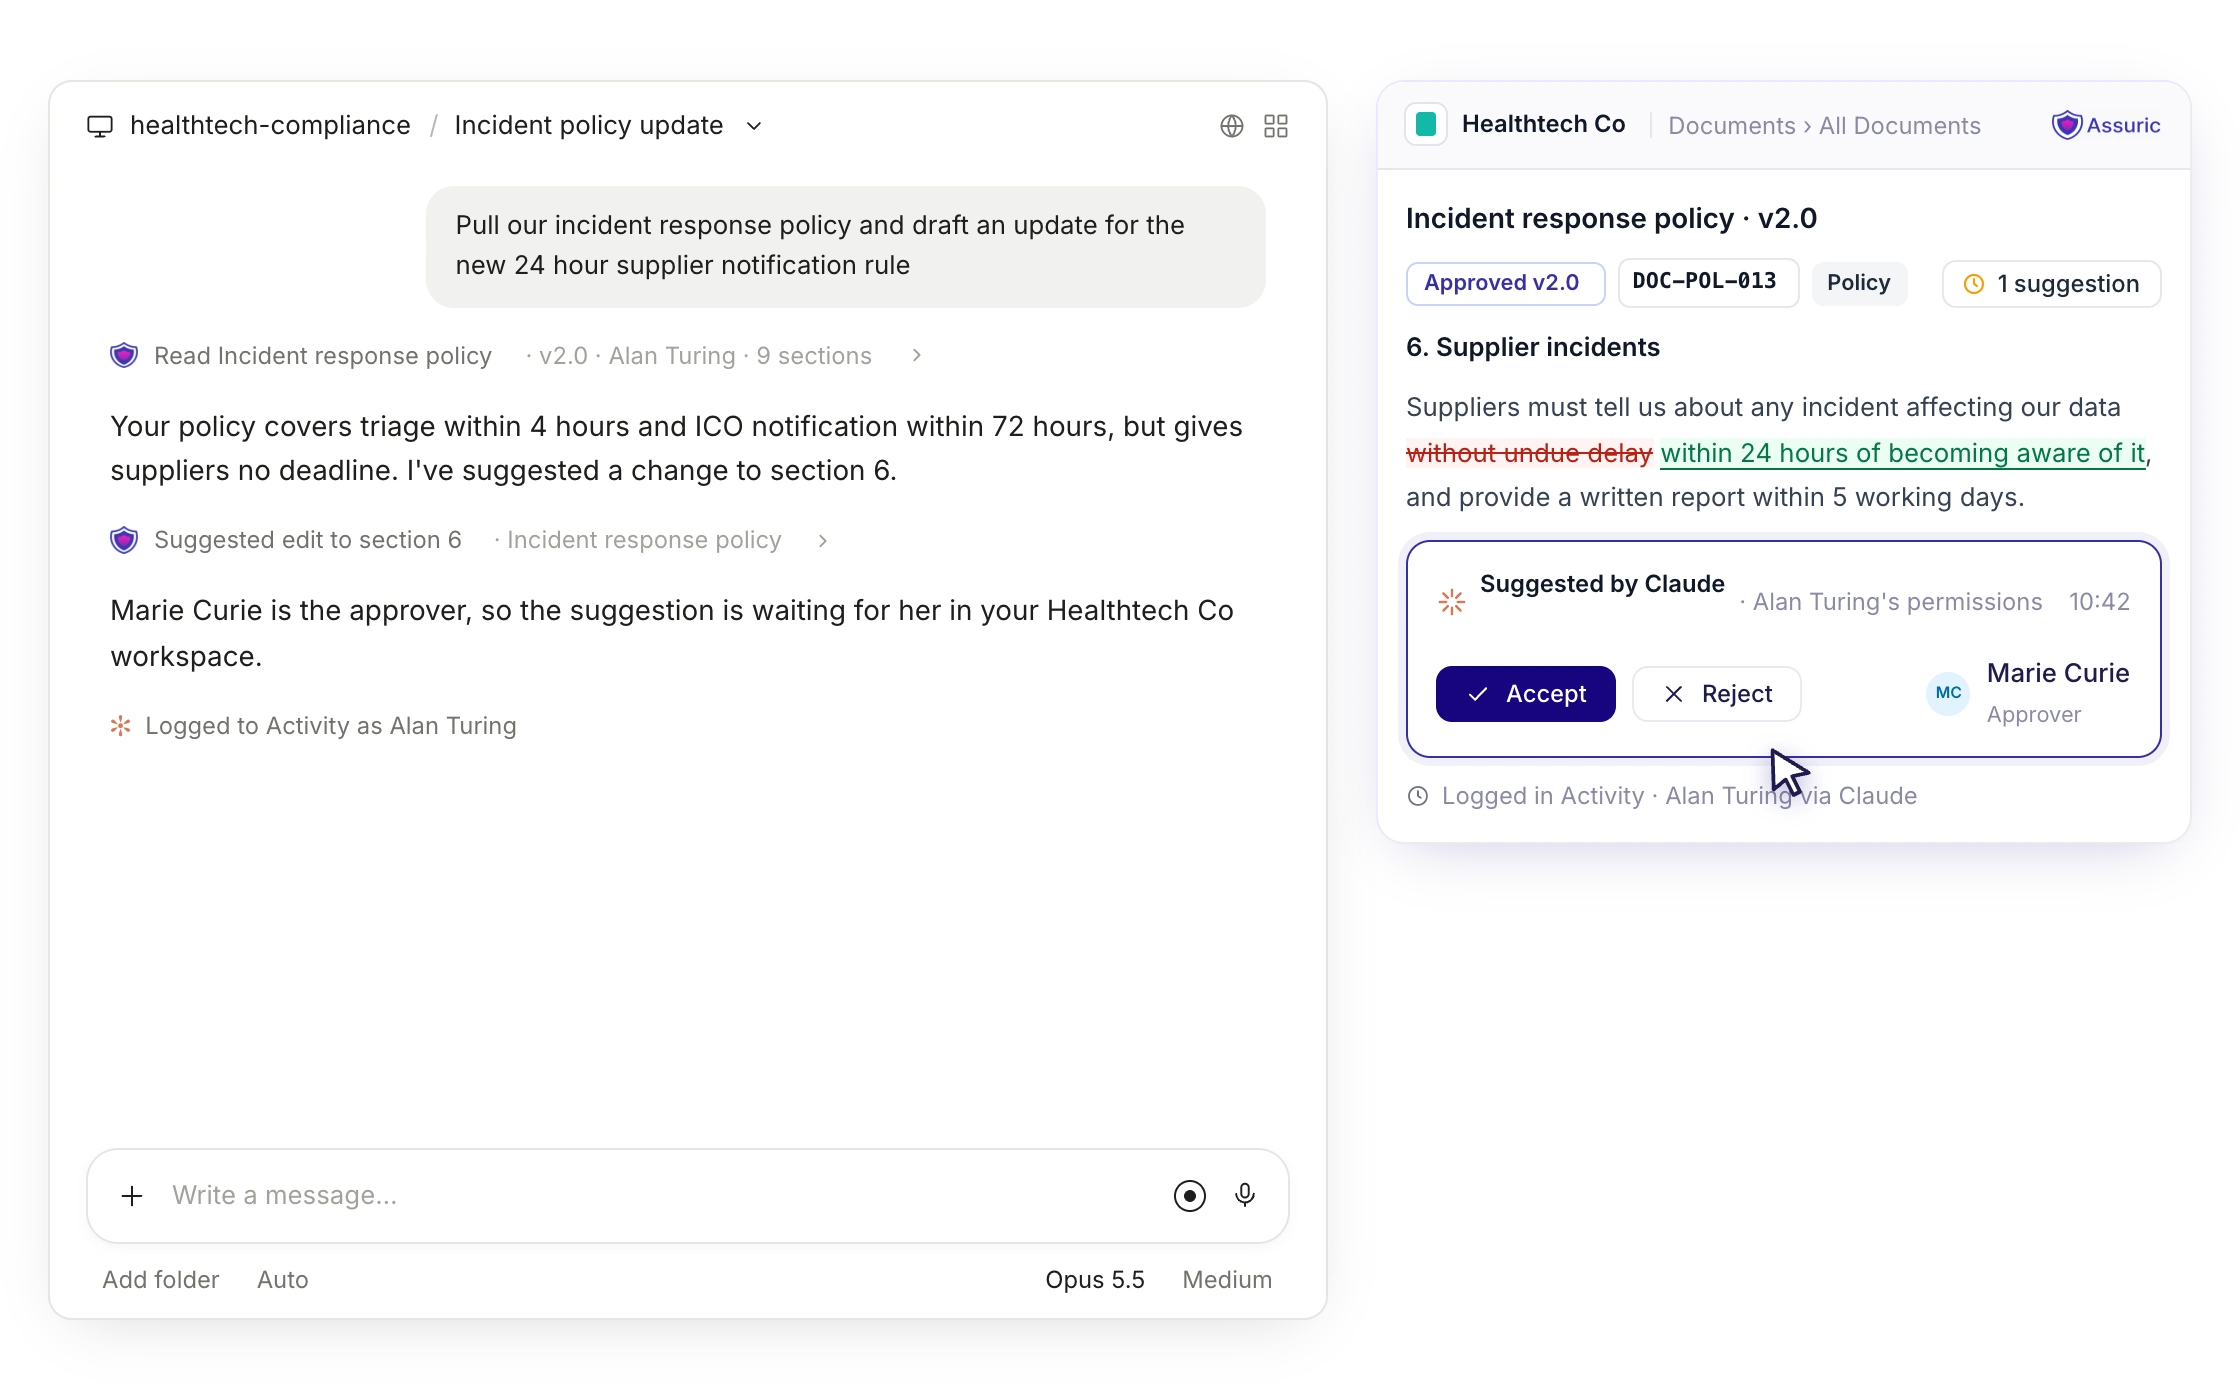
Connect Claude, ChatGPT, Copilot or Cursor through the Assuric MCP server to read and update your records.

Explore

Frameworks

Every standard the NHS asks for

Use intelligent automation to map overlapping framework requirements, reuse evidence and simplify compliance across multiple frameworks.

Less time on procurement, more time on deployment

VitVio

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”

Maks Kozarzewski

COO, VitVio

Accenture

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”

Paul Llewellyn

CCIO, Accenture

Tandem Health

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”

Katie Baker

Director UK & Ireland, Tandem

Frequently asked questions

Most NHS organisations ask suppliers for DTAC, which brings together clinical safety (DCB0129), data protection (DSPT and UK GDPR), technical security (Cyber Essentials), interoperability and usability. Some trusts also ask for ISO 27001. Assuric scopes exactly what applies to your product and keeps it all evidenced in one place.

DTAC, the Digital Technology Assessment Criteria, is the NHS baseline assessment for digital health technologies. With Assuric, teams that prioritise it can be DTAC ready in under four weeks, because the answers are drawn from evidence you already hold. Without it, the same work typically takes months.

Usually, yes. If you process NHS patient data or have access to NHS systems, you will need to complete the Data Security and Protection Toolkit every year. Assuric keeps each assertion evidenced through the year and flags the deadline well ahead, so renewal is a check, not a rebuild.

Yes, if your product could affect patient care. DCB0129 requires a named, suitably qualified Clinical Safety Officer. Our fractional CSO service can draft your safety case and hazard assessment and sign them off, without you hiring one.

DTAC asks for Cyber Essentials certification as part of its technical security section, so most NHS suppliers need it. Assuric includes an in-platform Cyber Essentials assessment, and our team can support Cyber Essentials Plus certification.

DCB0129 applies to the manufacturers of health IT systems, and DCB0160 applies to the NHS organisations that deploy them. As a supplier you own DCB0129, and your NHS customer uses your DCB0129 safety case to complete their DCB0160, so getting it right speeds up their deployment too.

Your DTAC, DSPT, DCB0129 and security evidence is kept current in one place and mapped across frameworks, so each new trust’s questions are answered from work you have already done. You can also share it through your Trust Centre, so buyers can review it before they ask.

Get assured and deployed
in the NHS, faster

See how Assuric prepares and updates your DTAC, DCB0129 and IG evidence, ready for every trust.