Every framework, mapped once
Track NHS, CQC, data protection, security, medical device and international frameworks side by side, with requirements and evidence mapped across them so nothing is done twice.
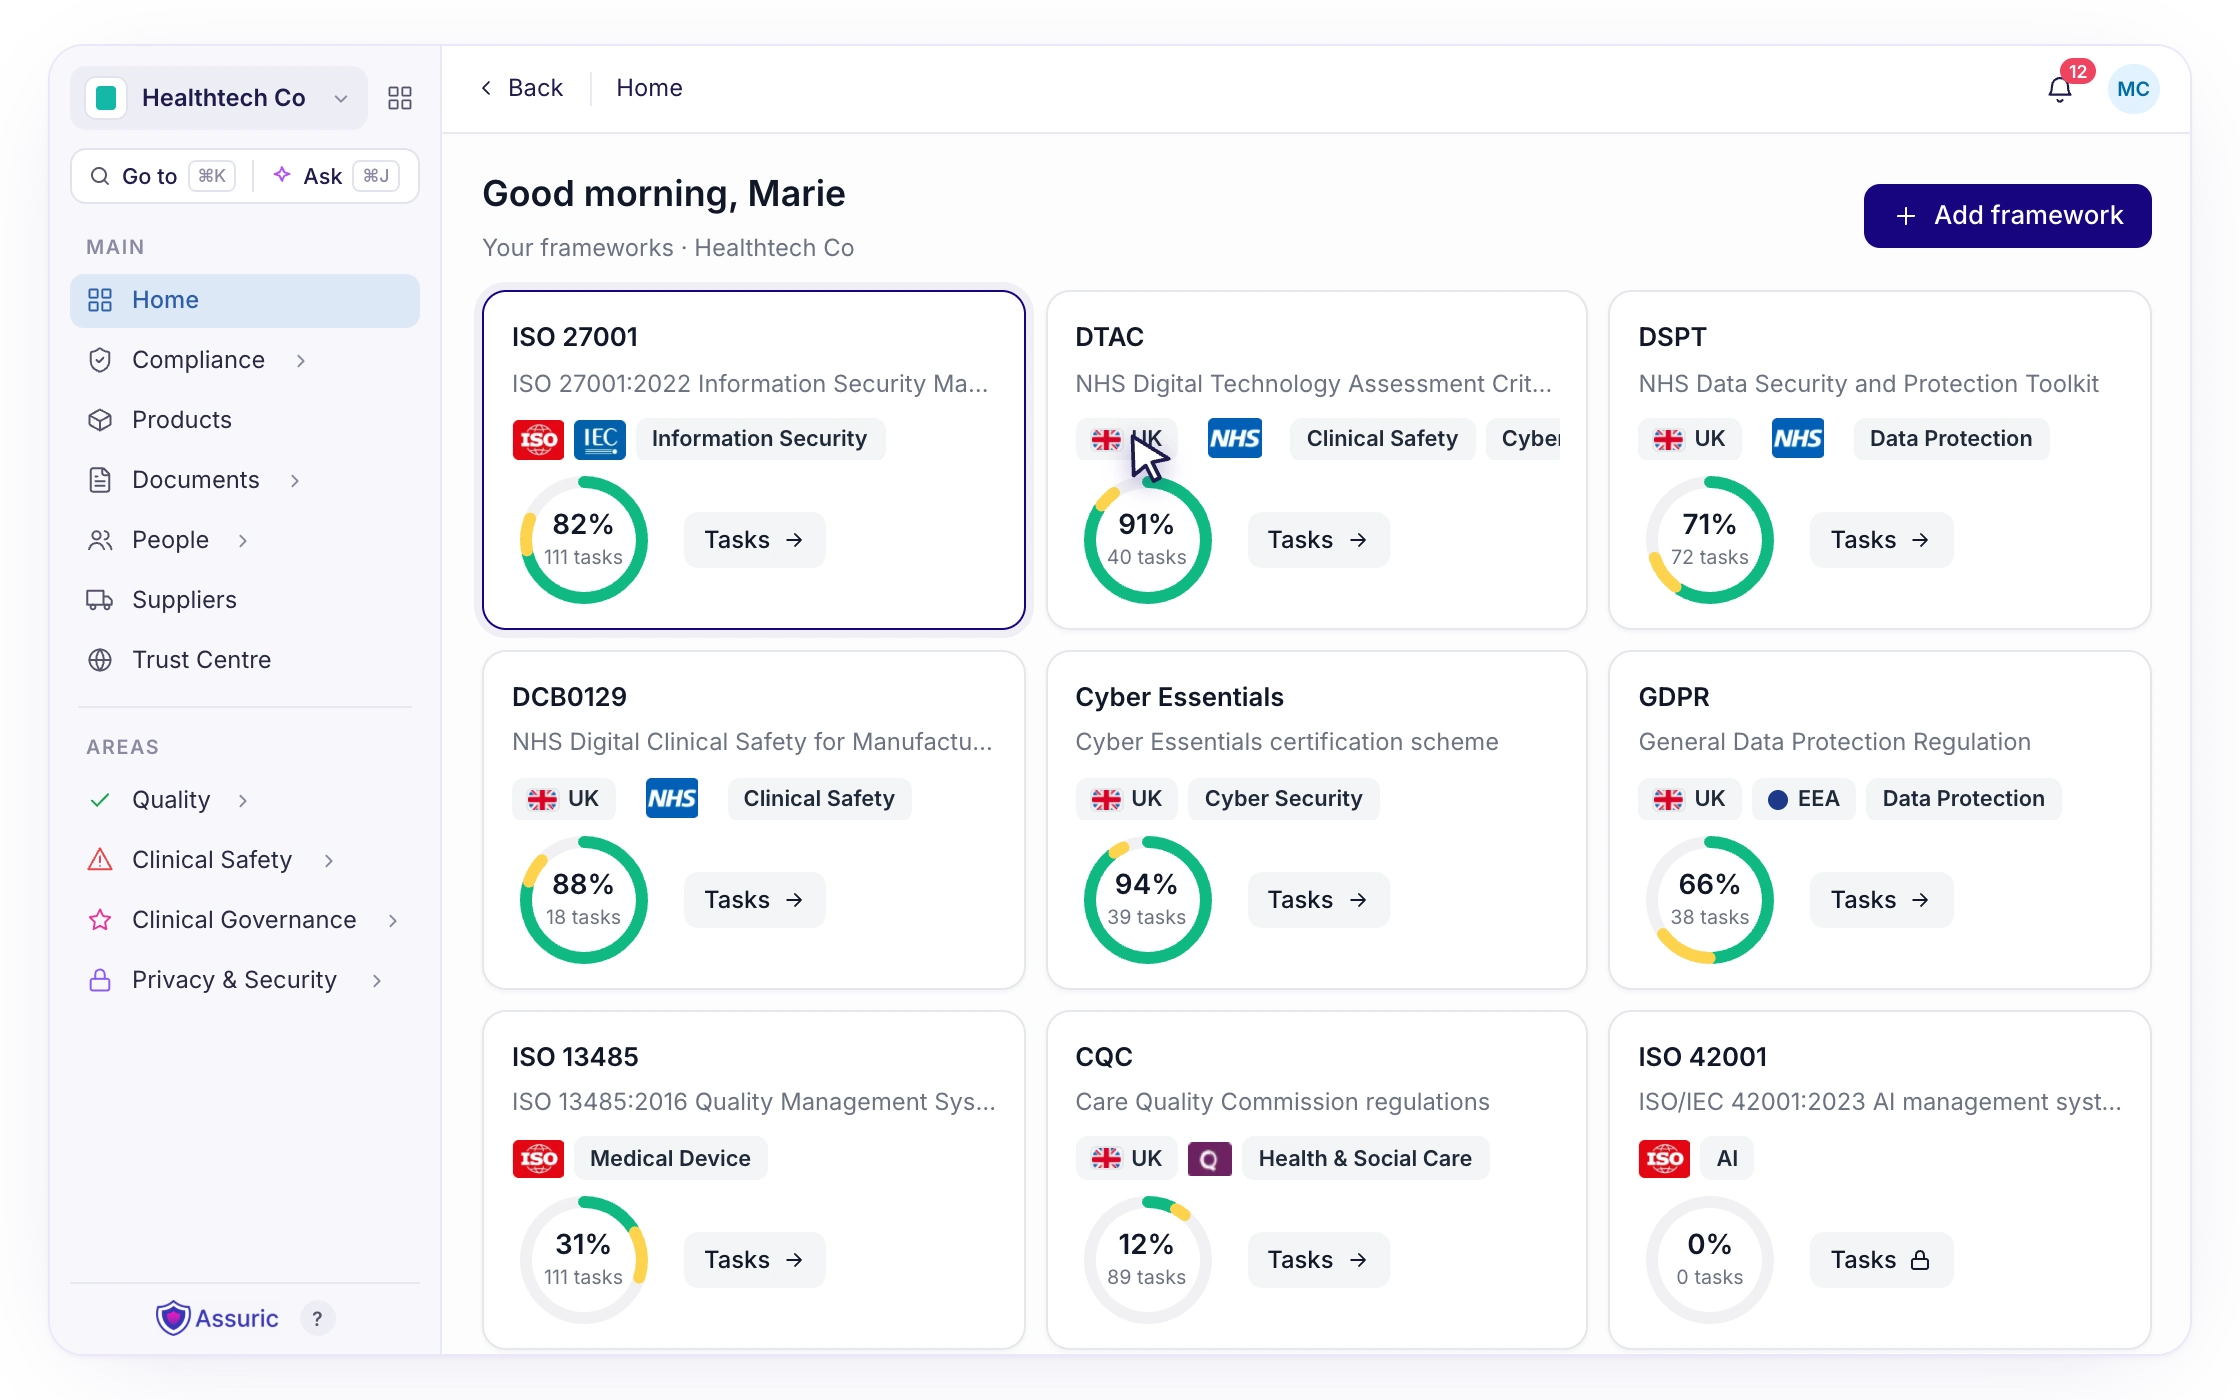
The only platform that covers international data protection, cybersecurity, NHS, medical device and healthcare provider compliance in one place.
Trusted byhealthtech teams


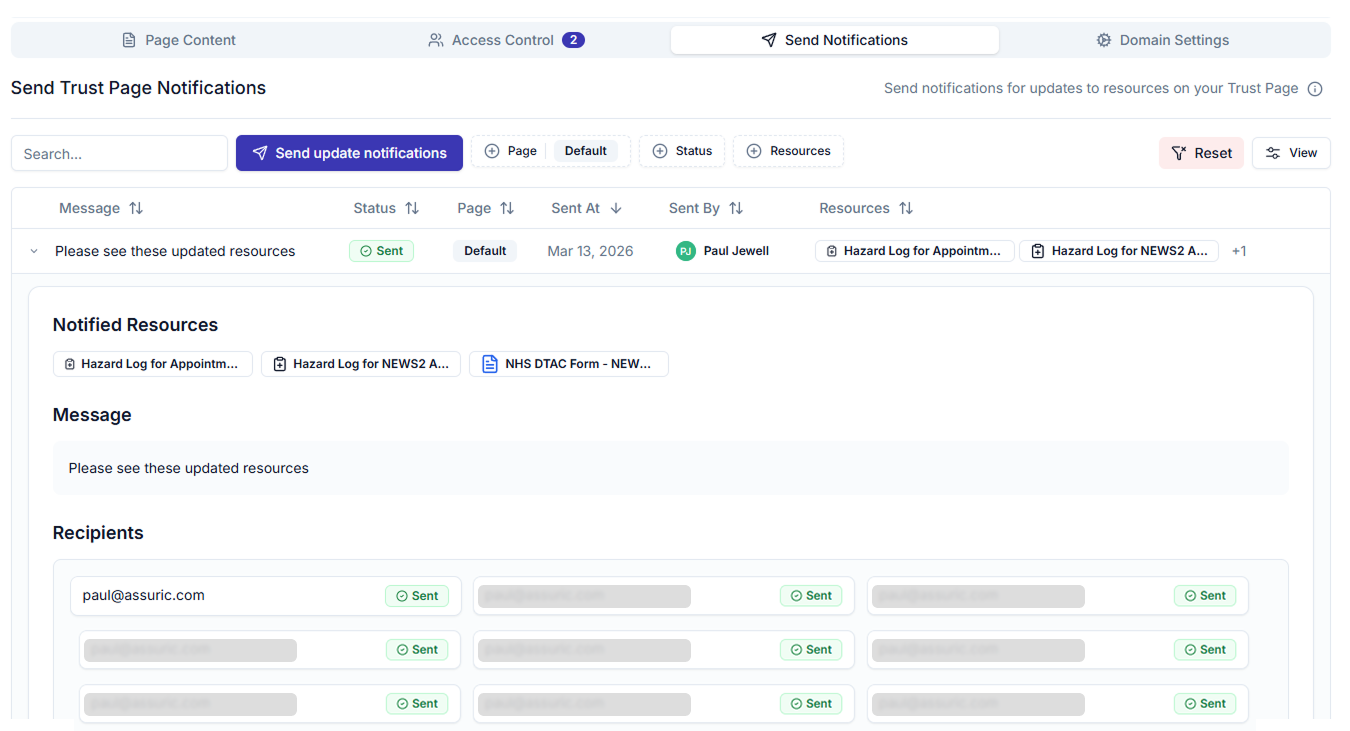
Features
Track NHS, CQC, data protection, security, medical device and international frameworks side by side, with requirements and evidence mapped across them so nothing is done twice.
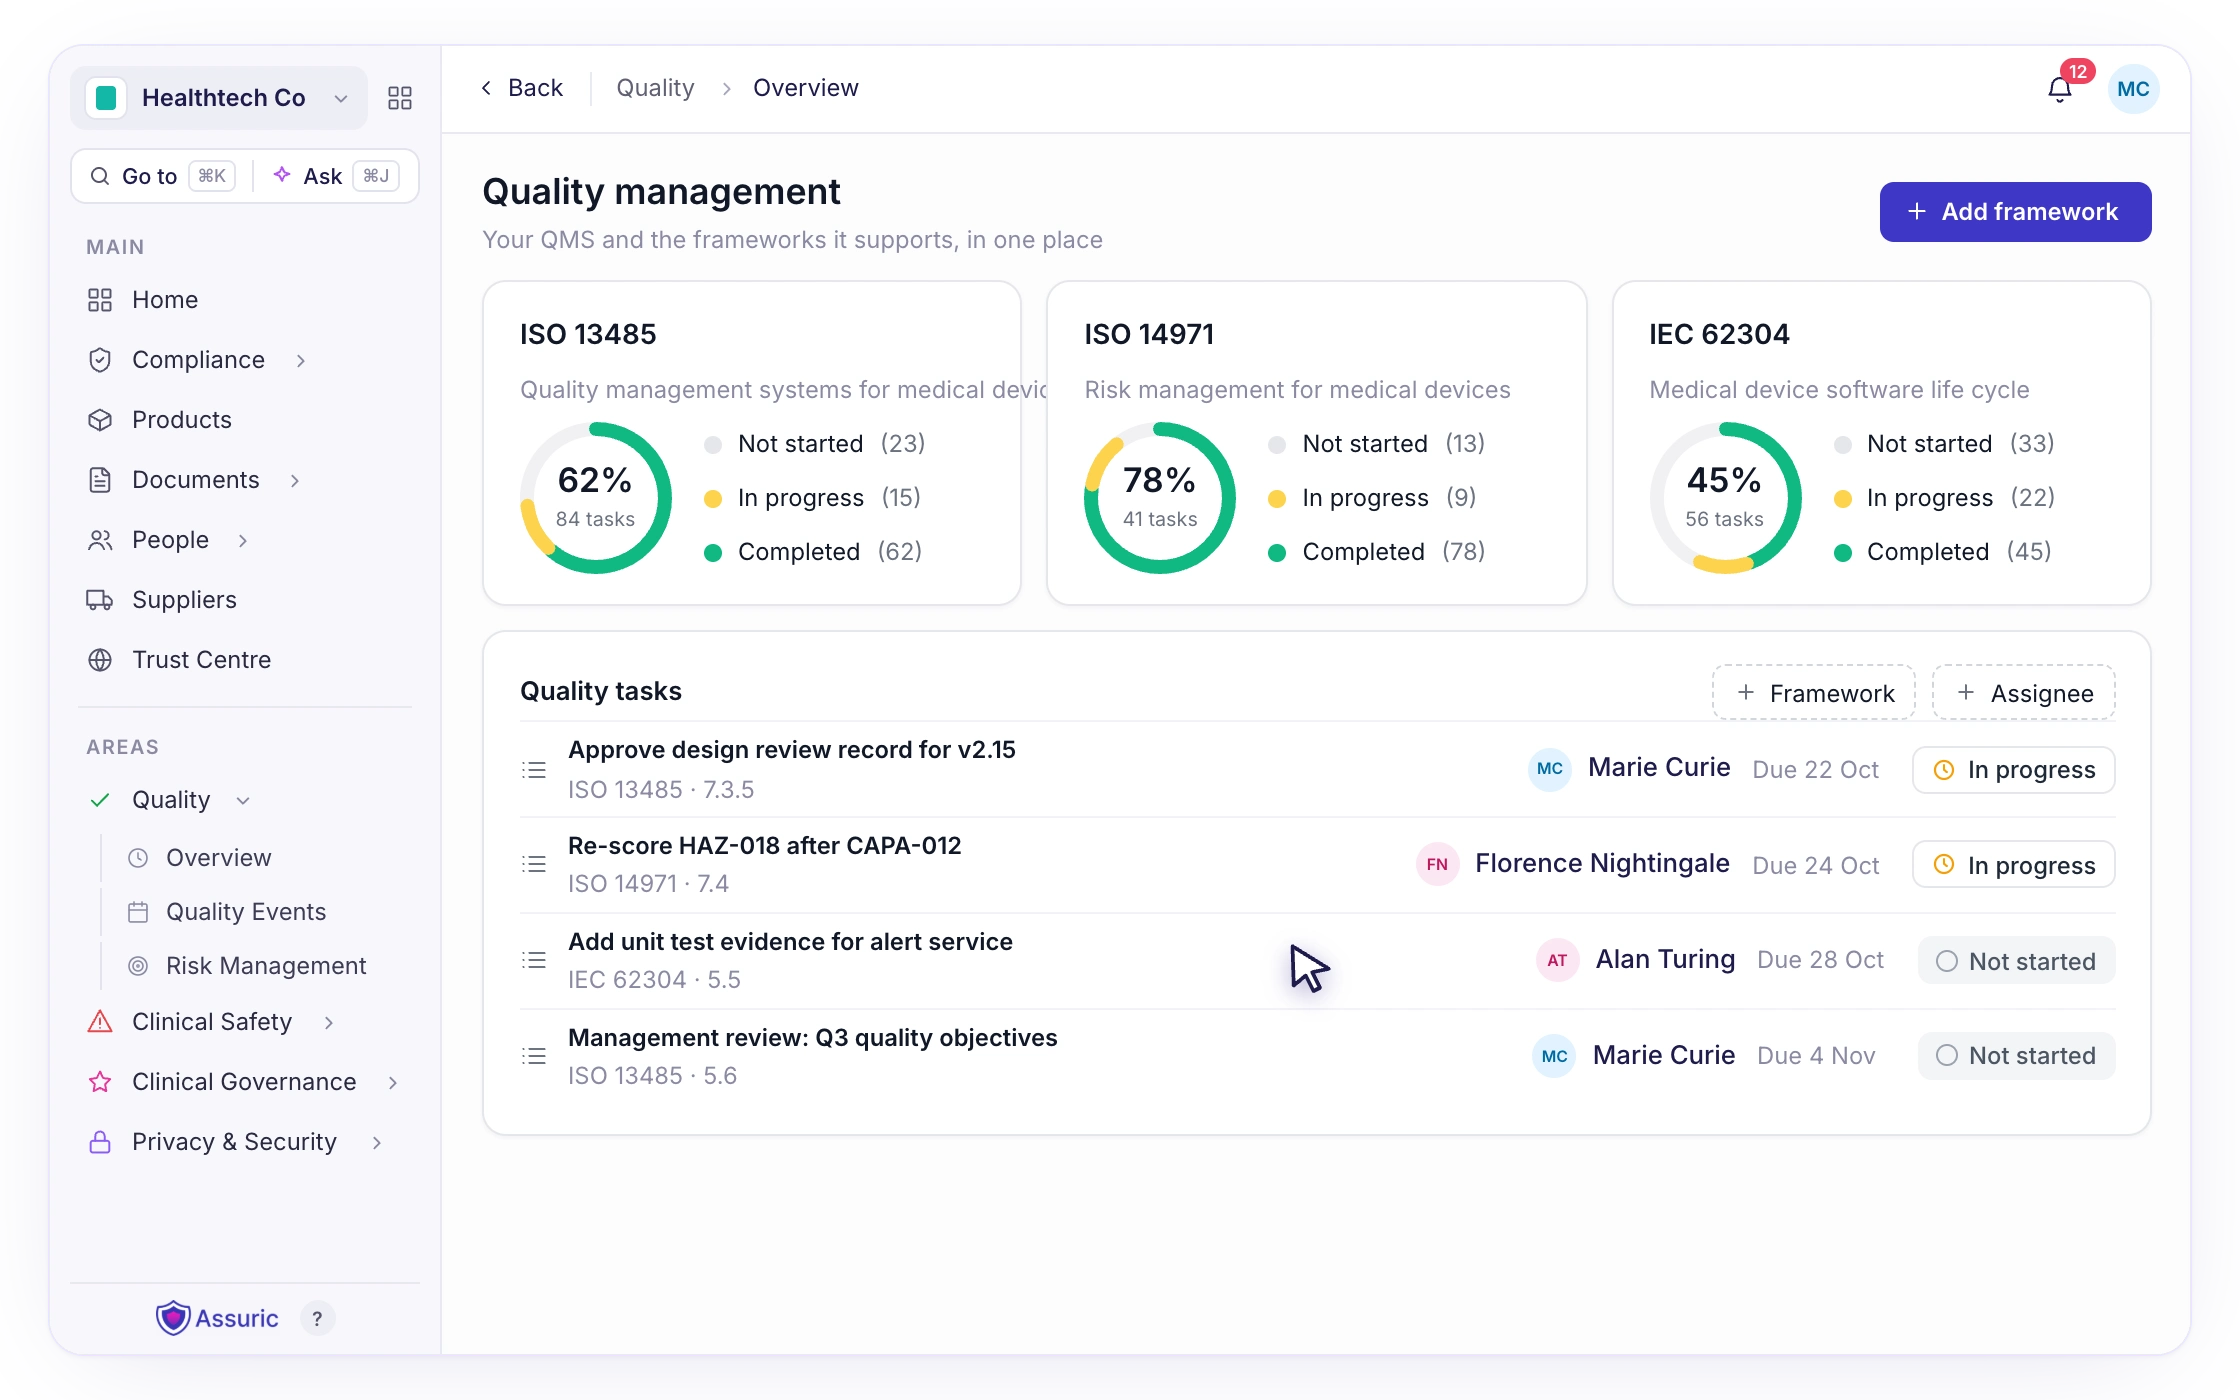
Run your quality, information security and AI management systems together, sharing documents, risks and evidence instead of maintaining three separate systems.
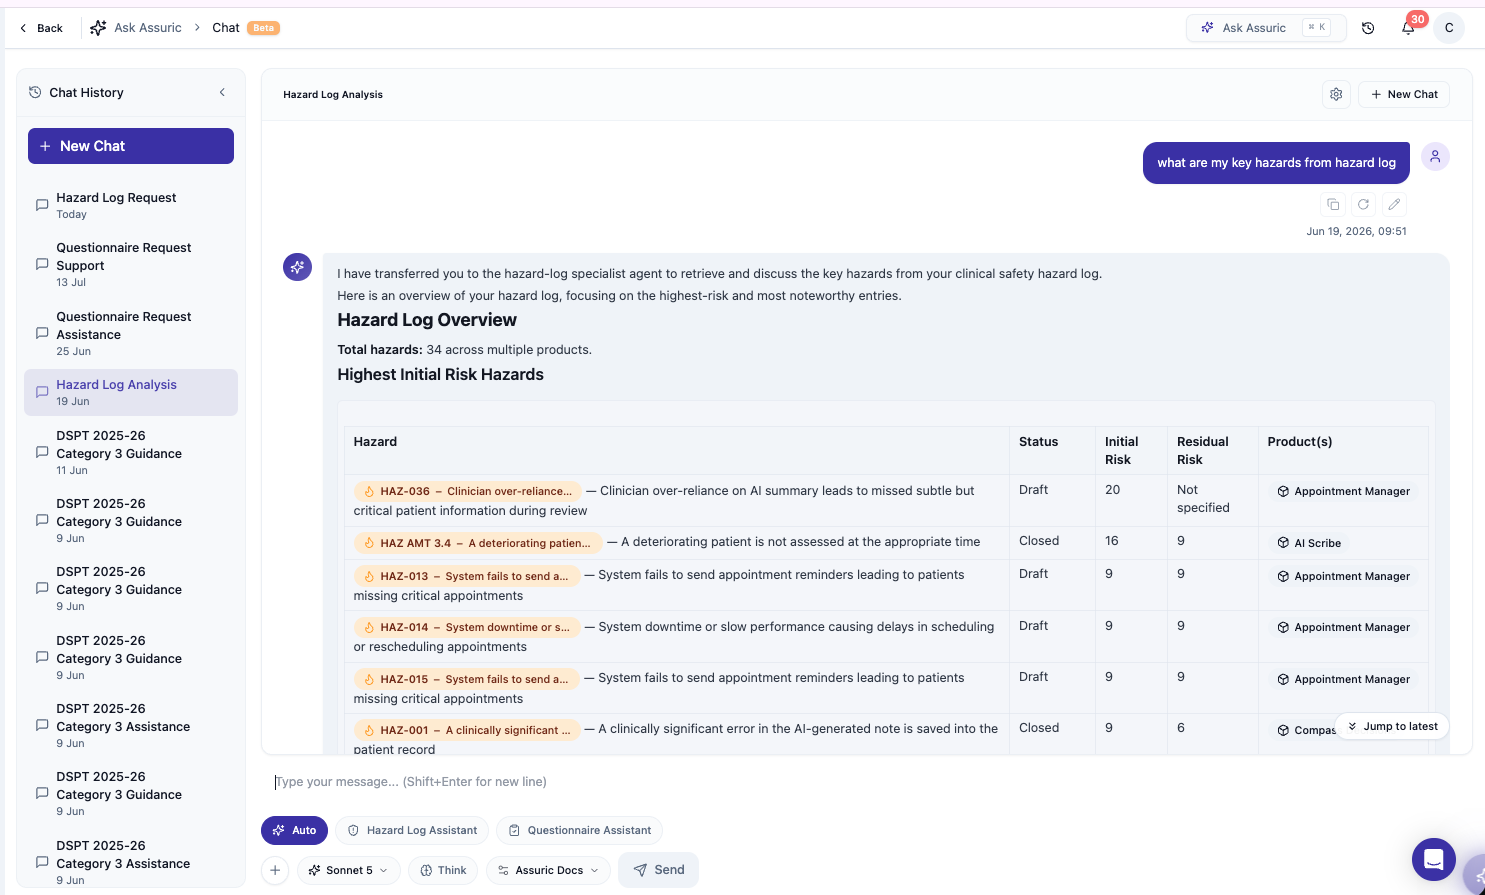
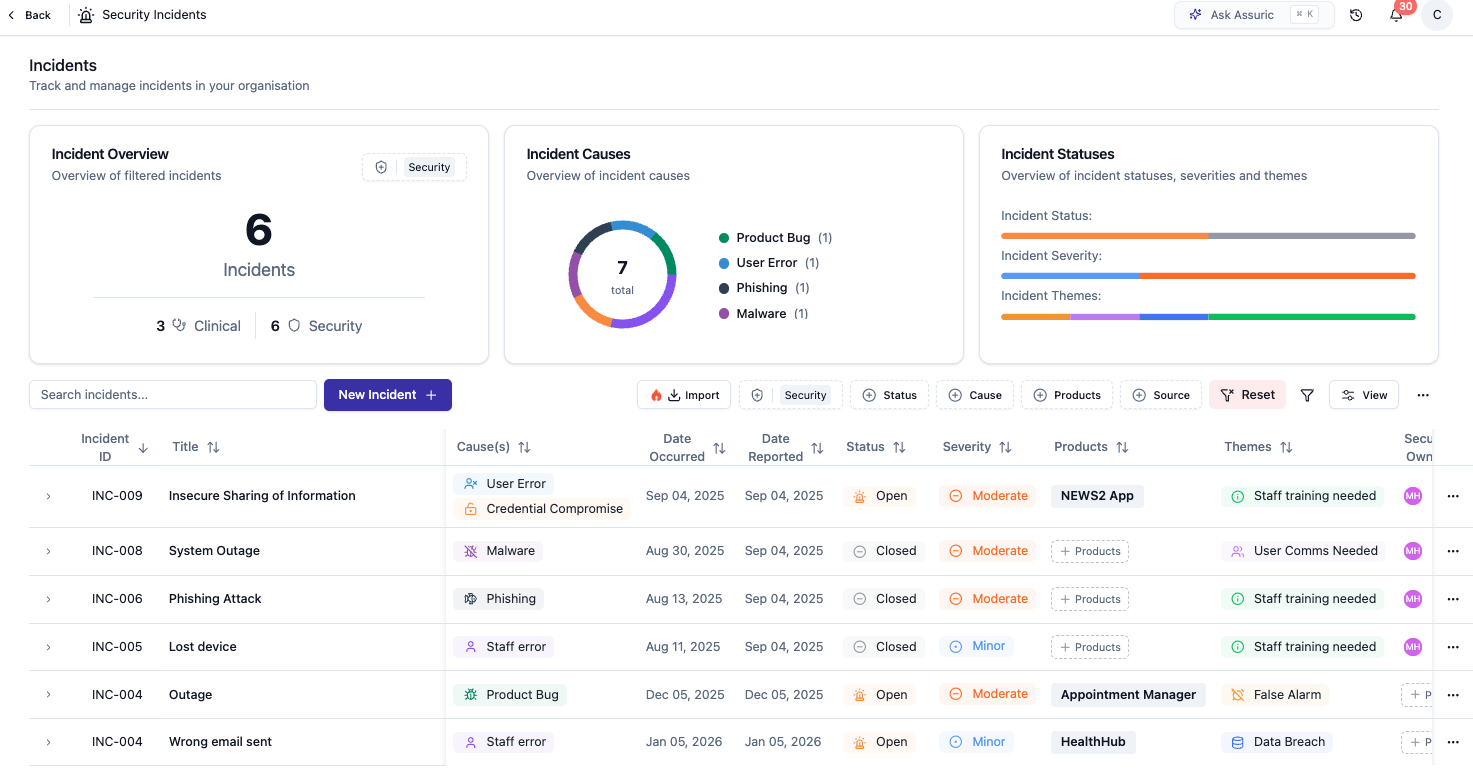
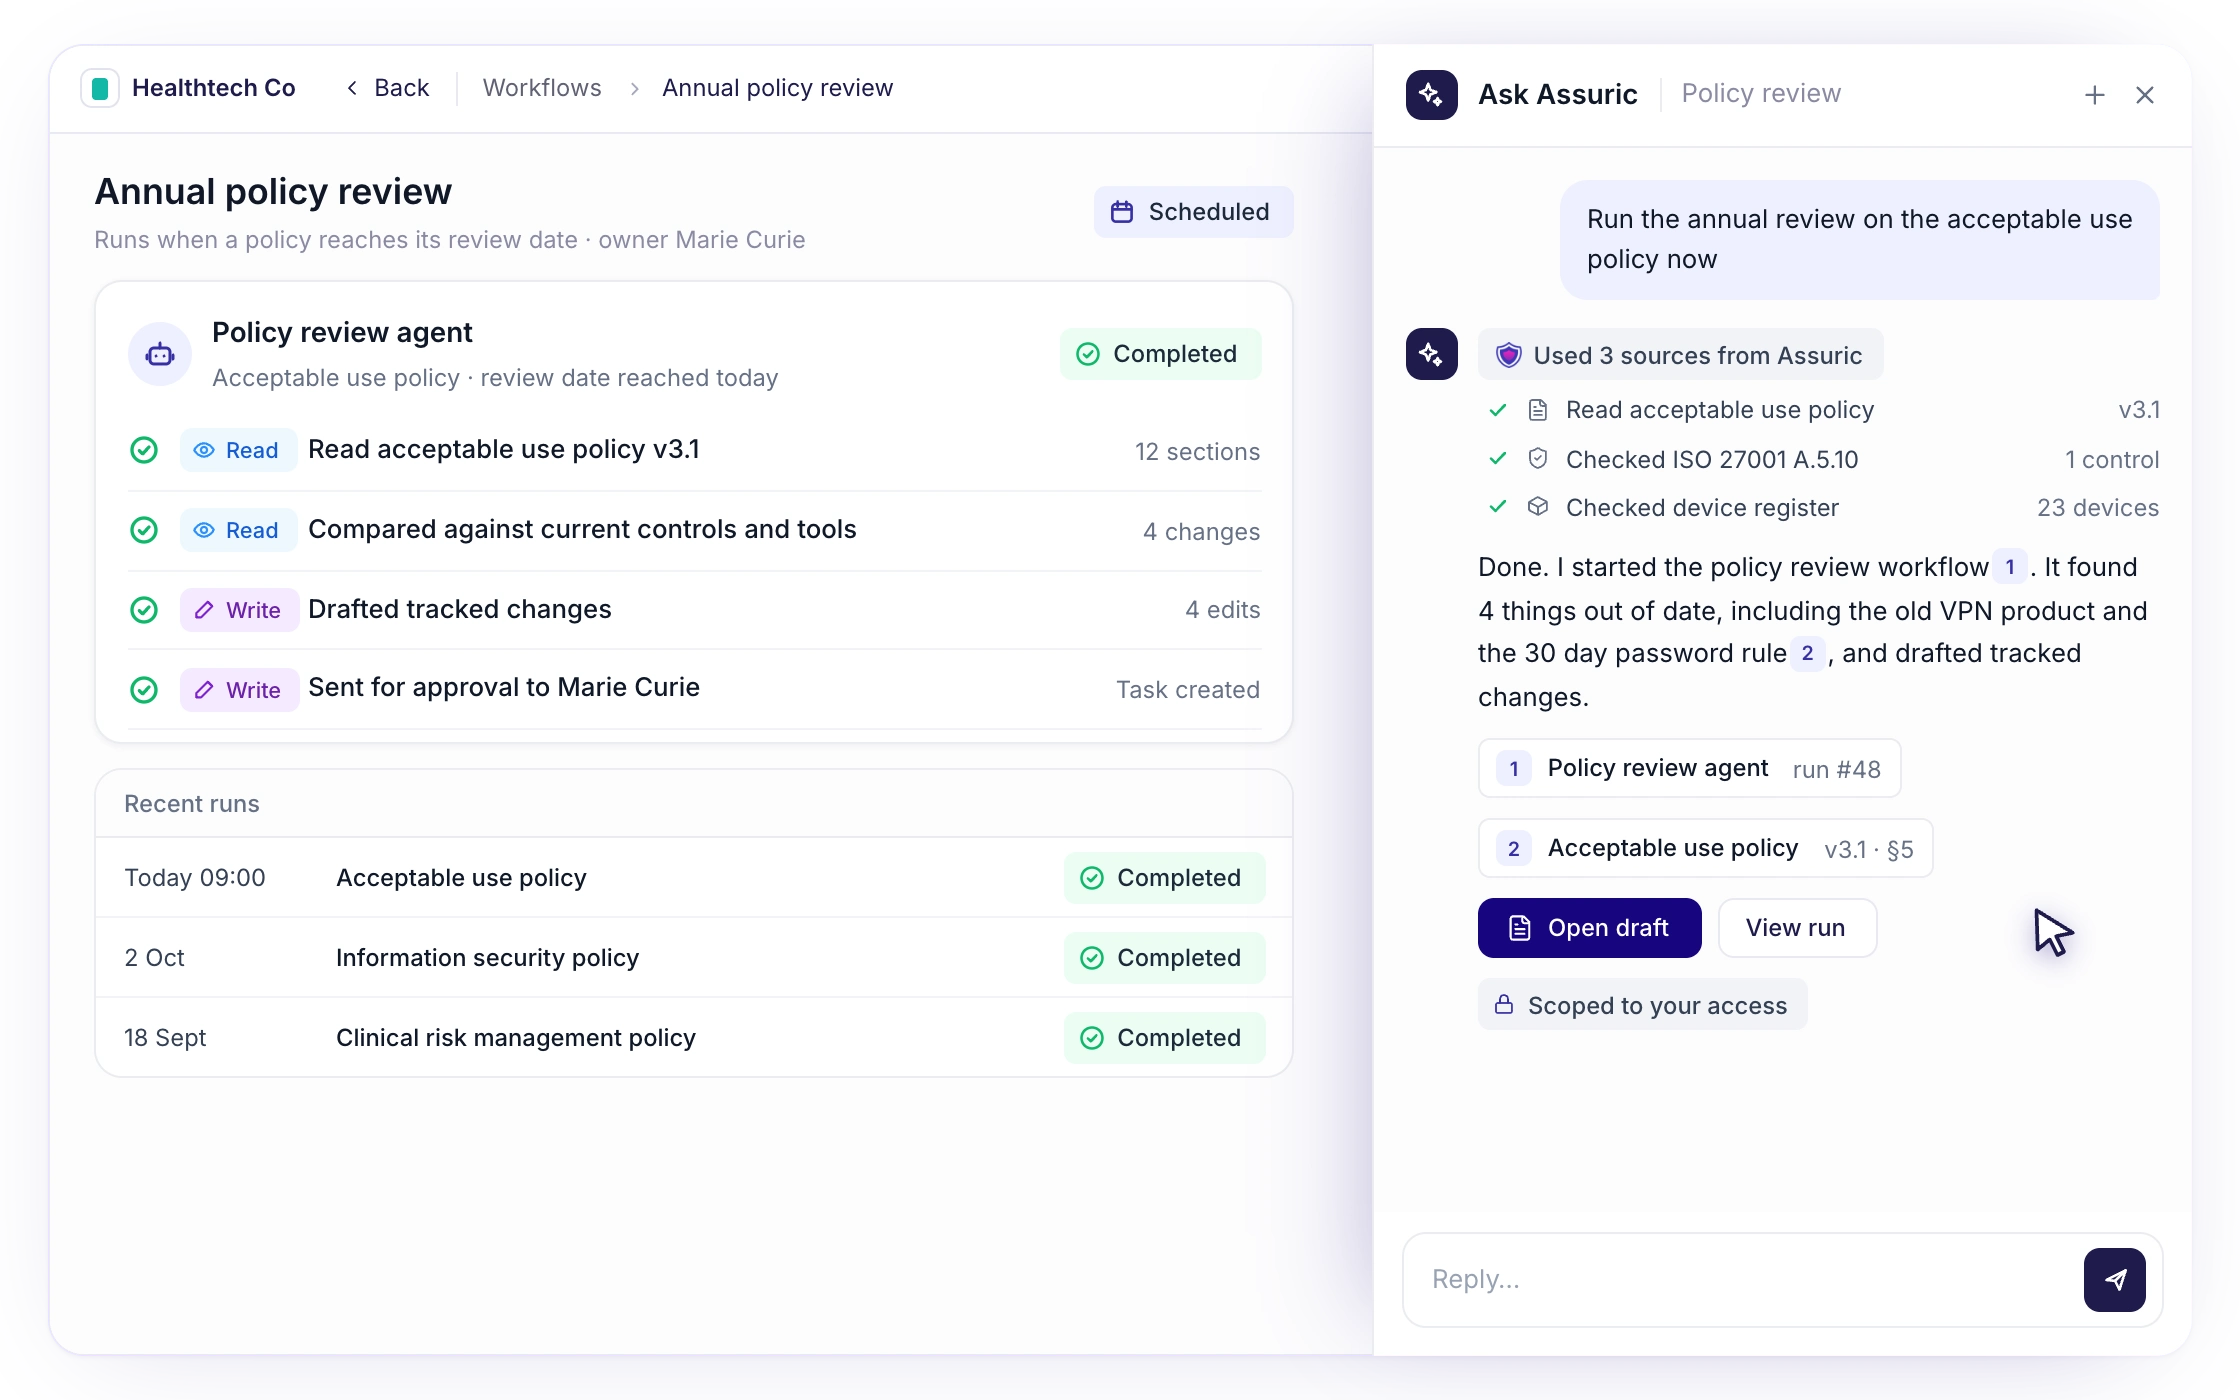
Agentic workflows, AI drafting and MCP read and write access keep records current and tasks moving, with full activity logs and enterprise-grade security keeping you in control.
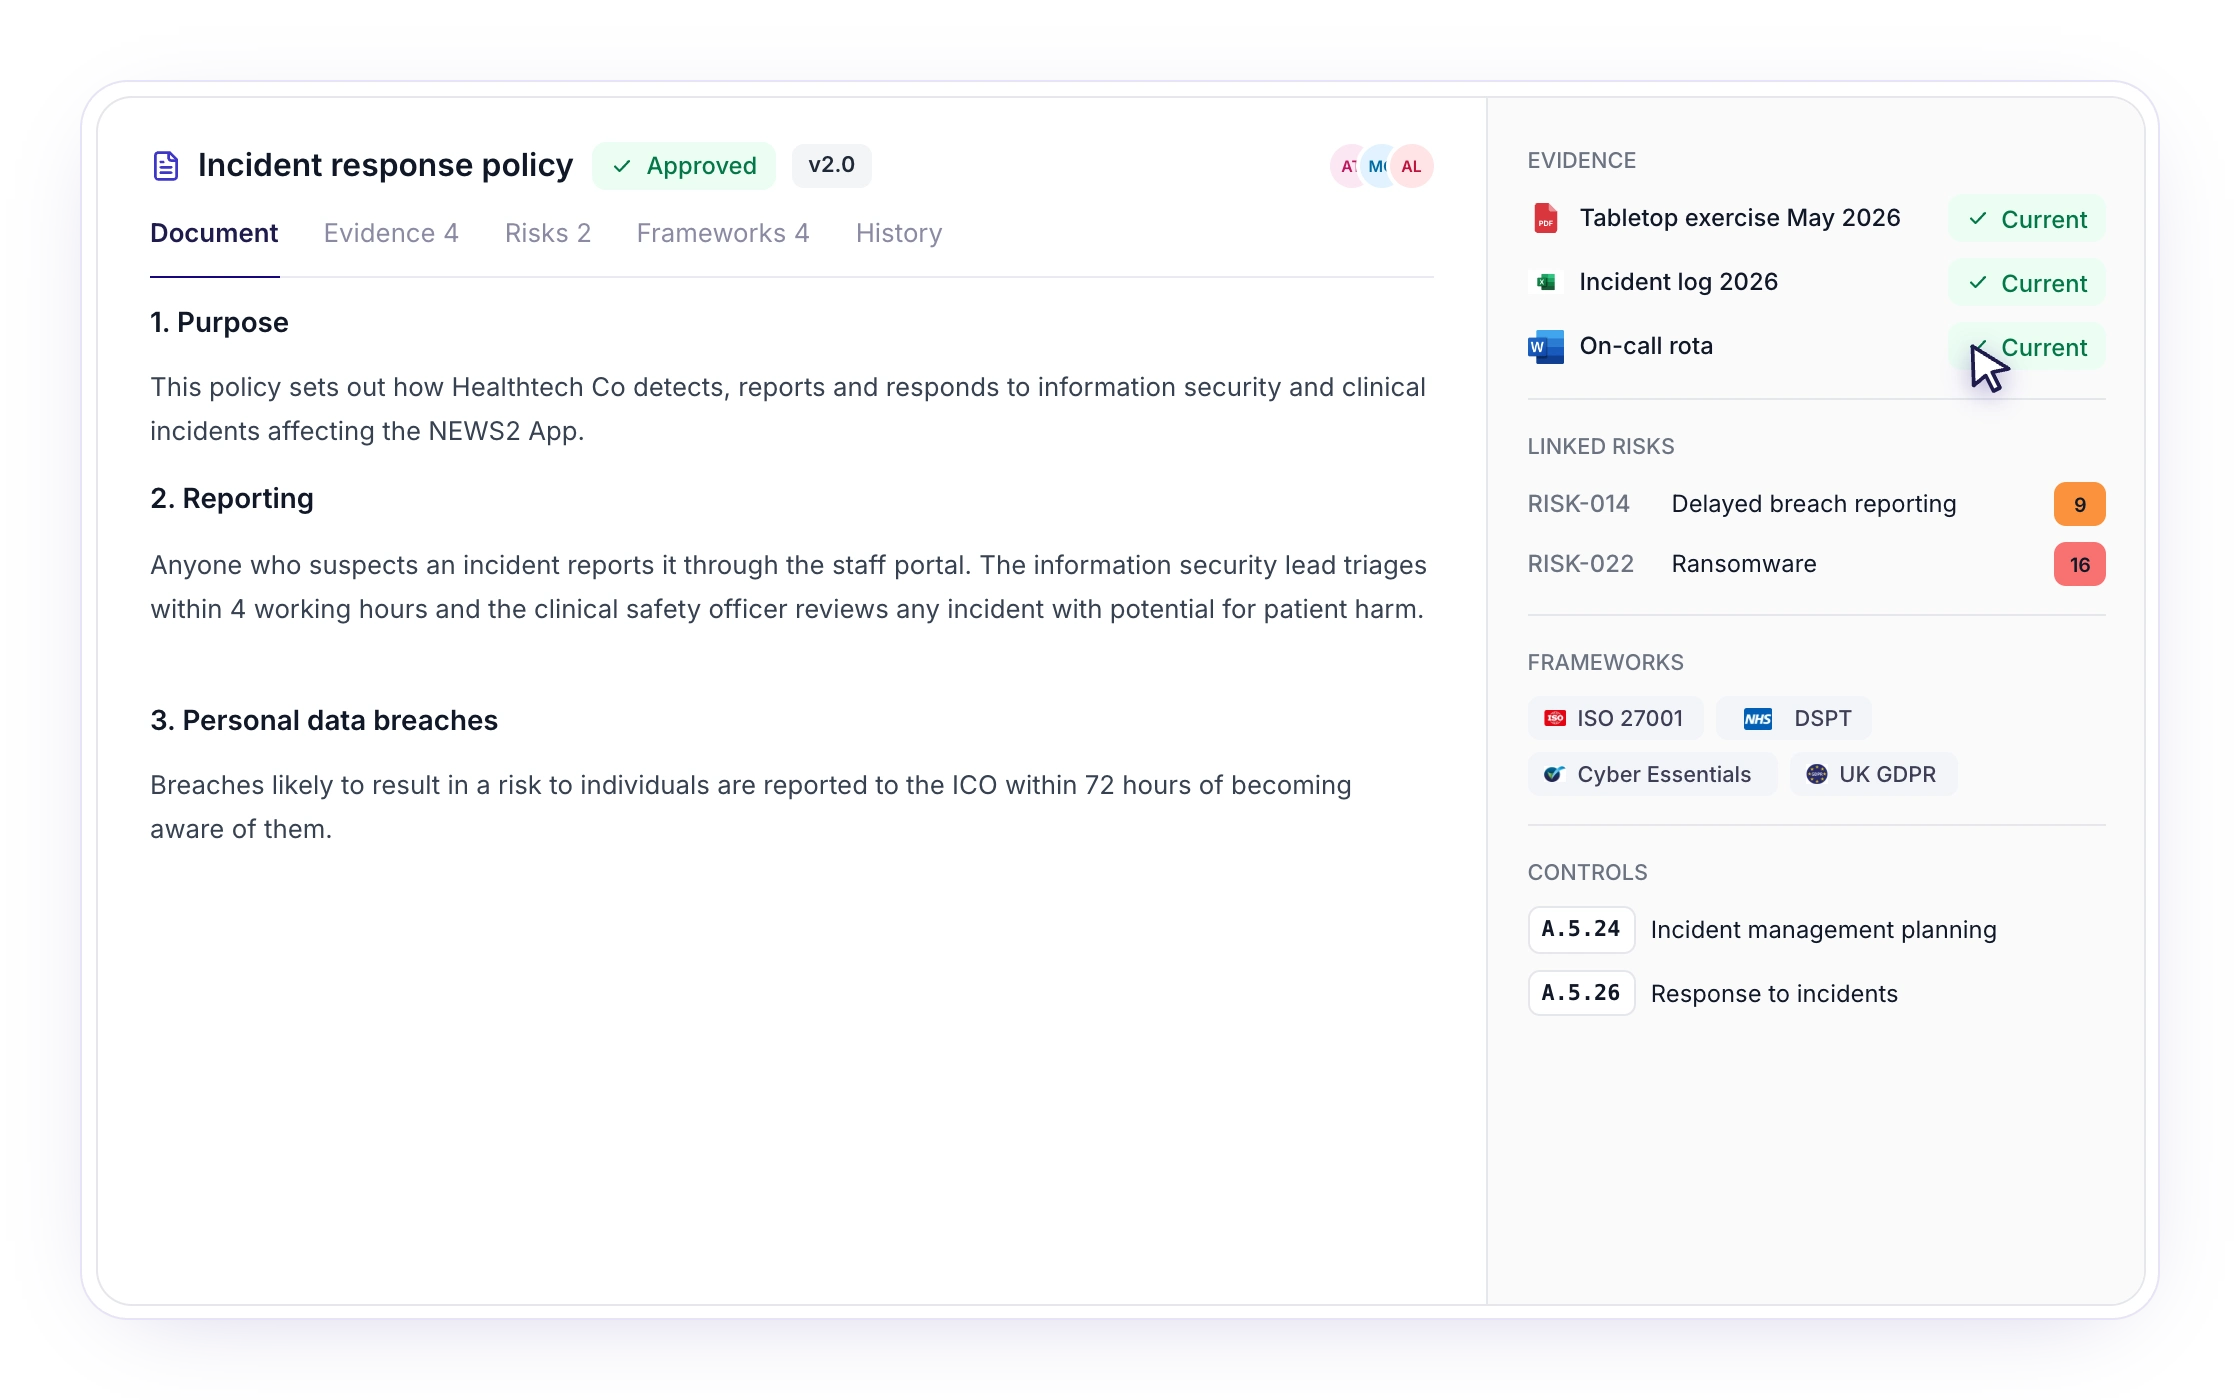
A built-in AI-native document editor and evidence repository hold your policies, risks, evidence and compliance work, all linked and version controlled.
Share your compliance position through your Trust Centre and answer security questionnaires with AI, so NHS and enterprise procurement keeps moving.
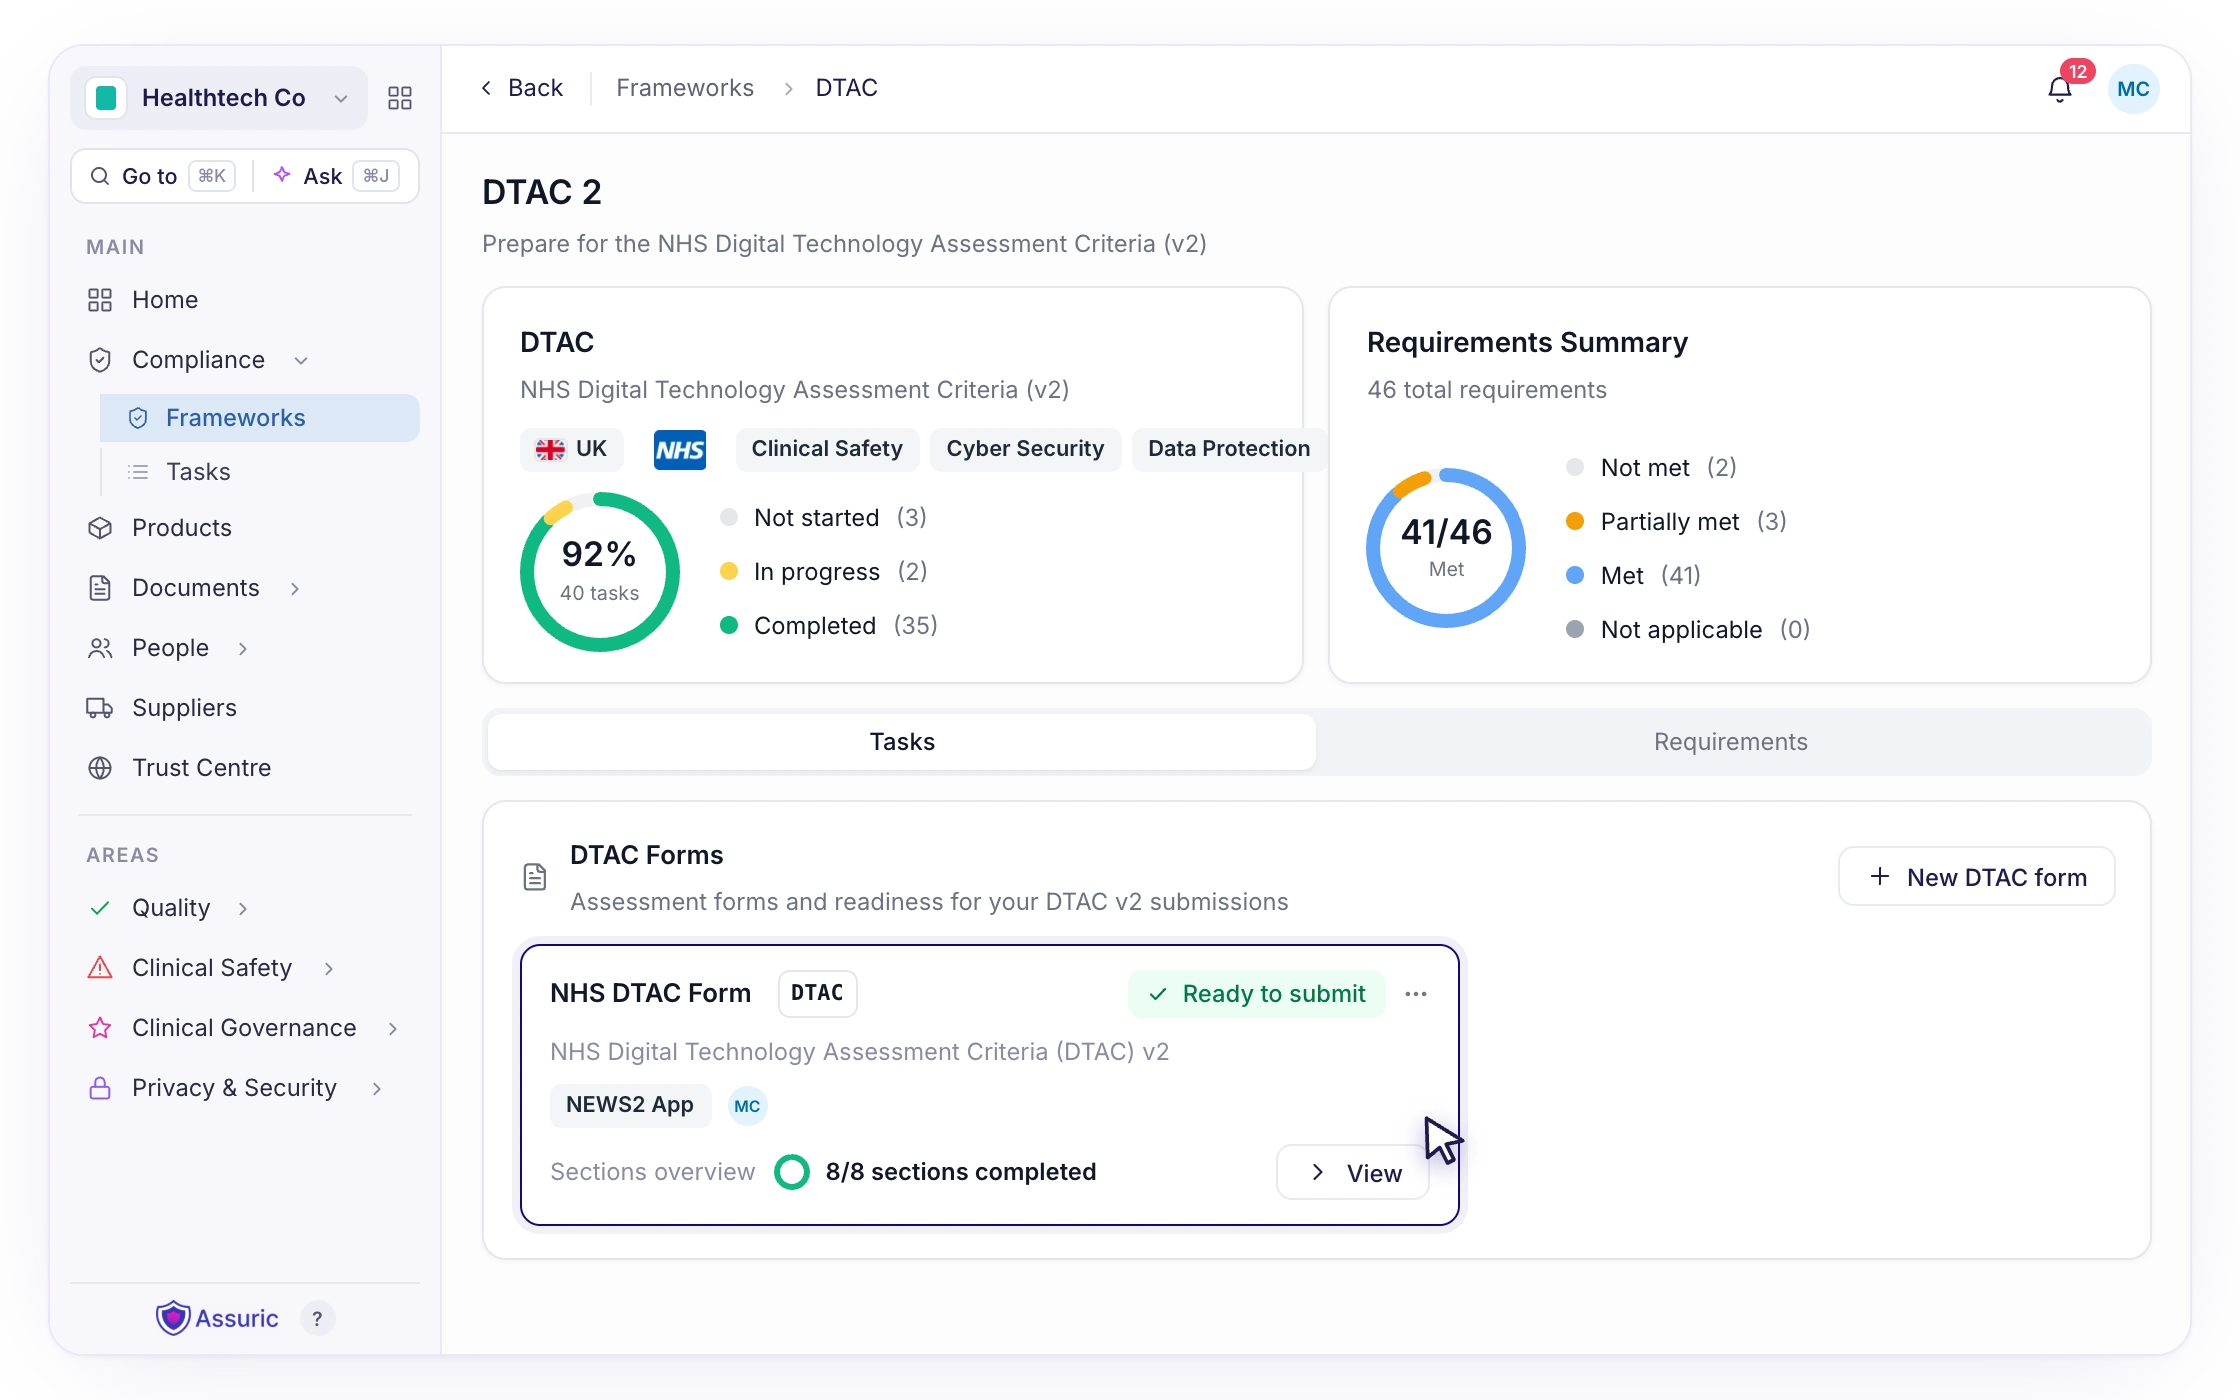
Named CSOs, DPOs and regulatory specialists can work inside your workspace through our expert support, from onboarding through to certification and audit.
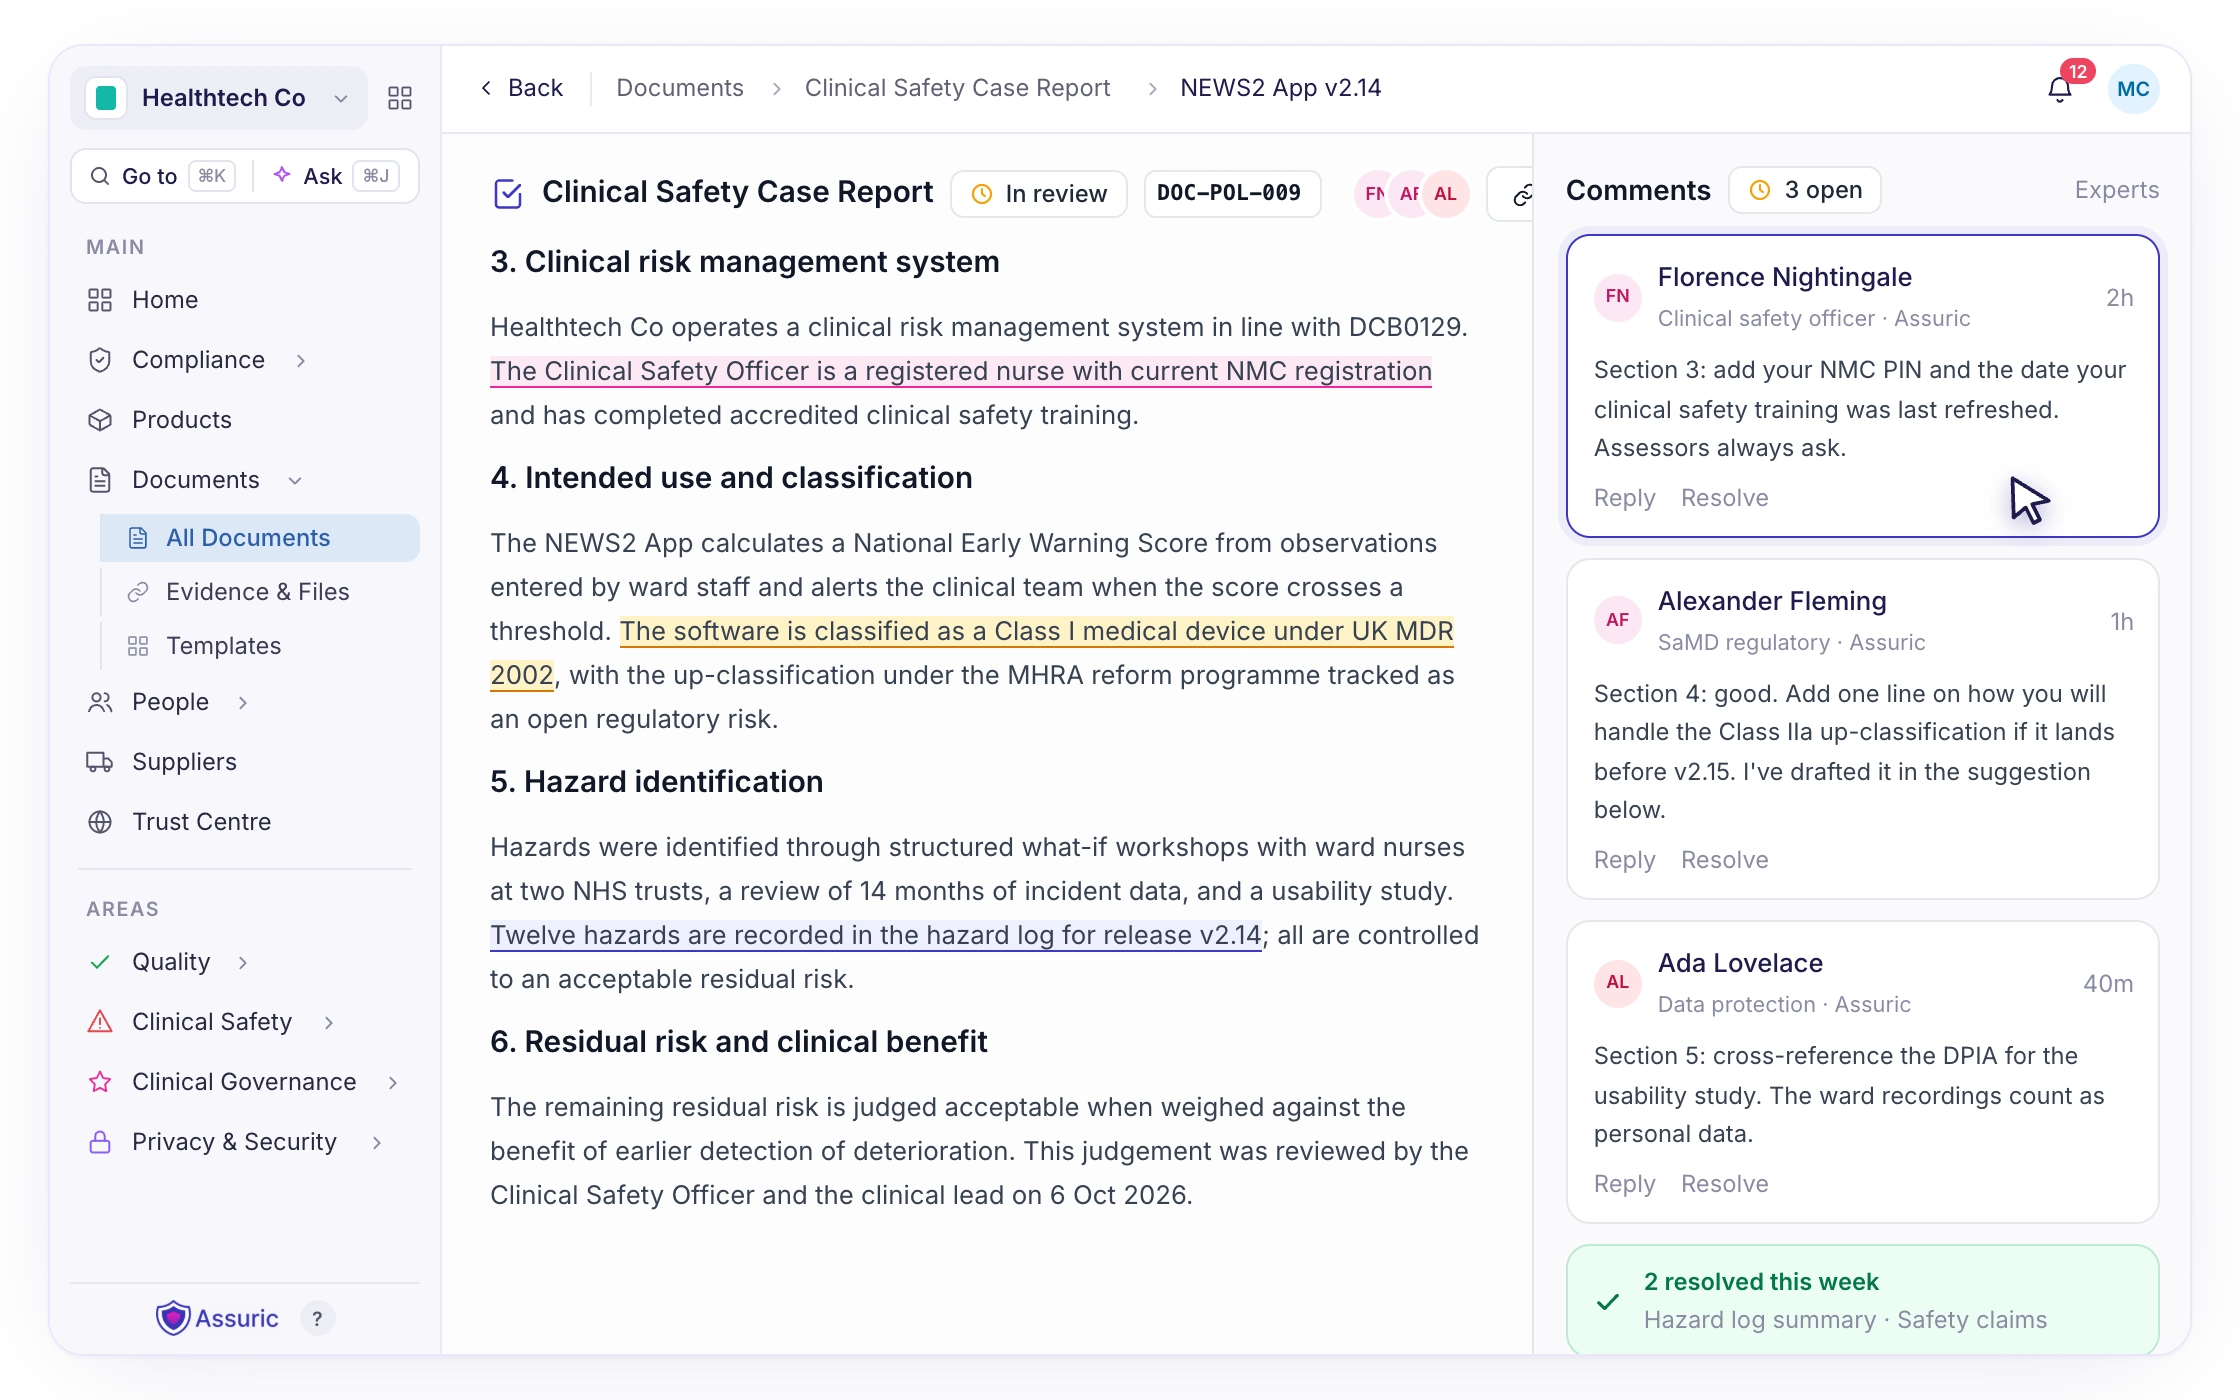
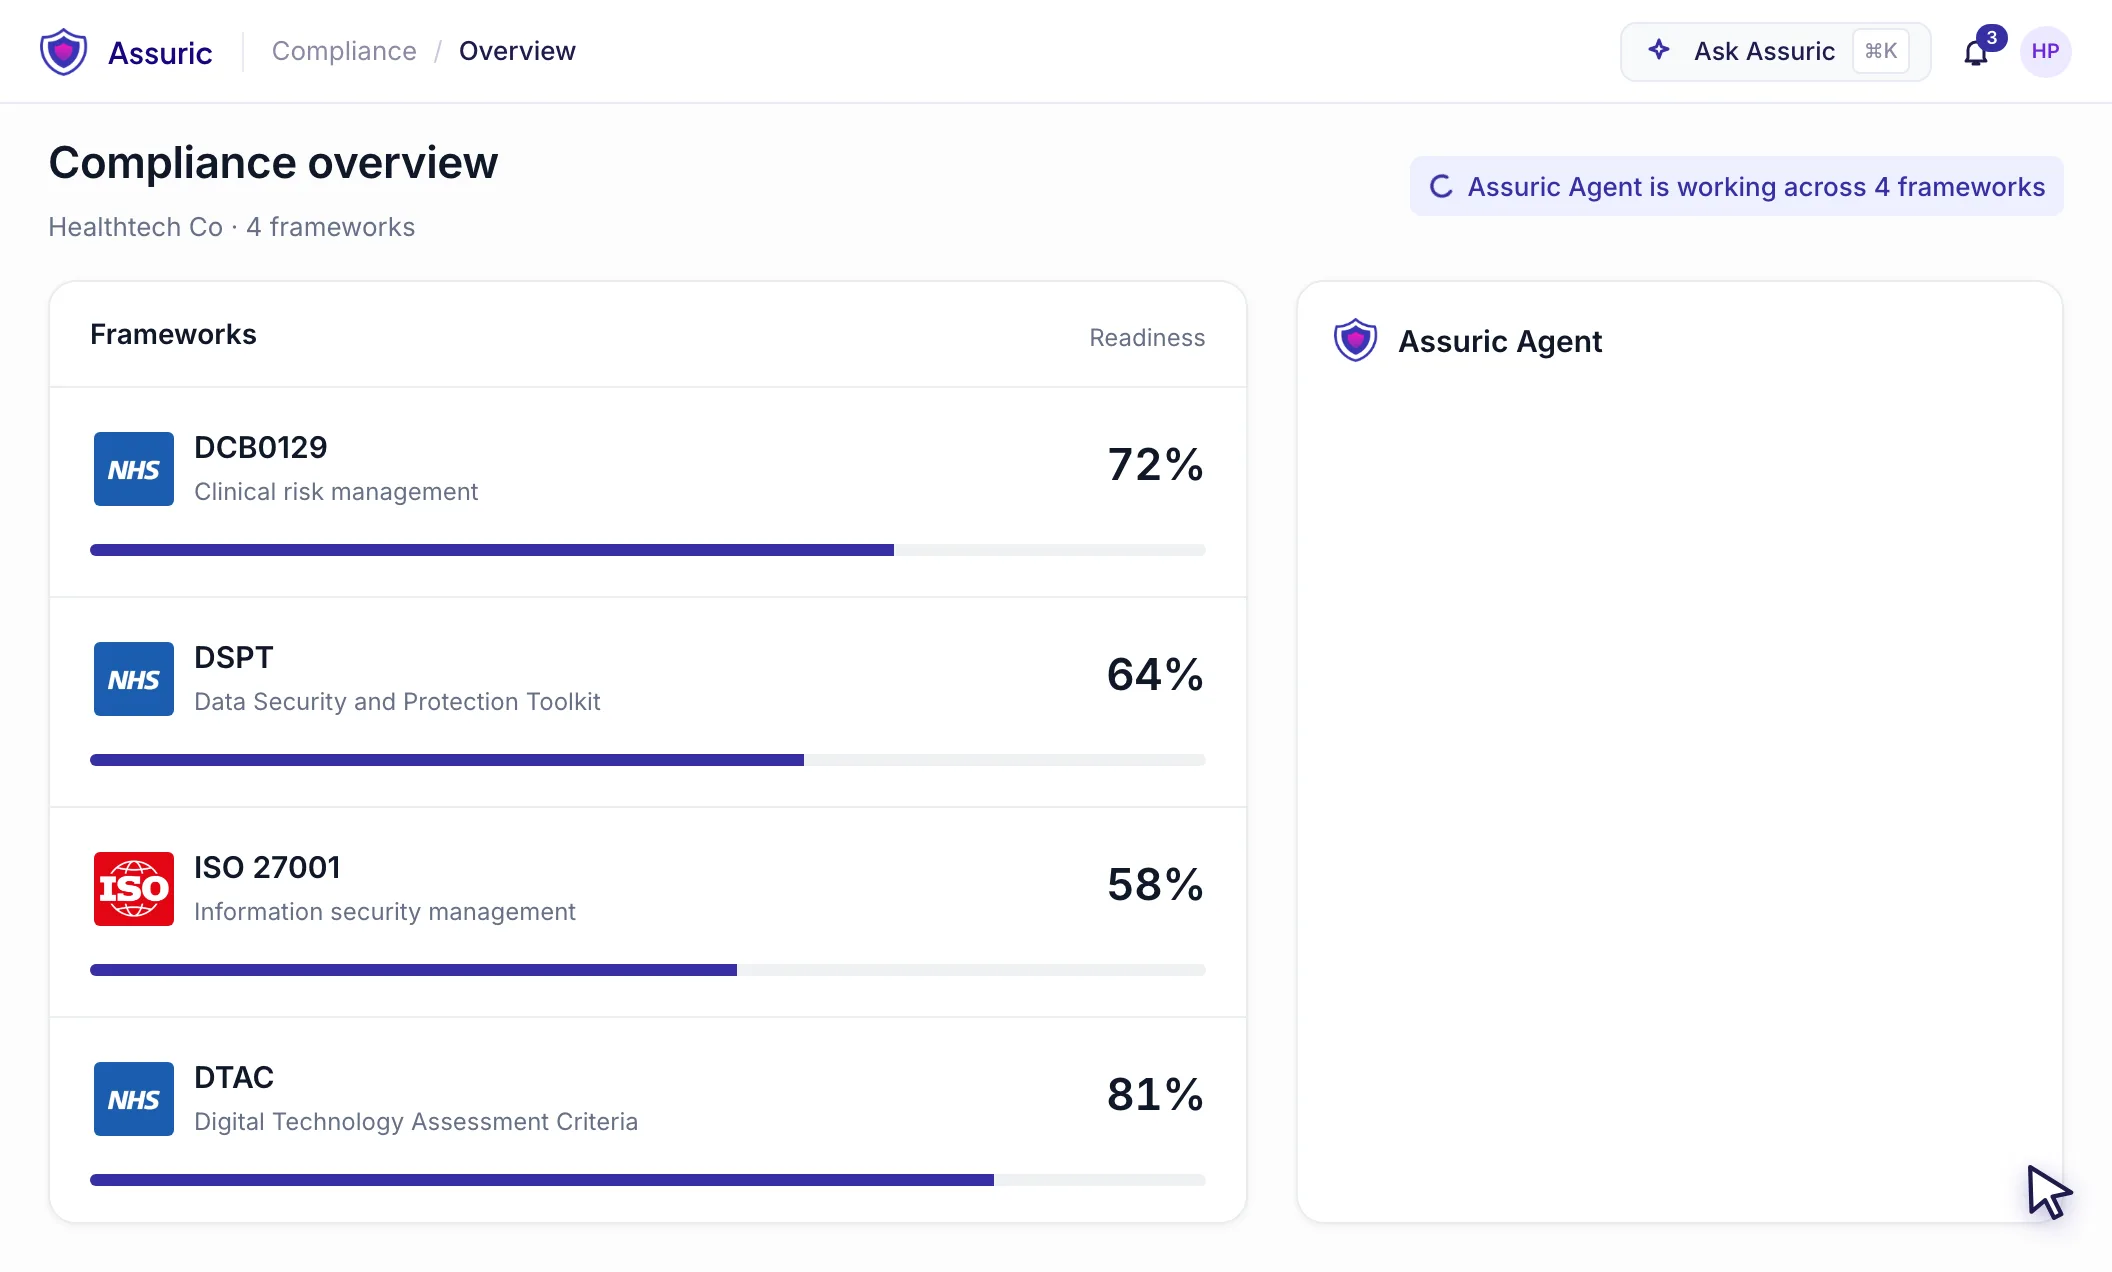
Use intelligent automation to map overlapping framework requirements, reuse evidence and simplify compliance across multiple frameworks.
Benefits
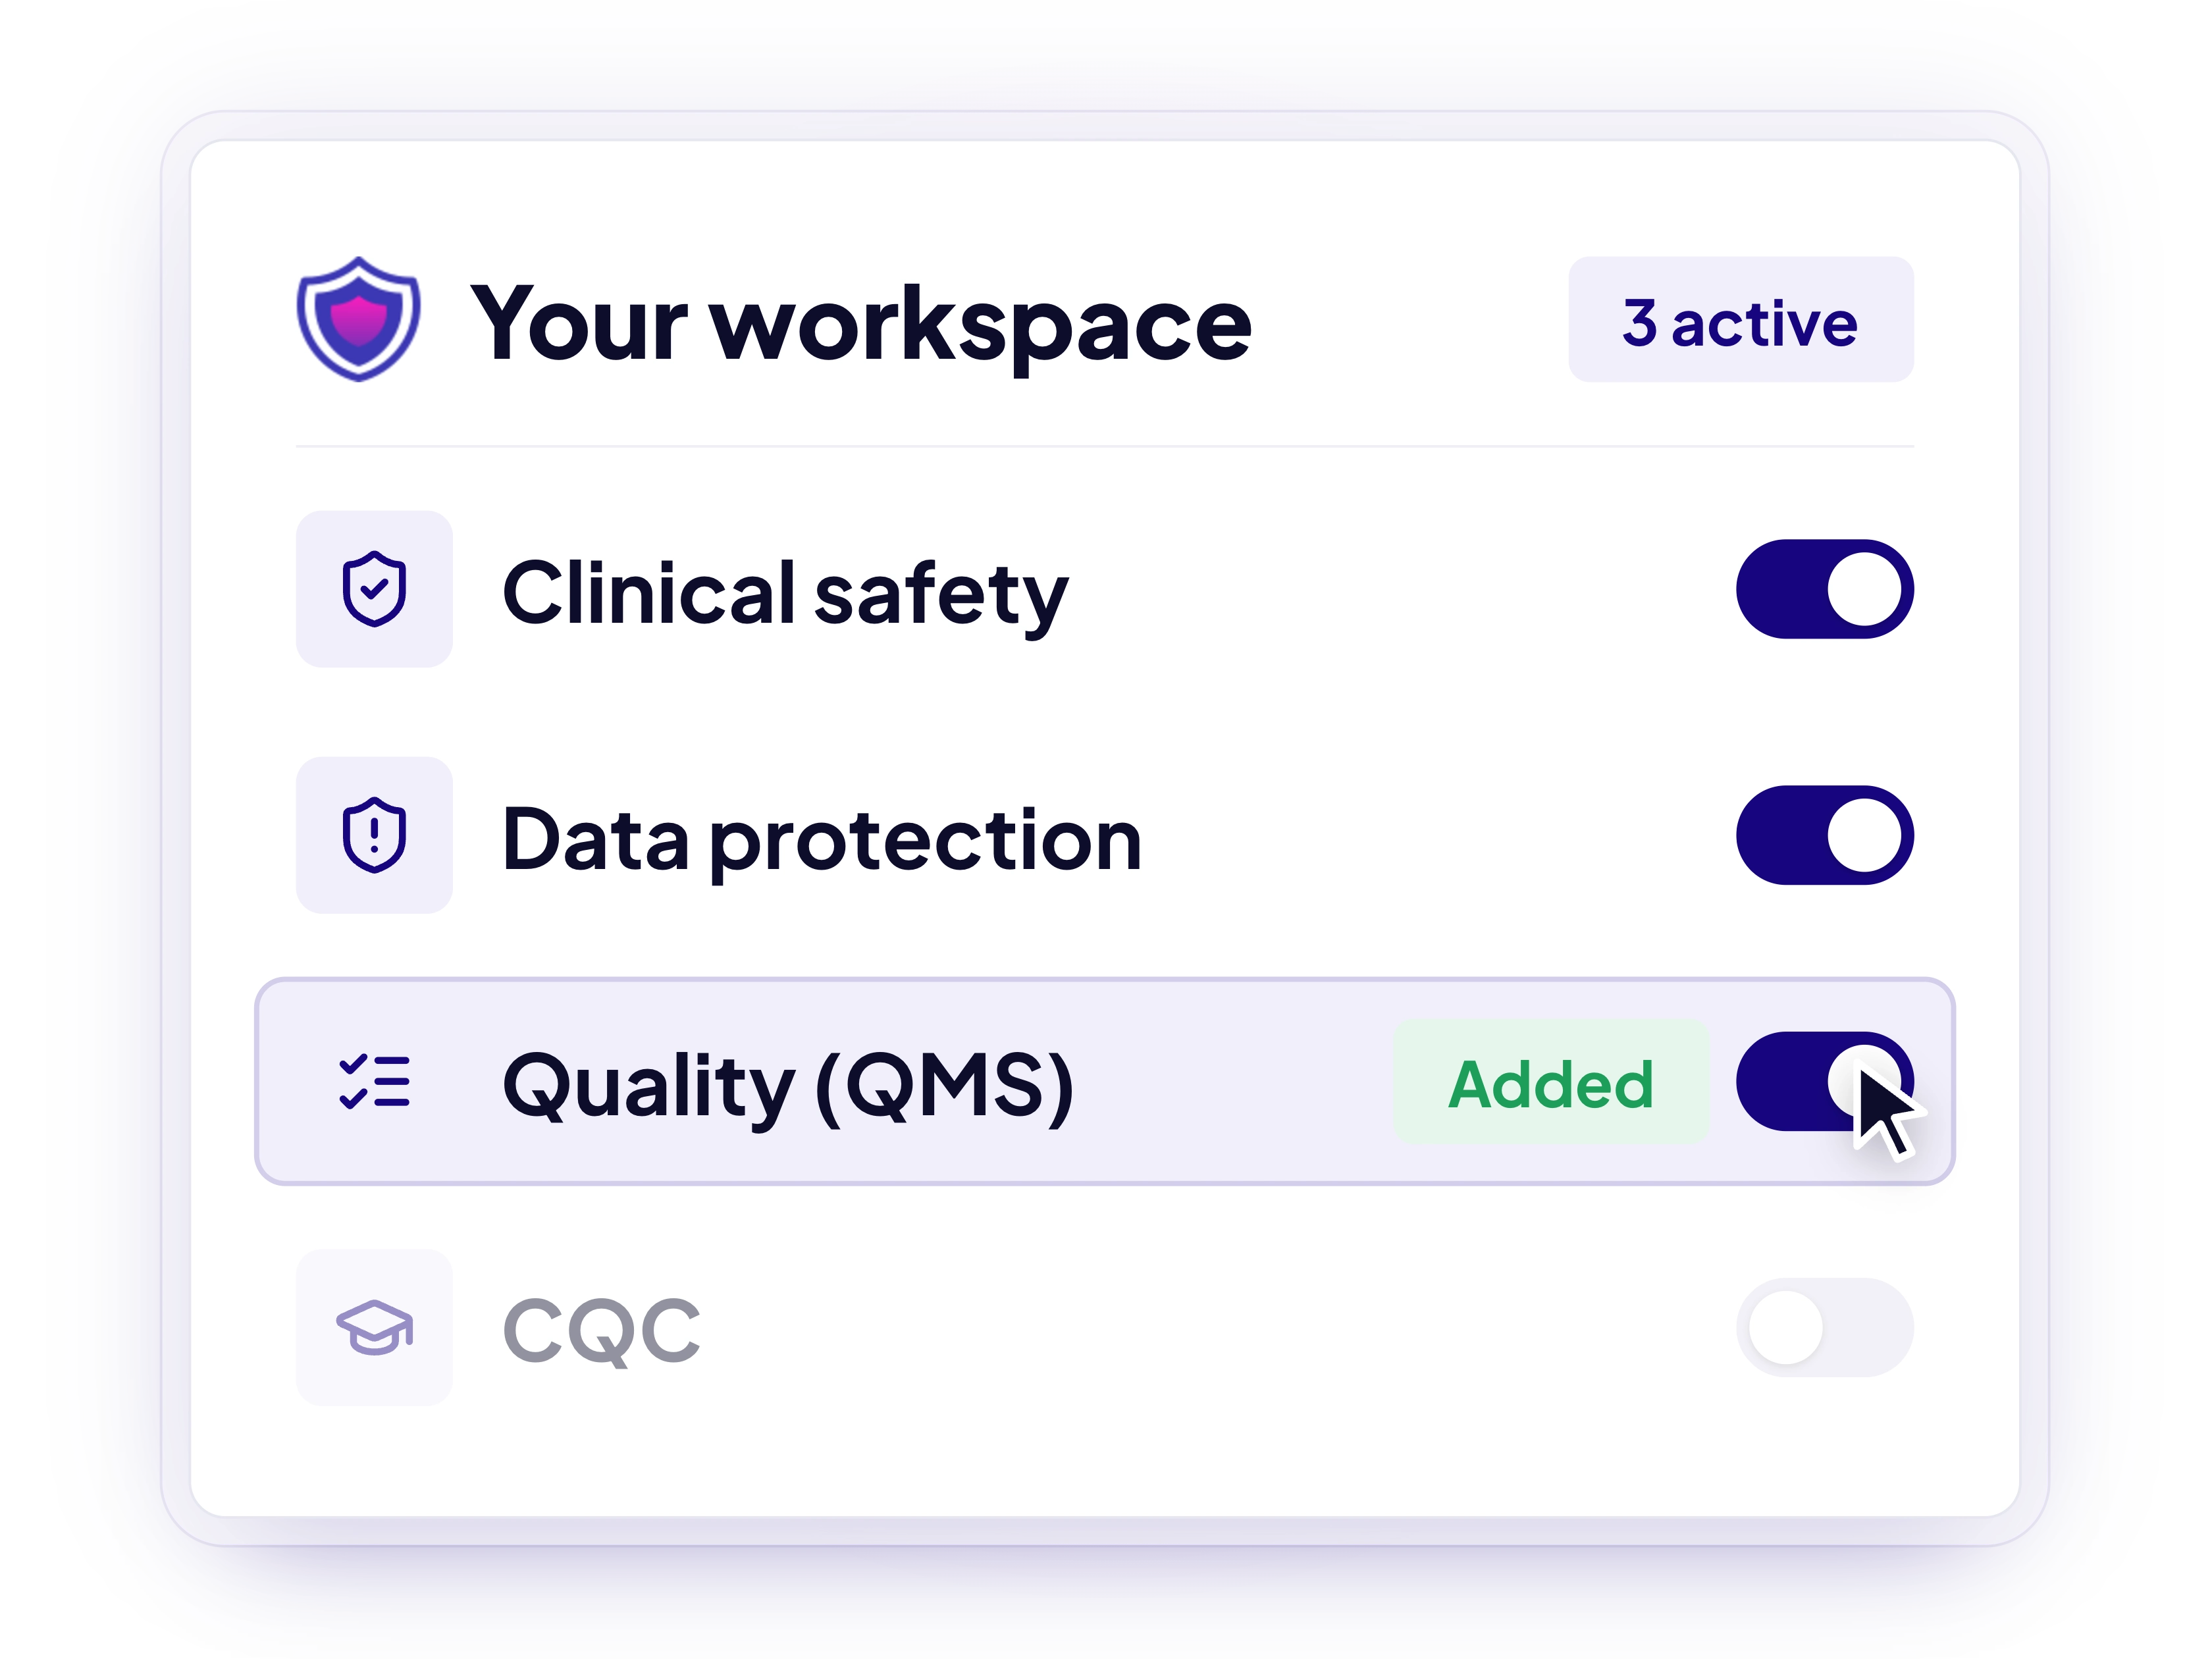
Start with the frameworks you need now and add more as you grow, from NHS and CQC to data protection, security, medical devices and international markets, reusing evidence instead of starting again.

AI, automation and live integrations take care of the repetitive work, from drafting documents to monitoring security, so your team can focus on building.
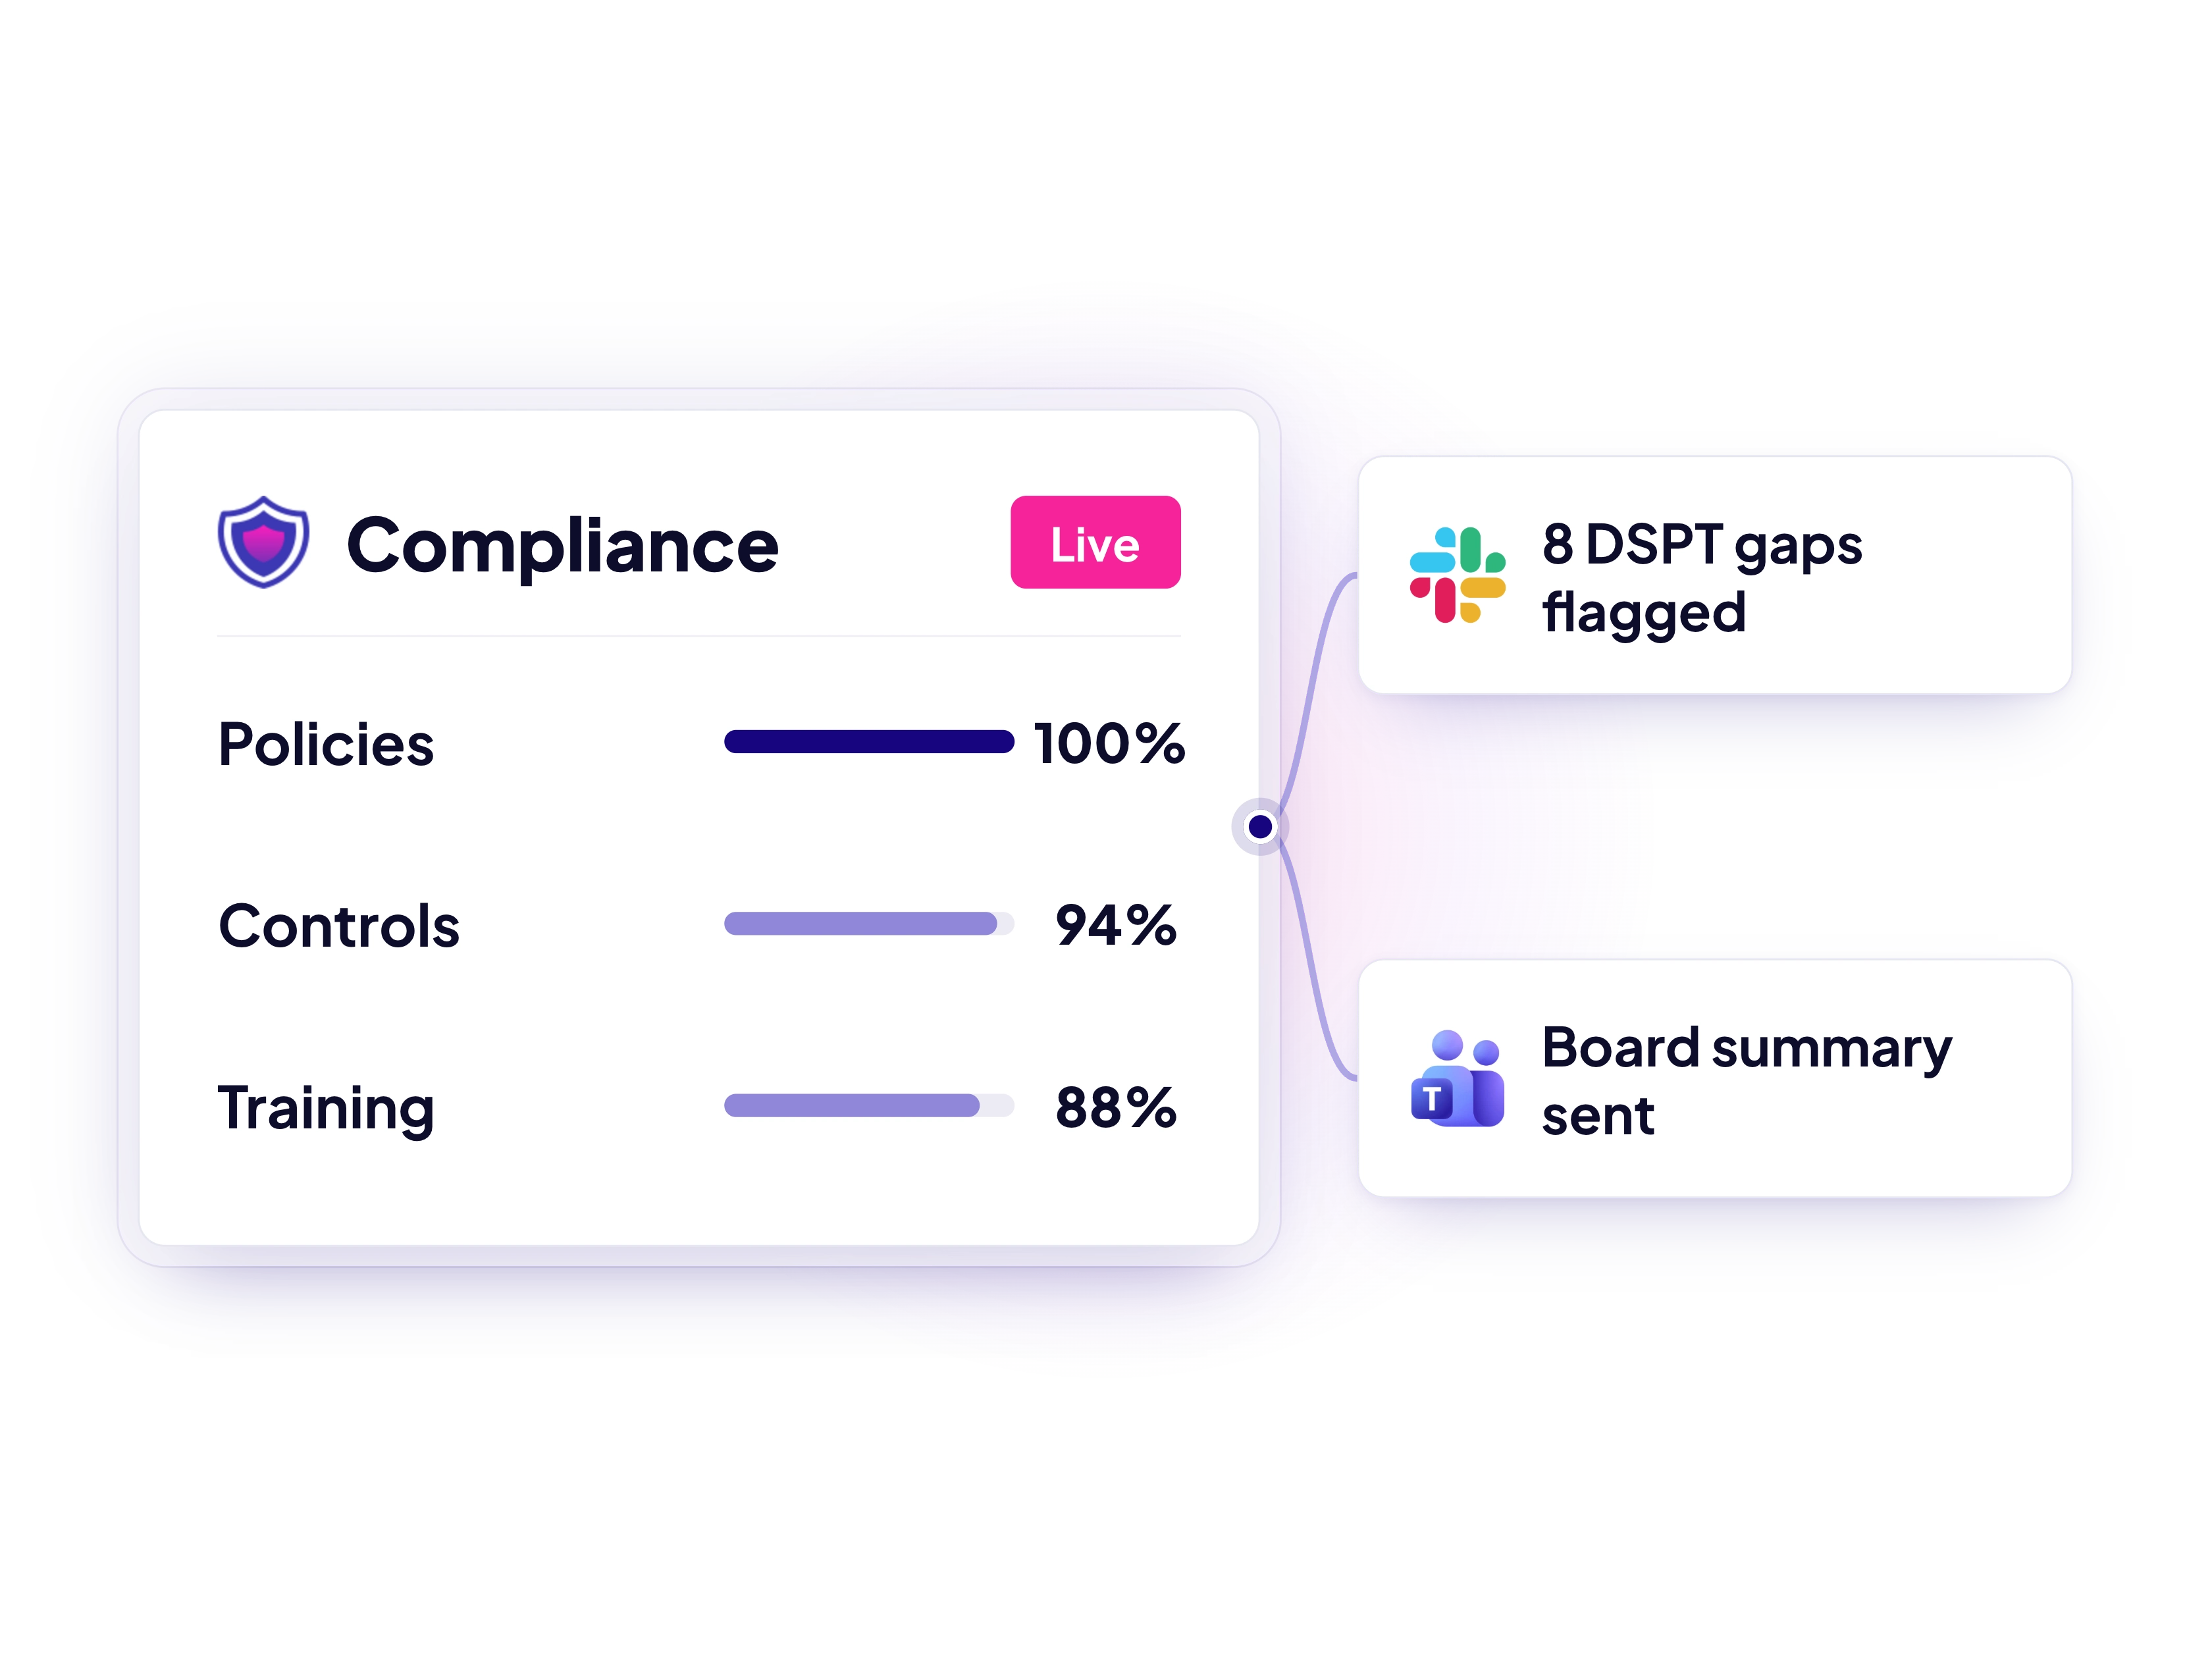
See where you stand across every framework at any moment, with reporting views and Slack alerts so you never miss a deadline or a review.
Show NHS buyers, enterprise customers and partners a mature, well-evidenced approach to compliance, with everything they ask for ready to share.
Built by NHS doctors, certified clinical safety officers, technology experts and software as a medical device regulatory specialists.

Hand over your existing documentation and we’ll map and upload all of it against your requirements.

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”
Maks Kozarzewski
COO, VitVio

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”
Paul Llewellyn
CCIO, Accenture

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”
Katie Baker
Director UK & Ireland, Tandem
It depends on who you sell to. Selling into the NHS usually means DTAC, which covers clinical safety (DCB0129), data protection (GDPR and DSPT) and cyber security (Cyber Essentials). Private healthcare is normally GDPR and Cyber Essentials. If your software influences clinical decisions you will also need MHRA registration and, above Class I, an ISO 13485 quality management system.
Alongside UK frameworks, Assuric covers international standards such as SOC 2, HIPAA, EU MDR, ISO 27001, ISO 13485 and ISO 9001, with evidence mapped across them so you can expand into new markets without starting again.
It’s all three. Assuric includes a document editor, a library of policies and SOPs, version control, approval workflows and 21 CFR Part 11 compliant e-signatures, so your ISO 13485 quality system, ISO 27001 information security management system and ISO 42001 AI management system live in the platform rather than in exported files alongside it.
Yes. Most teams start with what their first buyers ask for, often DTAC or Cyber Essentials, and add frameworks as they grow. Evidence you’ve already collected is mapped to each new framework, so you only fill the gaps.
Yes, and most customers do a mix. We bring your existing documents in during onboarding, map them to the frameworks they satisfy, and use our templates only for the genuine gaps.
It depends on which frameworks you need and how much documentation you already have. GDPR and Cyber Essentials are usually the quickest, while DTAC and medical device registration take longer. Whatever you’re working towards, Assuric gets you there at least twice as fast as doing it manually, because the platform shows you exactly what’s needed, reuses the evidence you already have and drafts much of the documentation for you.
Every software plan comes with extensive support to get you compliant, from onboarding and mapping your existing documentation to guidance on what each framework needs and help from our team whenever you need it. Dedicated consultancy and named roles, such as a Fractional CSO or Fractional DPO, are available as additional services.
No. Several customers keep a general GRC tool for their US and information security work and use Assuric for the NHS, clinical safety and quality side. During onboarding we import or link what you have already evidenced and map it across the UK frameworks, so nothing is duplicated.
A consultancy is limited by how many people it has. Assuric is technology first with the consulting built in, so the platform tells you what is needed and our clinical, regulatory and data protection specialists work through it with you inside the same system.
See how Assuric can help you manage every framework, document and record, all in one place.


