Add suppliers in seconds
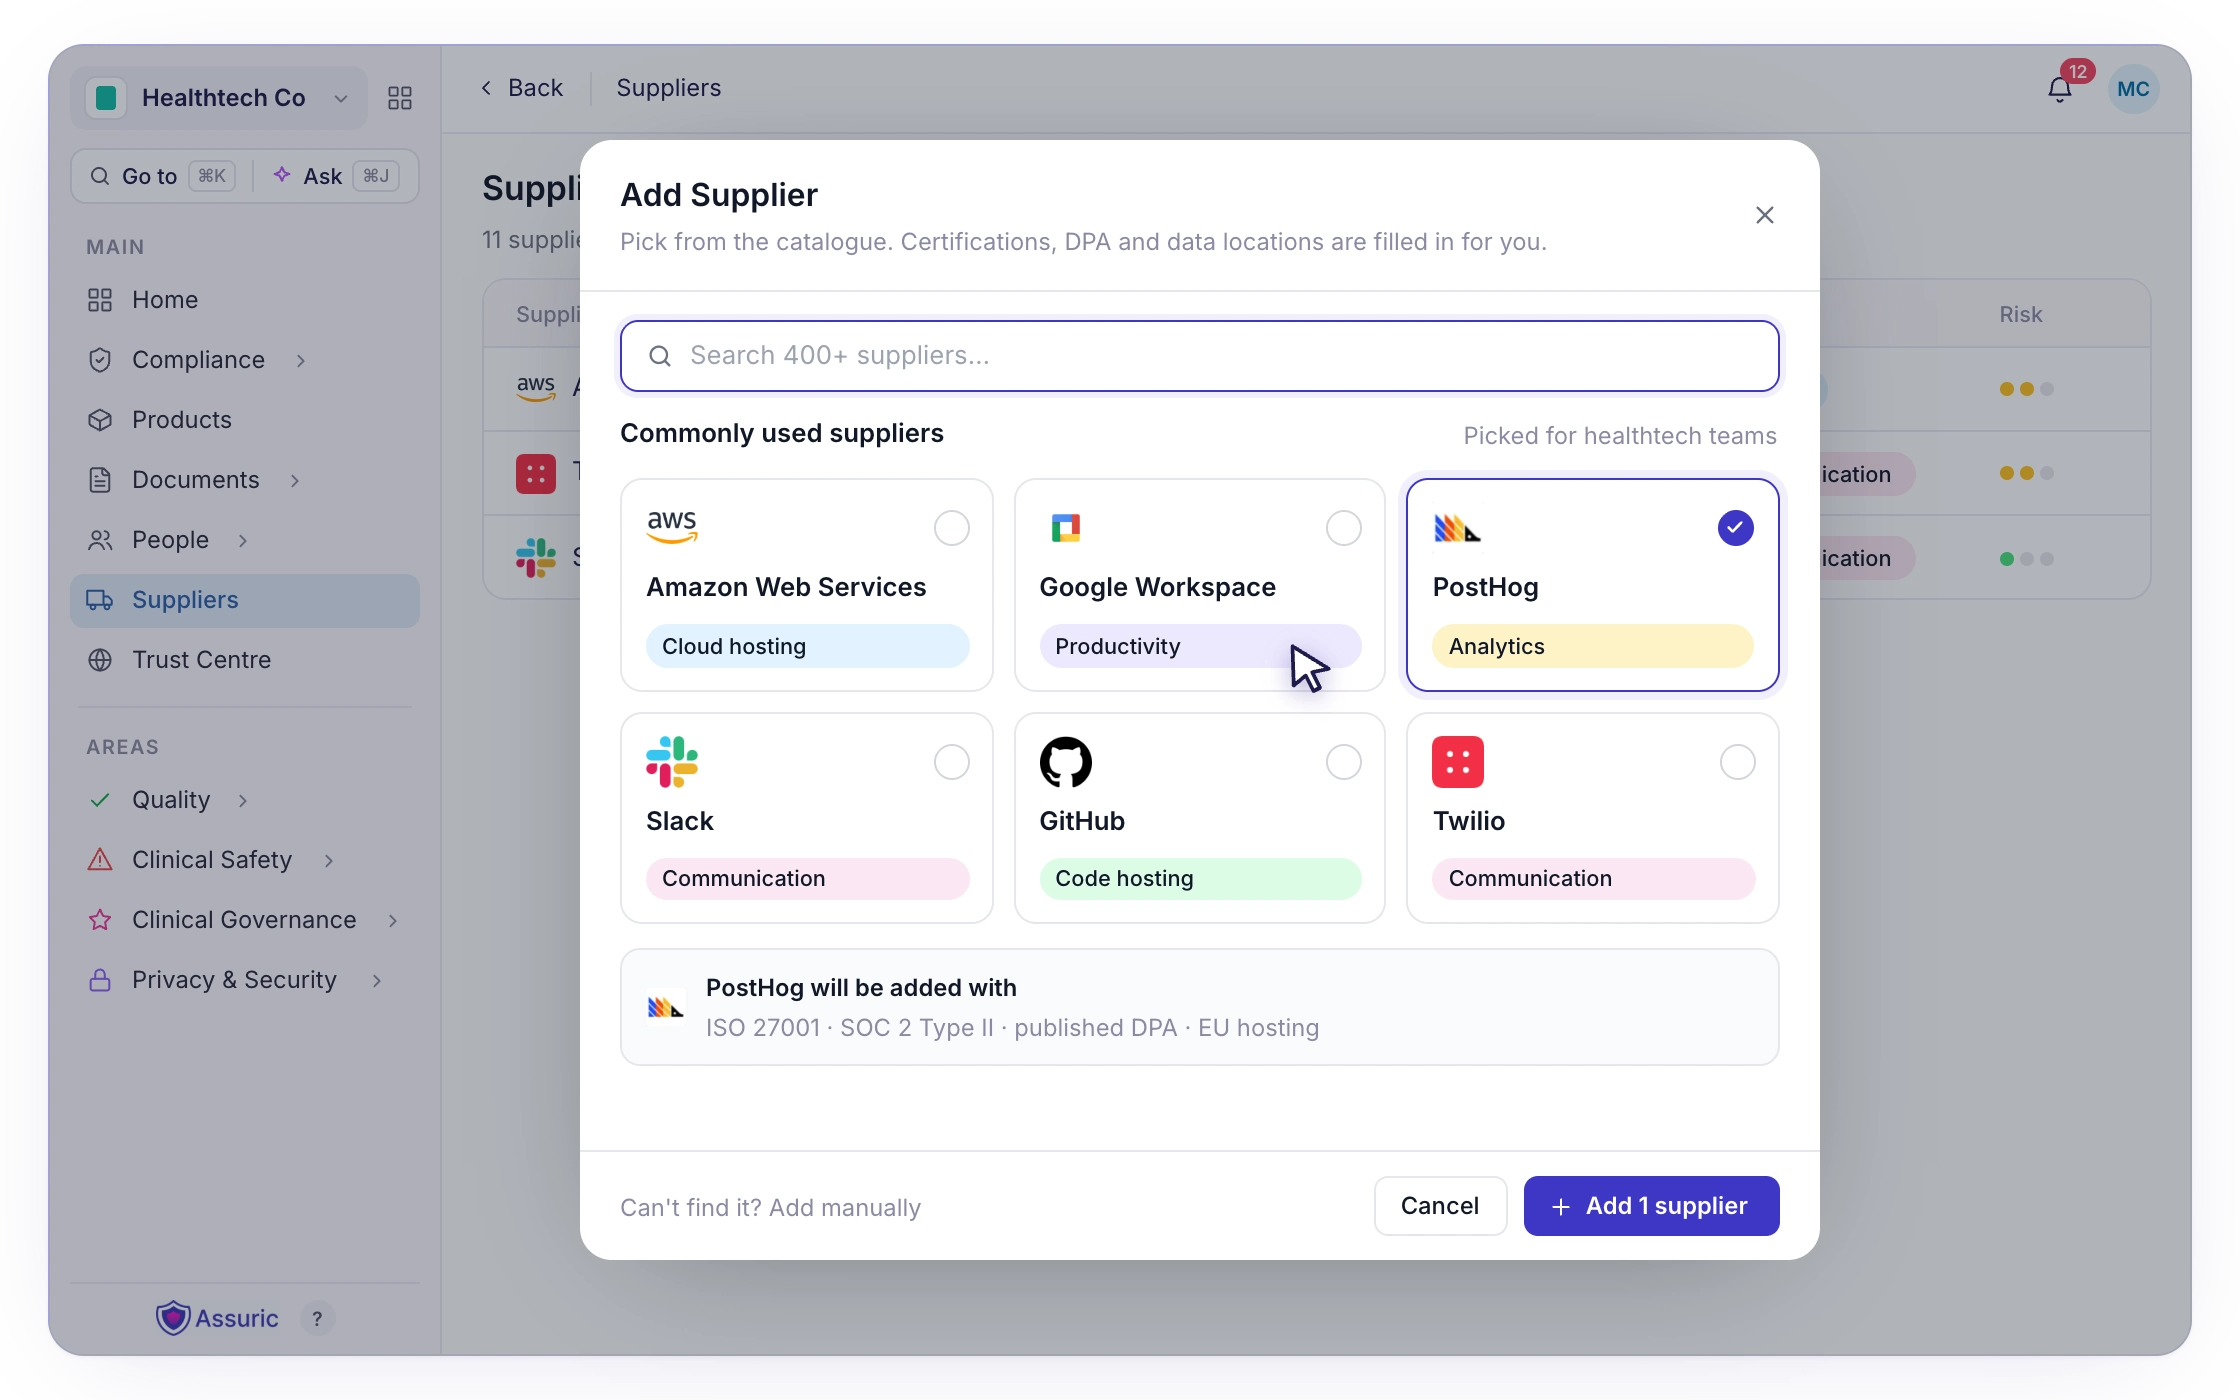
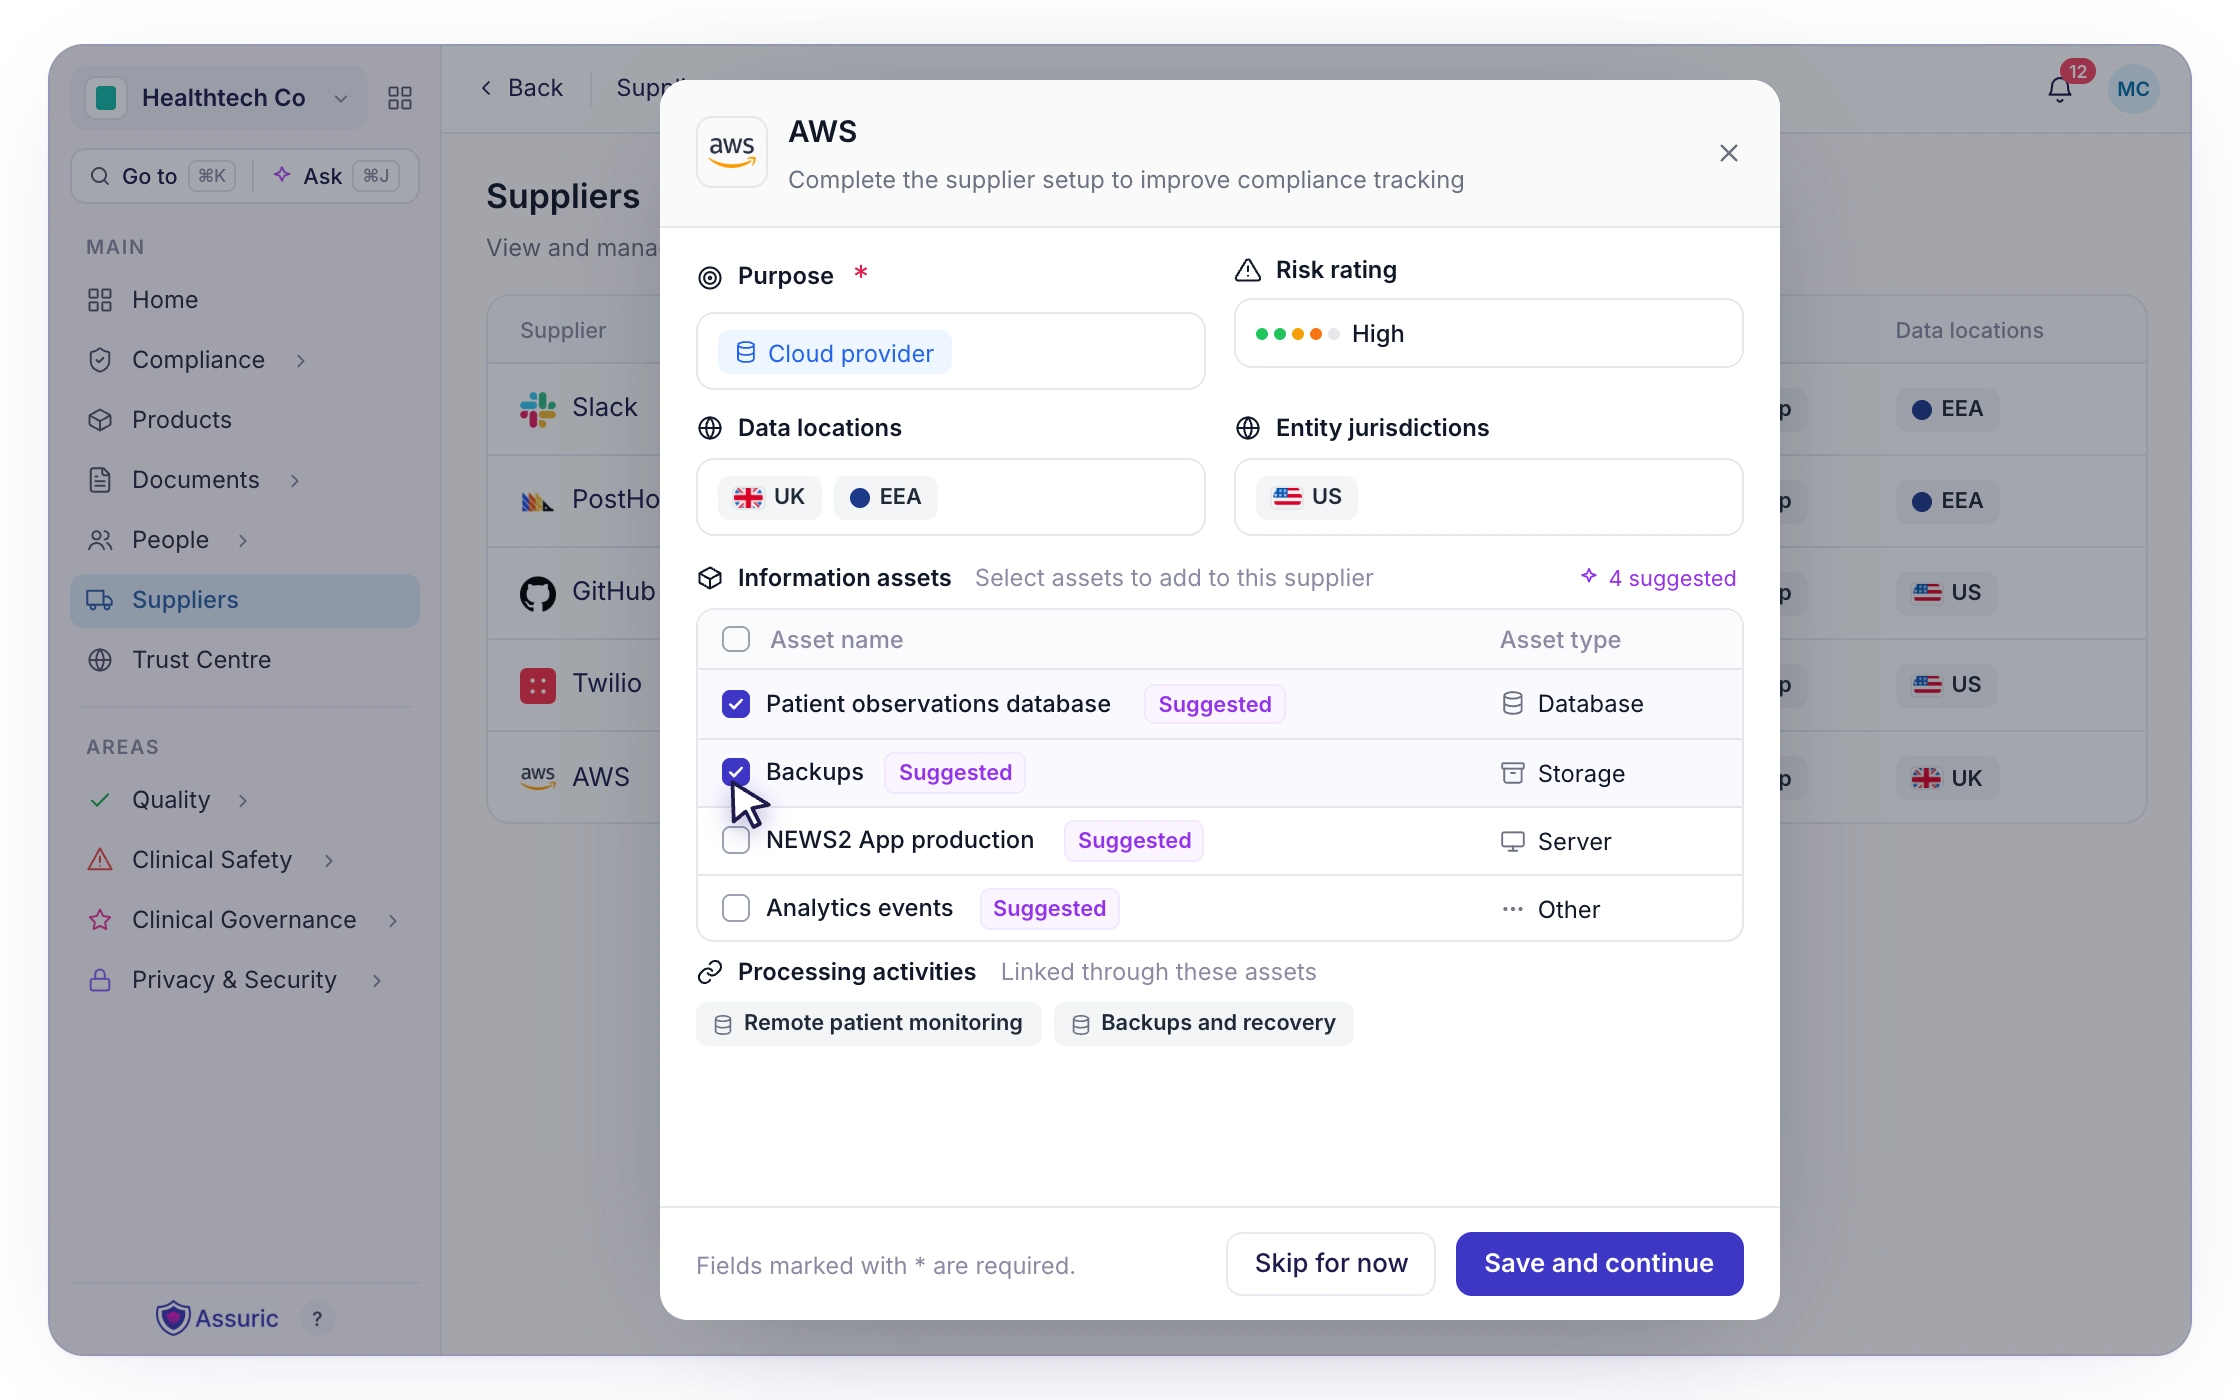
Add suppliers from a library of commonly used services, enriched with current security information, evidence and data residency details, instead of researching each one yourself.
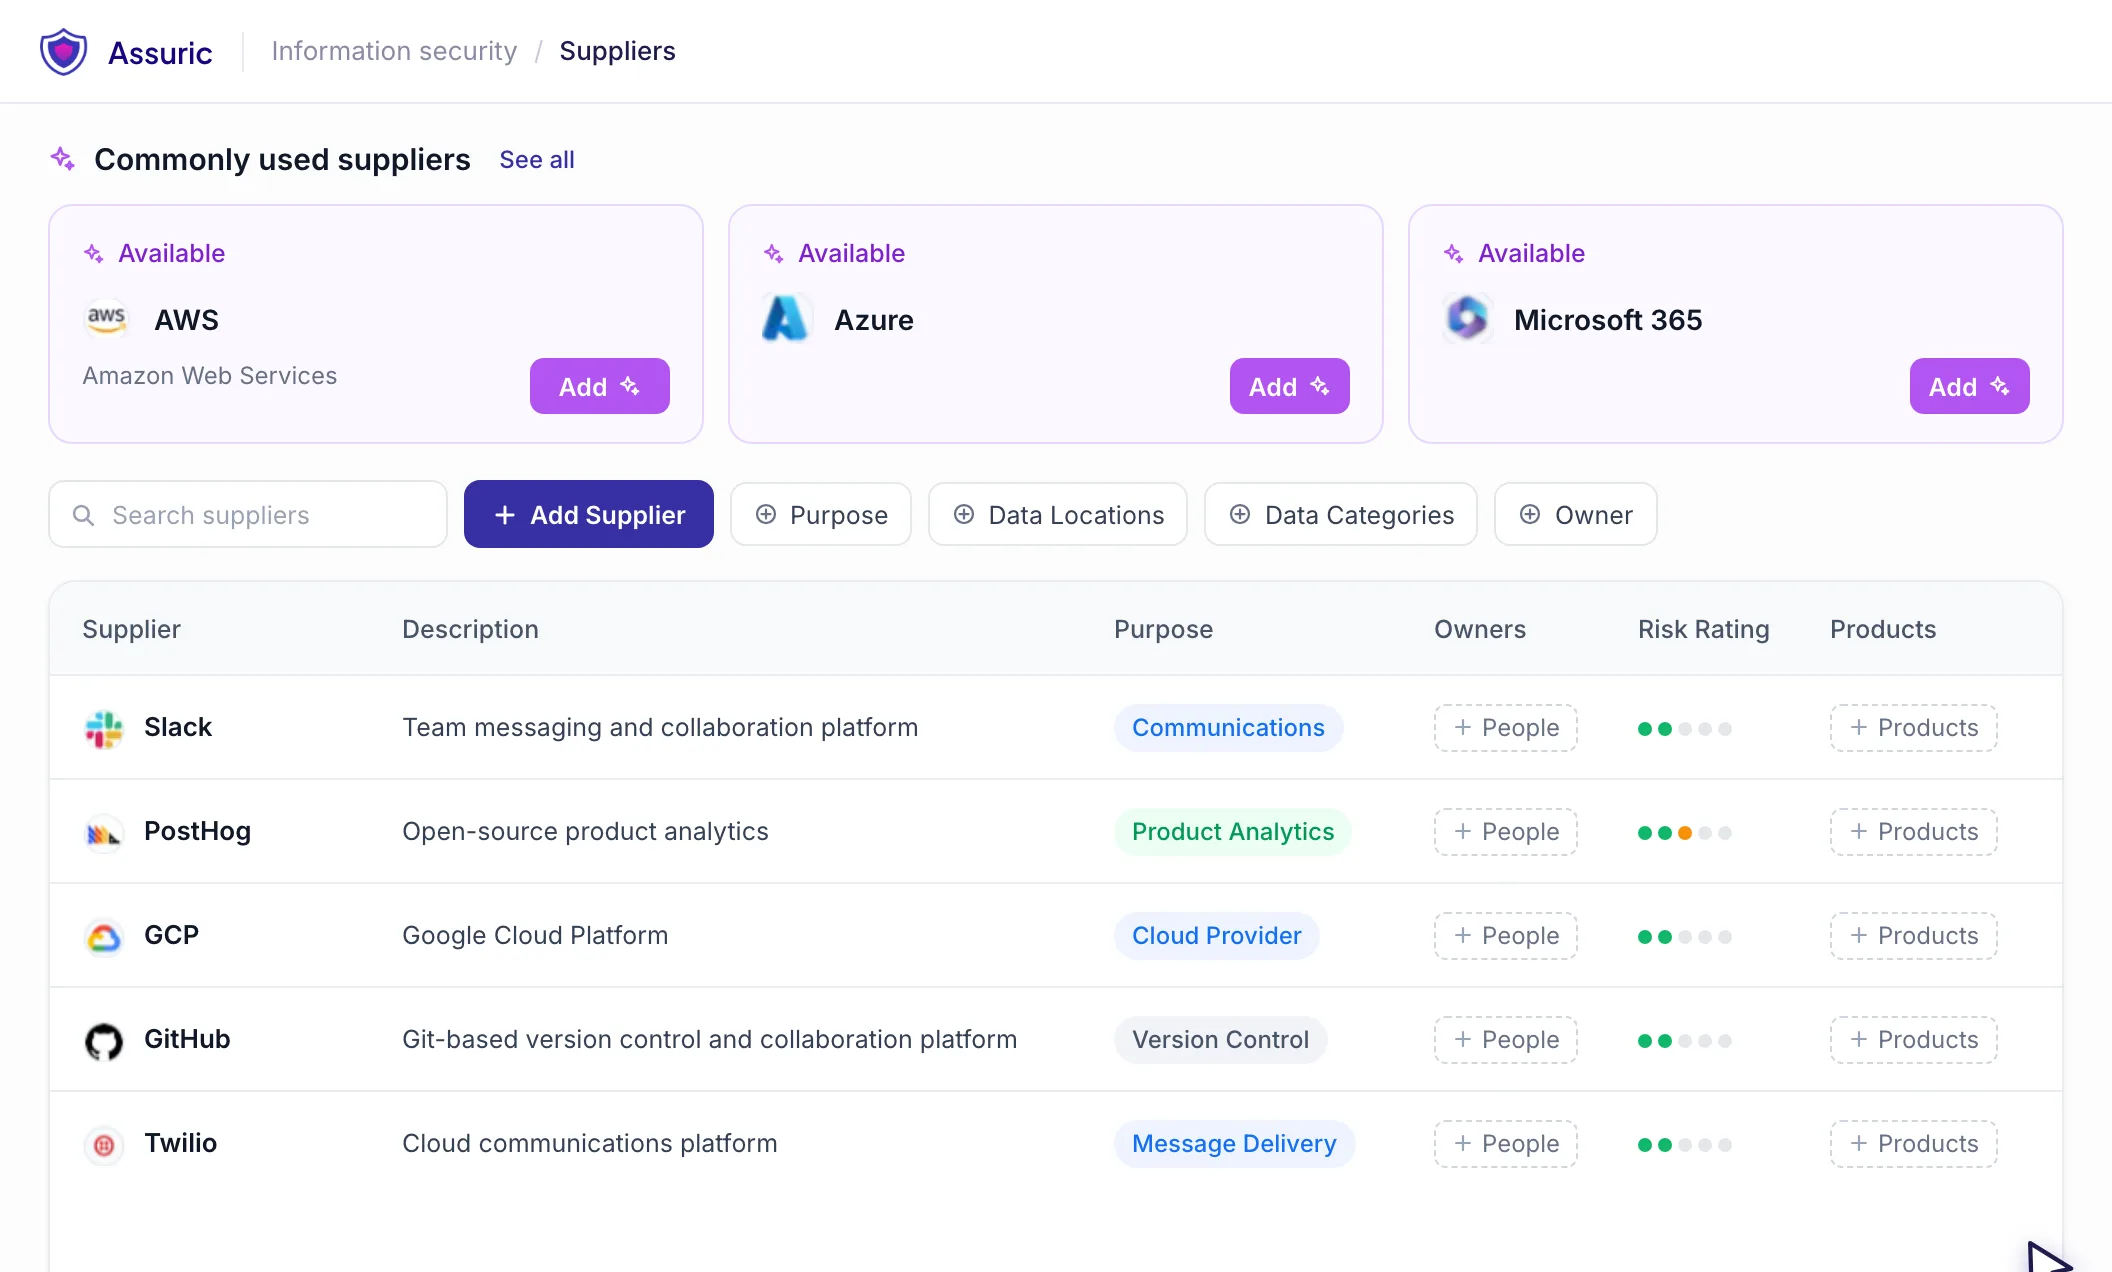
Track every supplier and data processor in one register, with risk assessments, agreements and review dates, linked to your assets, risks and processing activities.
Trusted bysecurity teams


Features
Add suppliers from a library of commonly used services, enriched with current security information, evidence and data residency details, instead of researching each one yourself.
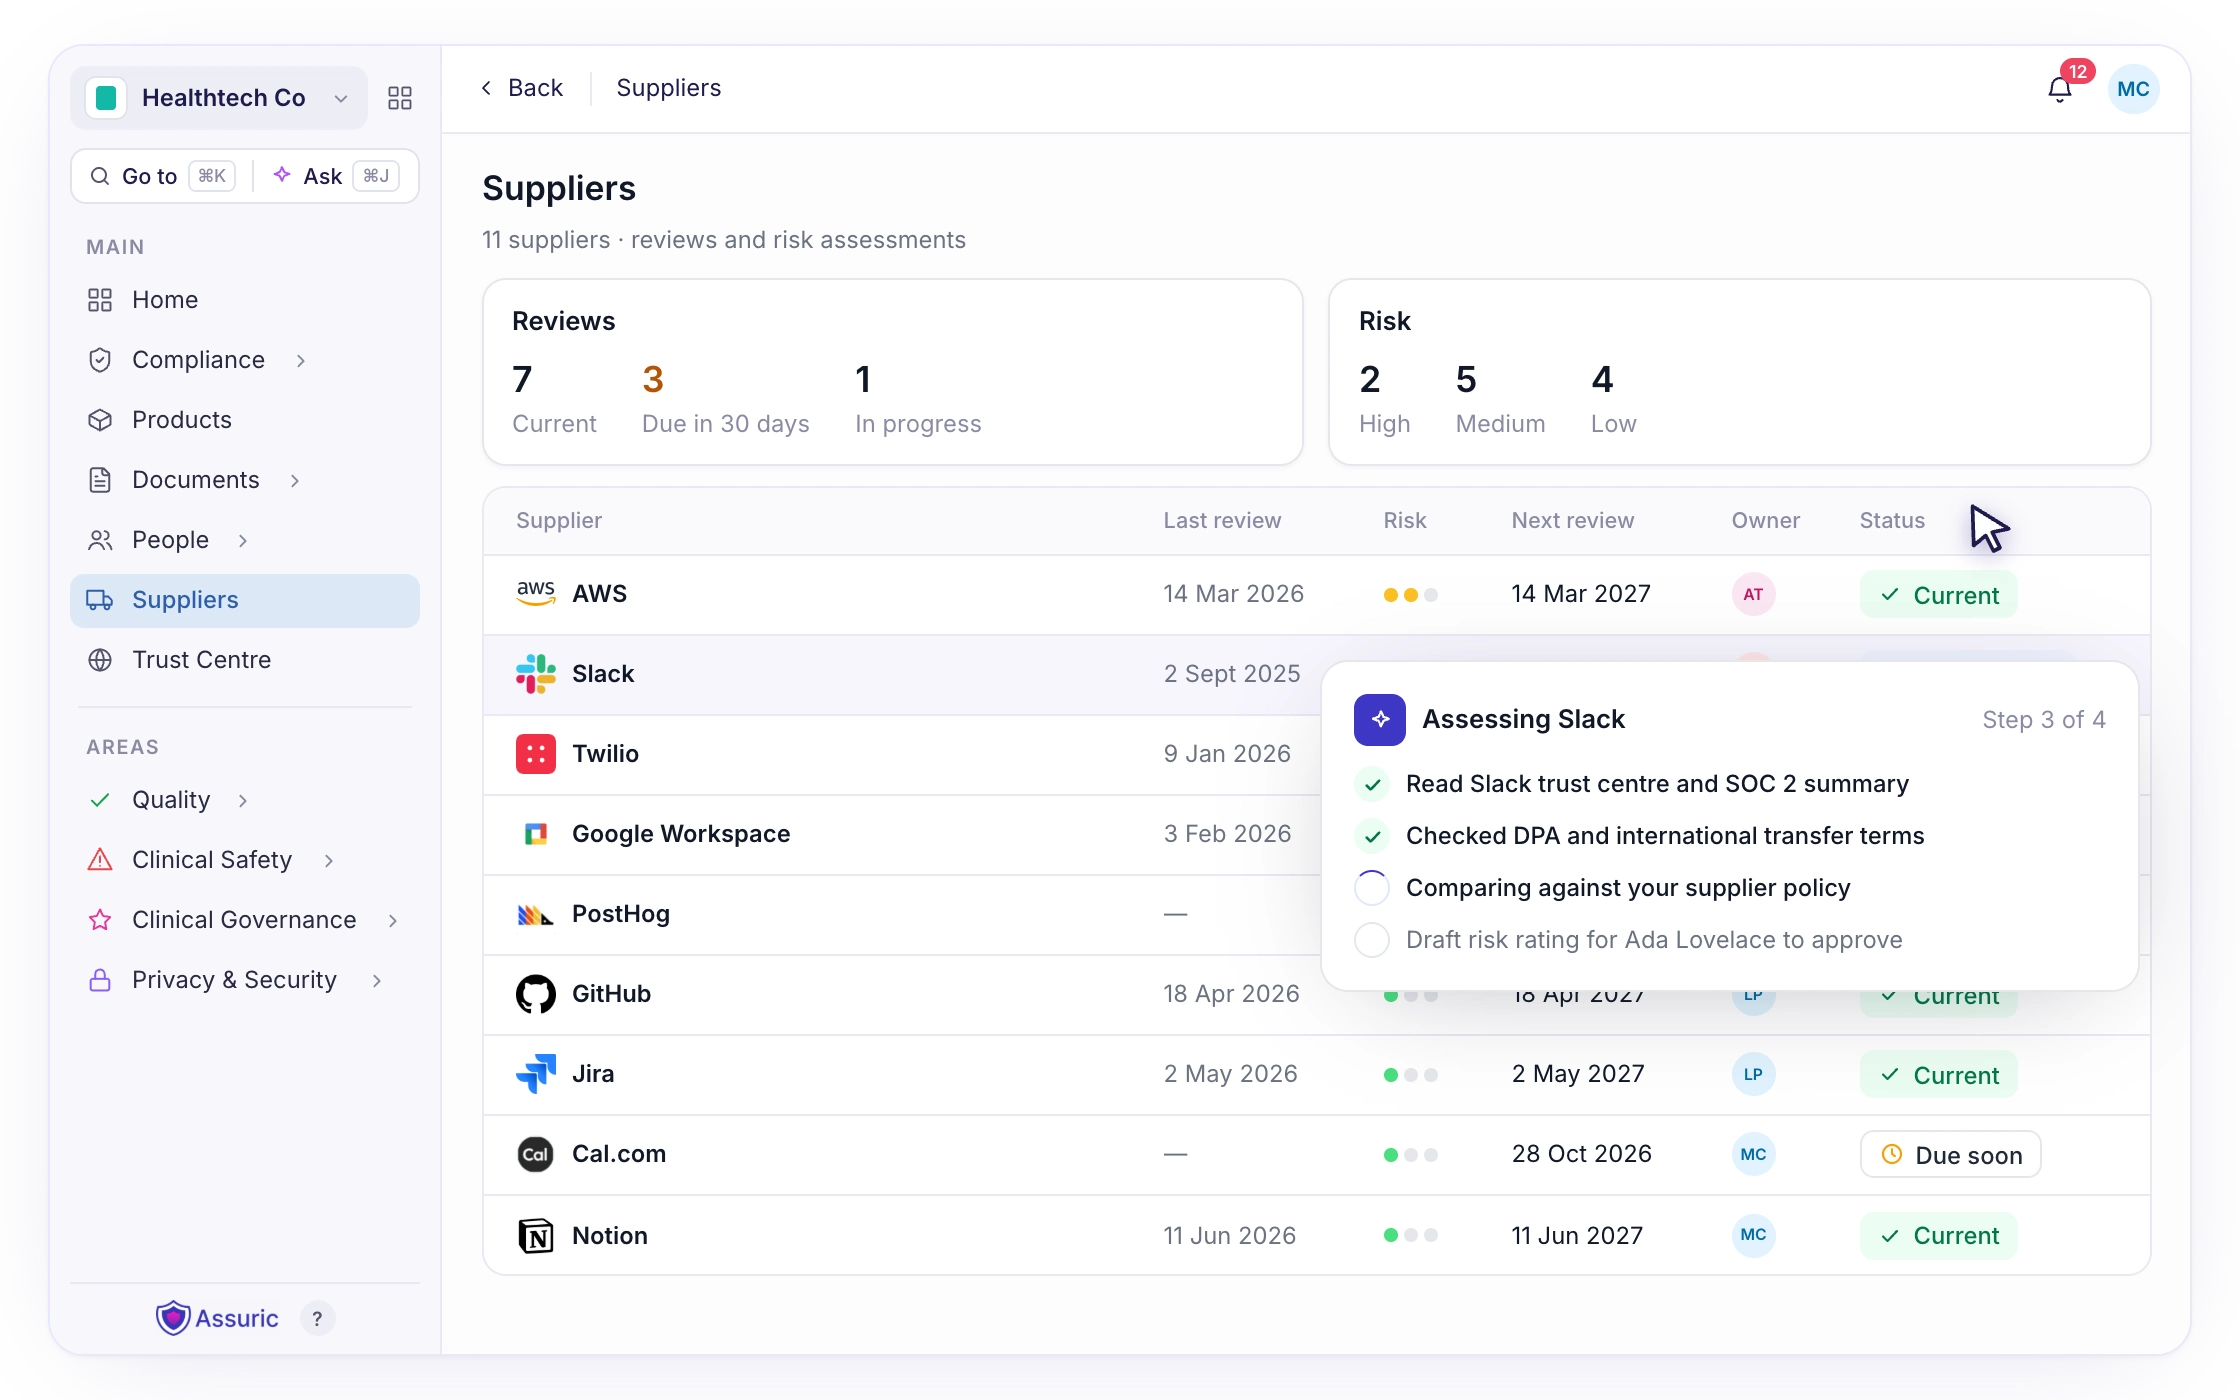
Run supplier reviews and risk assessments with AI assistance, linked to each supplier’s agreements, so every supplier is assessed to the same standard.
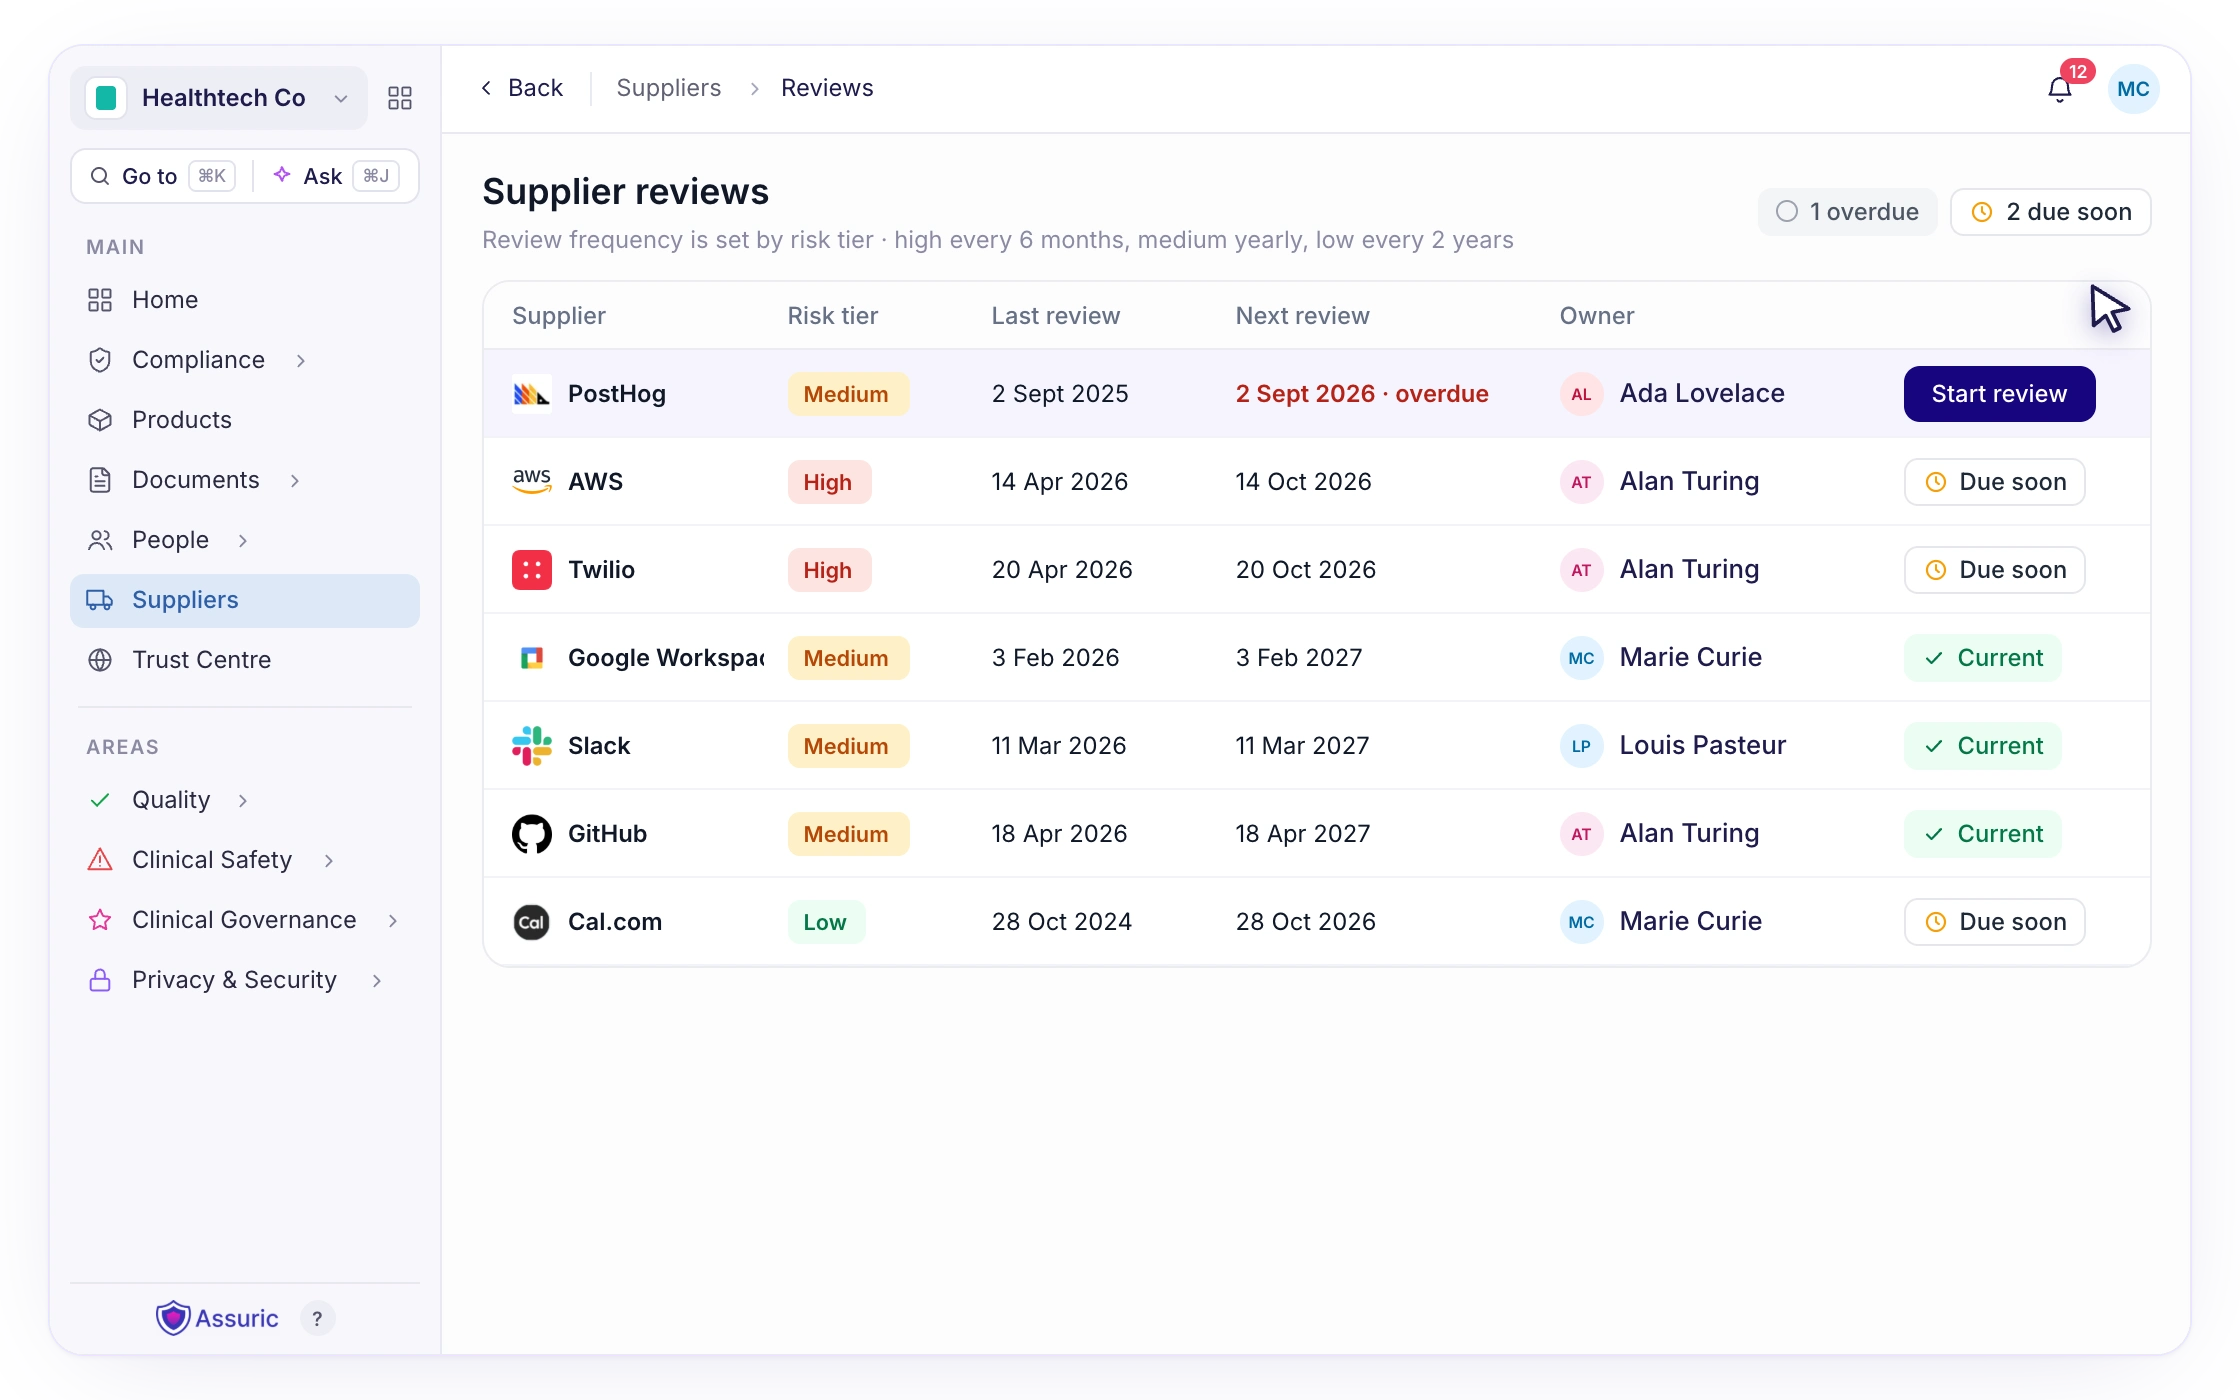
Set review dates and get reminders when reassessments are due, and keep each supplier’s security information current, so you know about changes before they become a problem.
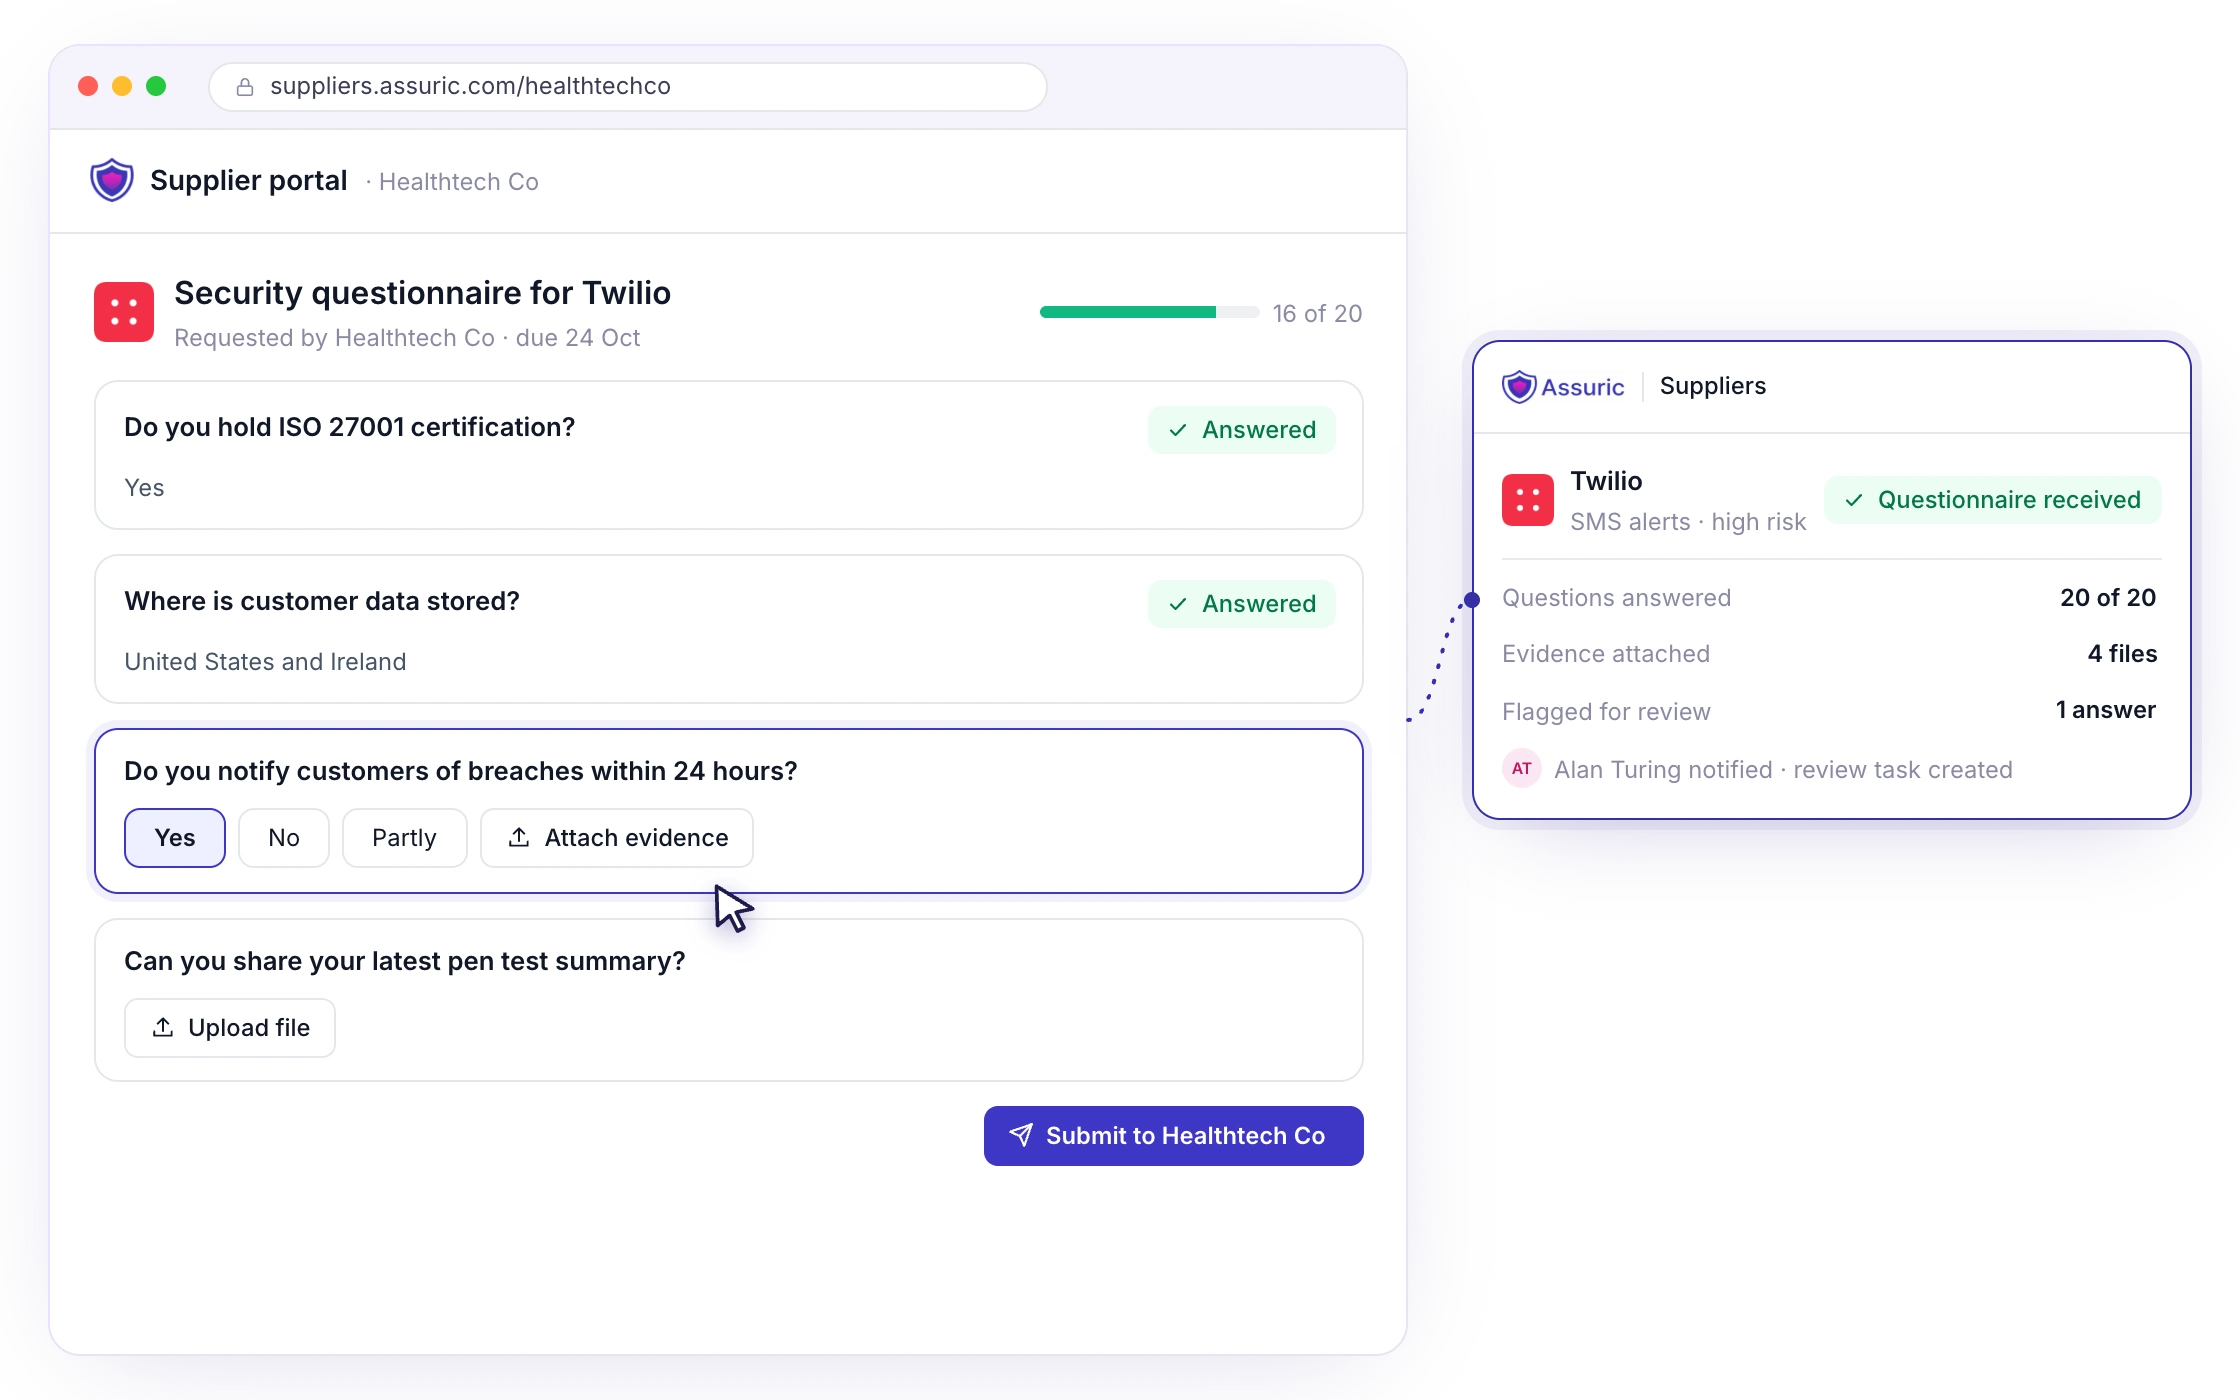
Send due diligence questionnaires to suppliers through the supplier portal, track their responses and keep the answers alongside each supplier’s record.
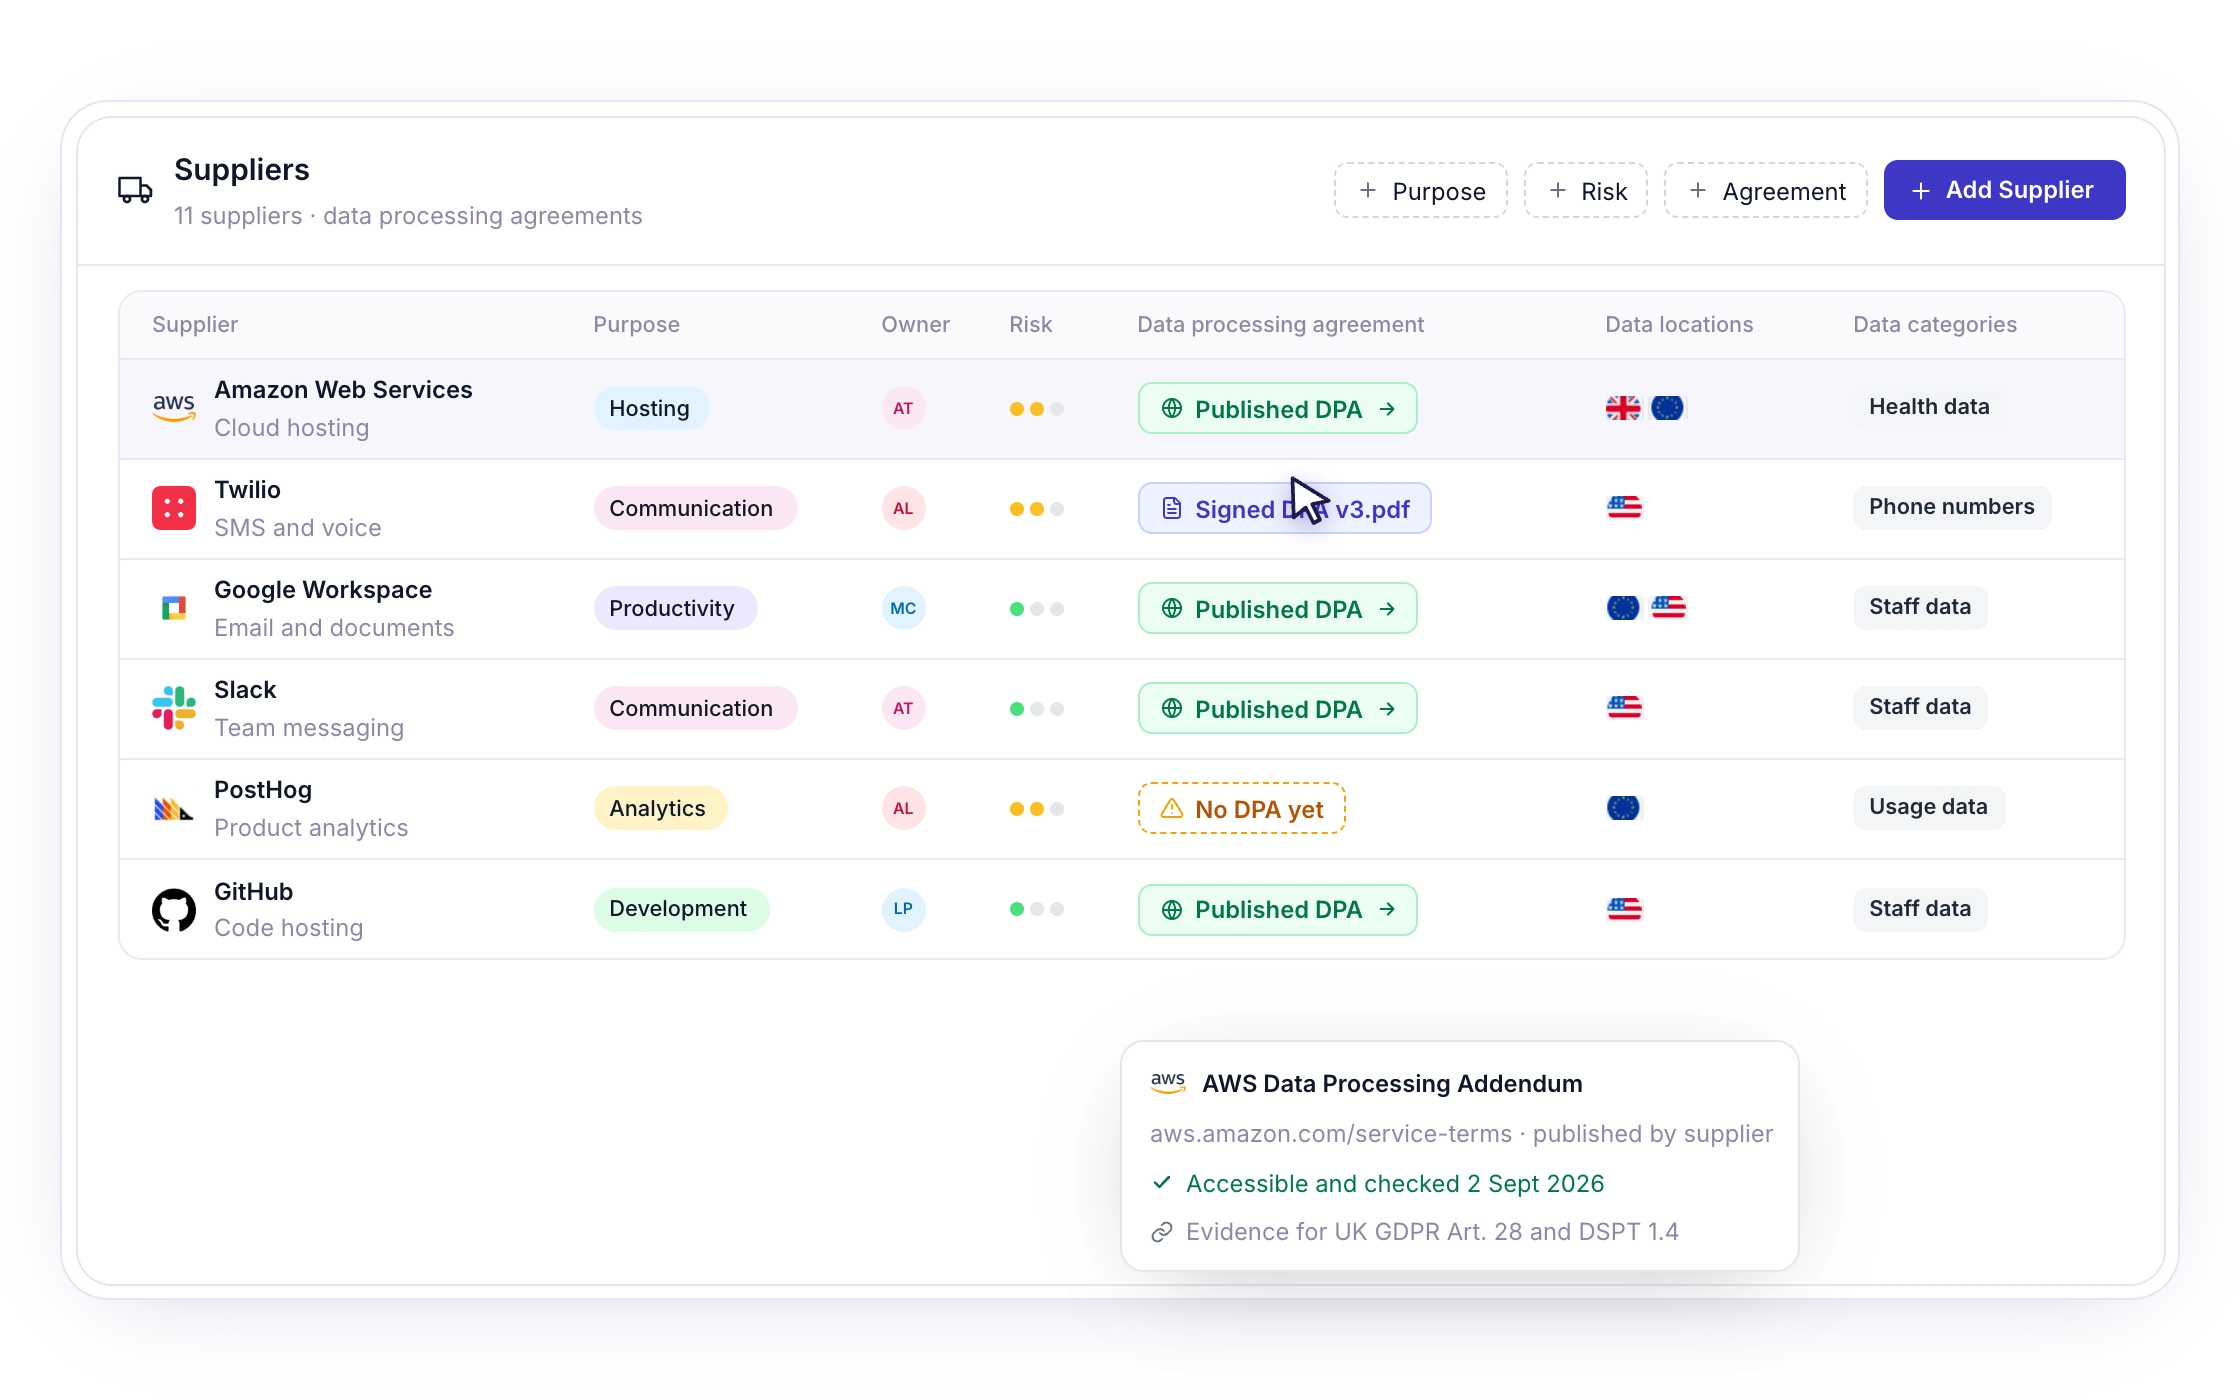
Link a supplier’s published DPA instead of negotiating your own, and record signed agreements alongside it, so any supplier without cover is obvious.
Share the same information across your supplier register, asset register, risks and record of processing activities, so updating one keeps the others current.
Benefits

Pre-filled supplier information and AI-assisted reviews take the legwork out of due diligence, so assessing a new supplier takes minutes, not days.

Every supplier’s assessment, agreement and review history is recorded, so you can show auditors and NHS buyers exactly how each supplier was evaluated.
See every supplier, its risk rating and anything overdue in one view, so a supplier issue never takes you by surprise.
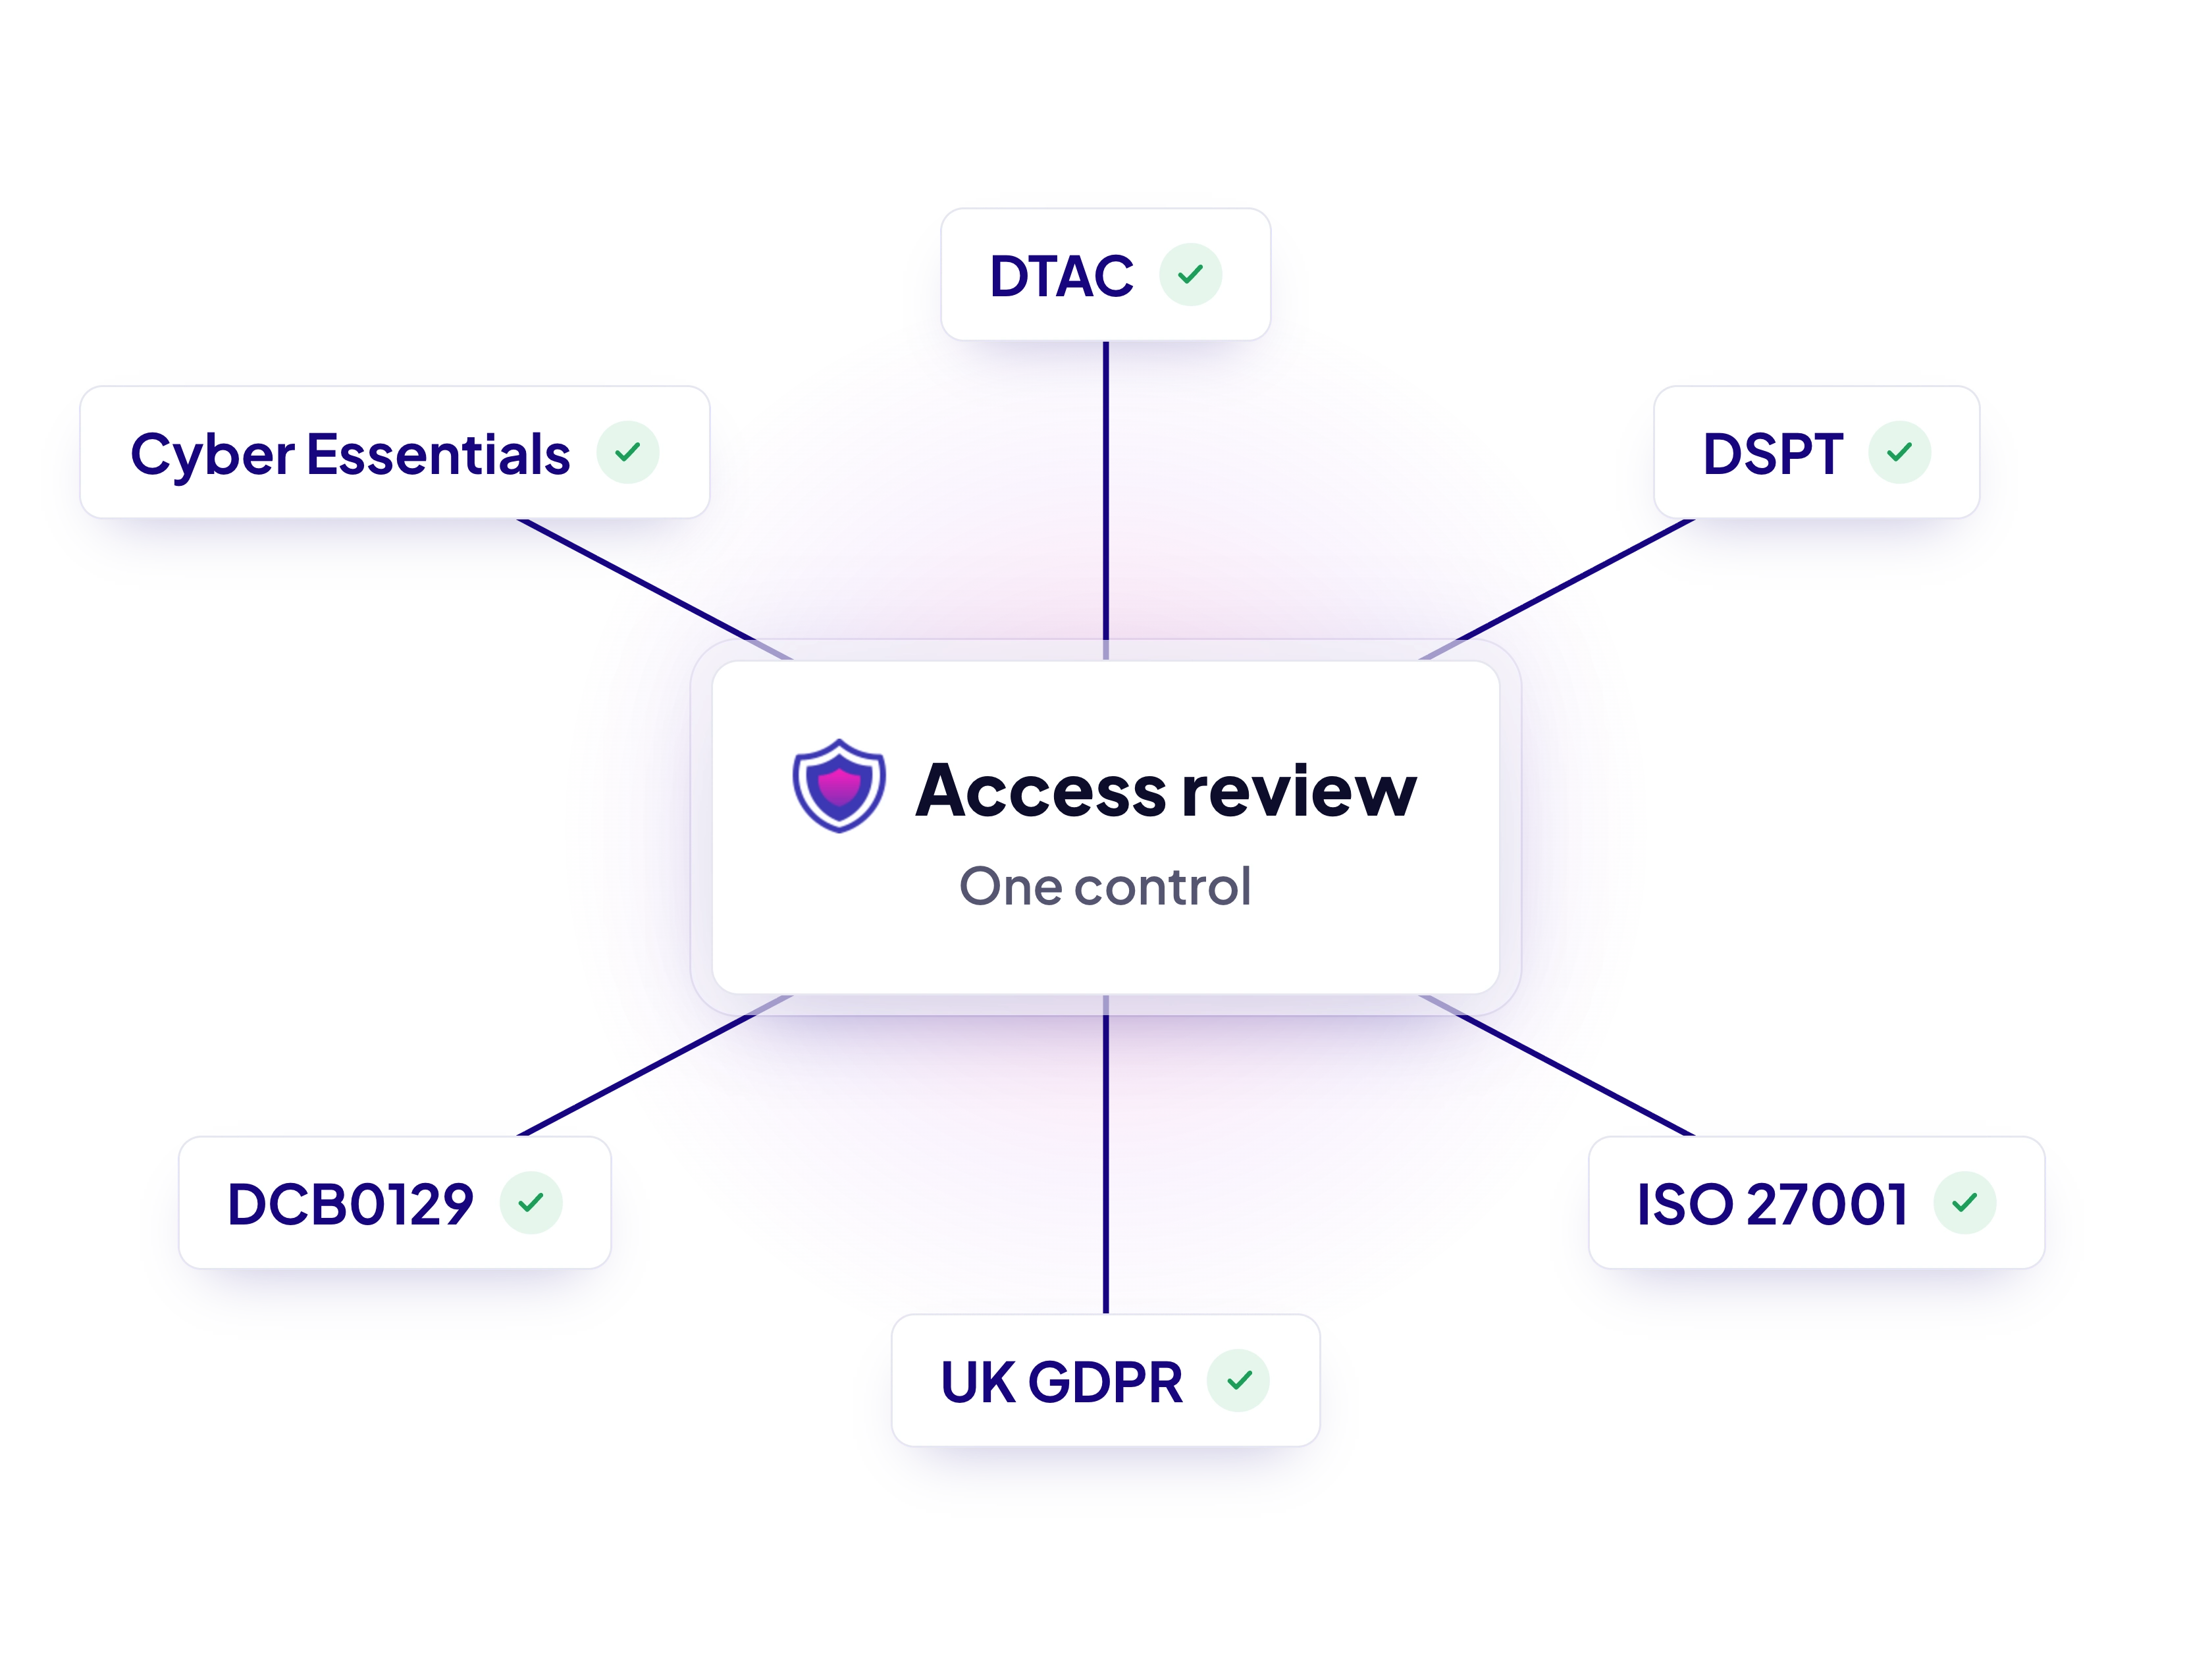
Evaluate suppliers for ISO 13485 and ISO 9001 as well as ISO 27001, SOC 2 and the DSPT, all from one supplier register.
Share your subprocessor list through your Trust Centre, so buyers can see exactly who handles their data.

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”
Maks Kozarzewski
COO, VitVio

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”
Paul Llewellyn
CCIO, Accenture

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”
Katie Baker
Director UK & Ireland, Tandem
Anyone processing personal data or providing something your product or service depends on: your hosting provider, analytics, support desk, email and payroll providers, contract manufacturers, and any subcontractor with access to your systems.
You remain accountable for what suppliers do on your behalf. Supplier tracking lets you show where personal data sits and under what terms, and that suppliers meet your security and quality requirements.
Proportionate to what they handle. A supplier processing patient data, or one critical to your product, warrants real scrutiny of their security posture and certifications. A supplier with no access to personal data or your systems does not.
A DPA is the contract term required under Article 28 of the UK GDPR whenever another organisation processes personal data on your behalf. If a supplier touches your personal data, you need one with them.
Usually not. Many established suppliers publish a standard DPA that you can accept and link to, which covers the requirement without a negotiation. Smaller or bespoke suppliers are more likely to need something signed.
Yes. Evaluate, approve and review suppliers against your quality requirements alongside your security and data protection checks, with the evidence and review history auditors expect, all in one register.
At least once a year is common, and more often for high-risk or critical suppliers. Assuric sets review dates for each supplier and reminds you when a reassessment is due.
Yes. We import your existing supplier register during onboarding and match suppliers to the library, so their security information is filled in for you.
See how Assuric can help you assess, approve and monitor every supplier, all in one place.