A complete record of processing, built in
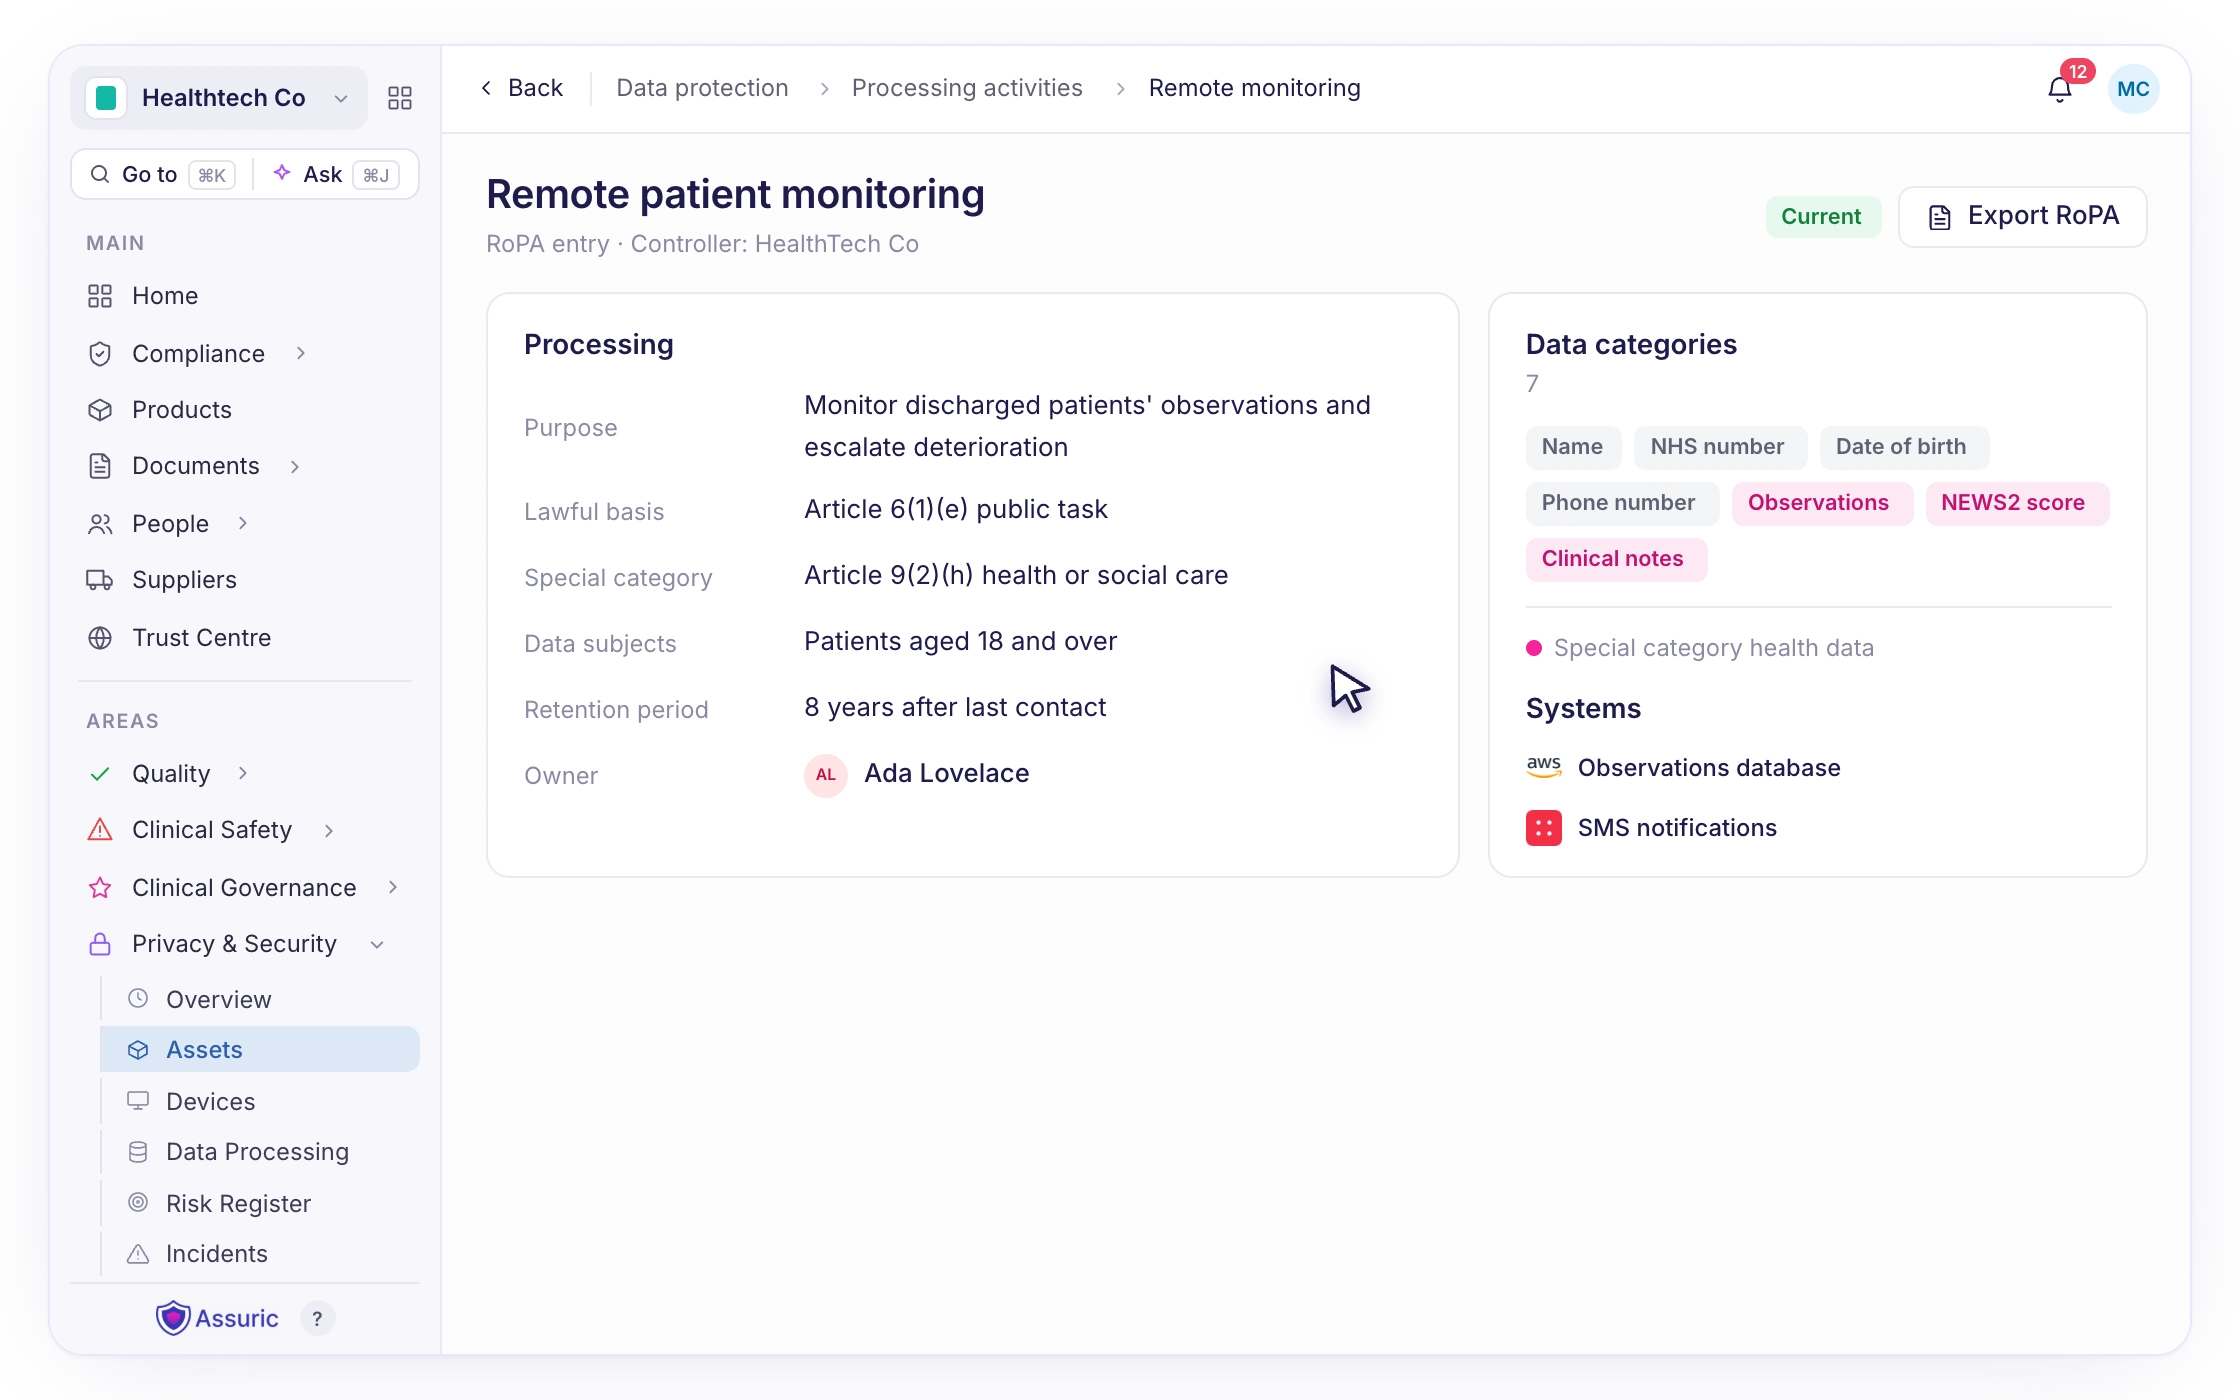
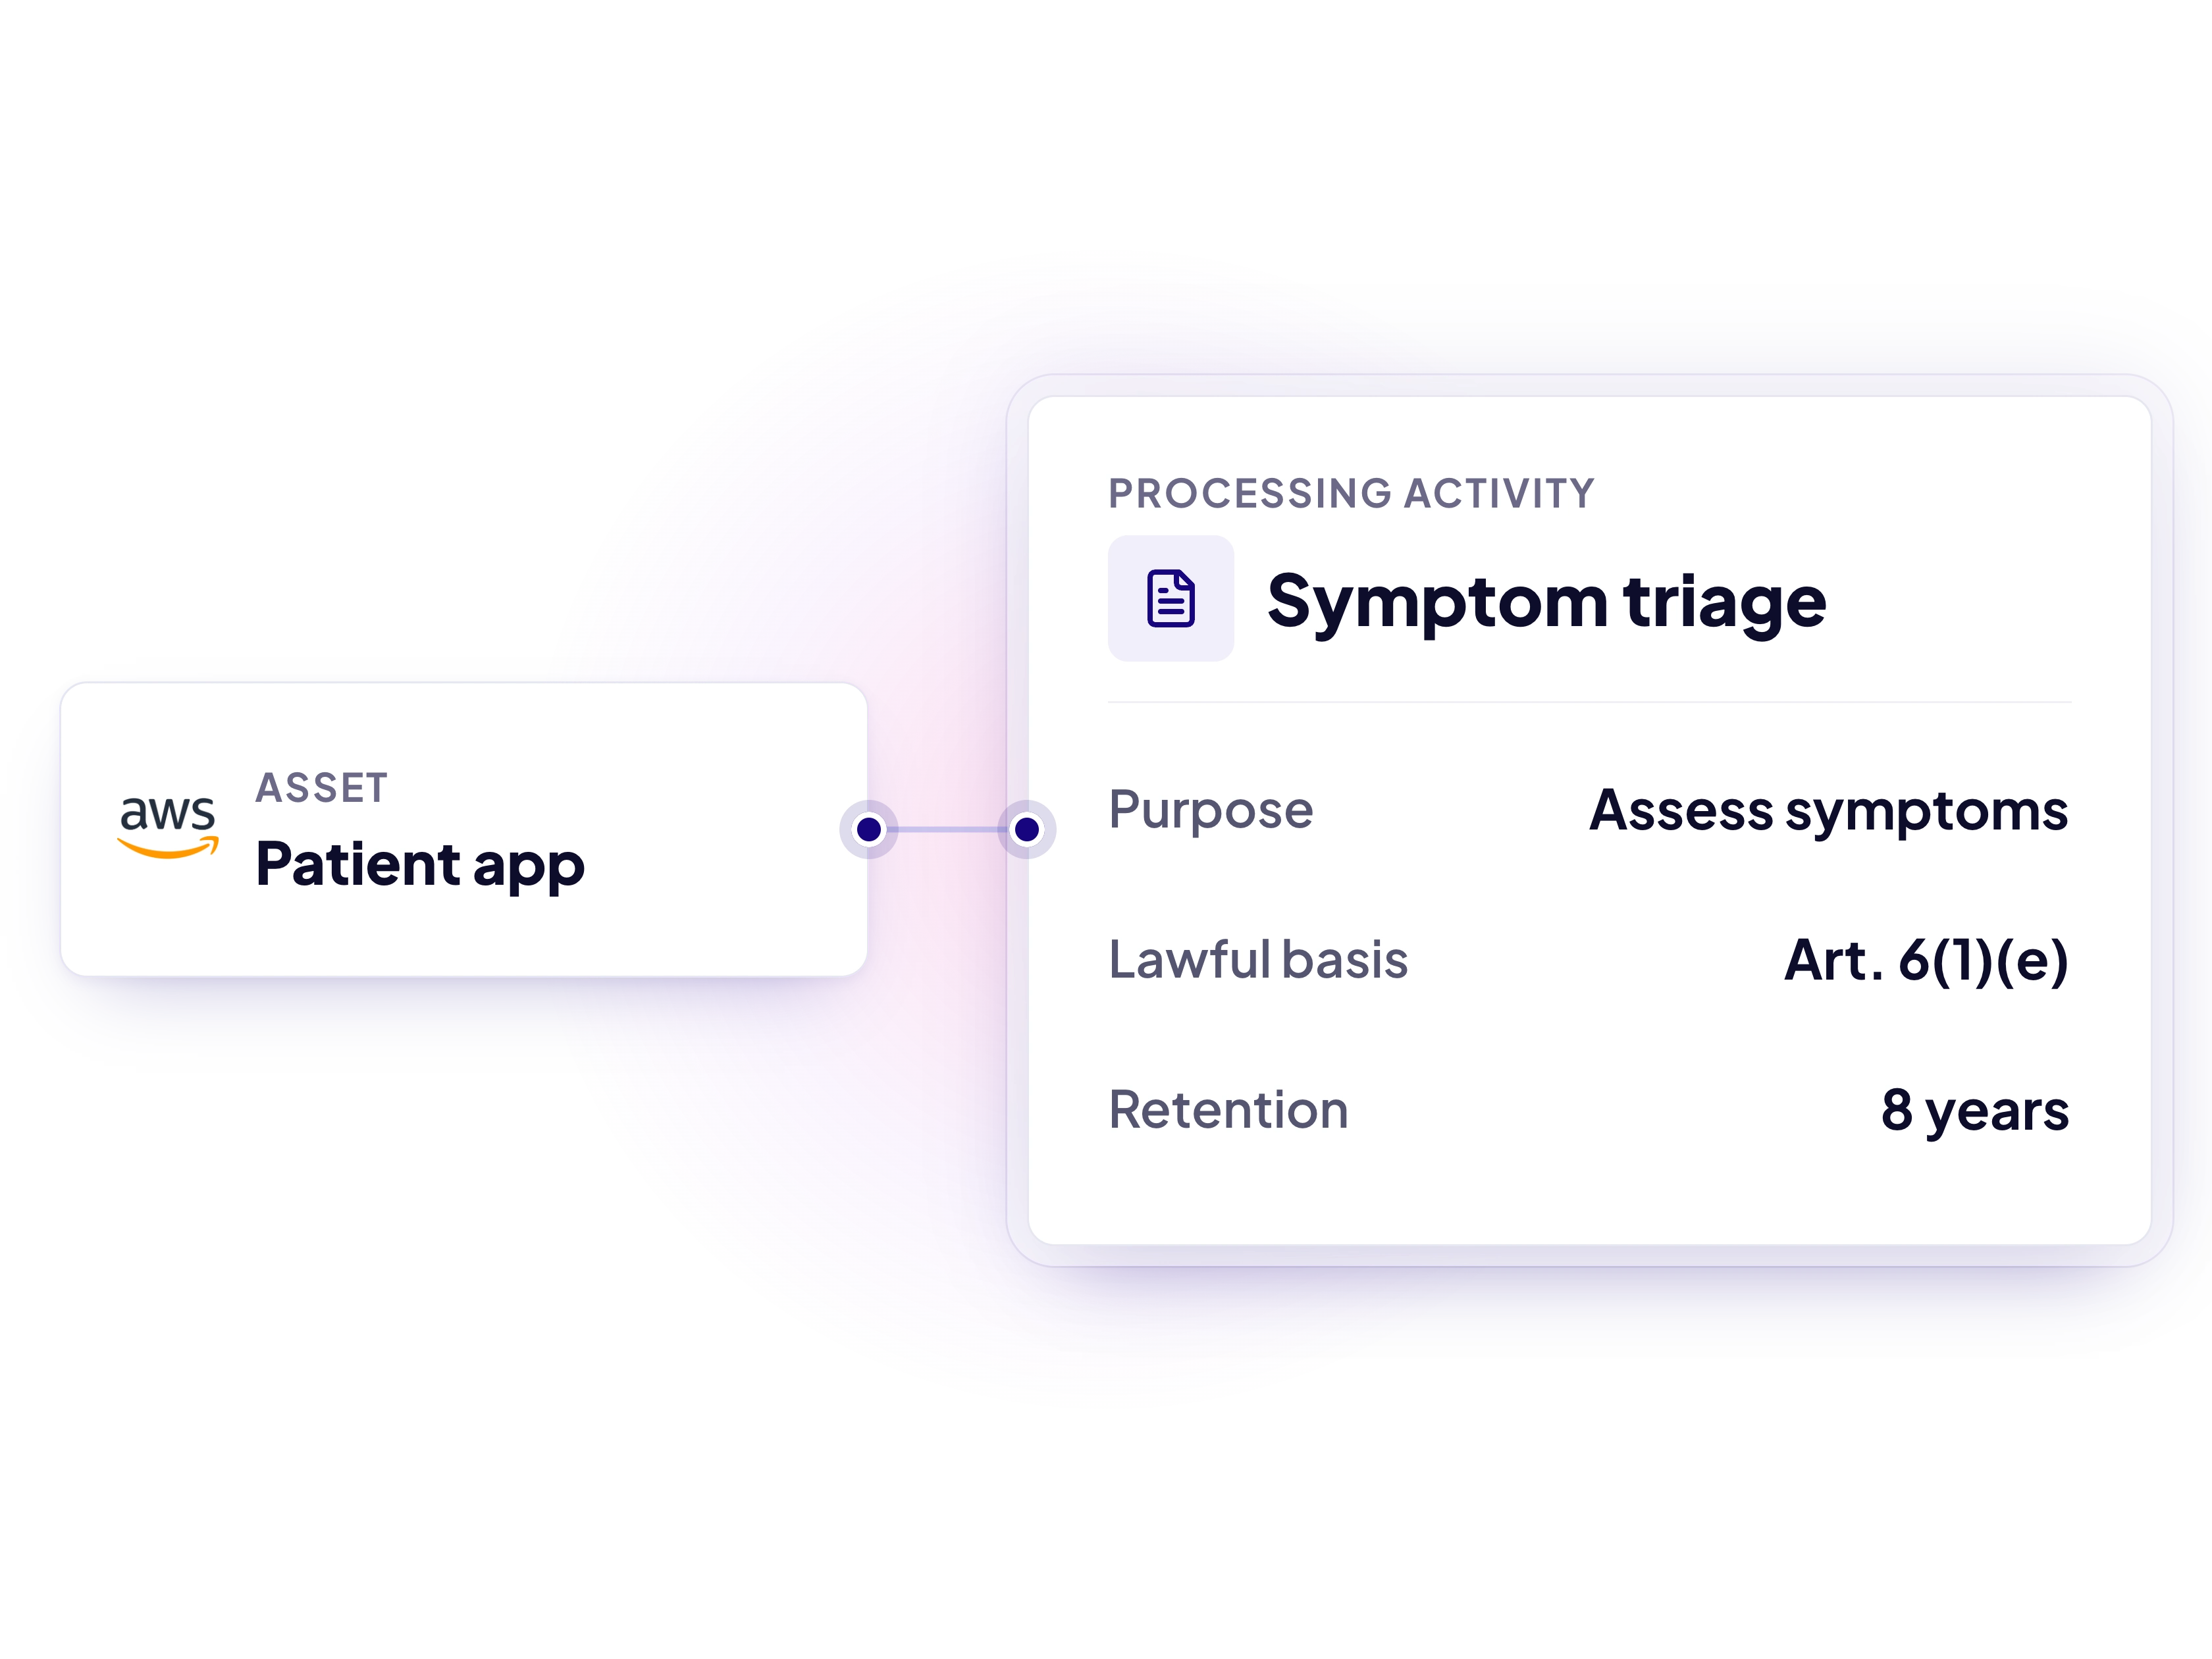
Track every processing activity in one Article 30 compliant record, with purpose, data categories, lawful bases, Article 9 conditions and retention periods all in one place.
Keep your DPIAs and records of processing activities (RoPA) in one place, easily kept current through AI and automation.
Trusted by dataprotection teams


Features
Track every processing activity in one Article 30 compliant record, with purpose, data categories, lawful bases, Article 9 conditions and retention periods all in one place.
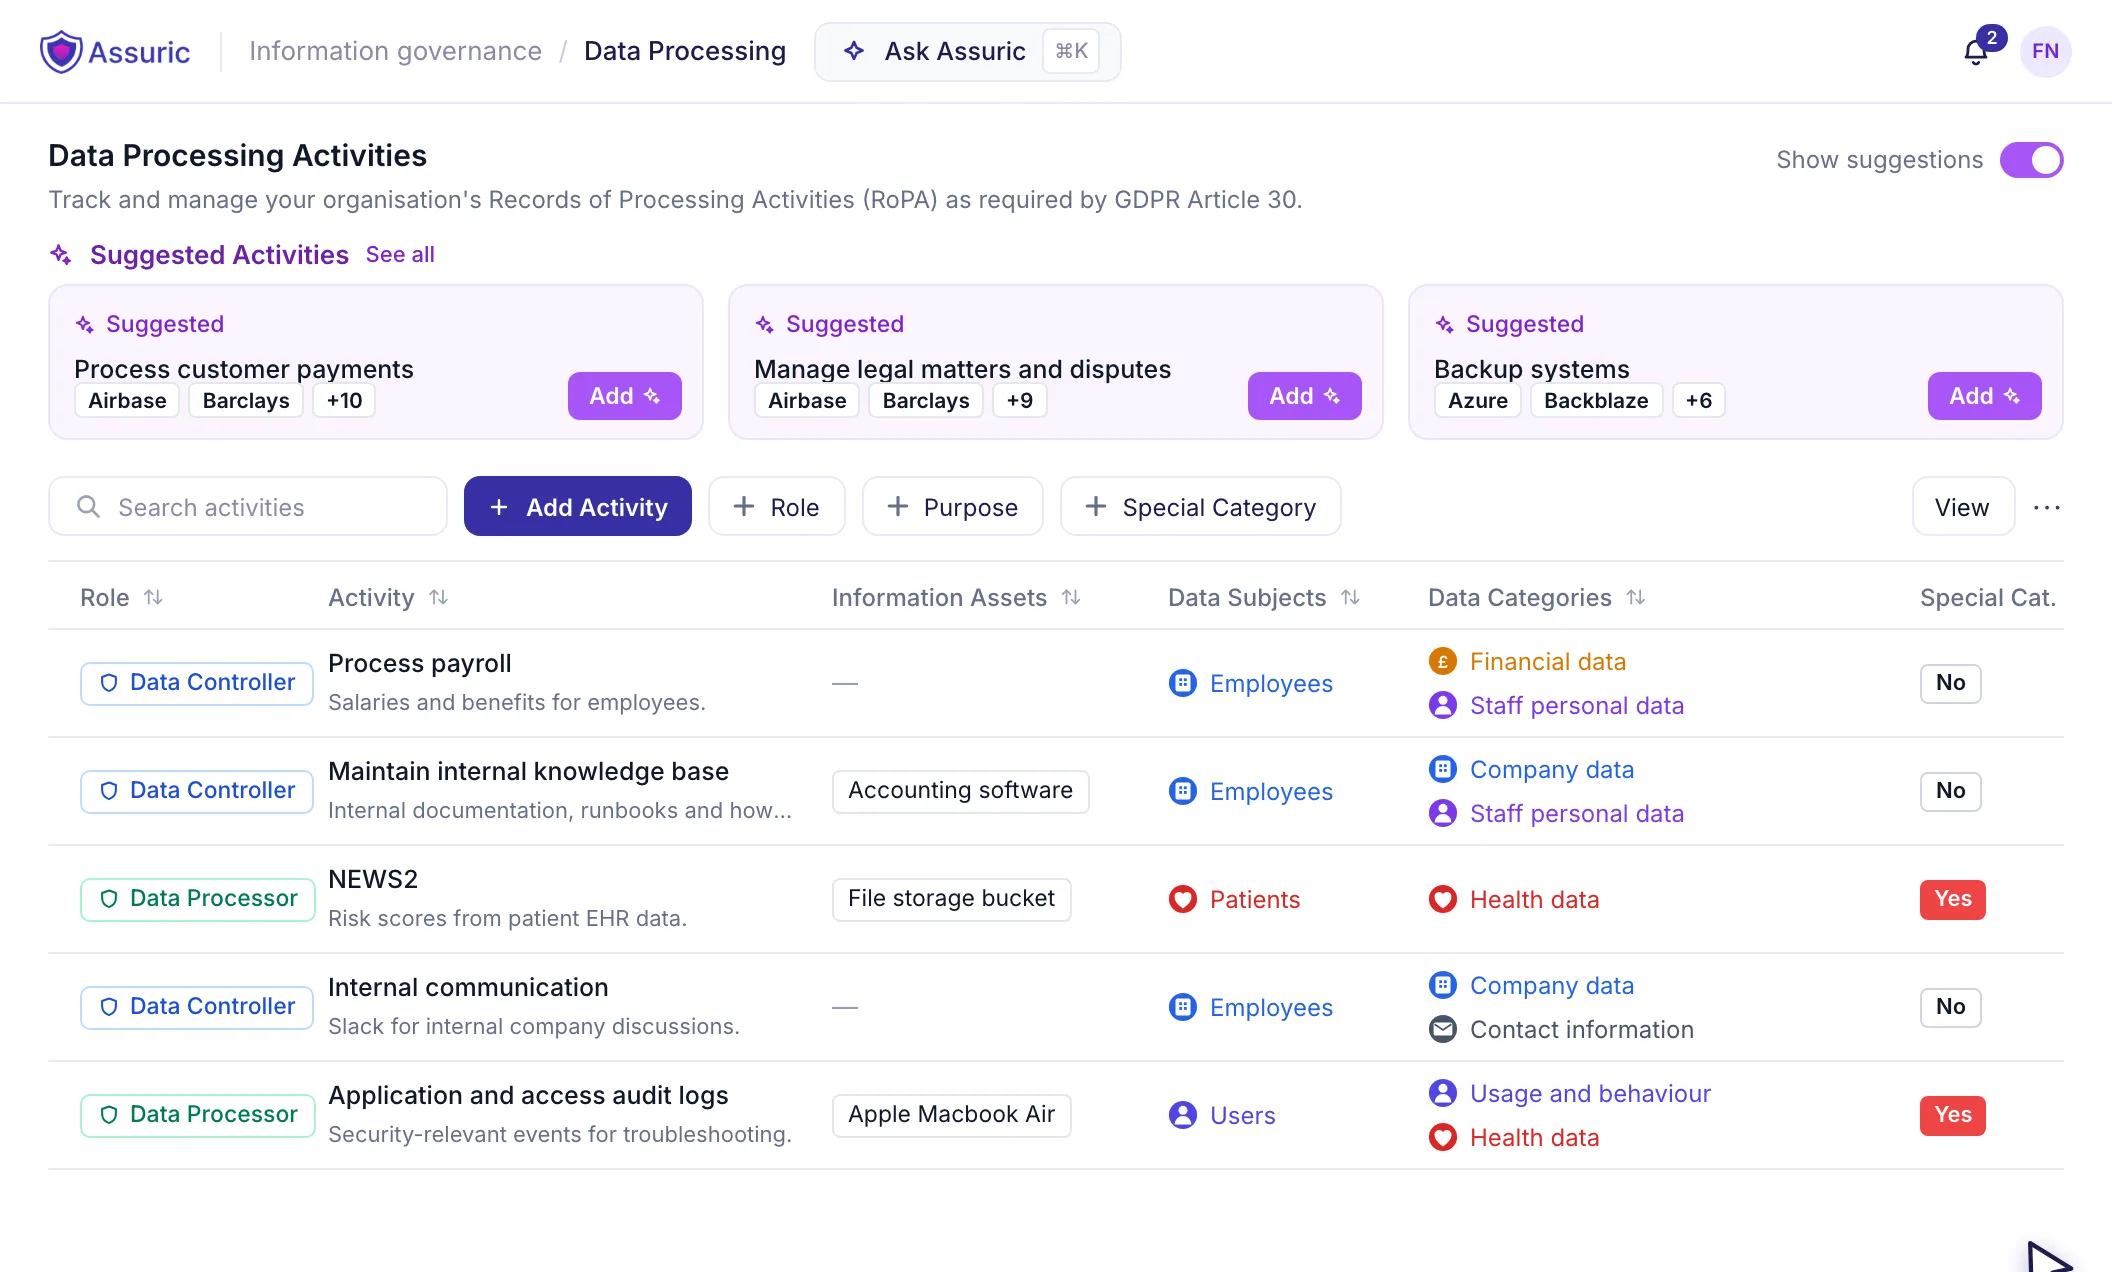
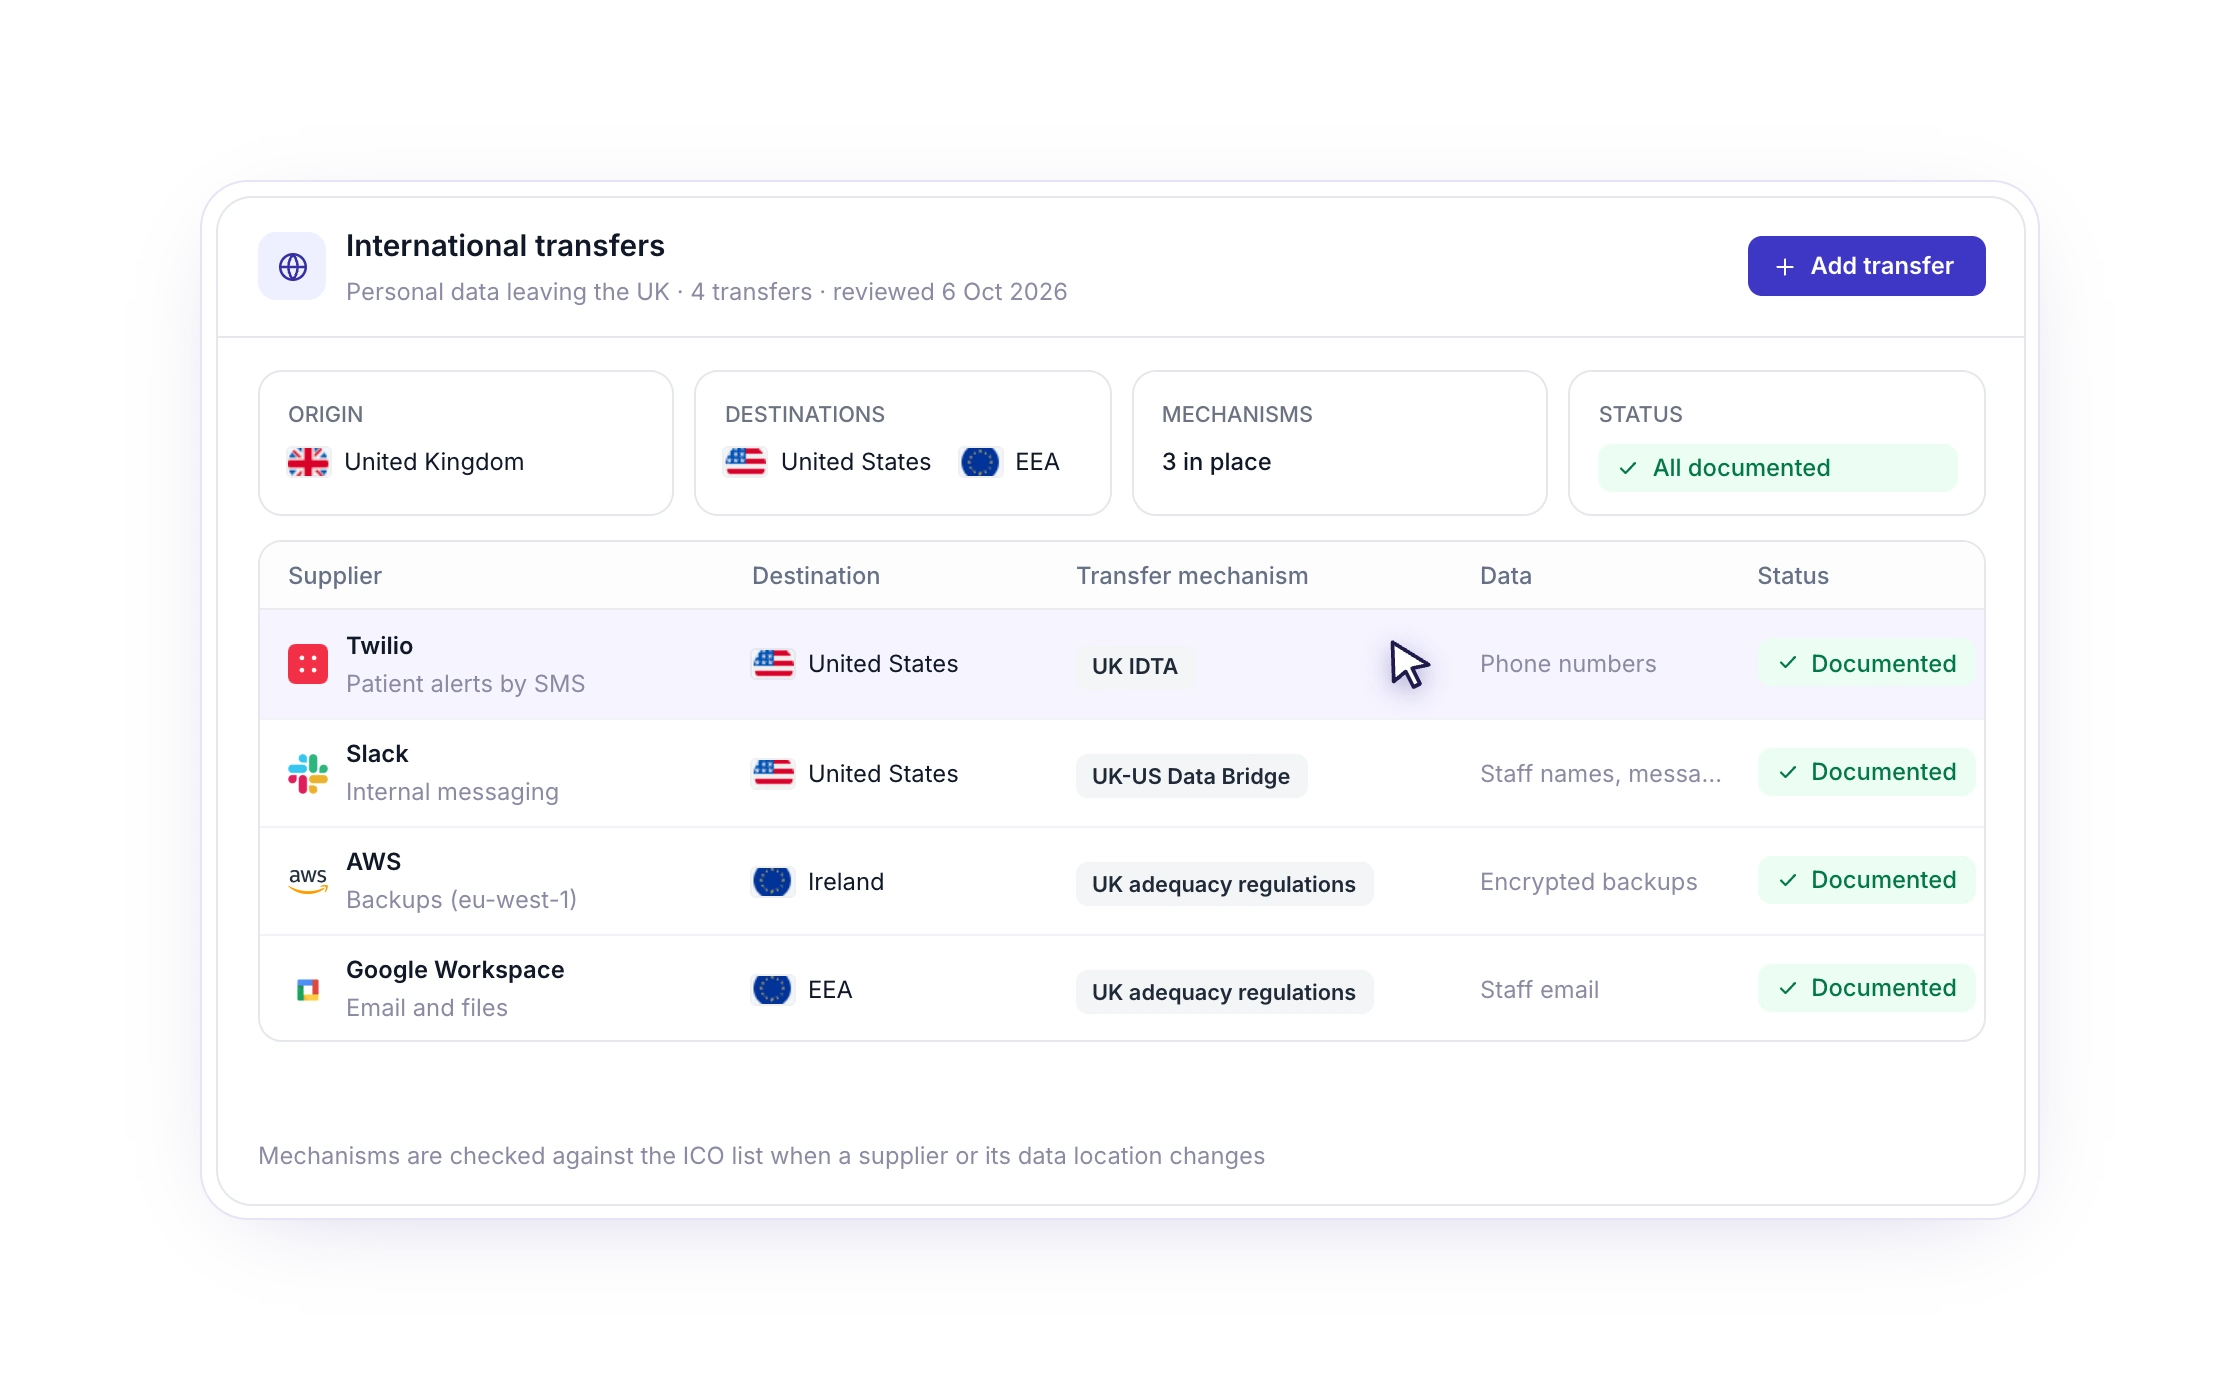
Track all activities, whether controller or processor, including international transfers. Integrations, automation and AI make it easy to keep your RoPA accurate and up to date as things change.
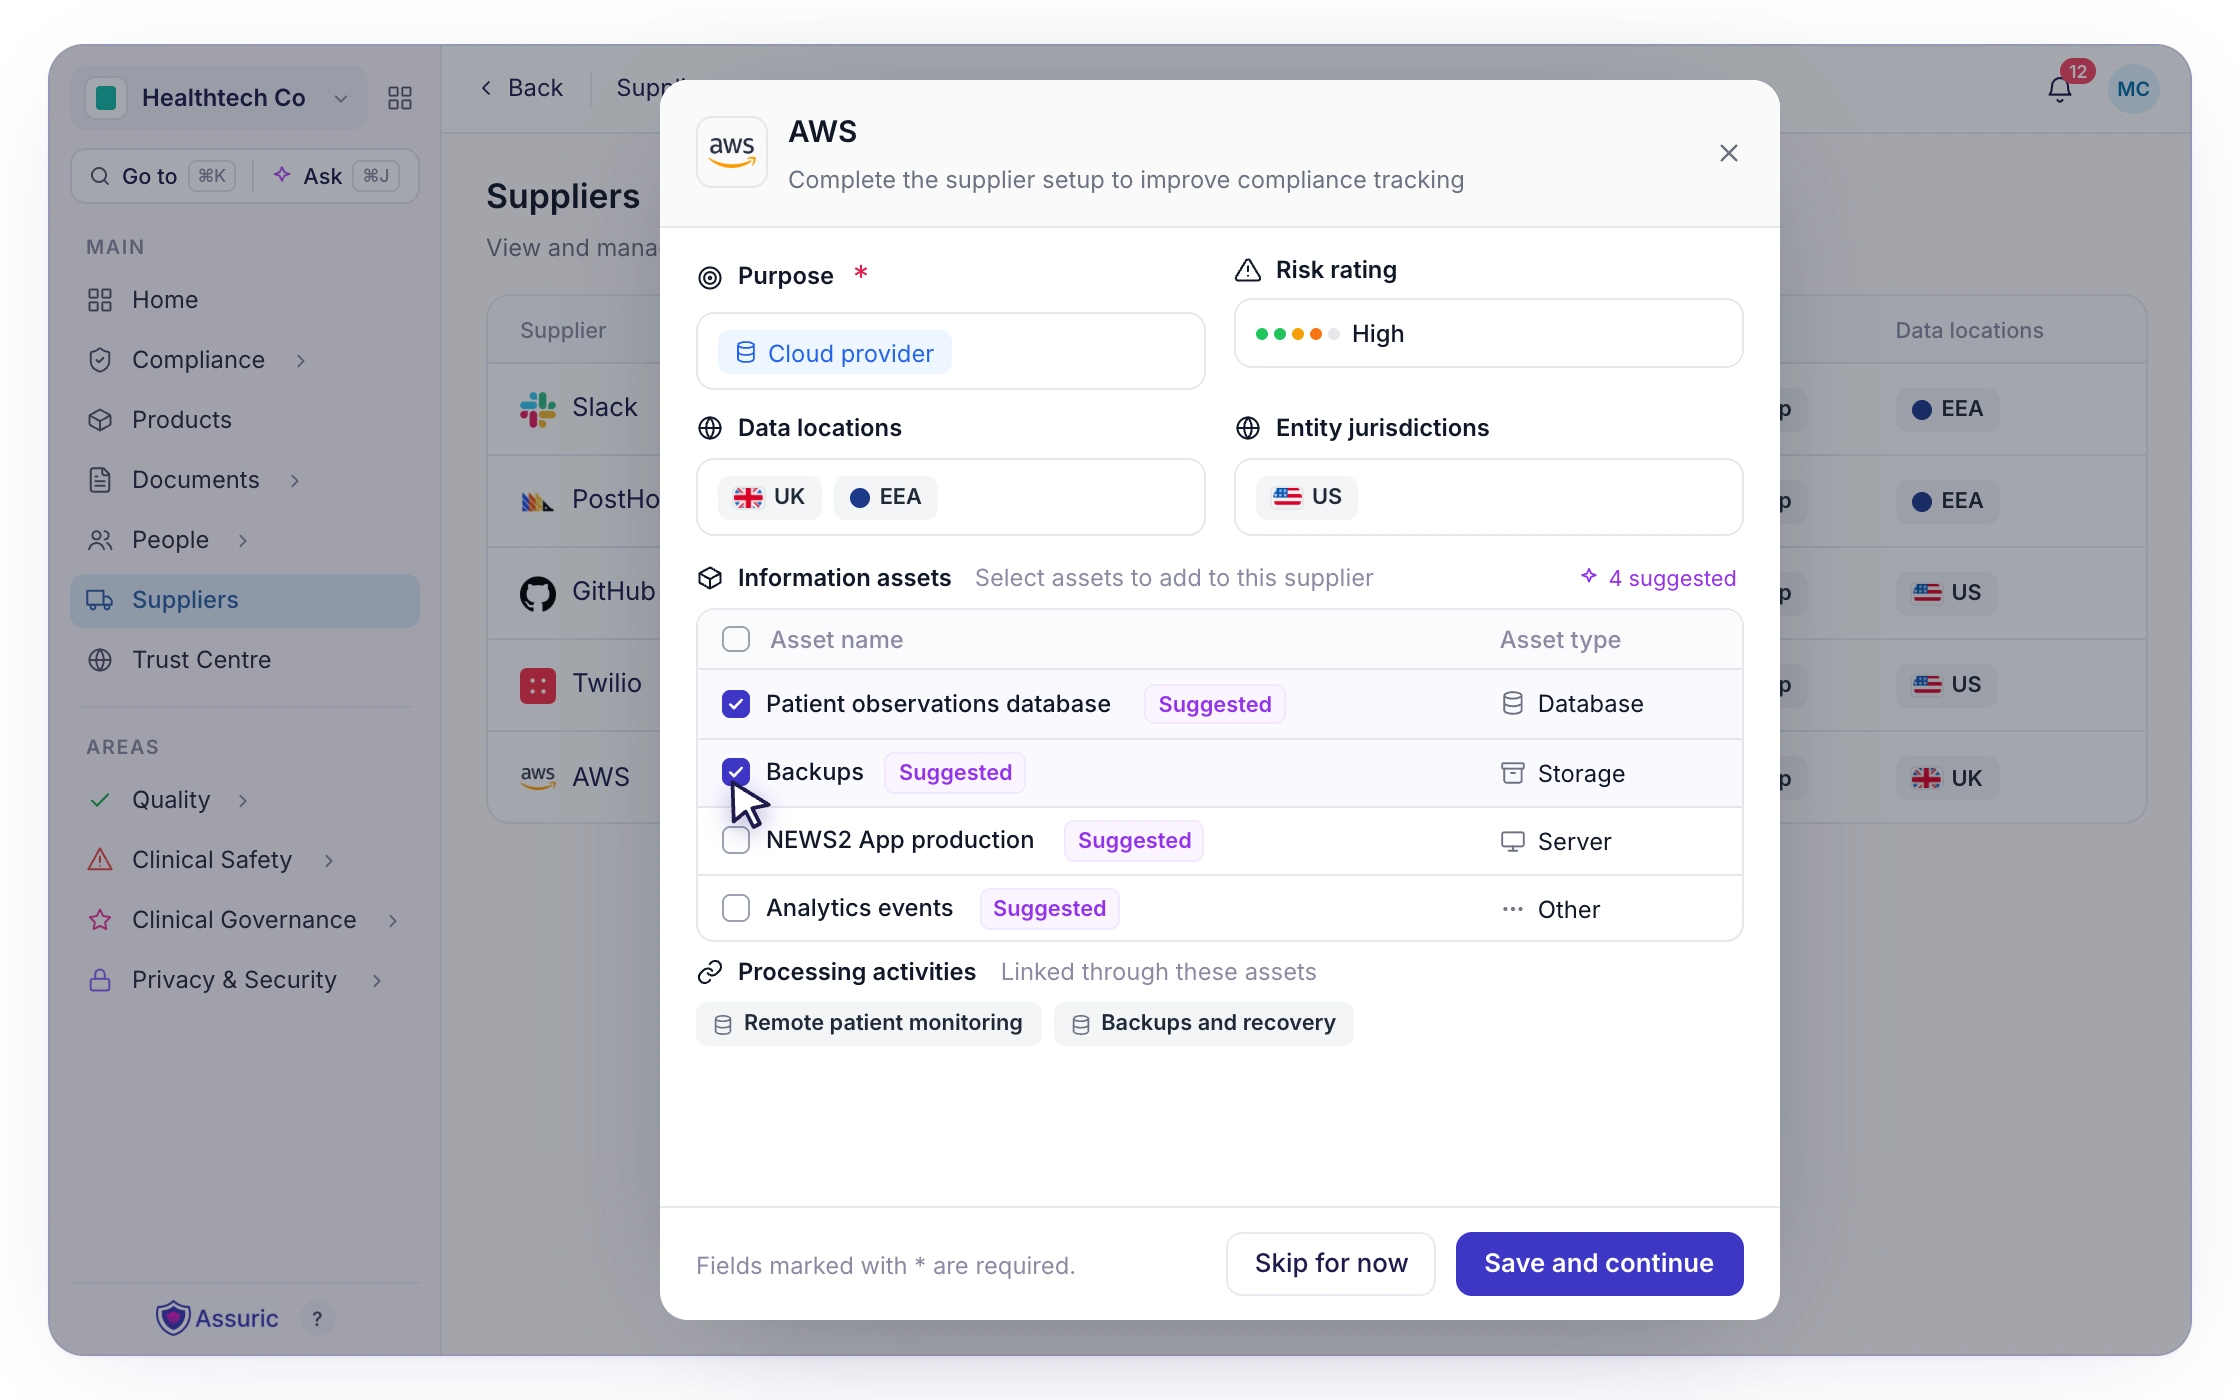
Link each processing activity to the relevant information assets, suppliers and risks with full traceability, so you can follow personal data end to end.
Start from smart, configurable templates and draft high-quality assessments using the processing activities, assets, suppliers and risks already recorded in your workspace.
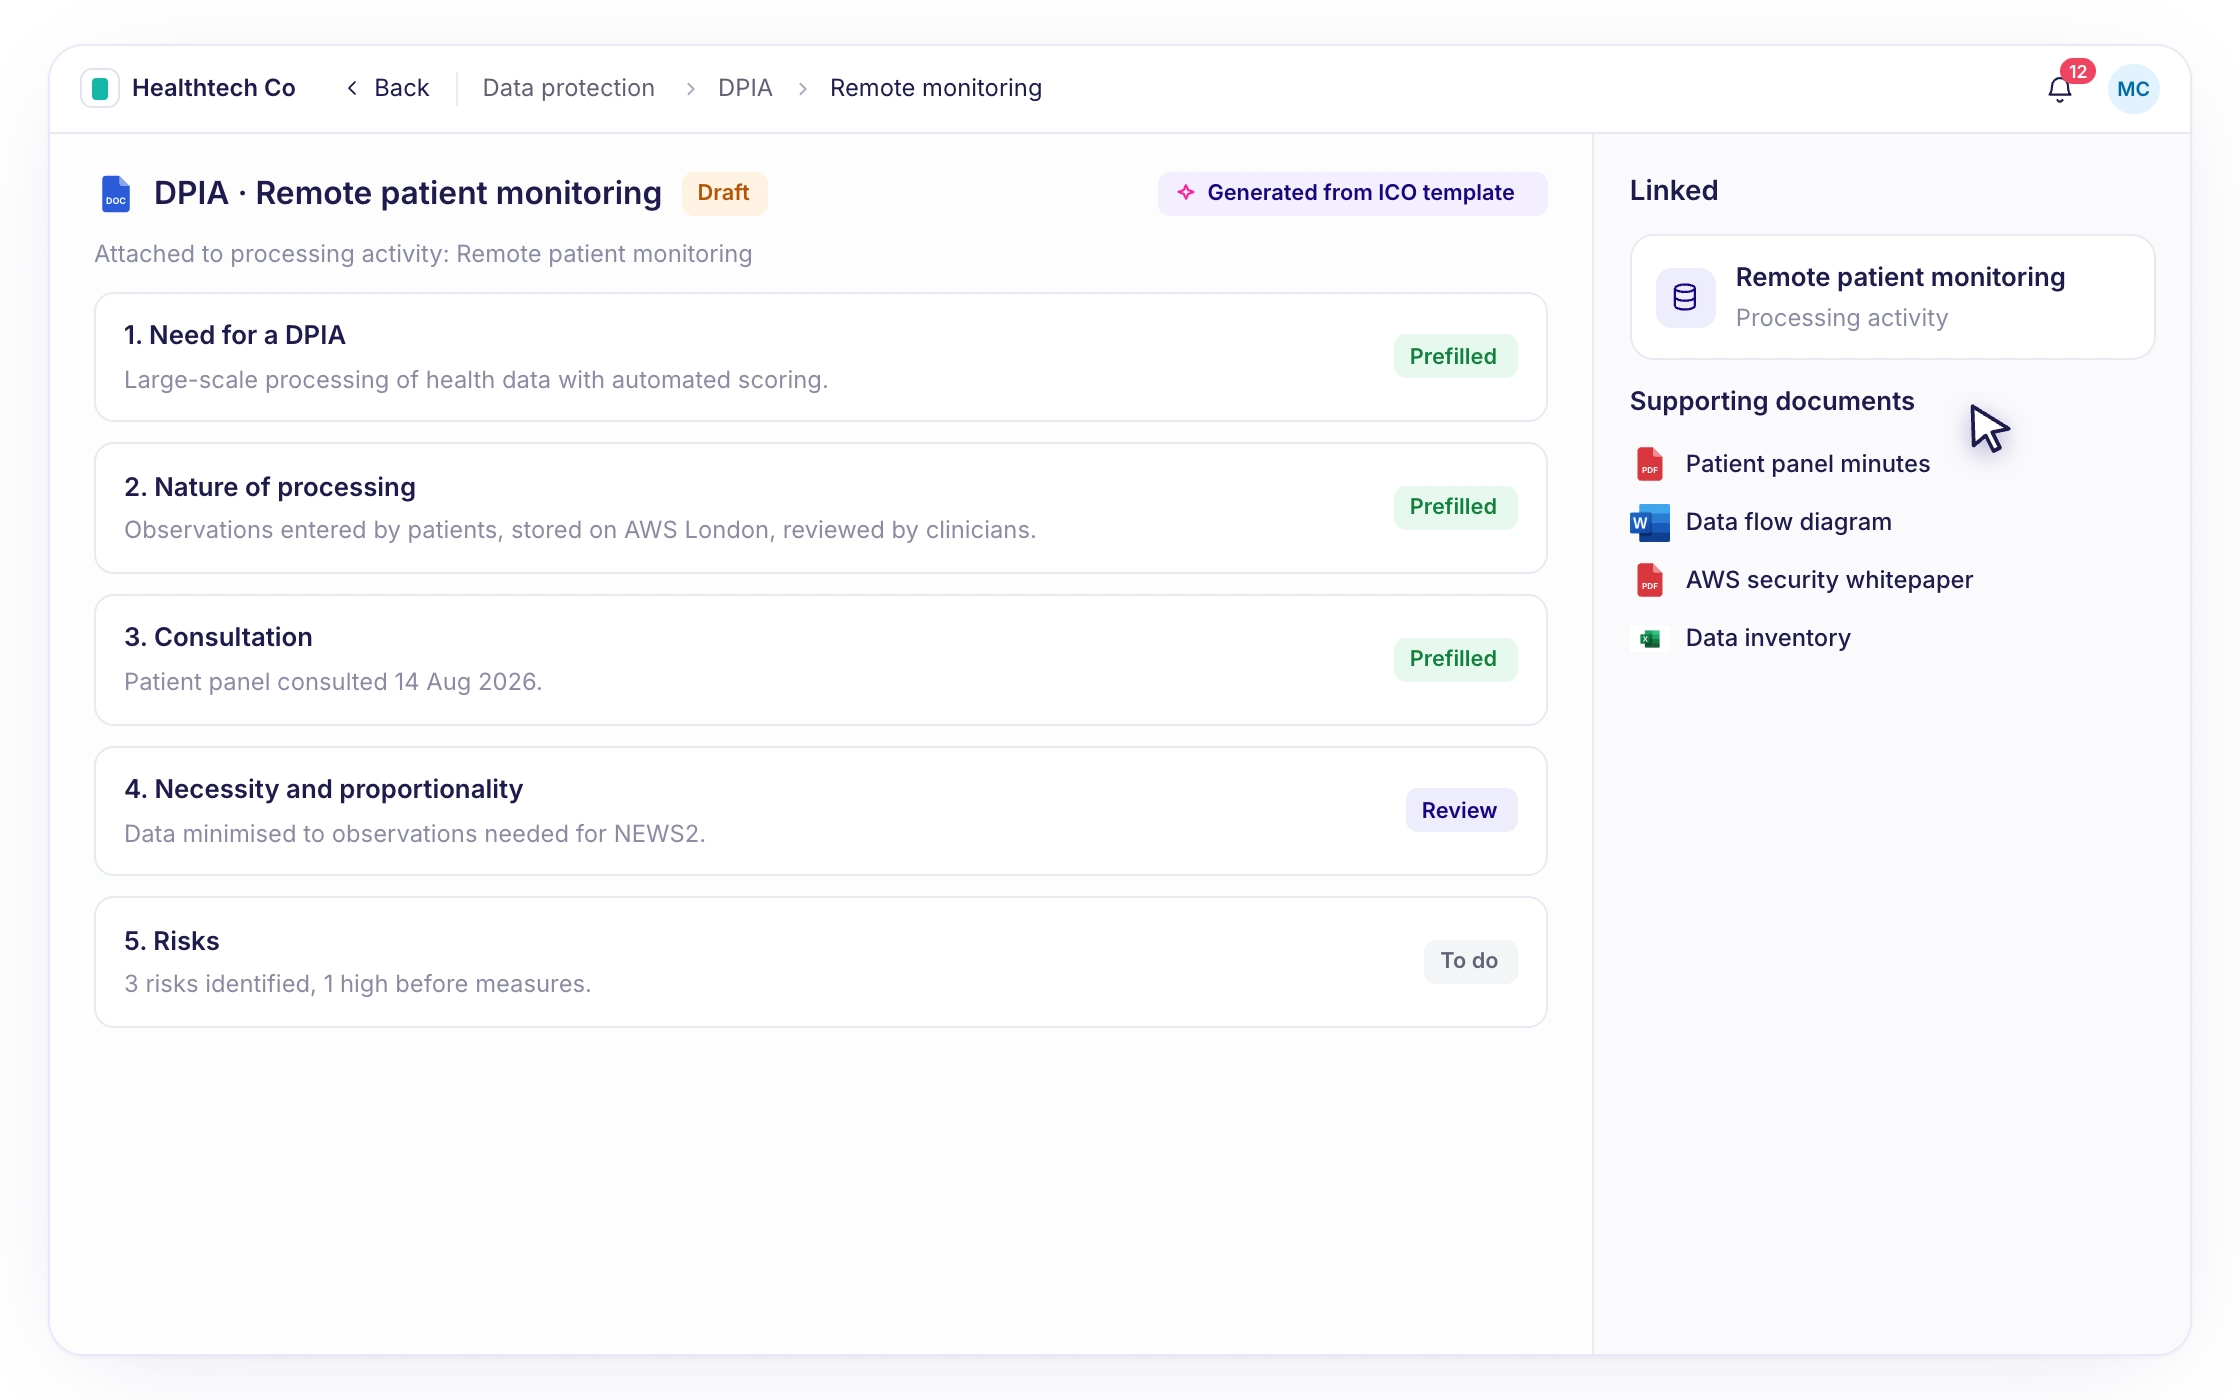
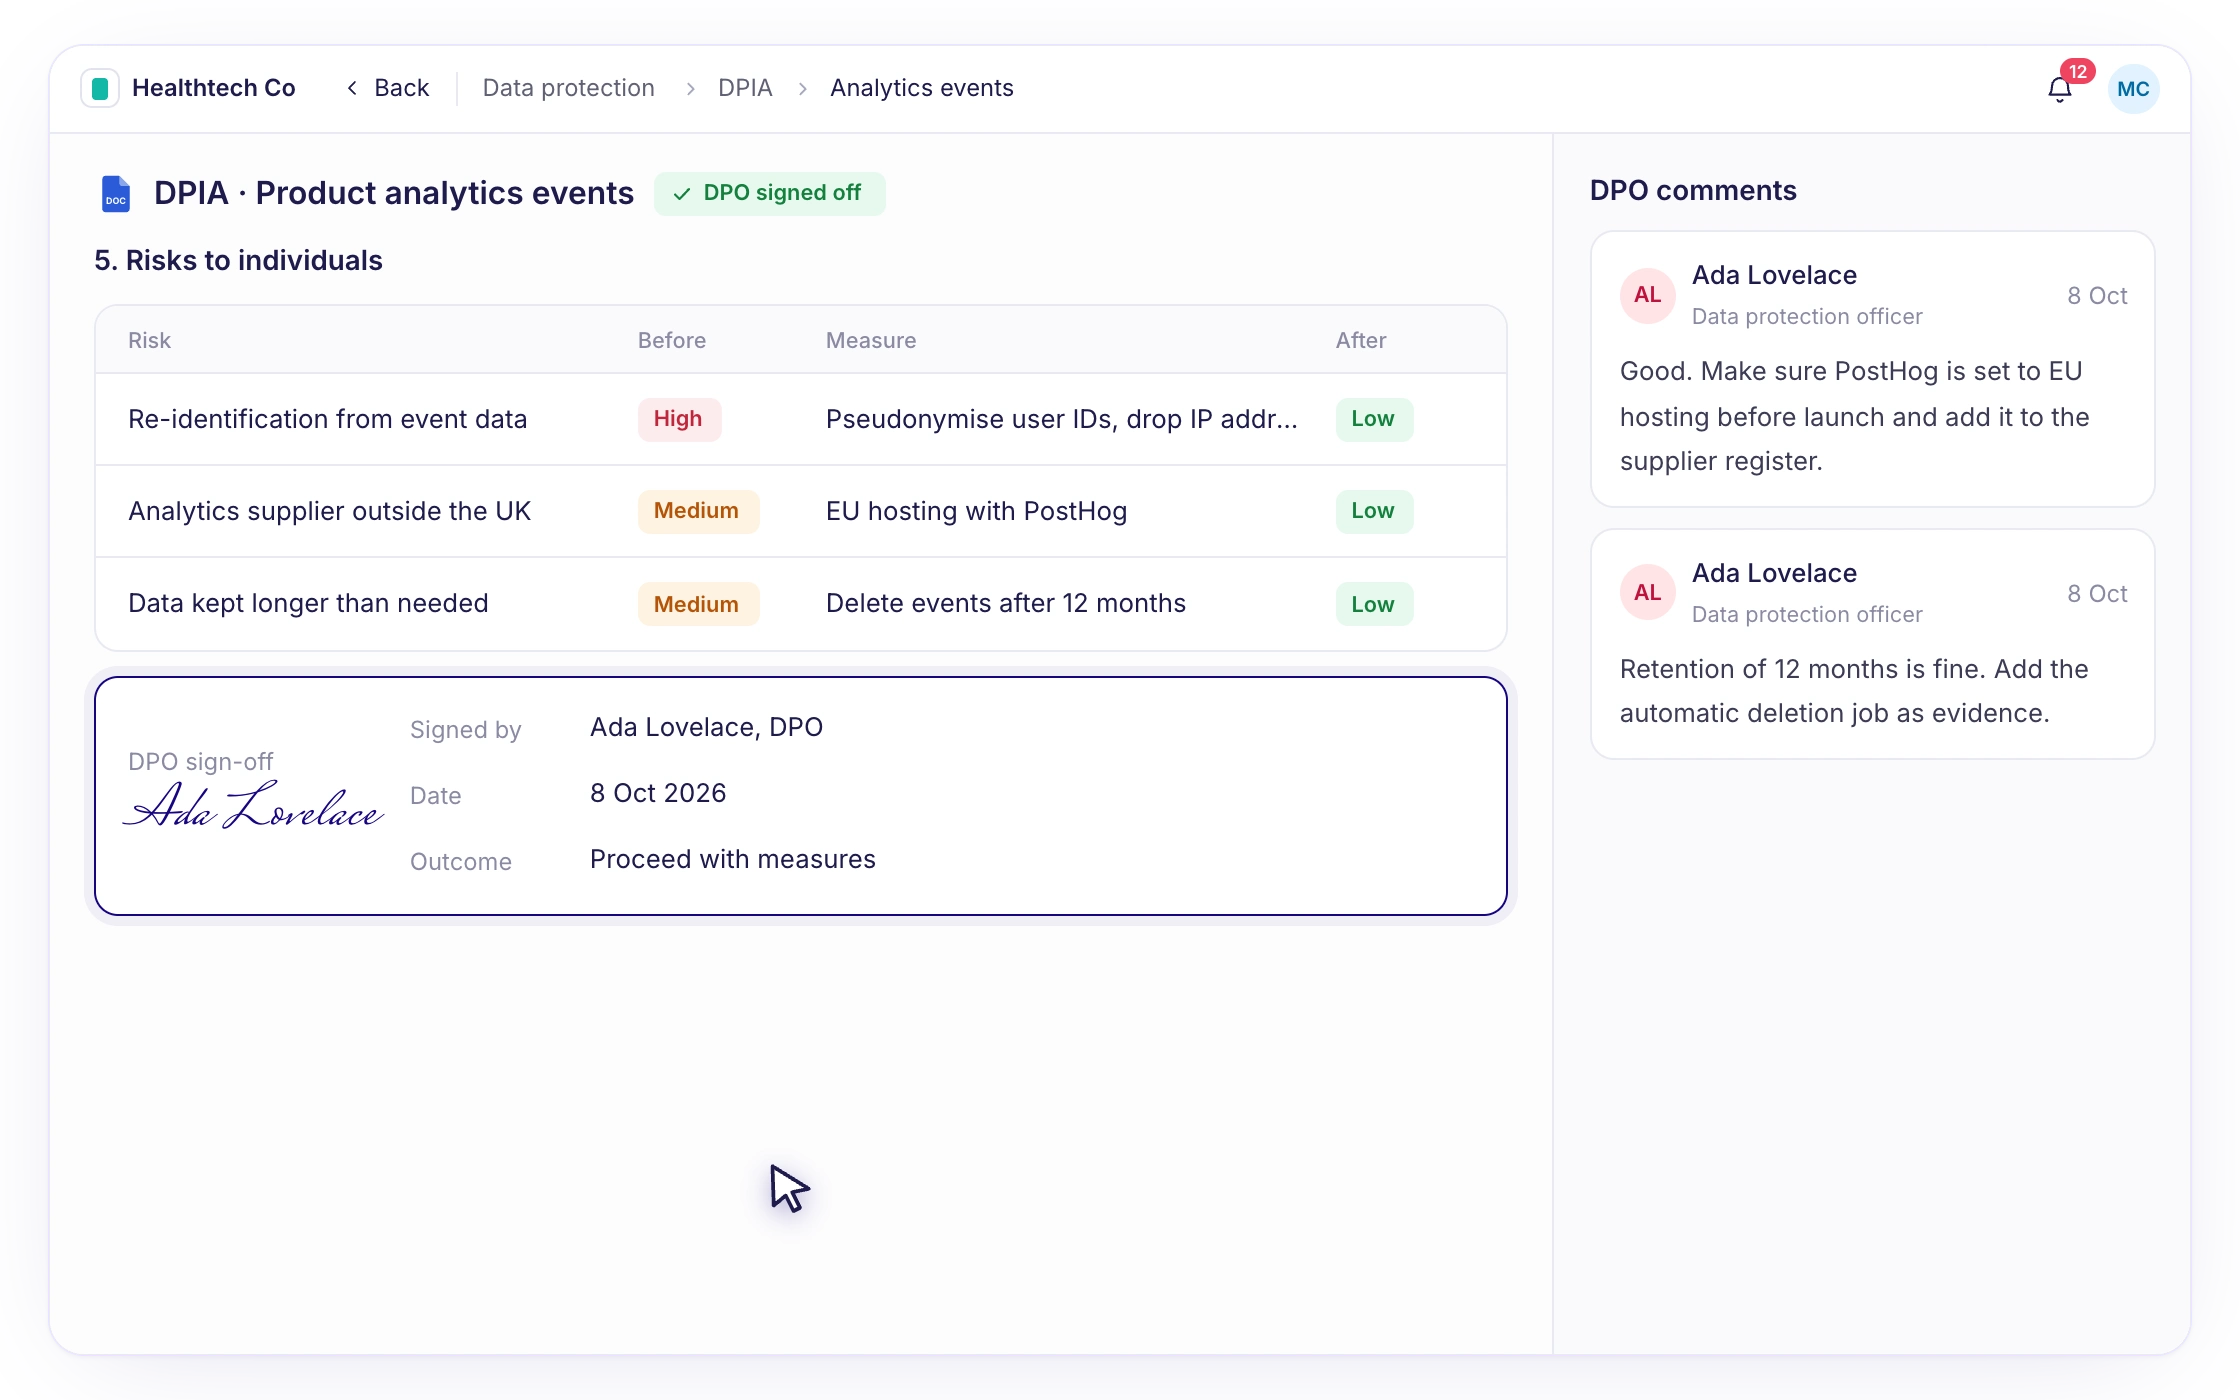
Track and manage all of your DPIAs in one place, with full version control and approval cycles, including external DPO review if required before they are finalised.
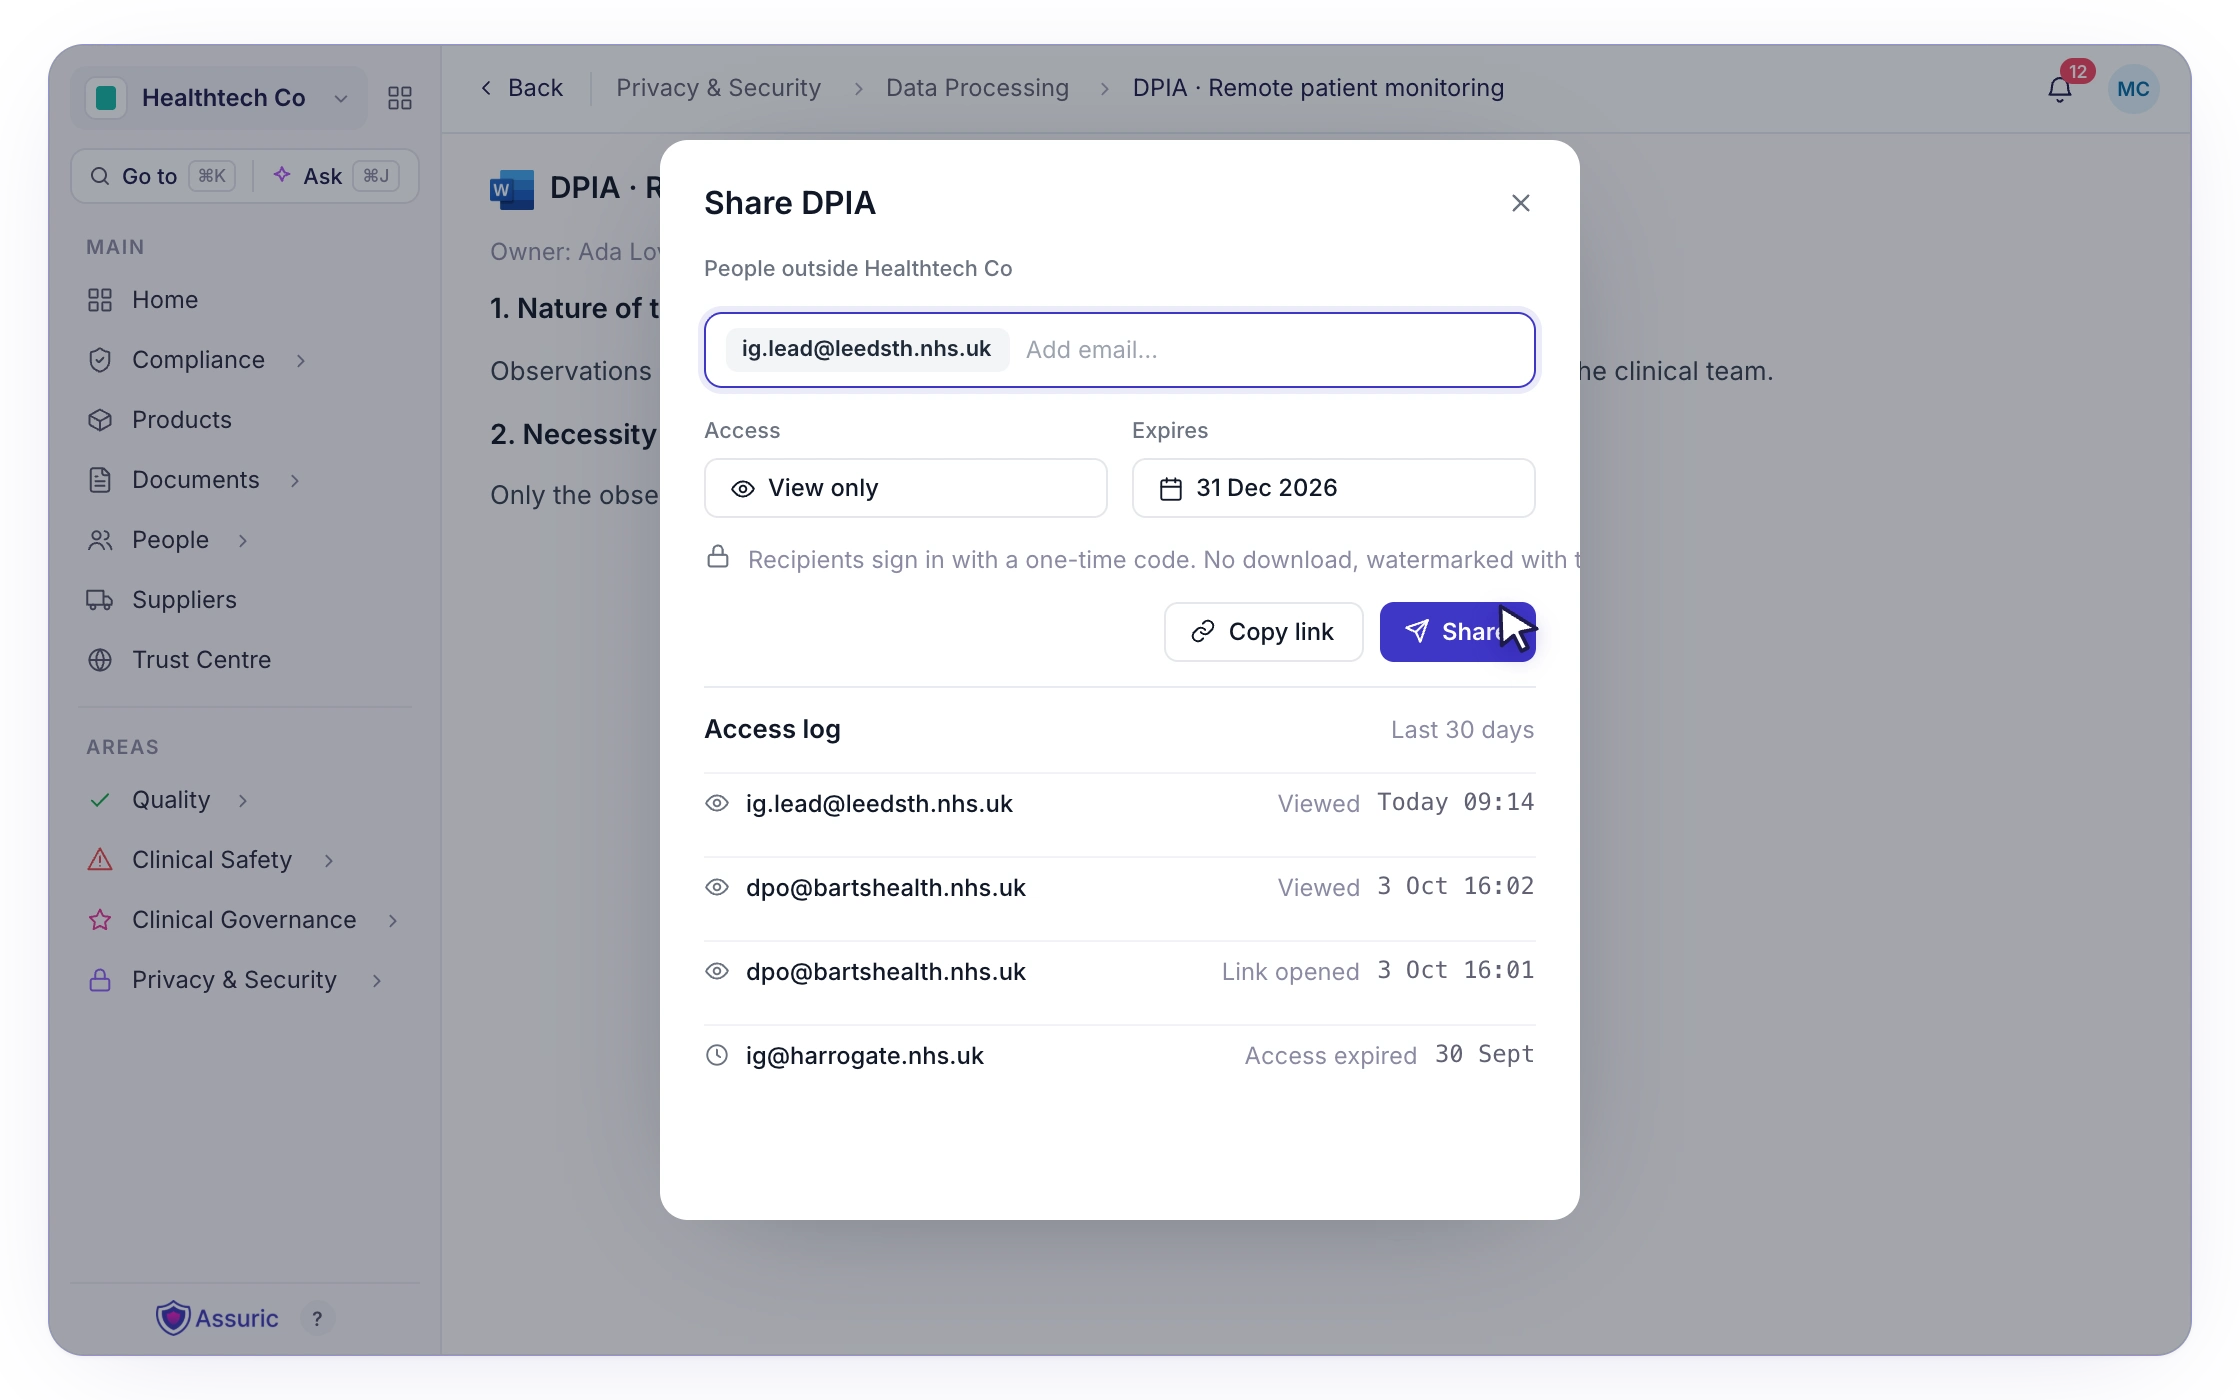
Share finished DPIAs with NHS buyers, partners and other external stakeholders through your own Trust Centre, without exporting and emailing documents back and forth.
Benefits
Know exactly what personal data you process, why, where it goes and how long you keep it, without chasing colleagues for answers.

Have your RoPA, DPIAs and supporting evidence ready when an NHS buyer, the DSPT or an assessor asks, rather than pulling them together at the last minute.
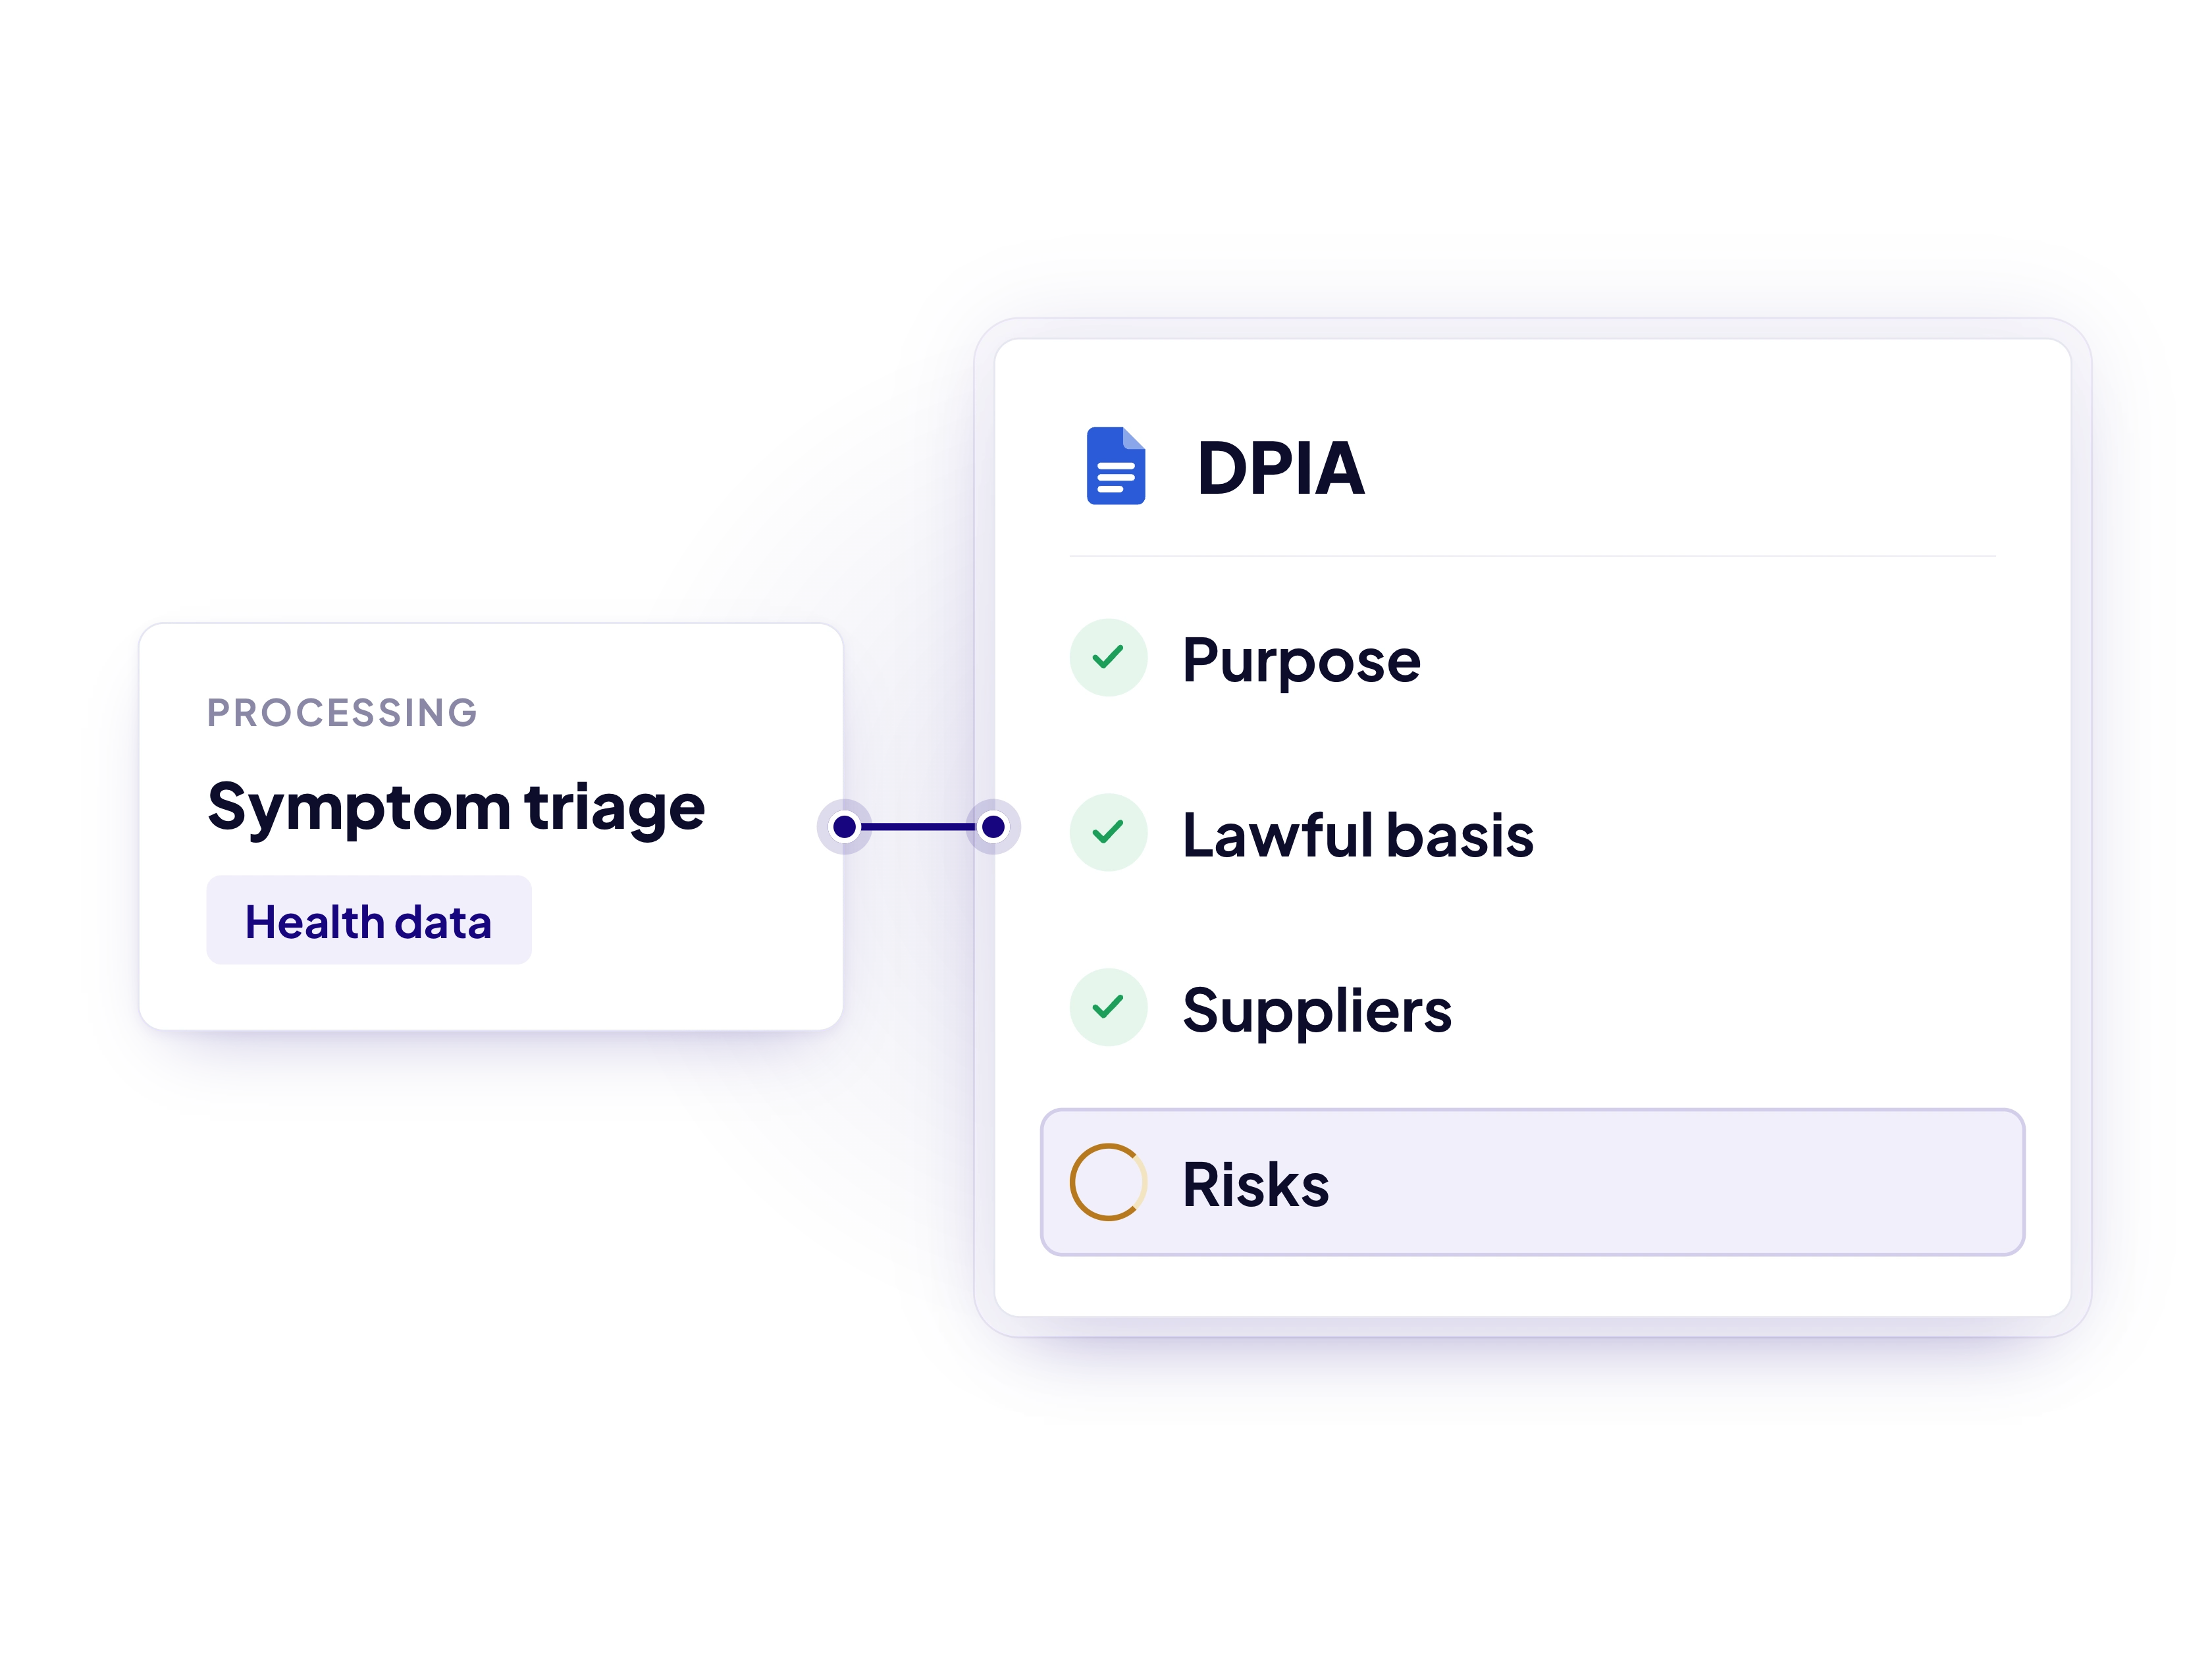
Templates, automation and AI take care of the repetitive work, so keeping records current takes minutes, not a quarterly clean-up.
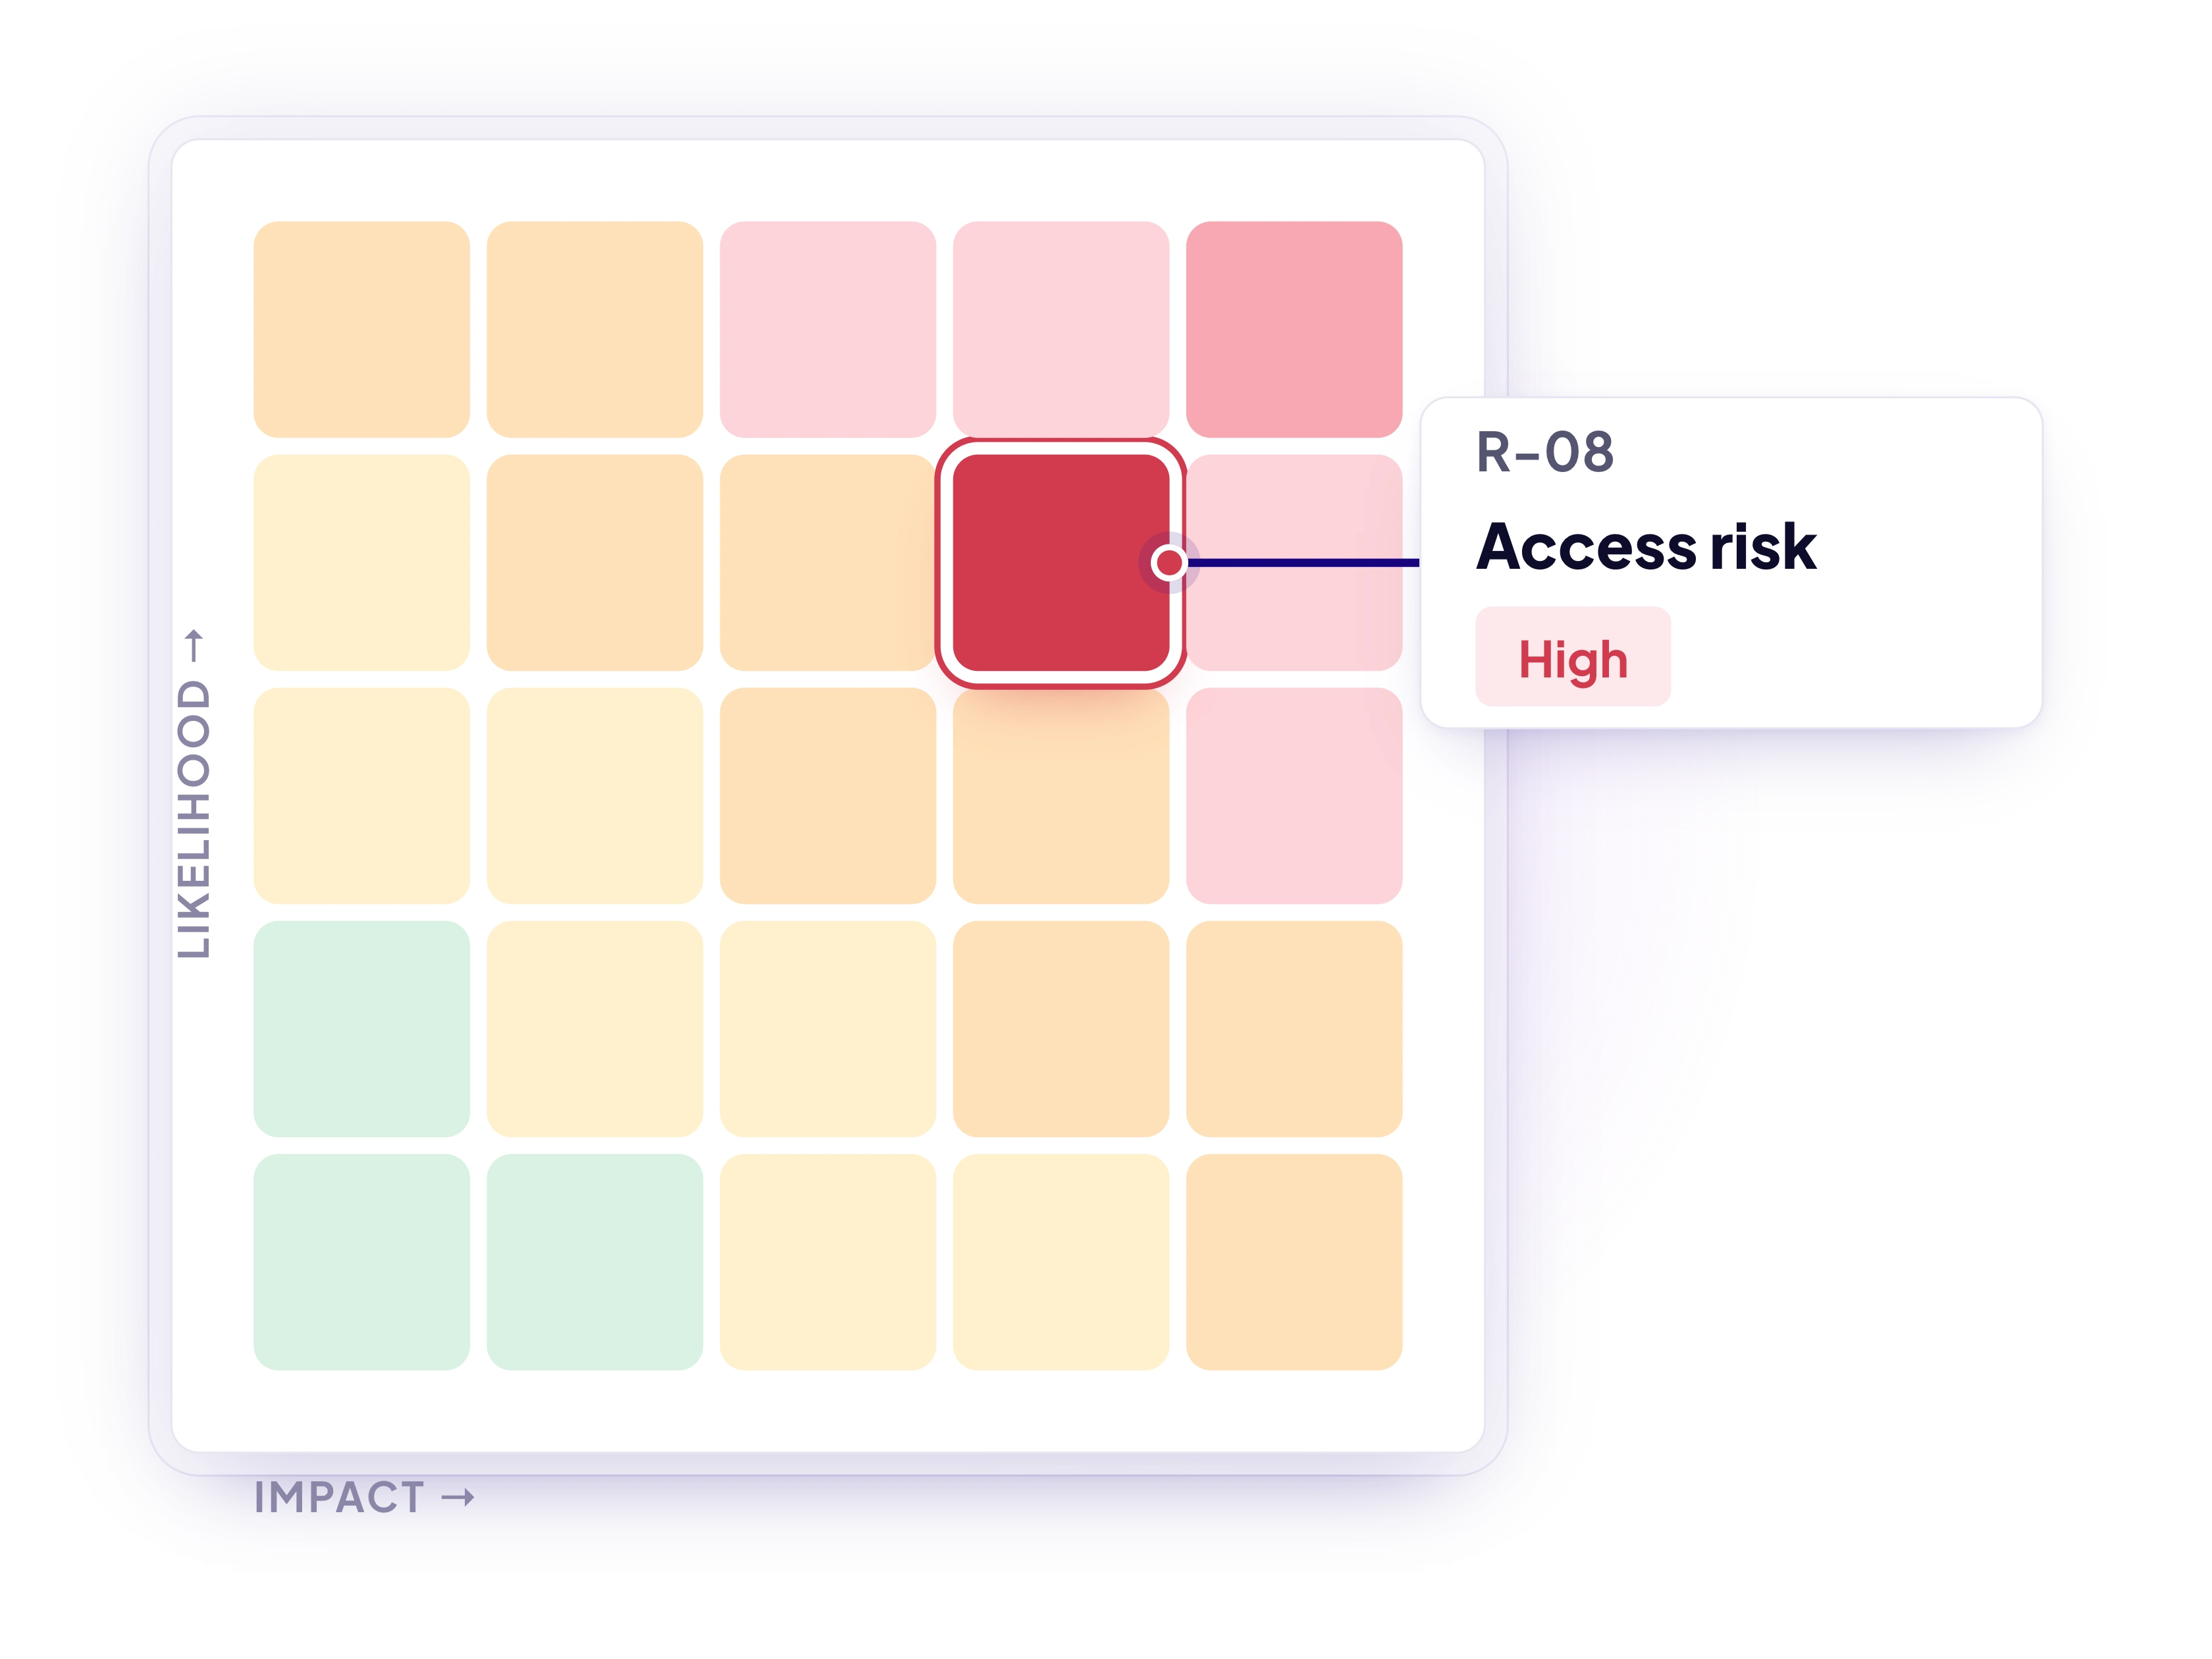
Spot high-risk processing early, with DPIAs and risks linked to each activity, so issues are dealt with before they reach a regulator.
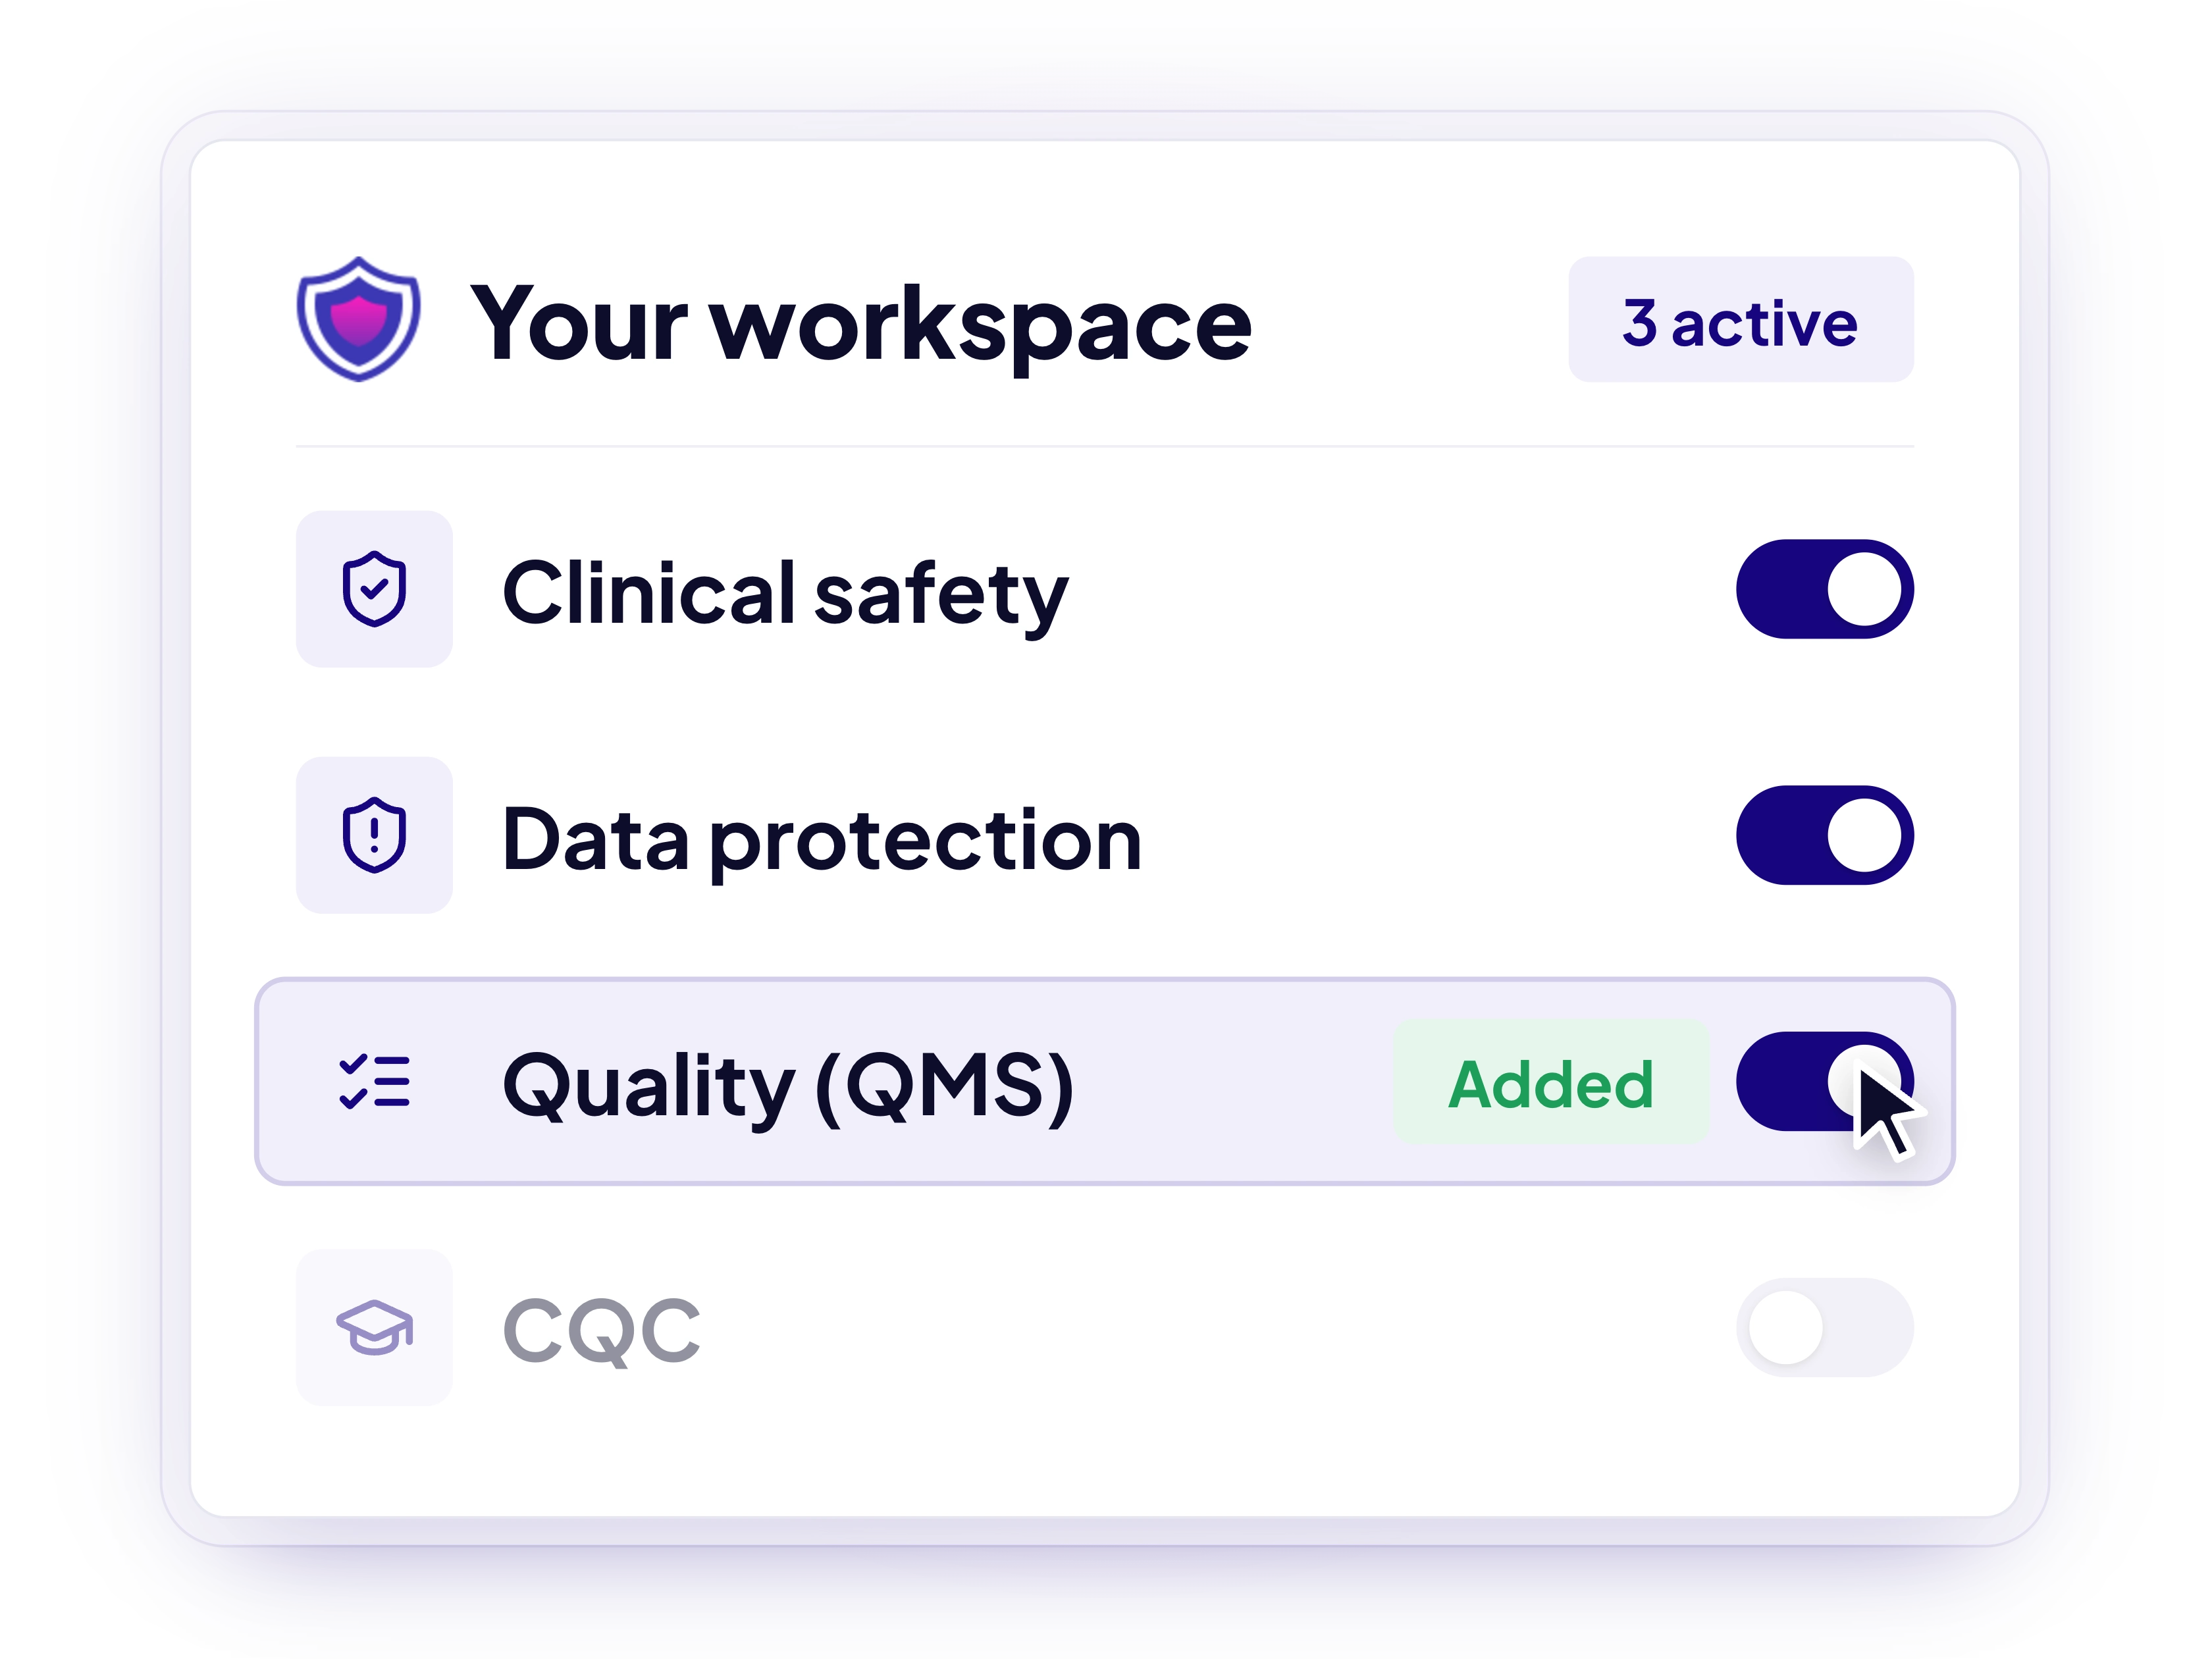
Cover UK and EU MDR, NHS compliance, CQC, information security and more in one place, reusing evidence across frameworks instead of starting again.

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”
Maks Kozarzewski
COO, VitVio

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”
Paul Llewellyn
CCIO, Accenture

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”
Katie Baker
Director UK & Ireland, Tandem
Overlapping requirements and evidence are mapped across frameworks automatically, so you never do the same work twice.
A record of processing activities (RoPA) is a written record of how your organisation uses personal data: what you process, why, on what lawful basis, who you share it with, where it is stored and how long you keep it. It underpins your data protection compliance, and reviewers will often ask to see it.
Article 30 of the UK GDPR requires both controllers and processors to keep one. There is a limited exemption for organisations with fewer than 250 employees, but it does not apply if you process special category data such as health data, so in practice every healthtech organisation needs one. The NHS Data Security and Protection Toolkit (DSPT) also requires an up-to-date RoPA.
Whenever processing is likely to result in a high risk to individuals, which includes most large-scale processing of health data and most new uses of AI on patient data. In practice, if you are building health software you will need them, and doing one early is far easier than retrofitting it.
Under the UK GDPR, carrying out a DPIA is the controller’s responsibility, so as a processor you are not strictly required to complete one for processing you do on a customer’s behalf. In practice, though, you will usually end up writing it: NHS organisations and other controllers will either ask you for a DPIA covering your product, or send you their own template to complete. You will also need your own DPIA for any processing where you are the controller, and a completed DPIA is a requirement of NHS DTAC.
The ICO says you must appoint one if you are a public authority, or if your core activities involve large-scale processing of special category data, such as health data, or large-scale, regular and systematic monitoring of individuals. Many NHS buyers also expect one. Our Fractional DPO service can act as your named data protection officer, covering the requirement without an early hire.
Yes. We offer a full migration service, and Assuric’s AI can import an existing RoPA in minutes, so you don’t start from scratch.
Featured post
Learn how to create and maintain a Record of Processing Activities (ROPA) to meet GDPR and NHS DSPT compliance. Includes practical steps, lawful basis guidance, and a free ROPA template for digital health companies.

See how Assuric can help you manage your RoPA, DPIAs and more, all in one place.


