Scoping and methodology
A teach-back on your product and infrastructure. We cover web apps, mobile apps, infrastructure and cloud. We'll scope a secure test proportional to your needs, not beyond.
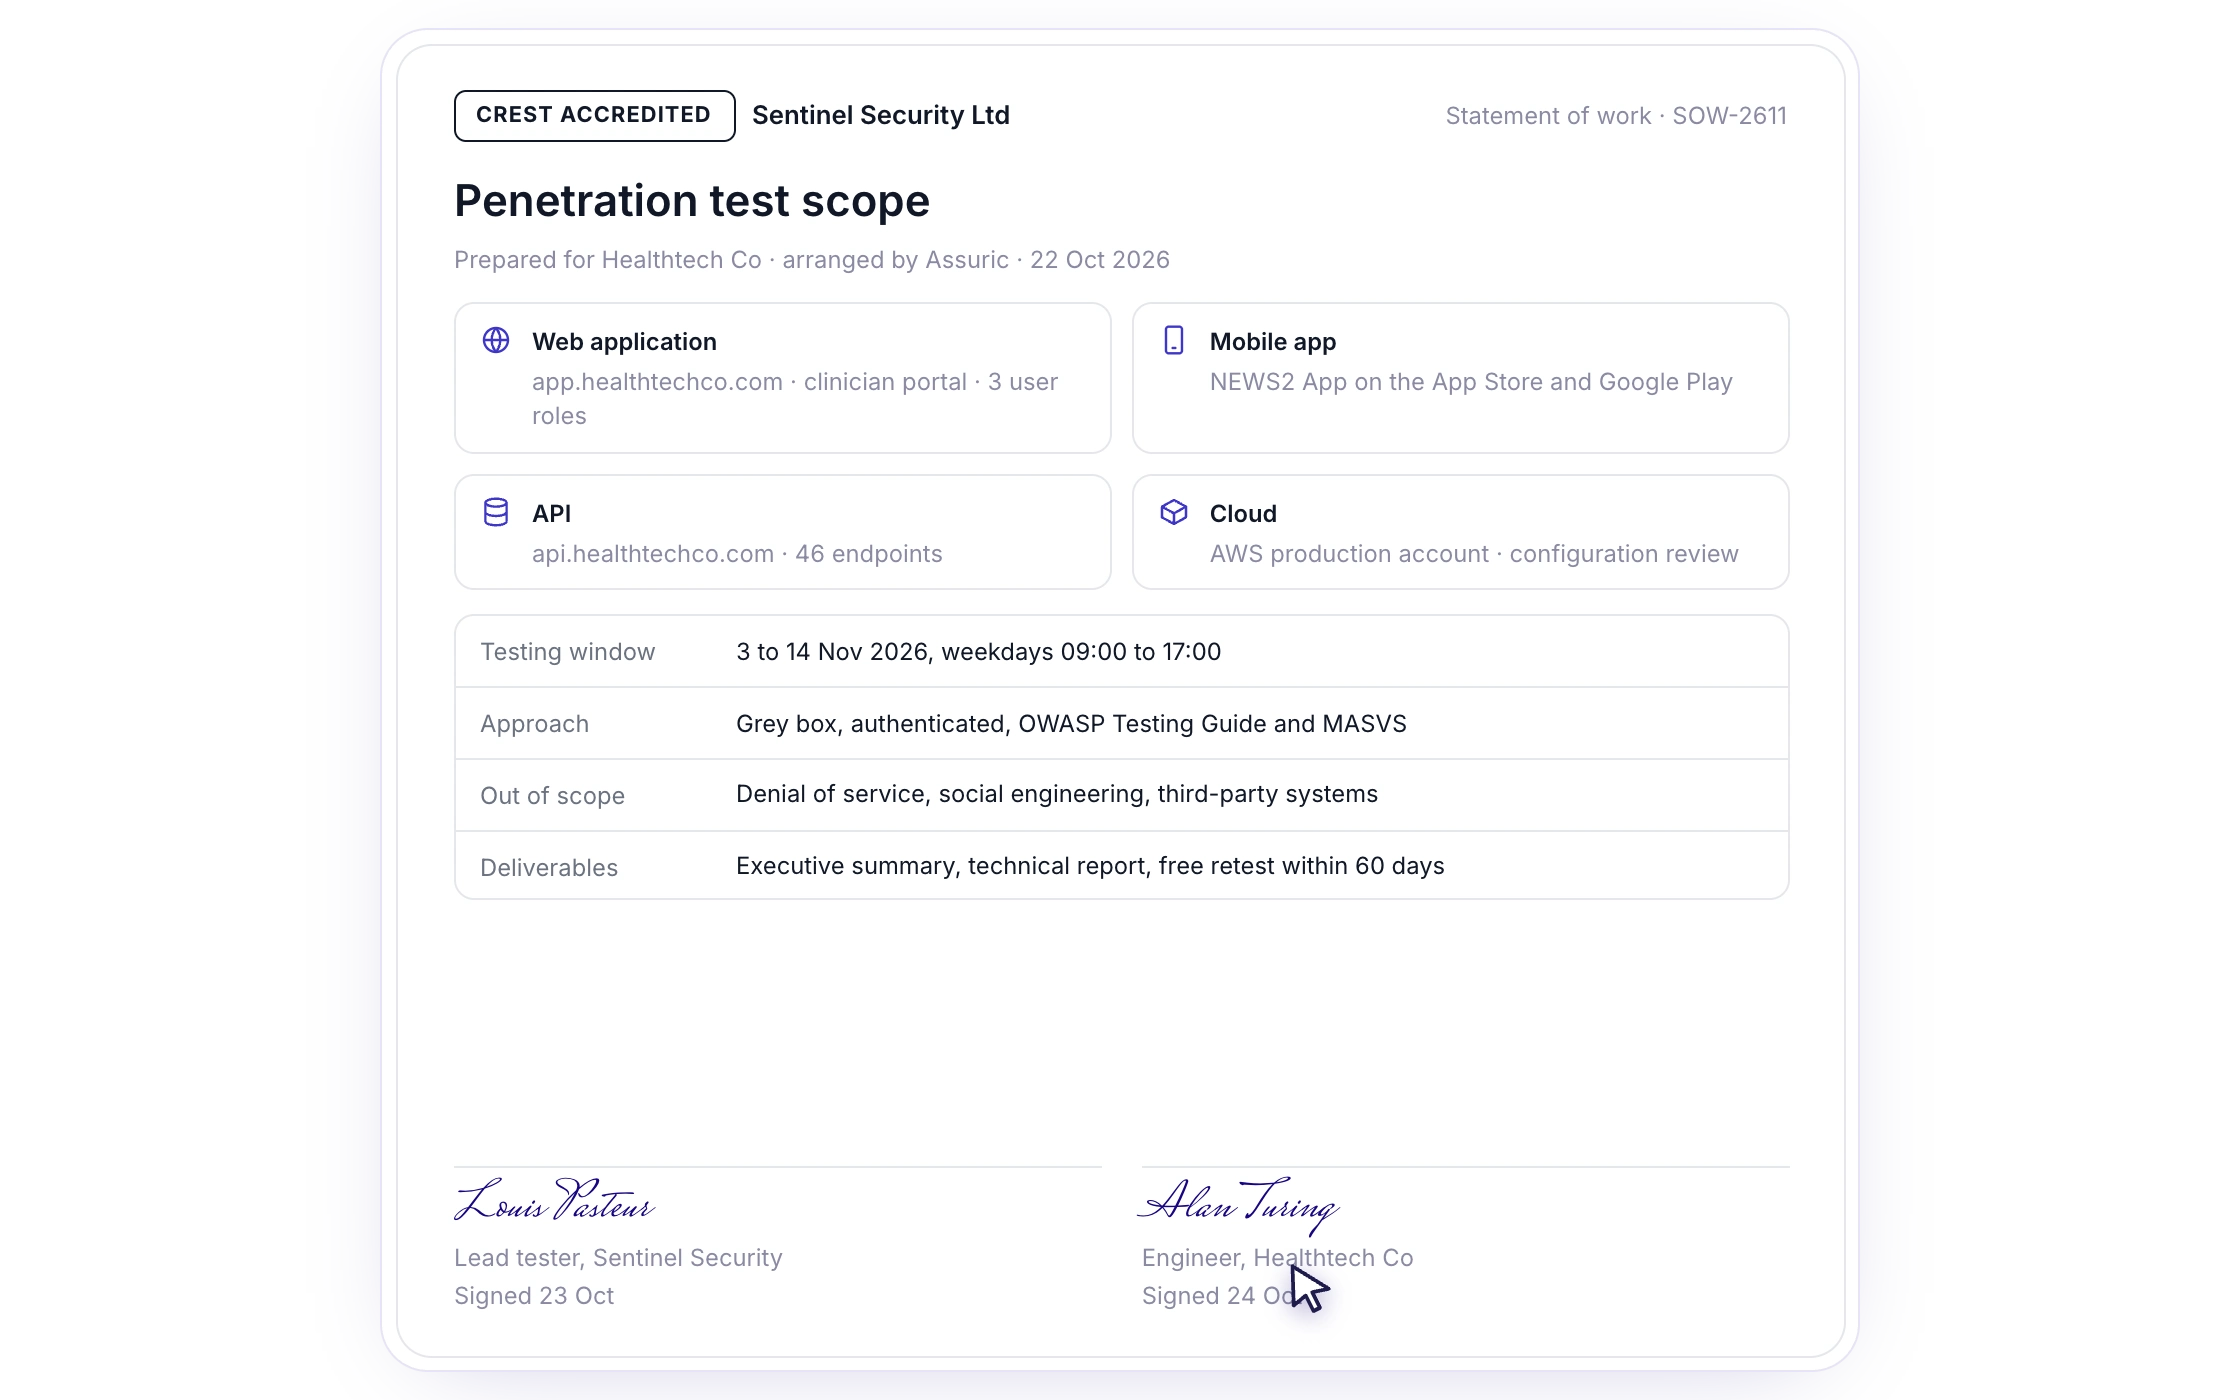
Get a quality accredited penetration test specialised for healthtech assurance, with the final report loaded straight into your workspace, mapped against the relevant controls and frameworks.
Trusted bysecurity teams


Features
A teach-back on your product and infrastructure. We cover web apps, mobile apps, infrastructure and cloud. We'll scope a secure test proportional to your needs, not beyond.
Receive a comprehensive security assessment from leading accredited testers, including CREST, who are well practised in assessing digital health technology. The methodology covers the OWASP Top 10 and AI security. We'll keep you in the loop throughout the process.

Once testing is finalised, you'll receive a report with a breakdown of the vulnerabilities identified and clear remediation advice. Executive summaries provide evidence and assurance that your app is safe.
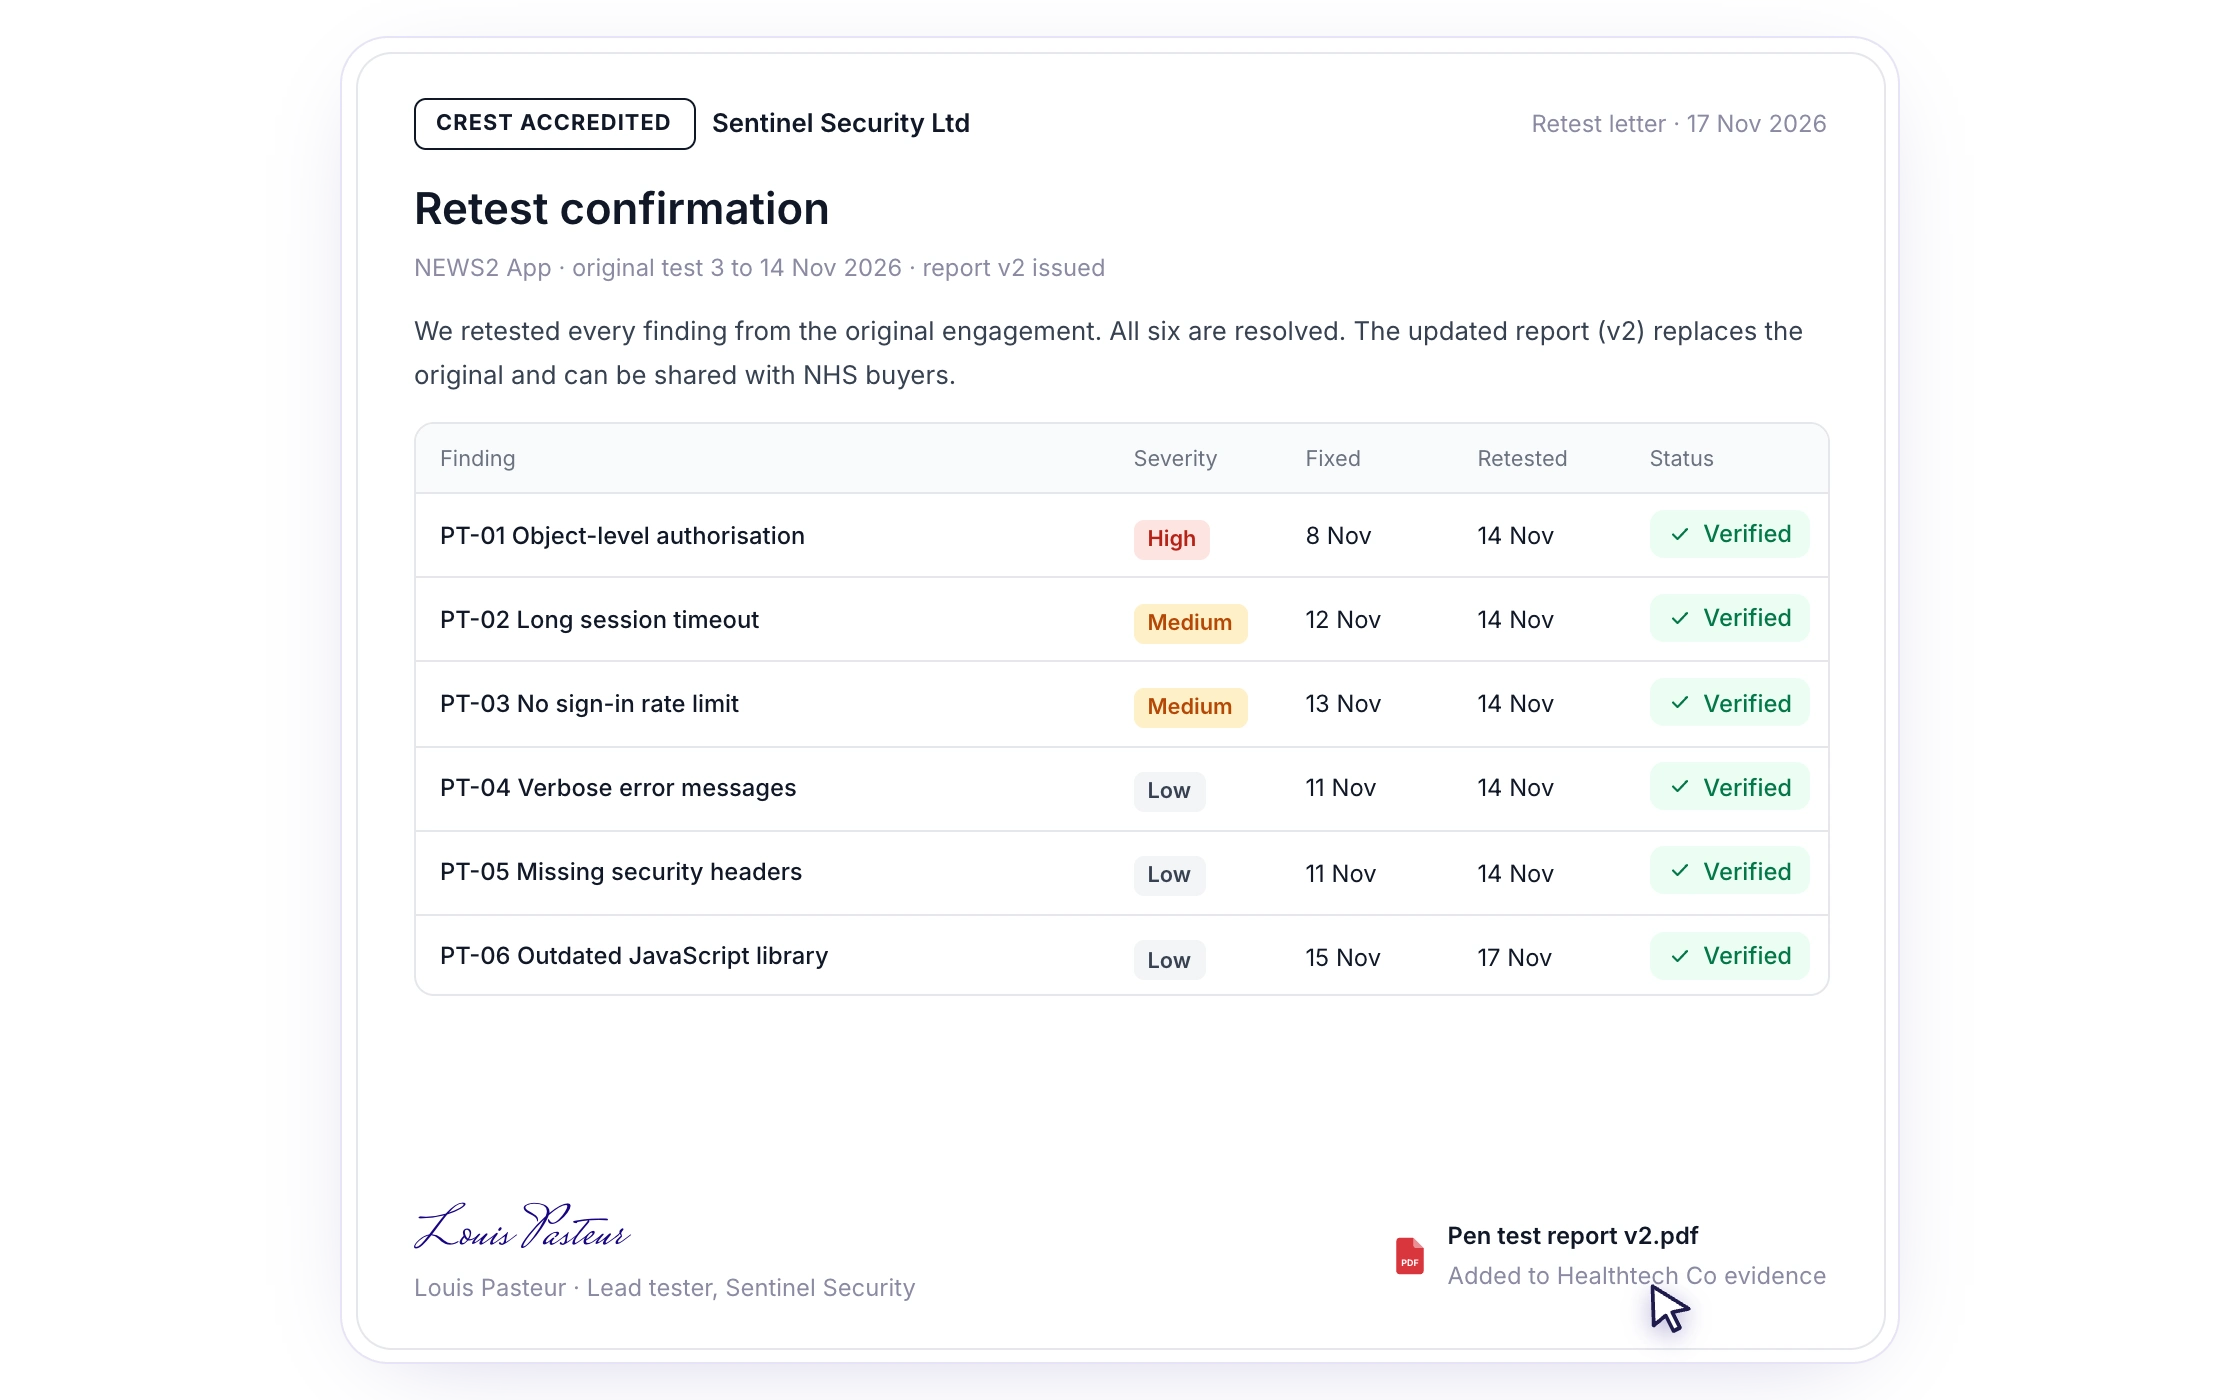
High and critical vulnerabilities are disclosed on the fly, so they can be retested straight away and there are no surprises. Outstanding remediation can be validated without additional cost, including an updated report.
Benefits

Your test is carried out by CREST-accredited penetration testers with experience assessing digital health technology. Assuric makes the introduction and handles communication throughout.
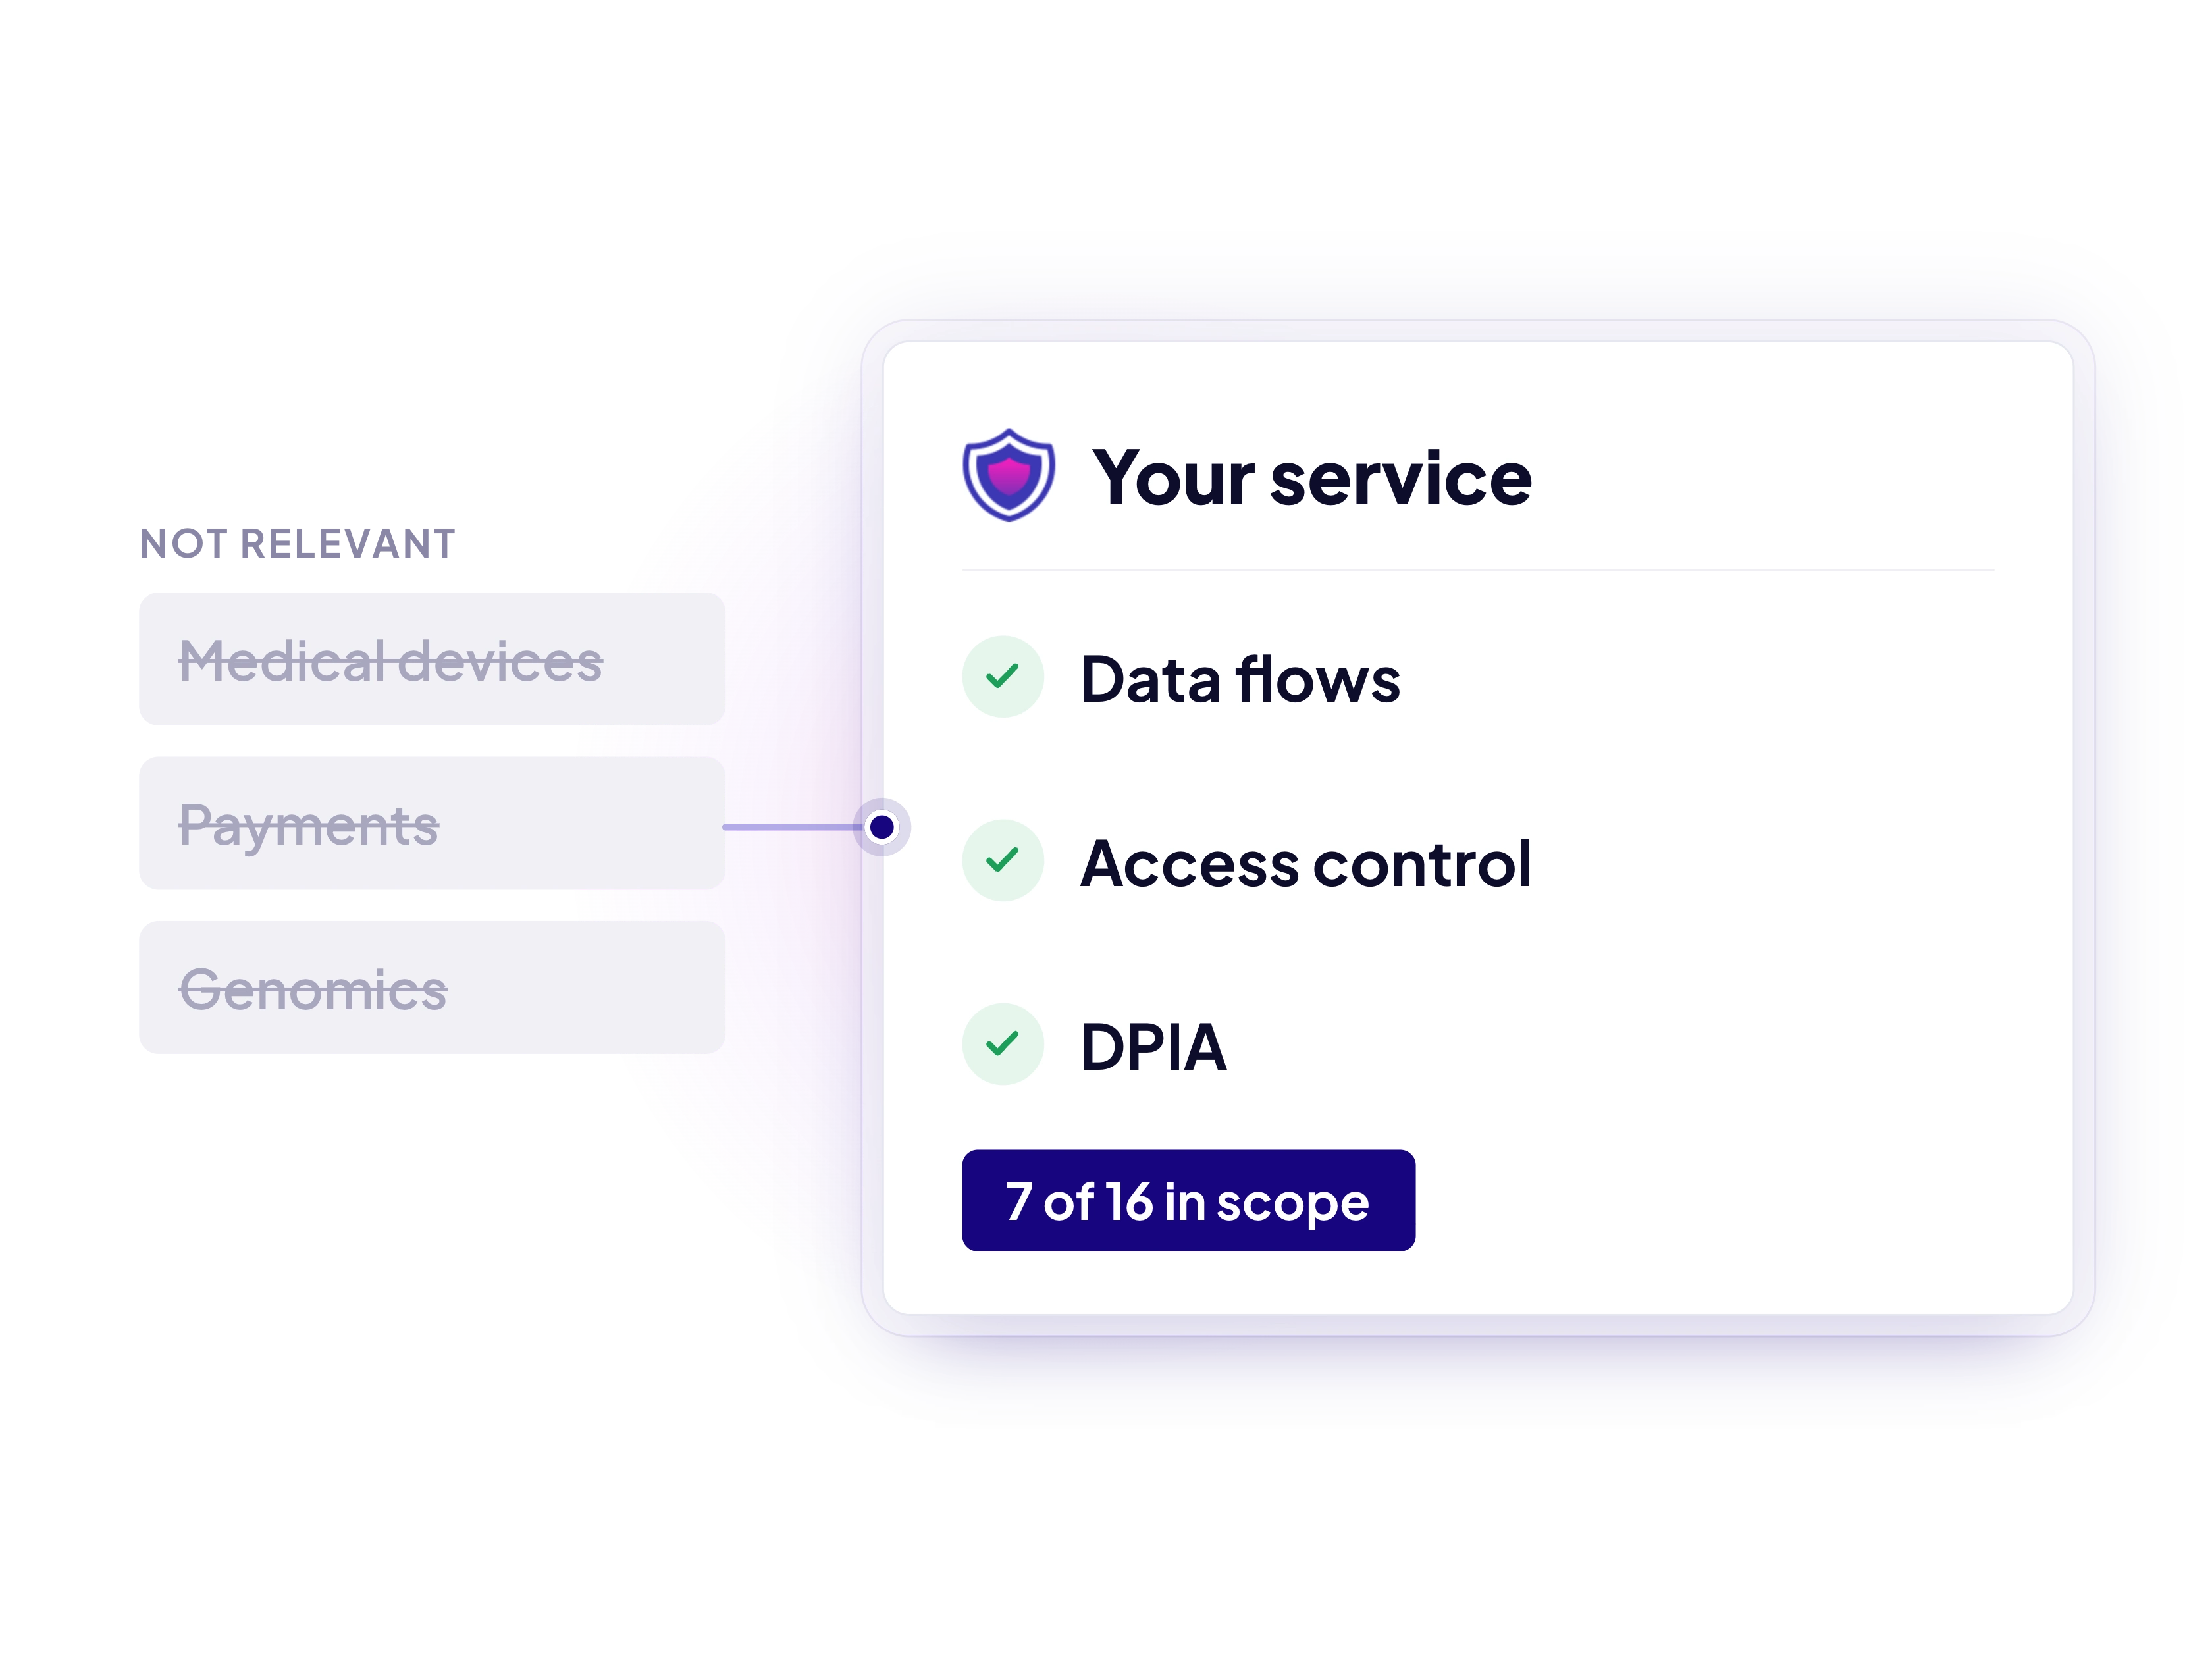
The engagement is scoped to the infrastructure, web applications and mobile applications you need tested.

Findings are identified and evaluated against the OWASP Top 10, with a clear breakdown of severity (CVSS score) and implications.

Findings are reported during the test, so you can fix issues immediately and have those fixes revalidated before the engagement ends.
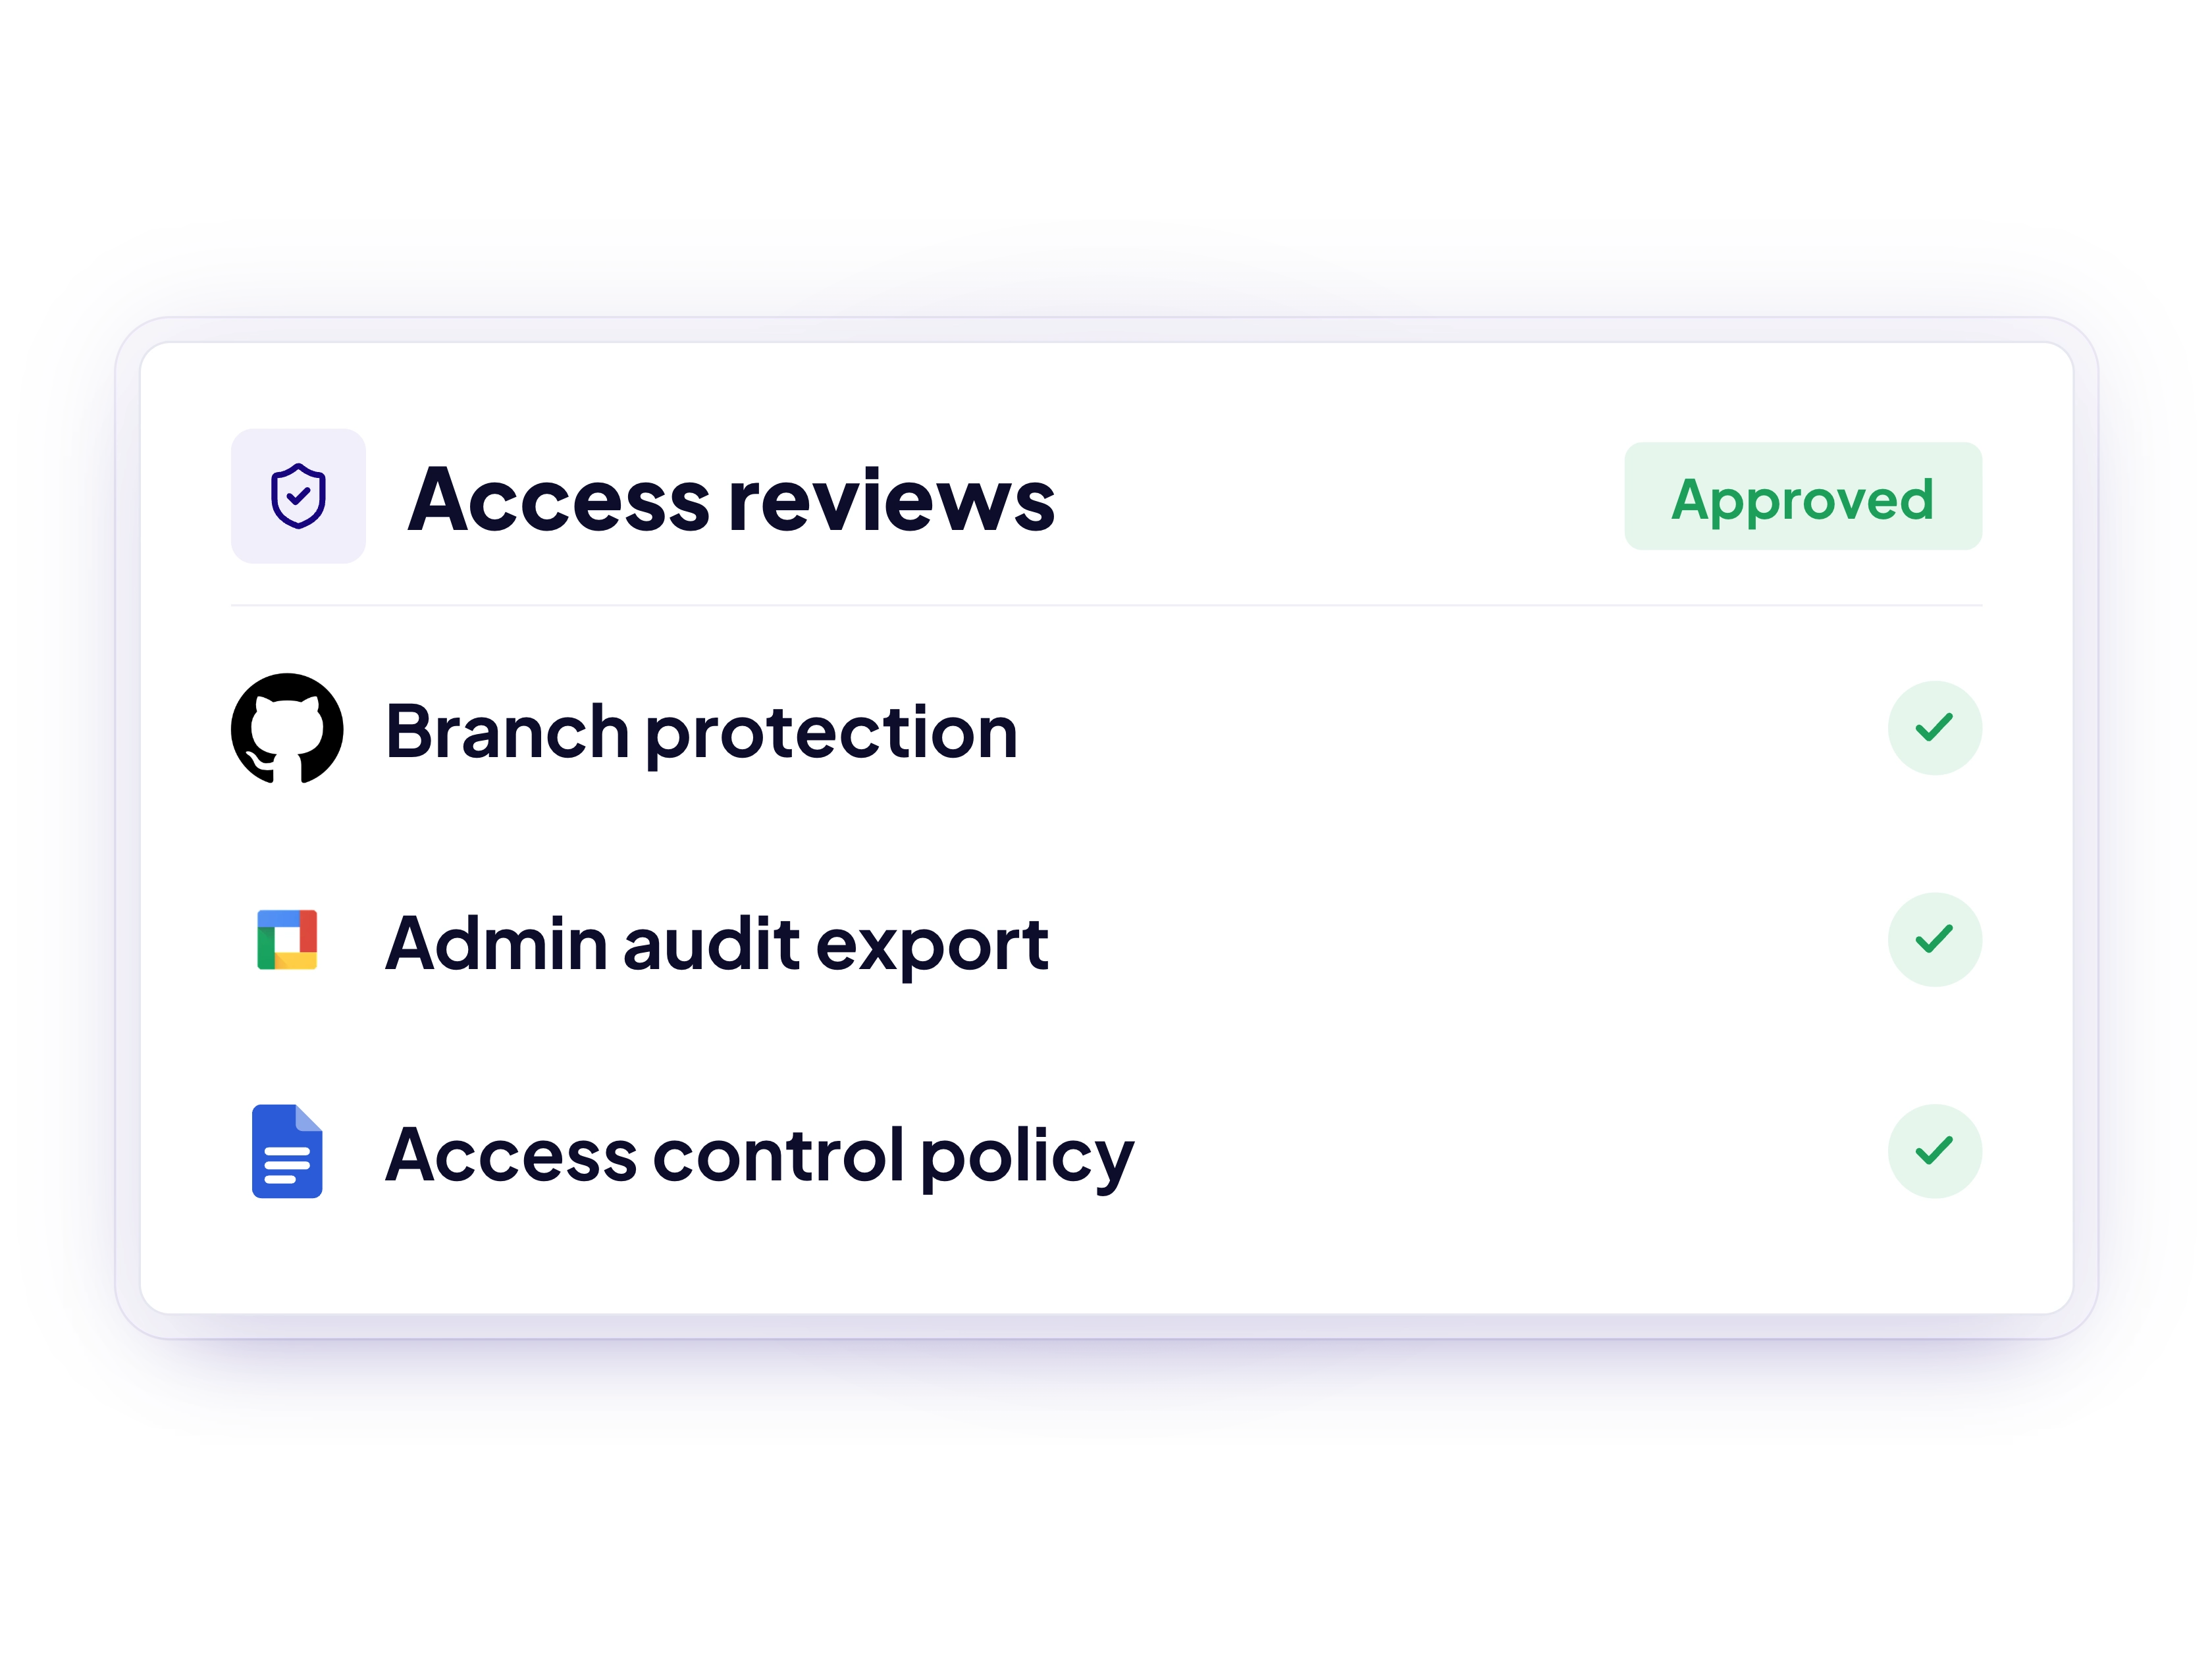
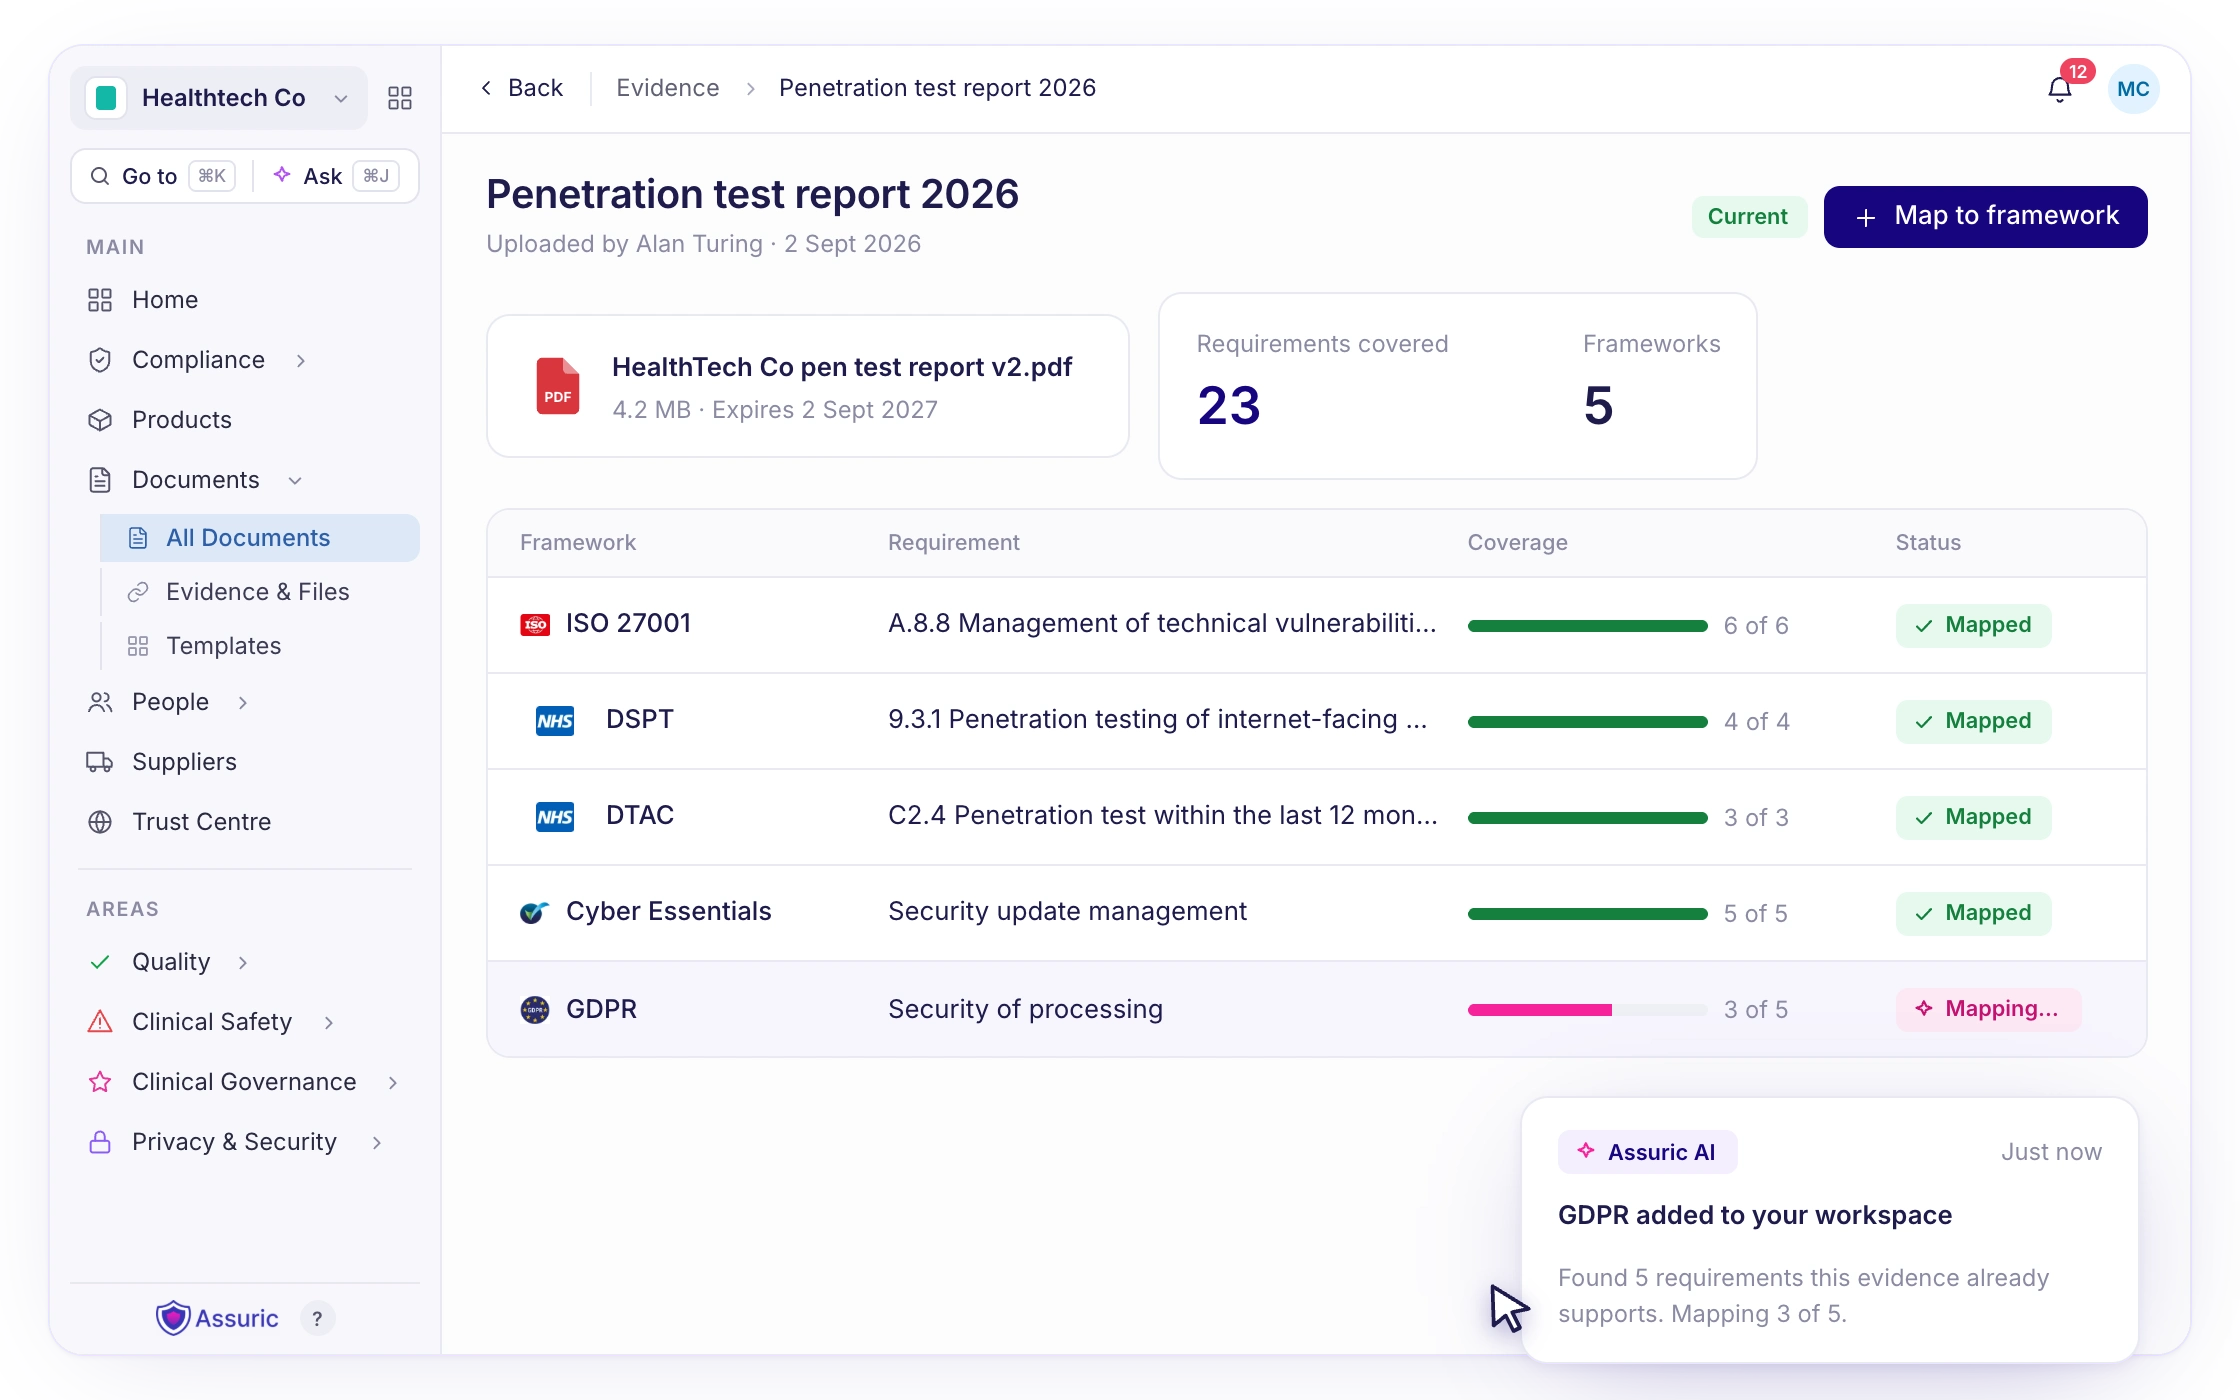
You receive a validated report, issued as evidence and held in the platform, providing a clear breakdown of identified vulnerabilities and detailed remediation advice.

Validation of required fixes can be provided at no additional cost, so each fix is validated thoroughly.

“We couldn't speak highly enough of both the Assuric team and the platform itself, which is incredibly easy to use, and with the skill and hardworking nature of the Assuric team. They've been a key component in accelerating our progress and deployments!”
Maks Kozarzewski
COO, VitVio

“The Assuric platform is a game changer in the clinical risk management field. It has been carefully designed to make the job of a CSO significantly more streamlined. The team are excellent and responsive to any product suggestions I have requested, and it has been a pleasure to work with them.”
Paul Llewellyn
CCIO, Accenture

“Assuric has been fantastic in helping us quickly and safely navigate regulatory compliance in the UK. From completing Cybersecurity requirements to DSPT, DCB0129, and DTAC, the team was supportive, extremely knowledgeable, and the platform made everything quick and straightforward. A separate regulatory company we consulted at the beginning even remarked on how quickly we achieved compliance!”
Katie Baker
Director UK & Ireland, Tandem
Overlapping requirements and evidence are mapped across frameworks automatically, so you never do the same work twice.
DTAC expects Cyber Essentials as a baseline, and asks whether your product has had a penetration test in the last 12 months, along with a summary of the findings and remediation.
Cyber Essentials Plus is a technical verification against a defined set of controls. A penetration test is an active attempt to find and exploit weaknesses, scoped to your systems. They serve different purposes, and many buyers ask for both.
At least once a year is the common expectation, and again after significant changes to your infrastructure or application, such as a major release or a new hosting environment.
One of our trusted partners, who have run tests with us for years. Every test is a CREST-accredited white box penetration test, carried out by testers experienced in digital health. Our rates are very competitive, and even lower for existing Assuric customers. The price depends on what’s in scope: the work is scoped on a free call, based on how many days the test needs, and you receive a statement of work and quote before you commit.
In a white box test, the testers are given information about your systems, such as architecture and access credentials, so they can test thoroughly and efficiently. A black box test simulates an outside attacker with no prior knowledge. Our tests are white box, which gives deeper coverage in the time available.
Web applications, mobile apps, infrastructure, cloud environments and AI features, depending on your scope. Findings are assessed against the OWASP Top 10 and scored by severity (CVSS), with clear remediation advice for each one. Most tests take a few days of testing time, and the timeline, including the start date and when you’ll receive the report, is agreed on the scoping call before you commit.
Testing is planned with you during scoping to avoid disruption. Where needed, tests can run against a staging environment or at agreed times, so your live service isn’t affected.
High and critical findings are shared with you as soon as they’re found, rather than waiting for the final report, so you can fix them straight away. Re-testing is included: fixes are validated at no additional cost, and you receive an updated report showing what’s been resolved.
Yes. The final report is held as evidence in your Assuric workspace, and you can share it, or its executive summary, through your Trust Centre, approving access for each buyer who requests it.
Featured post
A founder's guide to penetration testing, from a team that's run hundreds of them

Book a free scoping call and we’ll quote for a CREST-accredited test sized to your product, with the report filed straight into your workspace.


